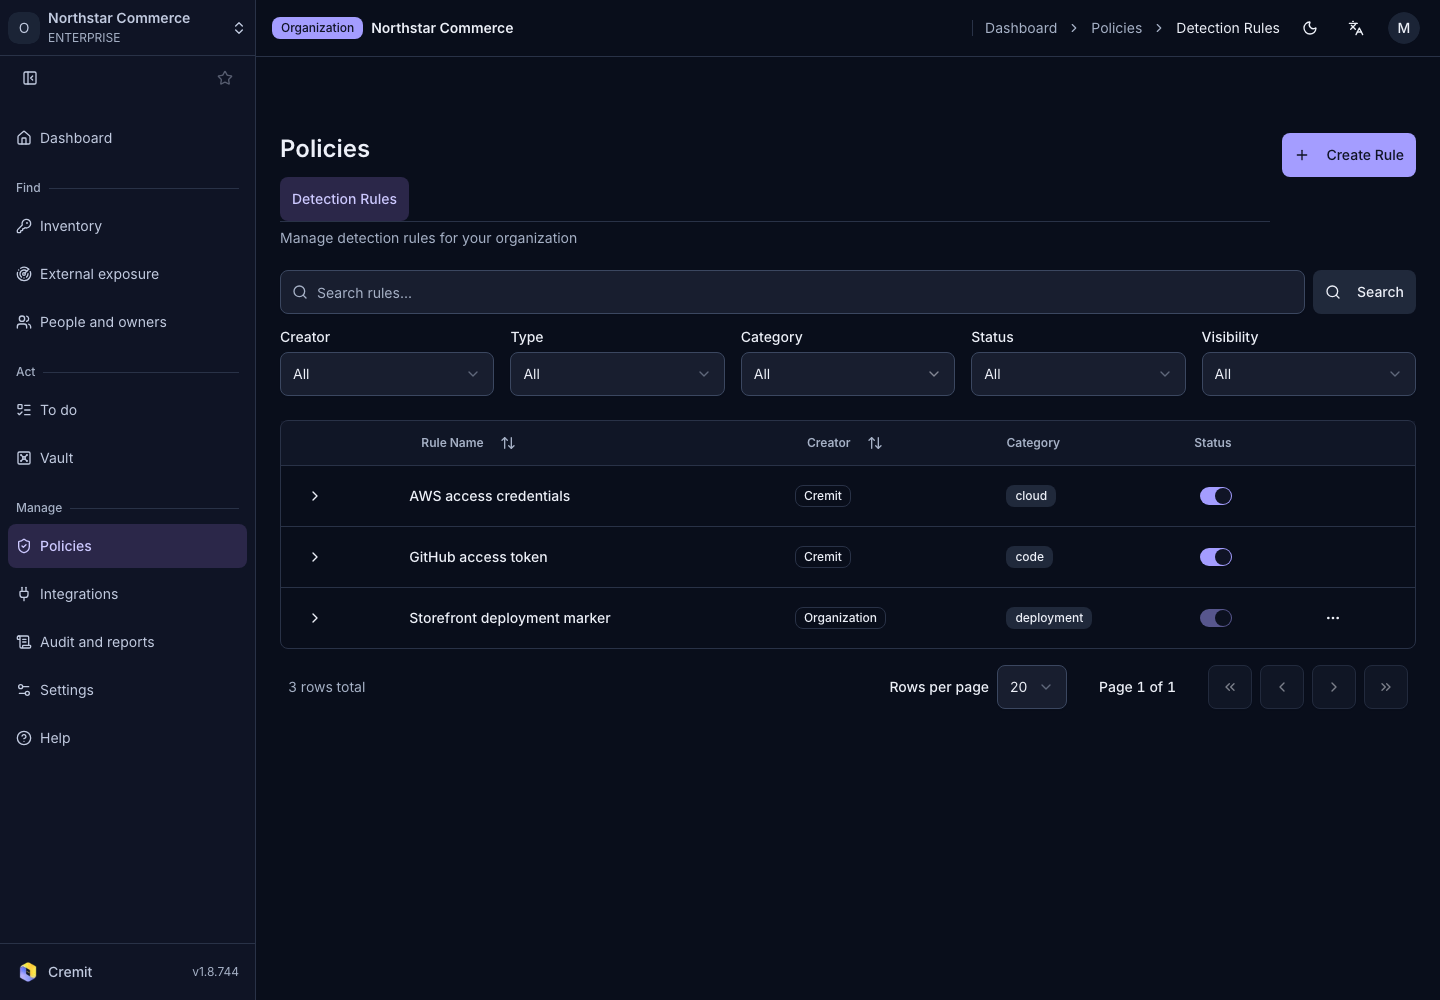
Policies
Detection rules
Search detection rules and review their matching criteria.
Find a rule
- Open Policies › Detection Rules.
- Use search and filters to find a rule.
- Open it to review its matching criteria and information.
Detection rules identify strings that may be secrets. A match alone does not establish that a secret works. Check Verification status separately when reviewing a finding.
Review changes
Edit and save fields on rules you have permission to change. Check changed criteria using a nonworking test string. Review the organization's required detection scope before applying changes.