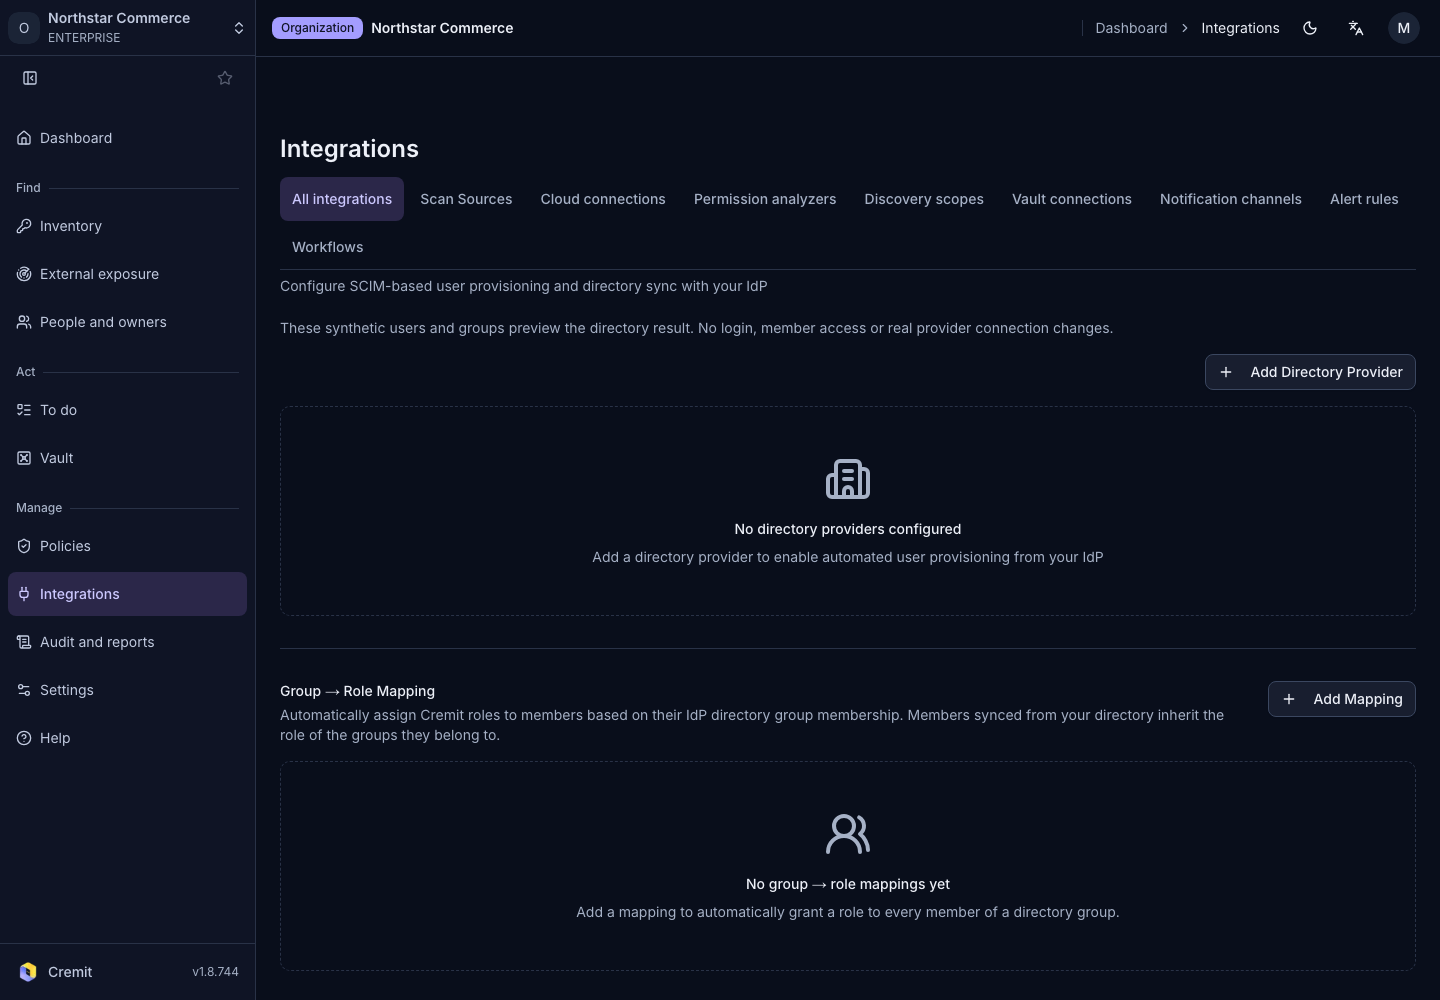
Integrations
Okta directory sync
Configure an Okta directory provider and SCIM token for user and group provisioning.
Create a provider
- Open Directory sync from All integrations.
- Select Add Directory Provider.
- Enter Provider Name.
- Choose Okta in Provider Type.
- Select Create.
Verify synchronization
The organization owner creates a token in the provider’s token list and gives it, together with the displayed SCIM endpoint, to your IdP administrator. The plaintext token is shown only immediately after creation; store it securely. Configure provisioning in Okta, then review actual synchronized users and groups.
See the official documentation for setup and permissions. Directory inactivity and secret revocation are separate states. Review an inactive user's secrets with the current responder and issuing service.