Integrations
GCP API key restriction analysis
Use the GCP analyzer entry to connect a project for API key restriction analysis.
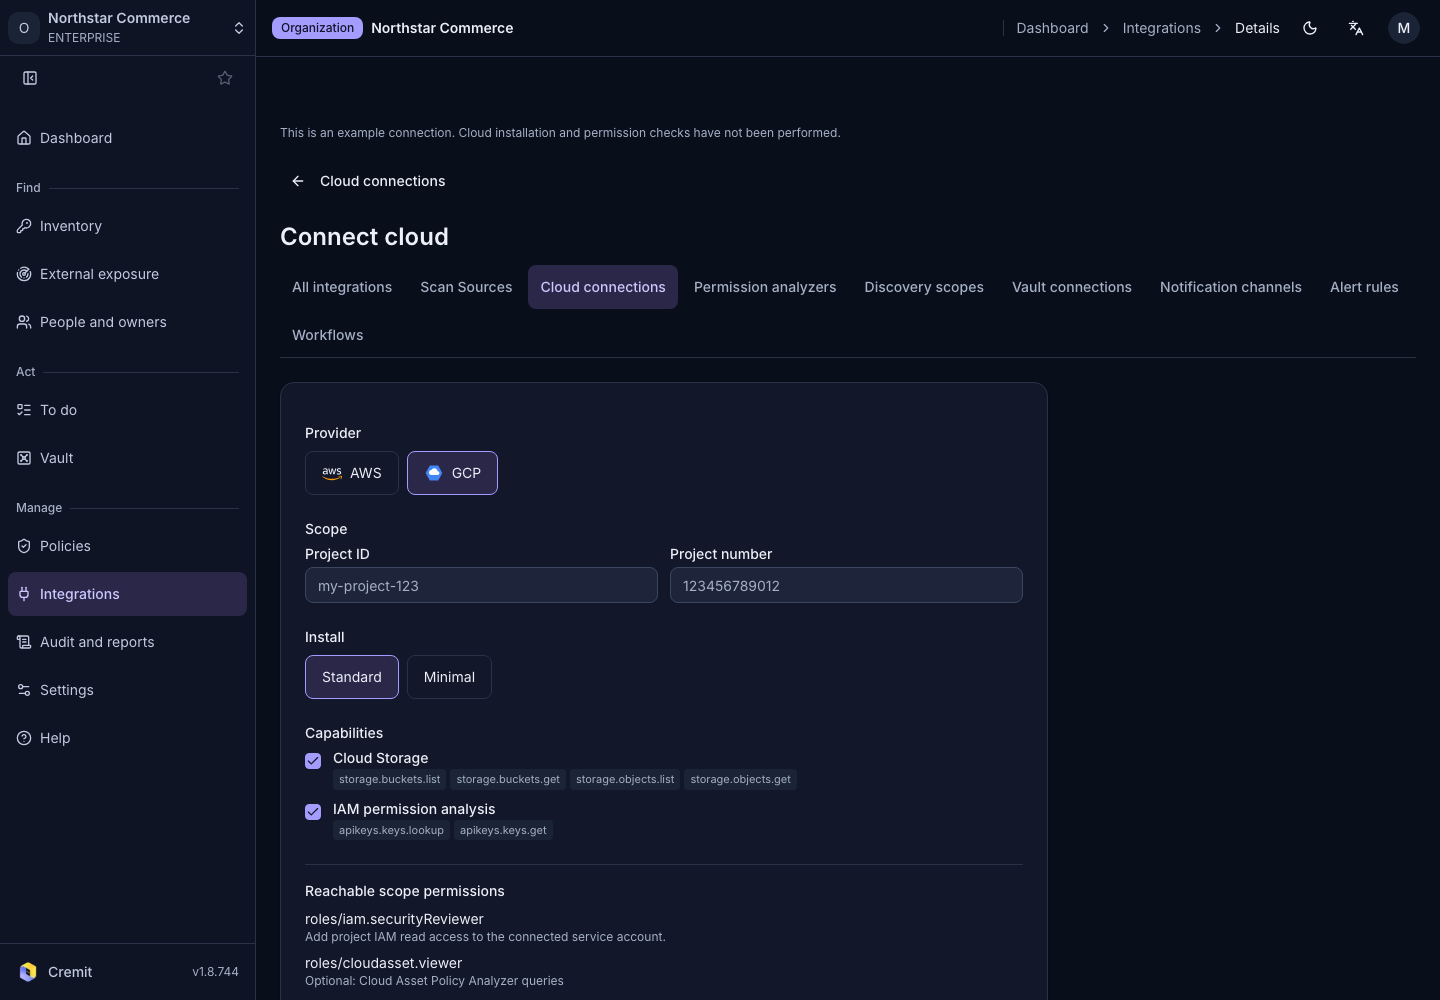
Connect a GCP analyzer
- In Permission analyzers, select Add GCP Analyzer.
- Check the GCP provider on the cloud connection form that opens.
- Enter the analysis project's Project ID.
- Enter the same project's Project number.
- Choose Standard or Minimal under Install.
- Check that IAM permission analysis is selected.
- Select Create connection.
New analyzers use the project's Workload Identity Federation connection instead of a pasted key file. Choose a format in Setup and save it with Download. Review and apply the project permissions, then select Verify. Follow Google Cloud projects for the detailed setup sequence.
Check the registration
Return to the Registered Analyzers table and review the GCP row's connection status, account information, and registration date. Its cloud detail button opens the project's permission and feature usage state.
Analysis helps investigate API key restrictions and access scope. It does not represent actual API call history or every permission evaluation.