
Apr 15, 2026
The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure
An organization's core credentials sat in public repositories for years. The security industry's answer: "Out of scope."

Ben Kim
Field studies, incident analyses and response guides from the Cremit research team, written from what we measured.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy
An organization's core credentials sat in public repositories for years. The security industry's answer: "Out of scope."
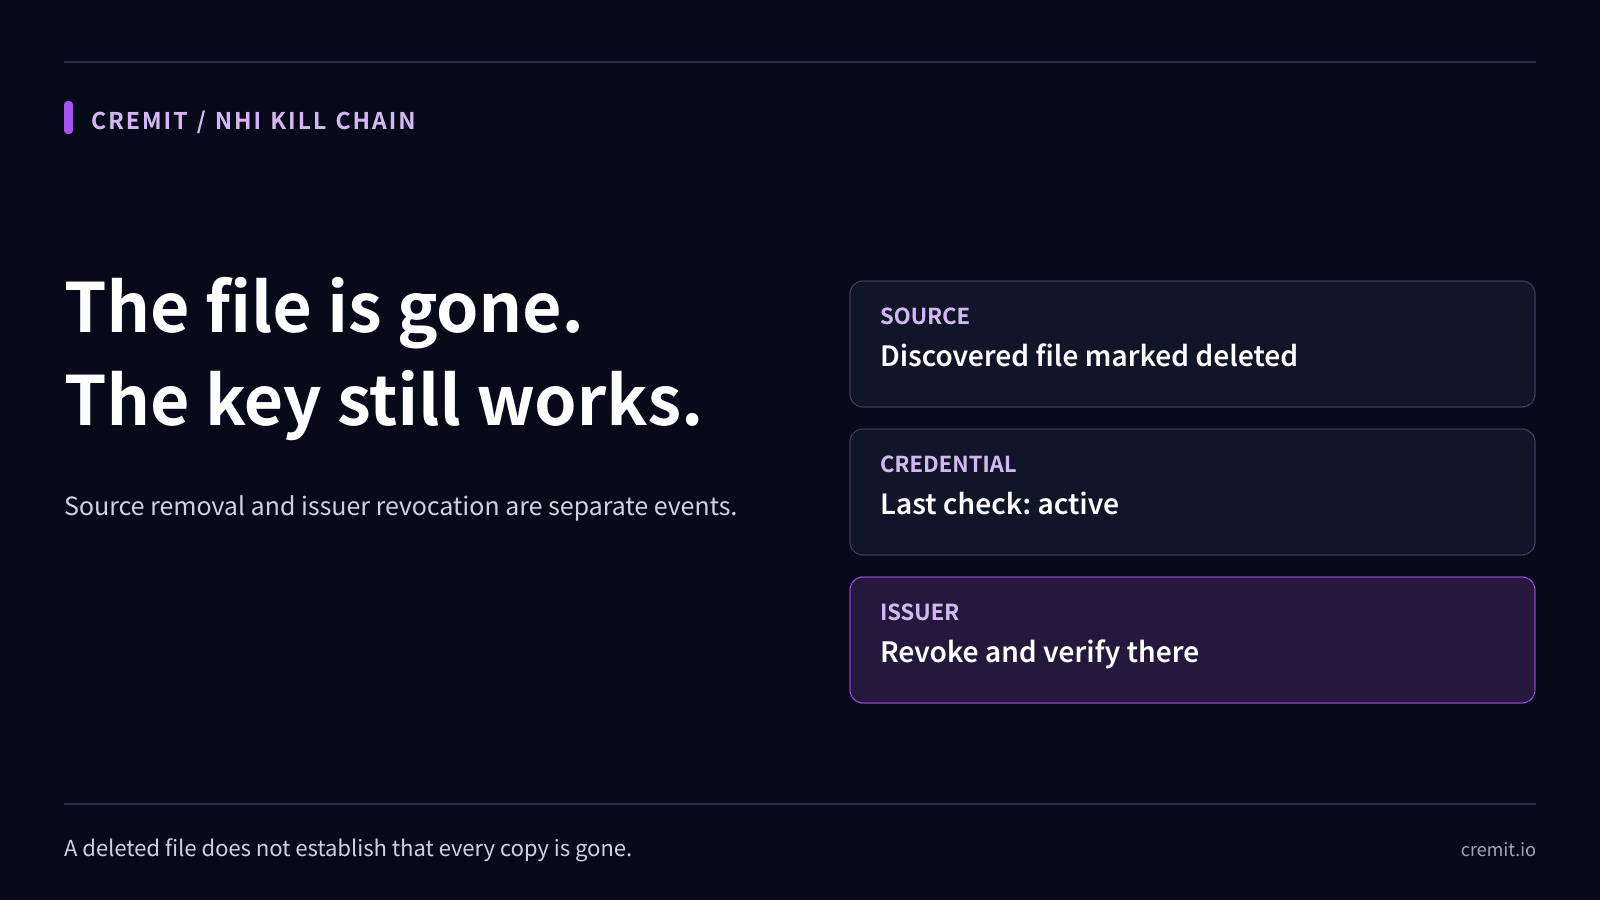
Source removal does not revoke a credential. Check the issuer, Git history, current owner, and last verification before closing the finding.
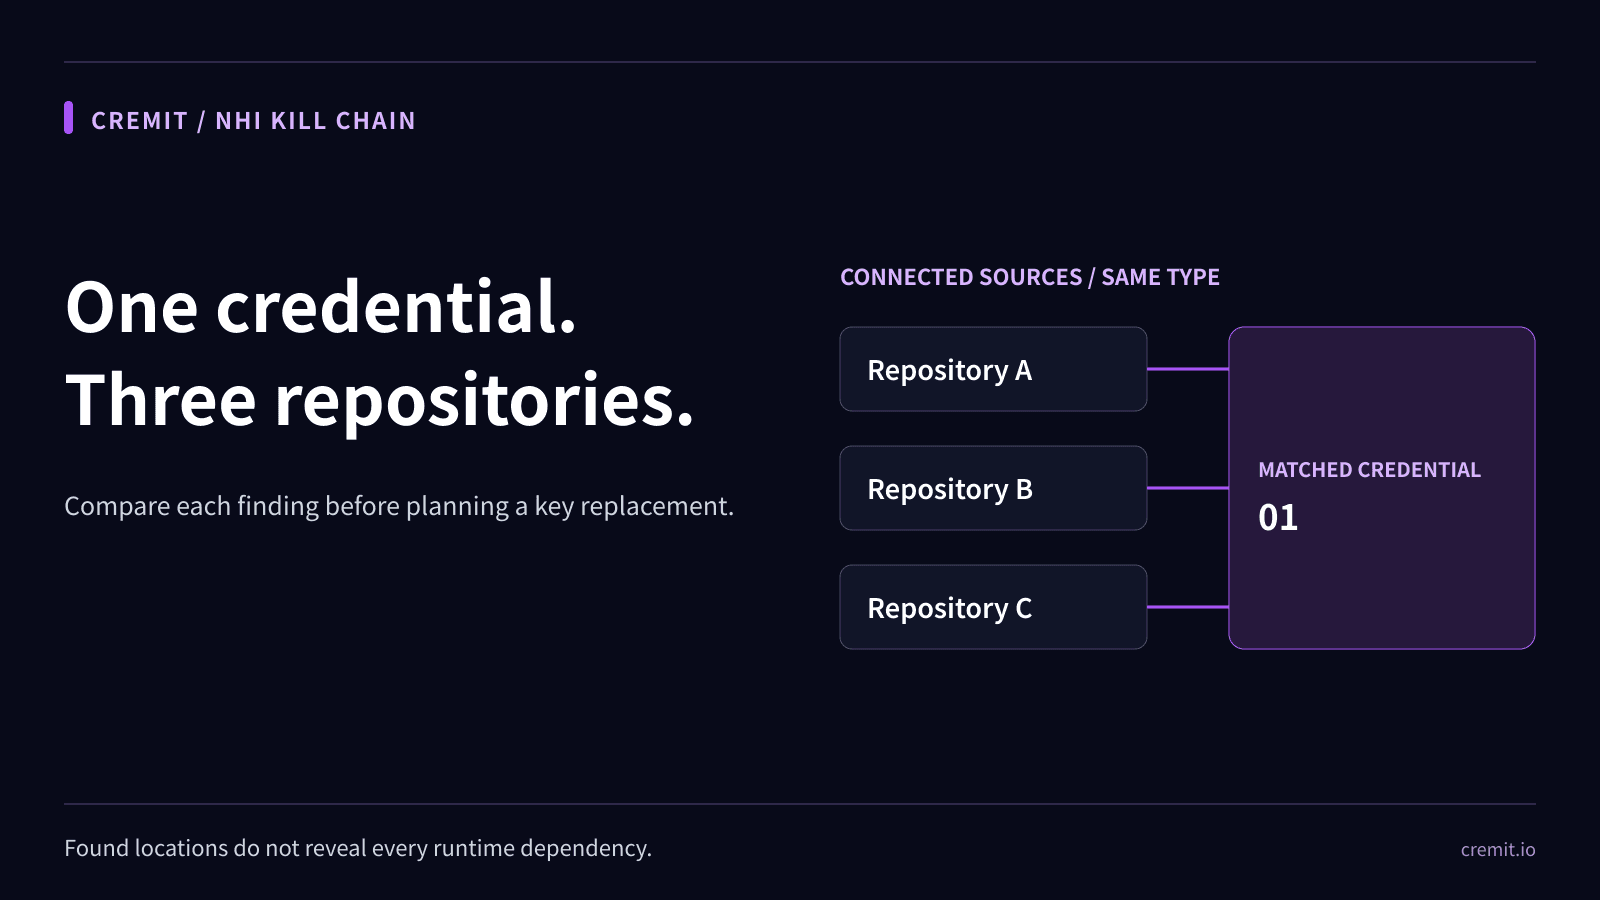
Three observed locations are not a complete dependency map. Check key type, issuer status, permissions, and actual consumers before replacement.
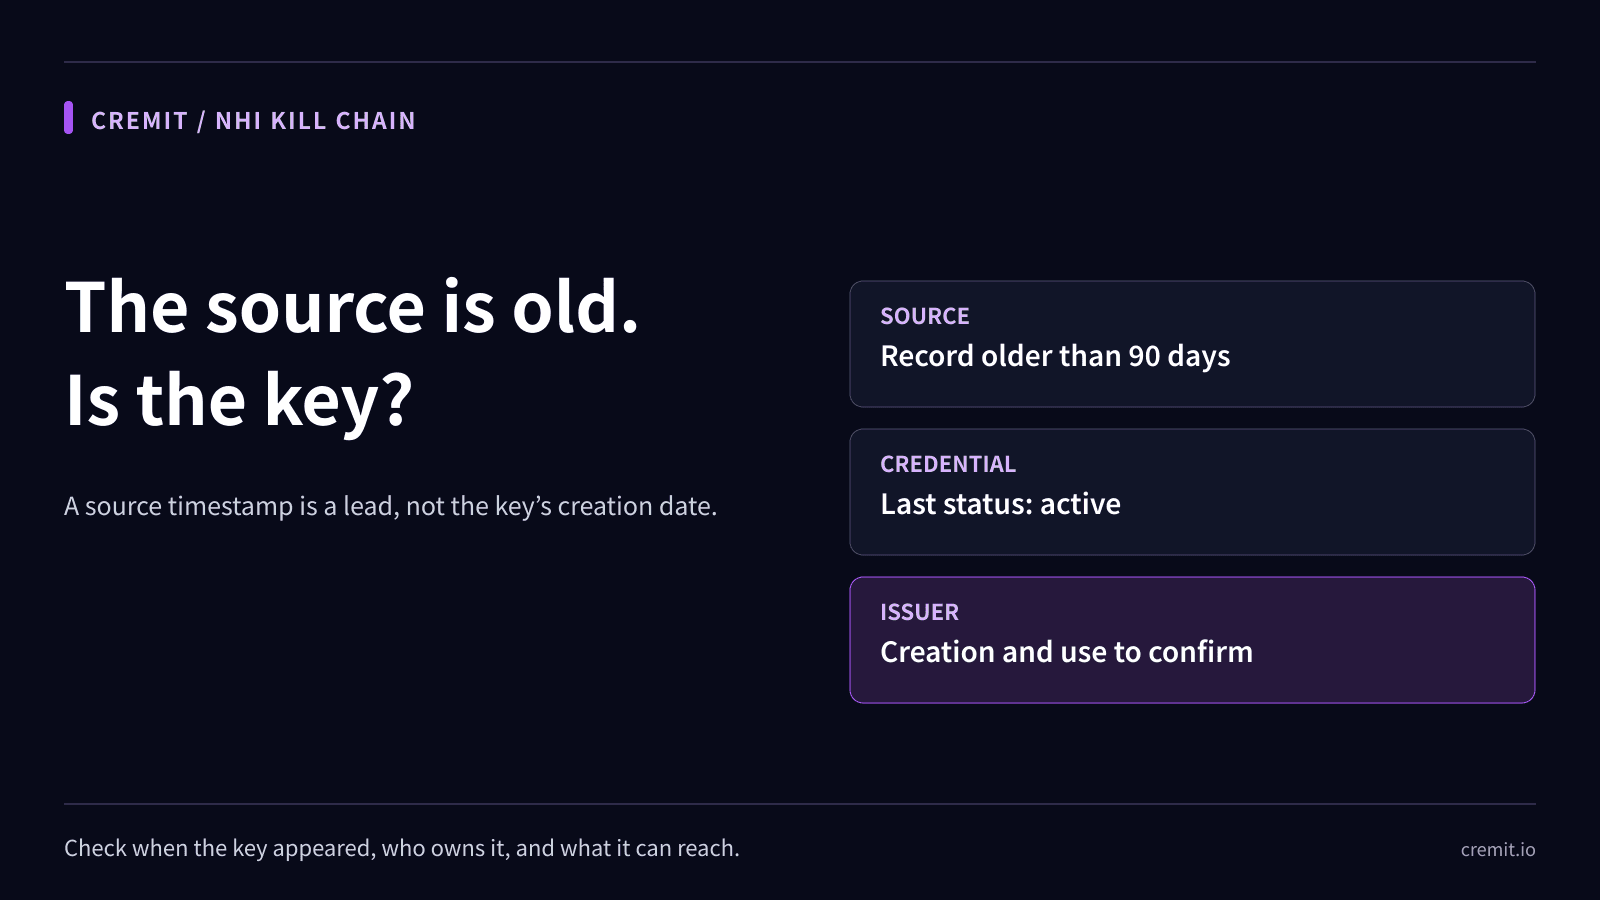
An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.
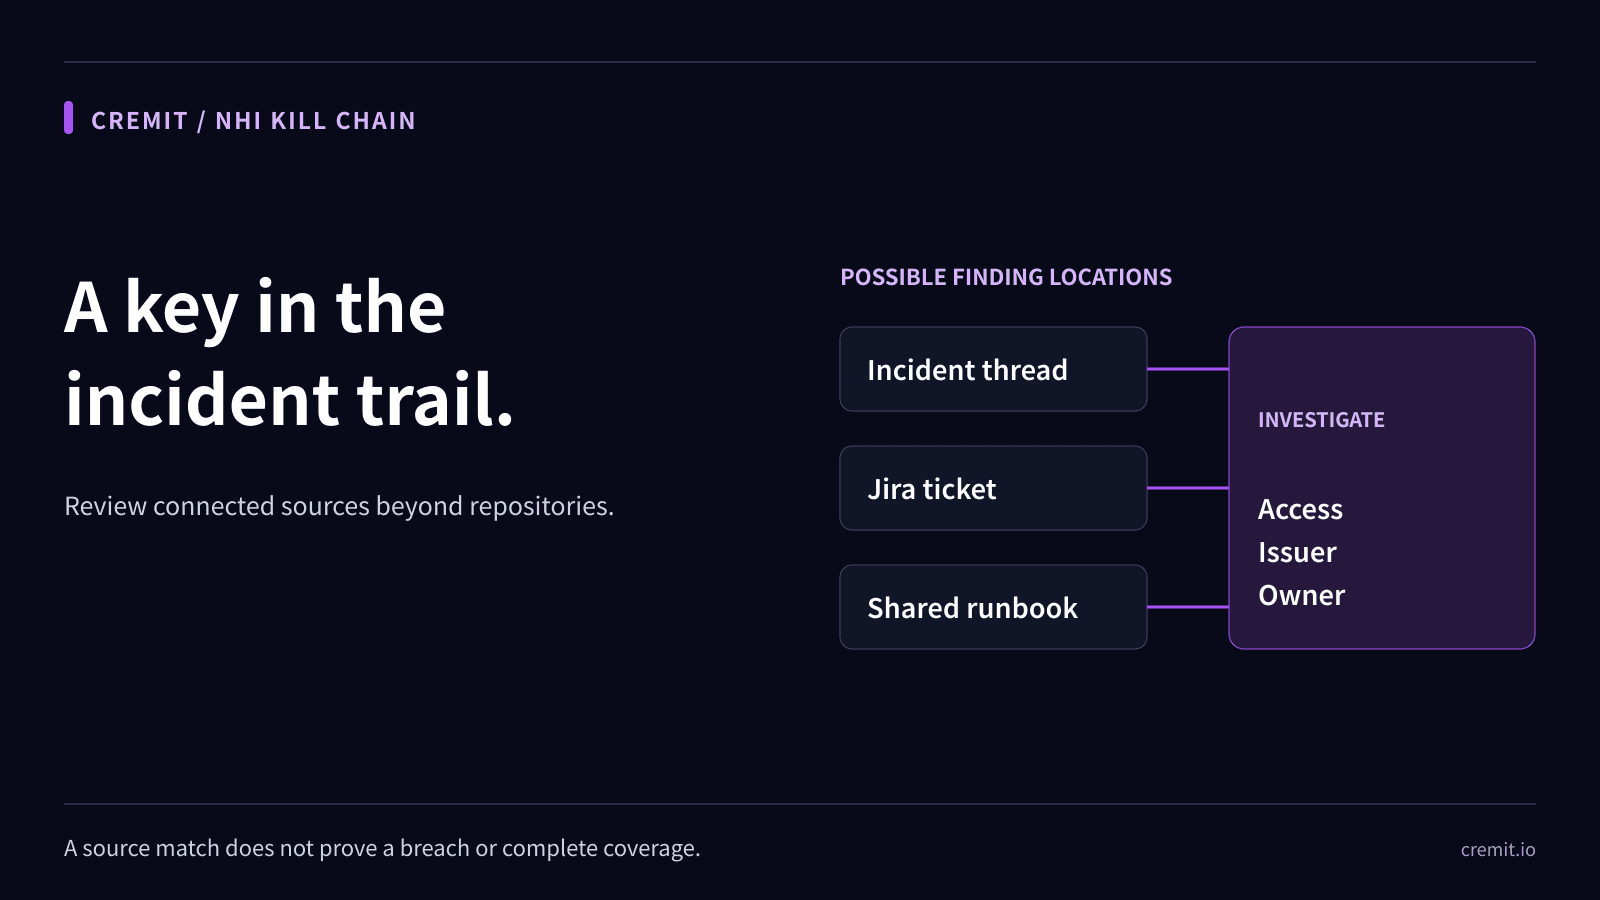
A credential outside a repository needs a source-access review, issuer check, owner, and verified response. A finding alone does not prove misuse.
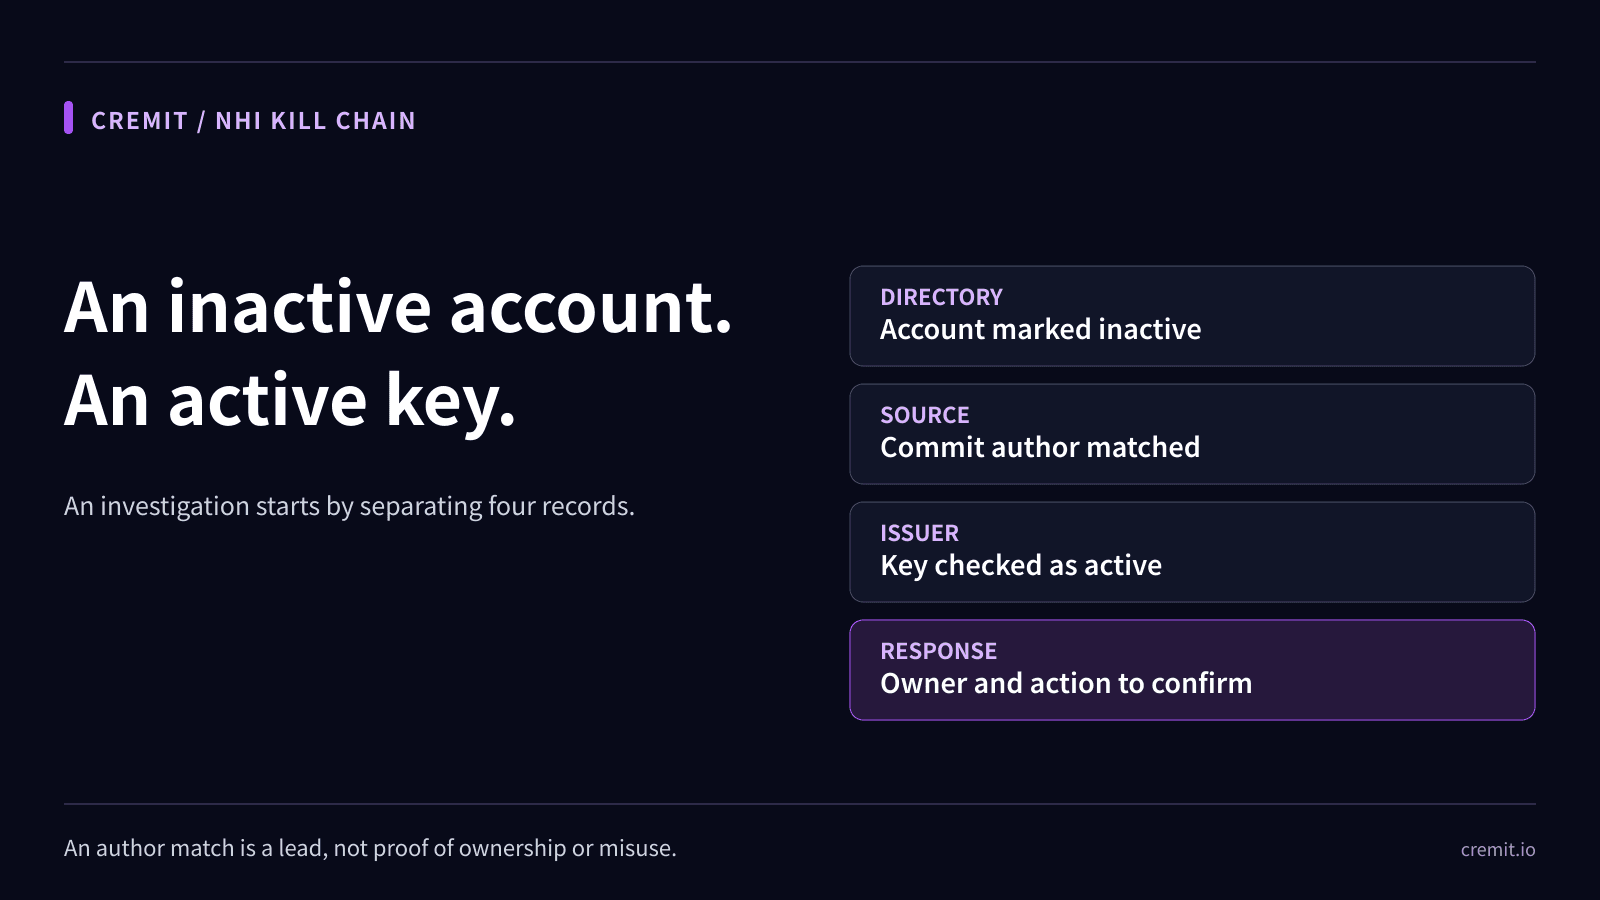
An active key linked to an inactive author is a lead. Check the directory, source, issuer, and current service owner before deciding what happened.

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.
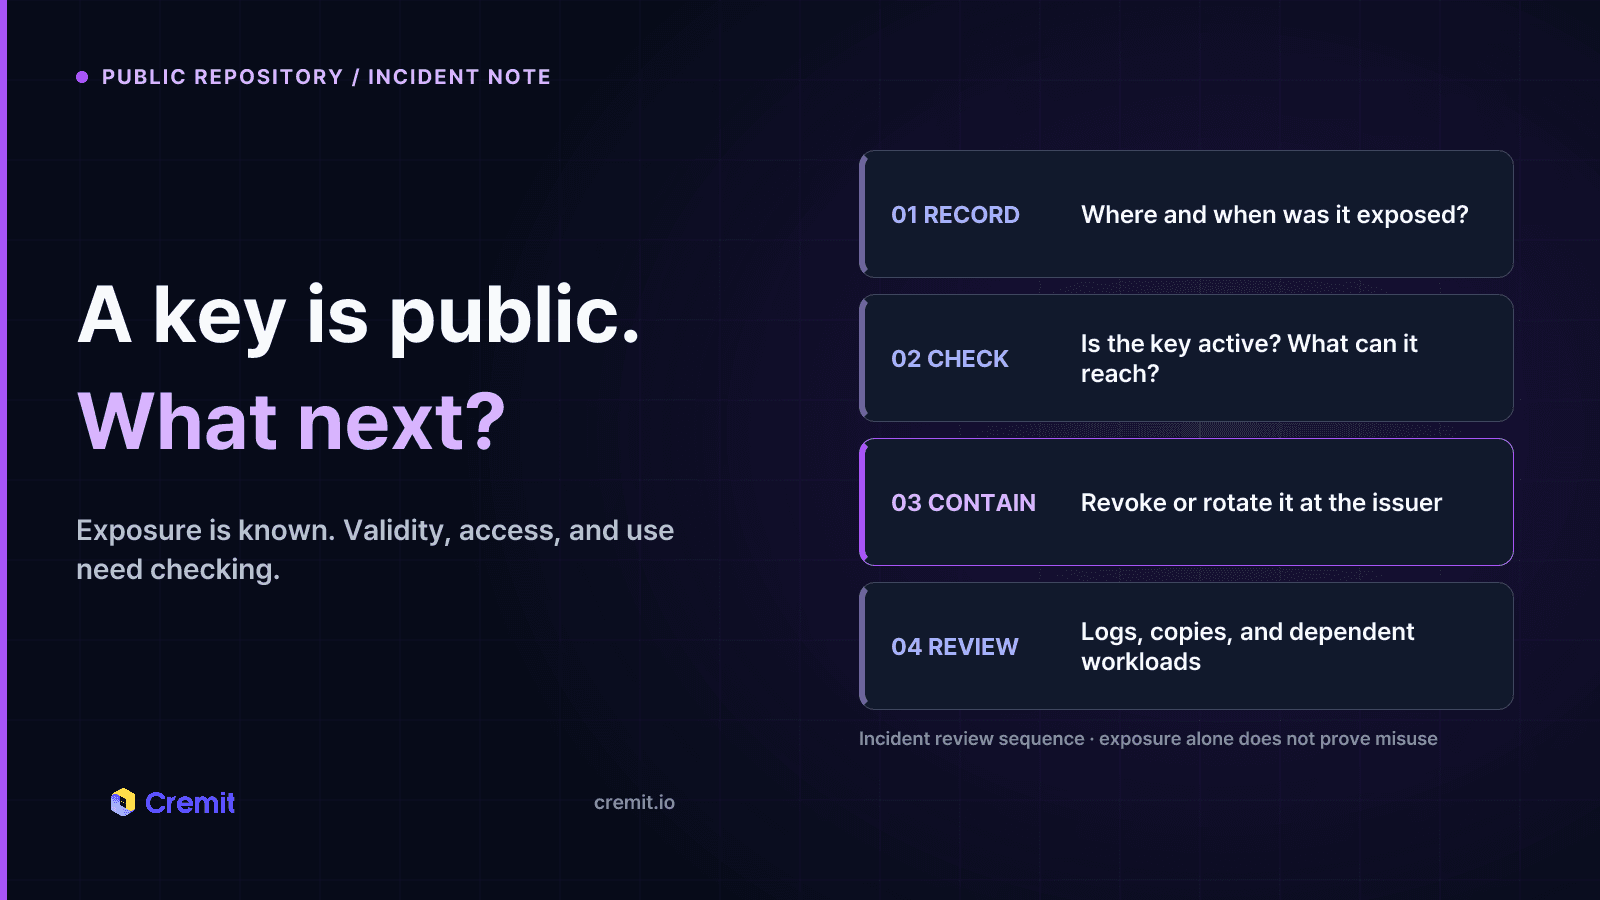
A public commit proves exposure, not misuse. Check validity, permissions, issuer logs, and dependent workloads before closing the incident.
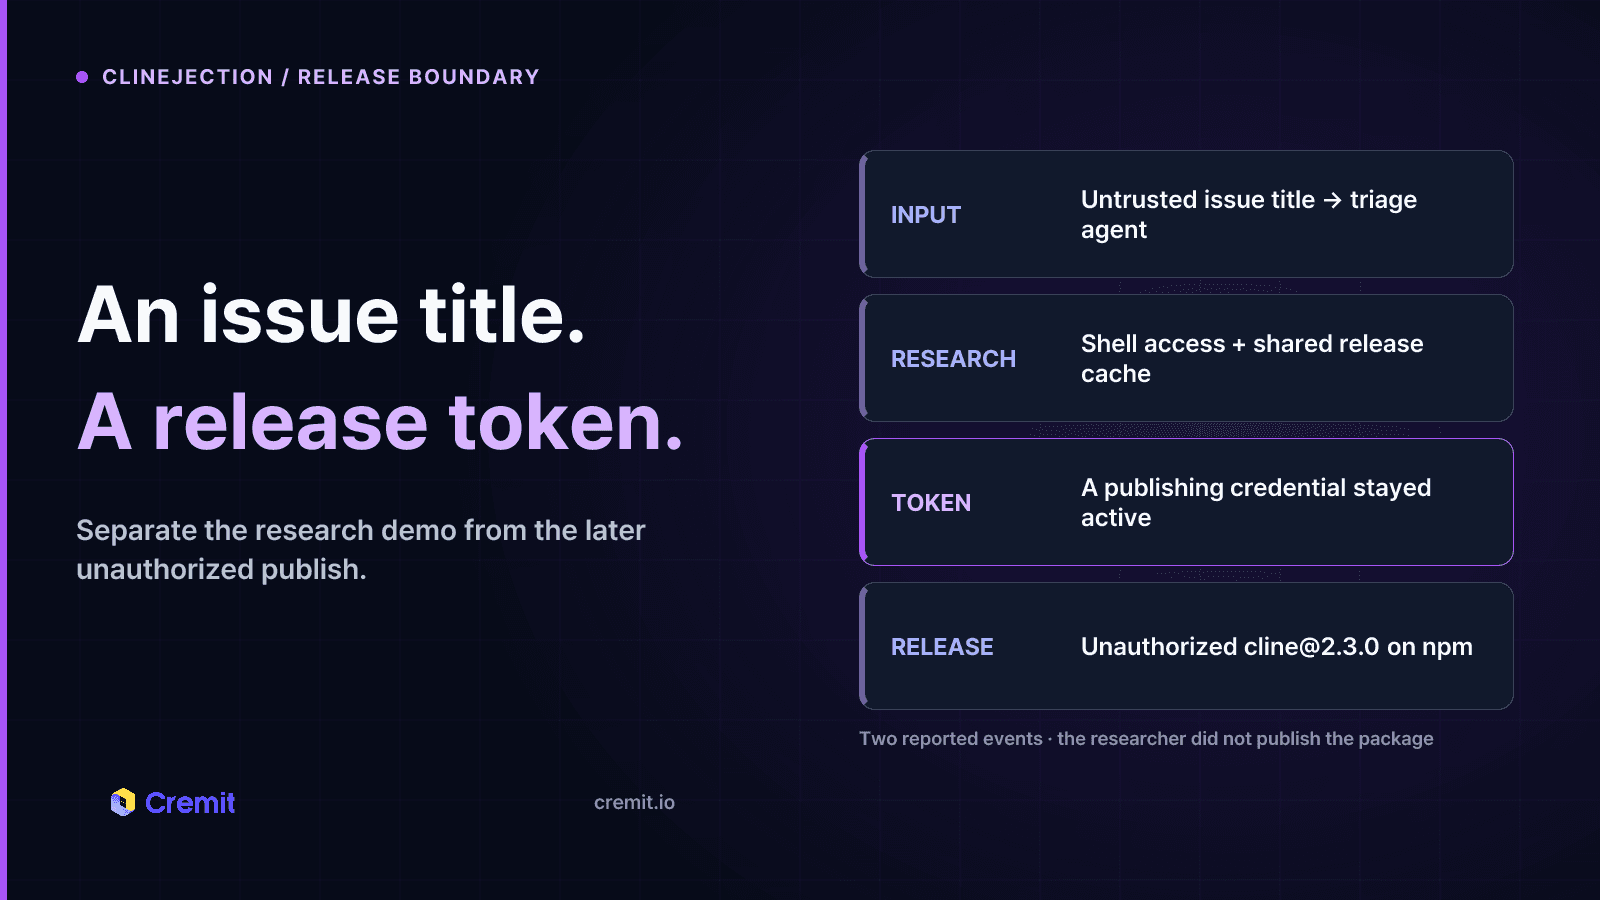
Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.
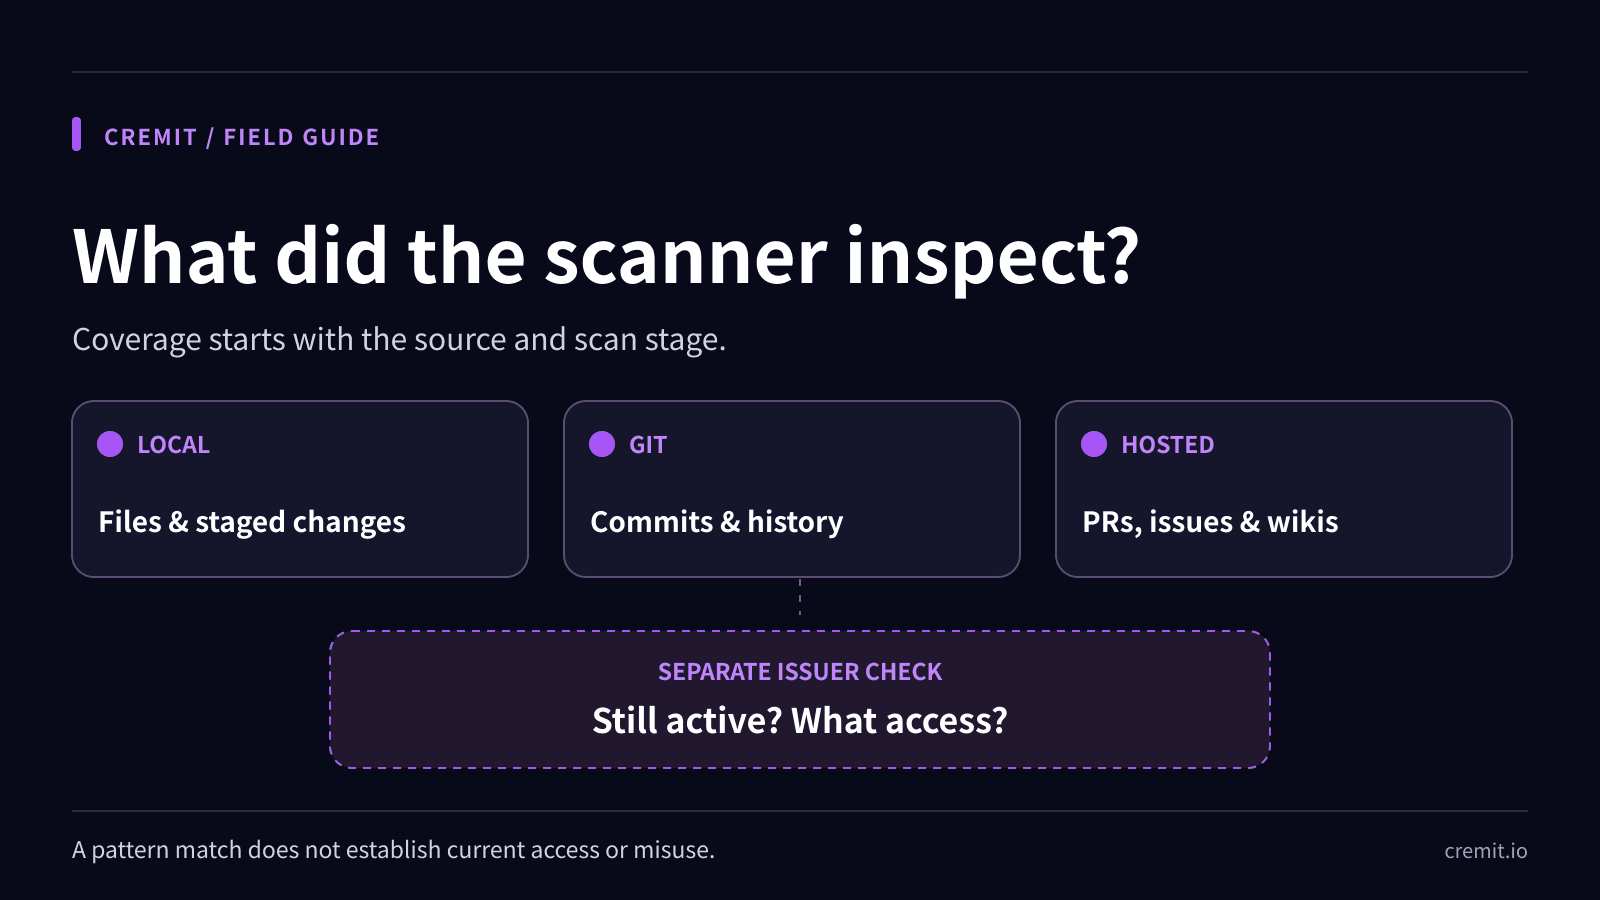
A practical guide to push protection, history scans, validity checks, and issuer-side response, with GitHub, GitLab, and Gitleaks source links.
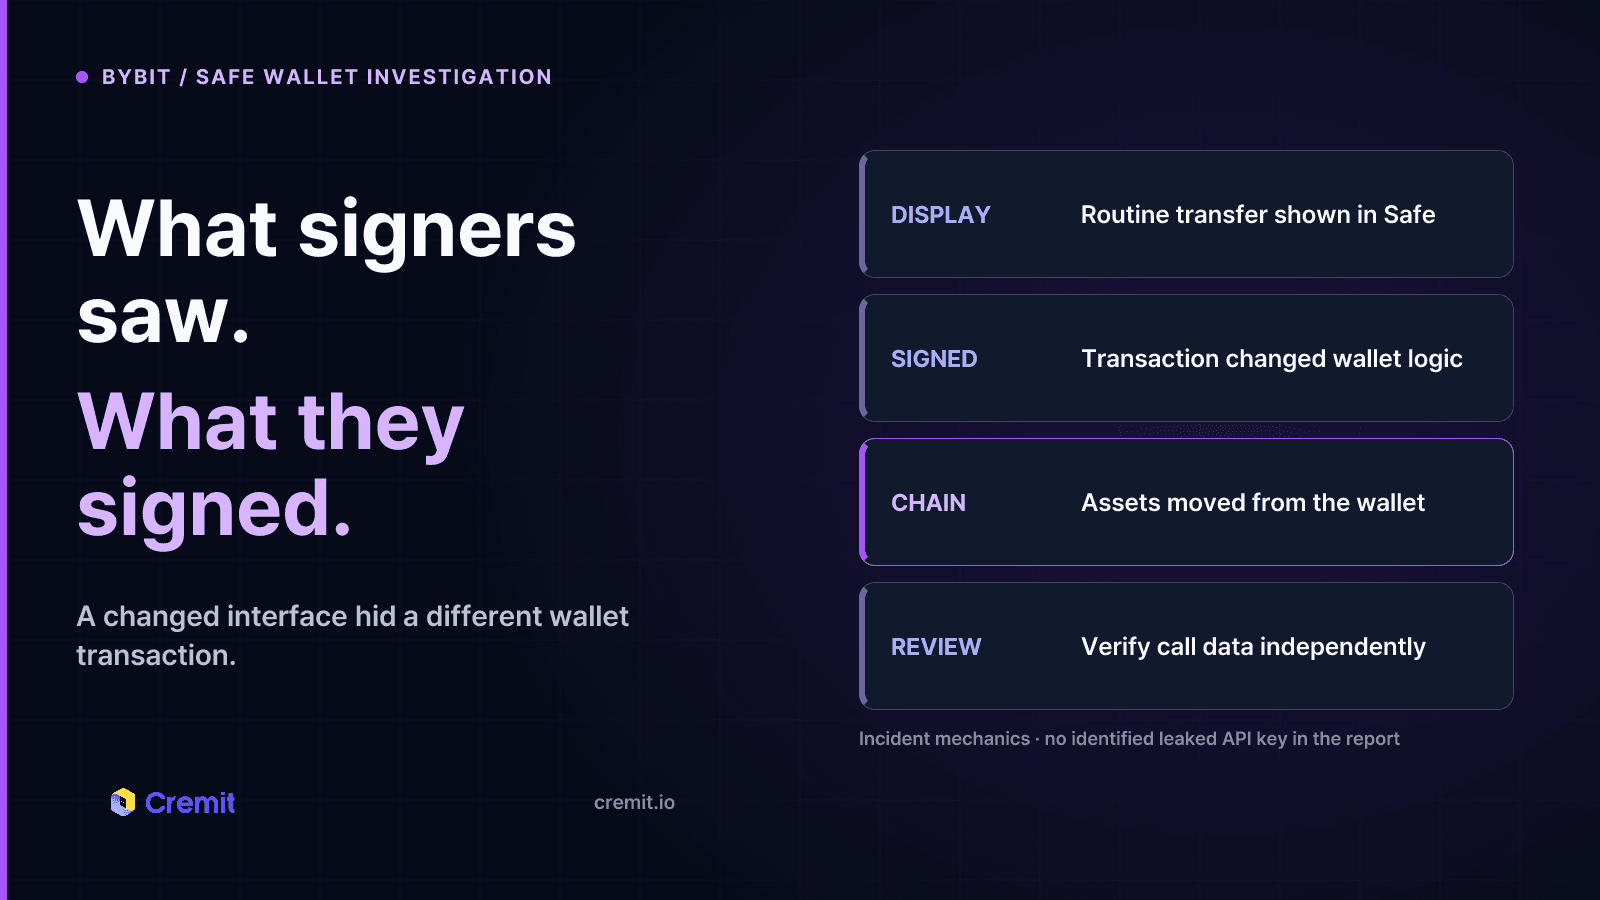
The February 2025 theft involved a compromised Safe developer and a manipulated transaction interface. Here is what investigators confirmed and what remains unknown.
A public leak, a valid key, and evidence of misuse are different findings. Here is how to investigate each without claiming a sale you cannot prove.
A short monthly brief on credential security from Cremit.