Mar 25, 2025
Wake-Up Call: tj-actions/changed-files Compromised NHIs
A GitHub Action used by more than 23,000 repositories was altered and its version tags retagged, leaking CI/CD secrets into build logs. The incident read as an NHI failure.

Ben Kim
Field studies, incident analyses and response guides from the Cremit research team, written from what we measured.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy
A GitHub Action used by more than 23,000 repositories was altered and its version tags retagged, leaking CI/CD secrets into build logs. The incident read as an NHI failure.
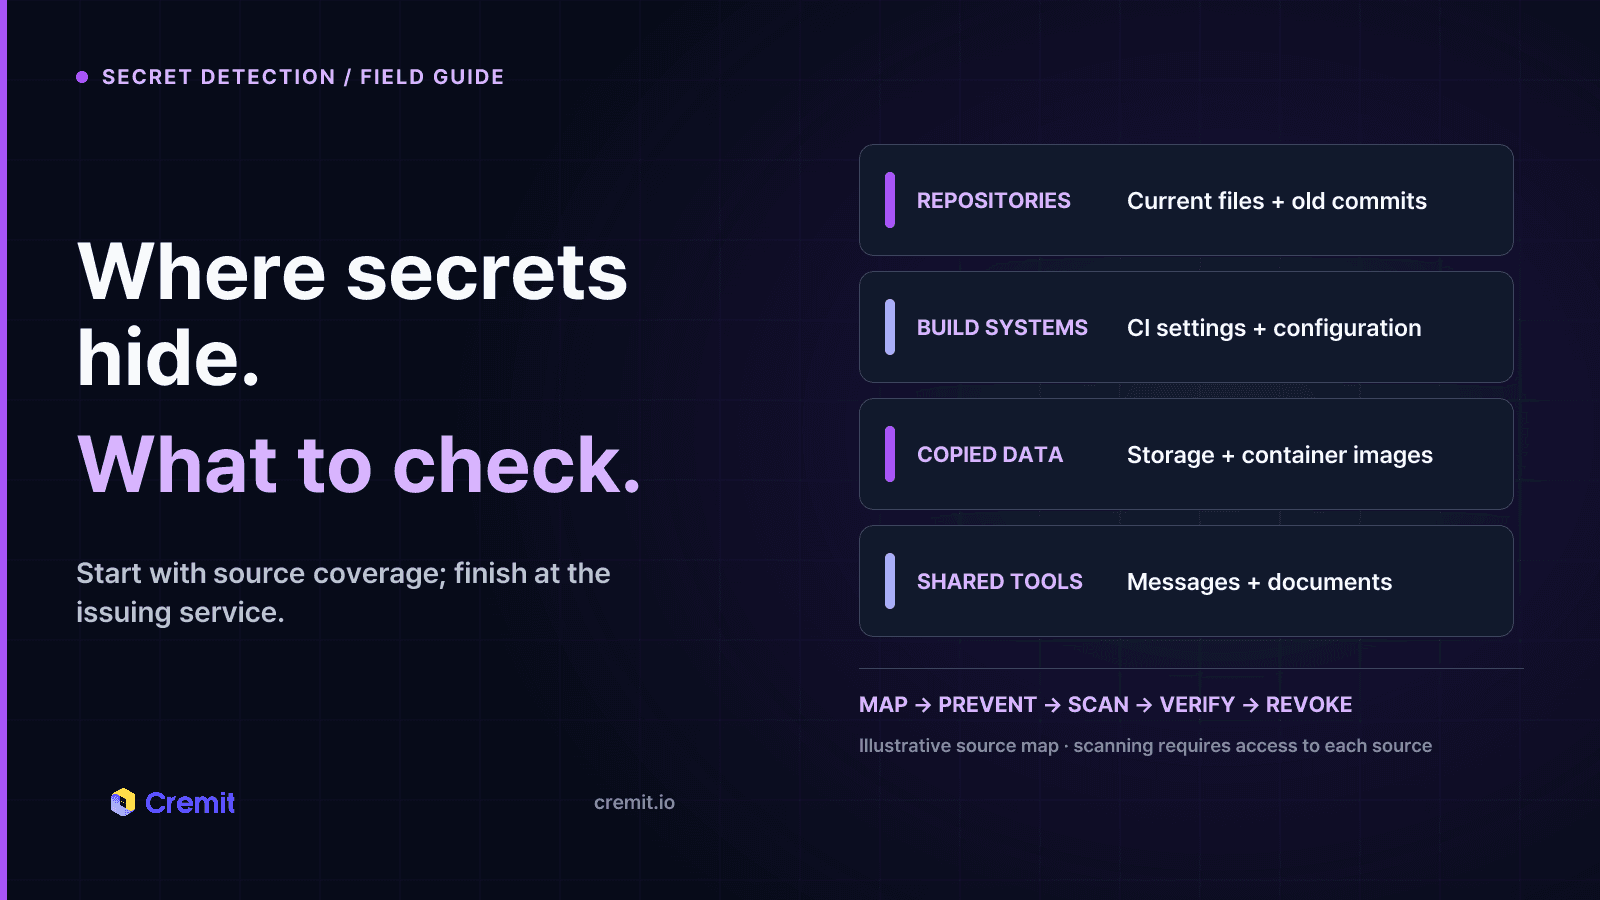
A practical workflow for preventing, finding, verifying, and replacing exposed credentials across code and shared tools.
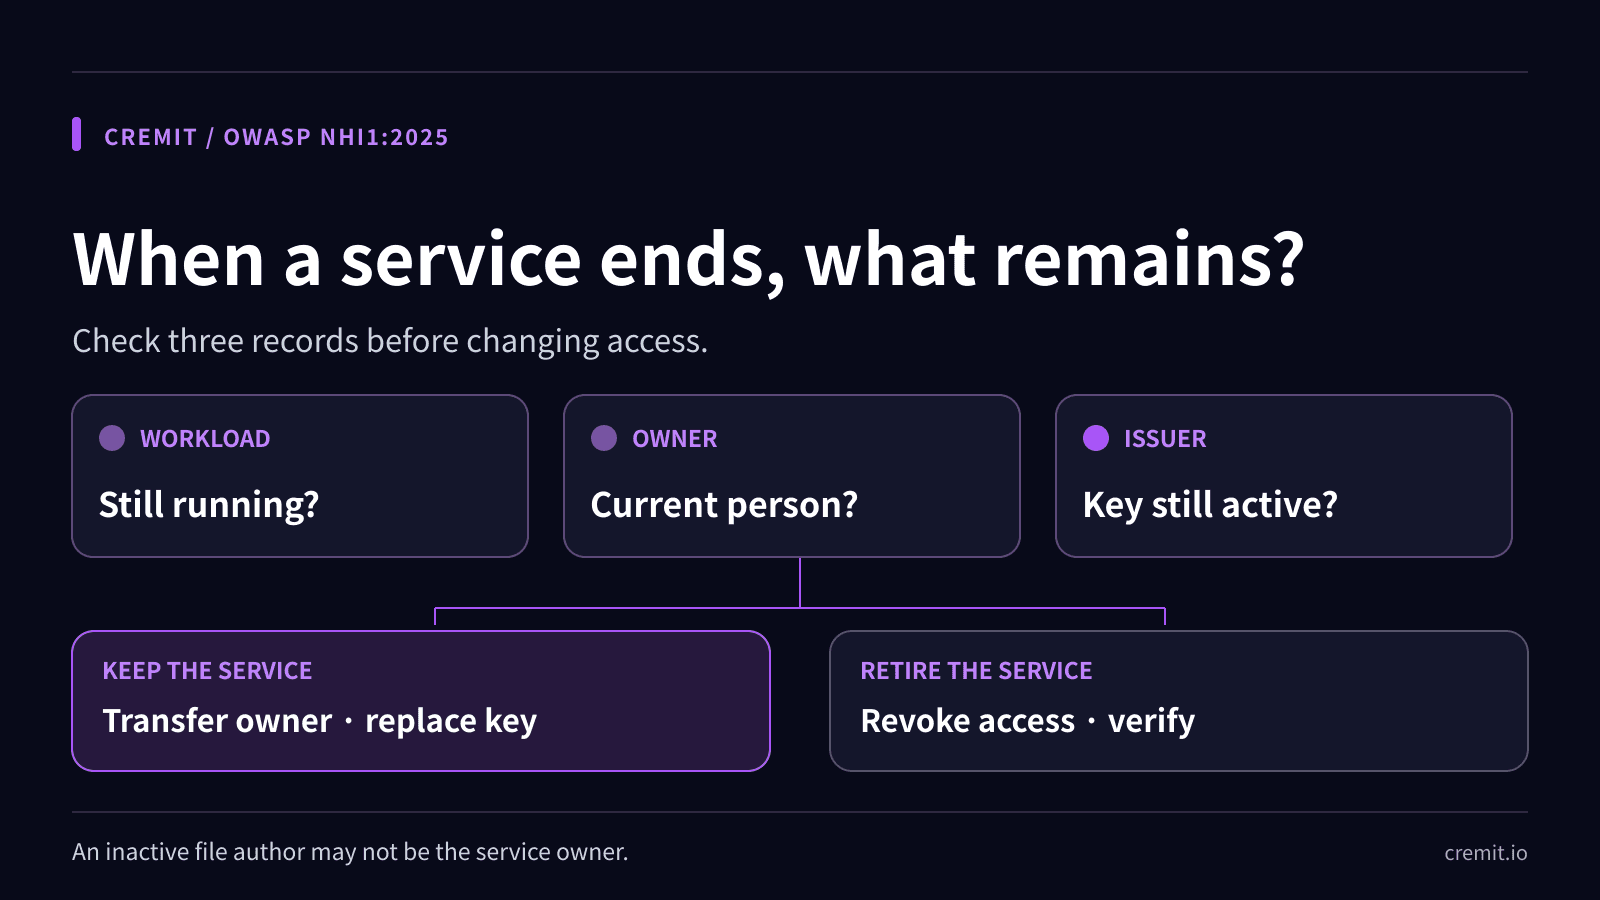
When a service ends or its owner leaves, decide what still runs, transfer responsibility or revoke access, and verify the old key no longer works.
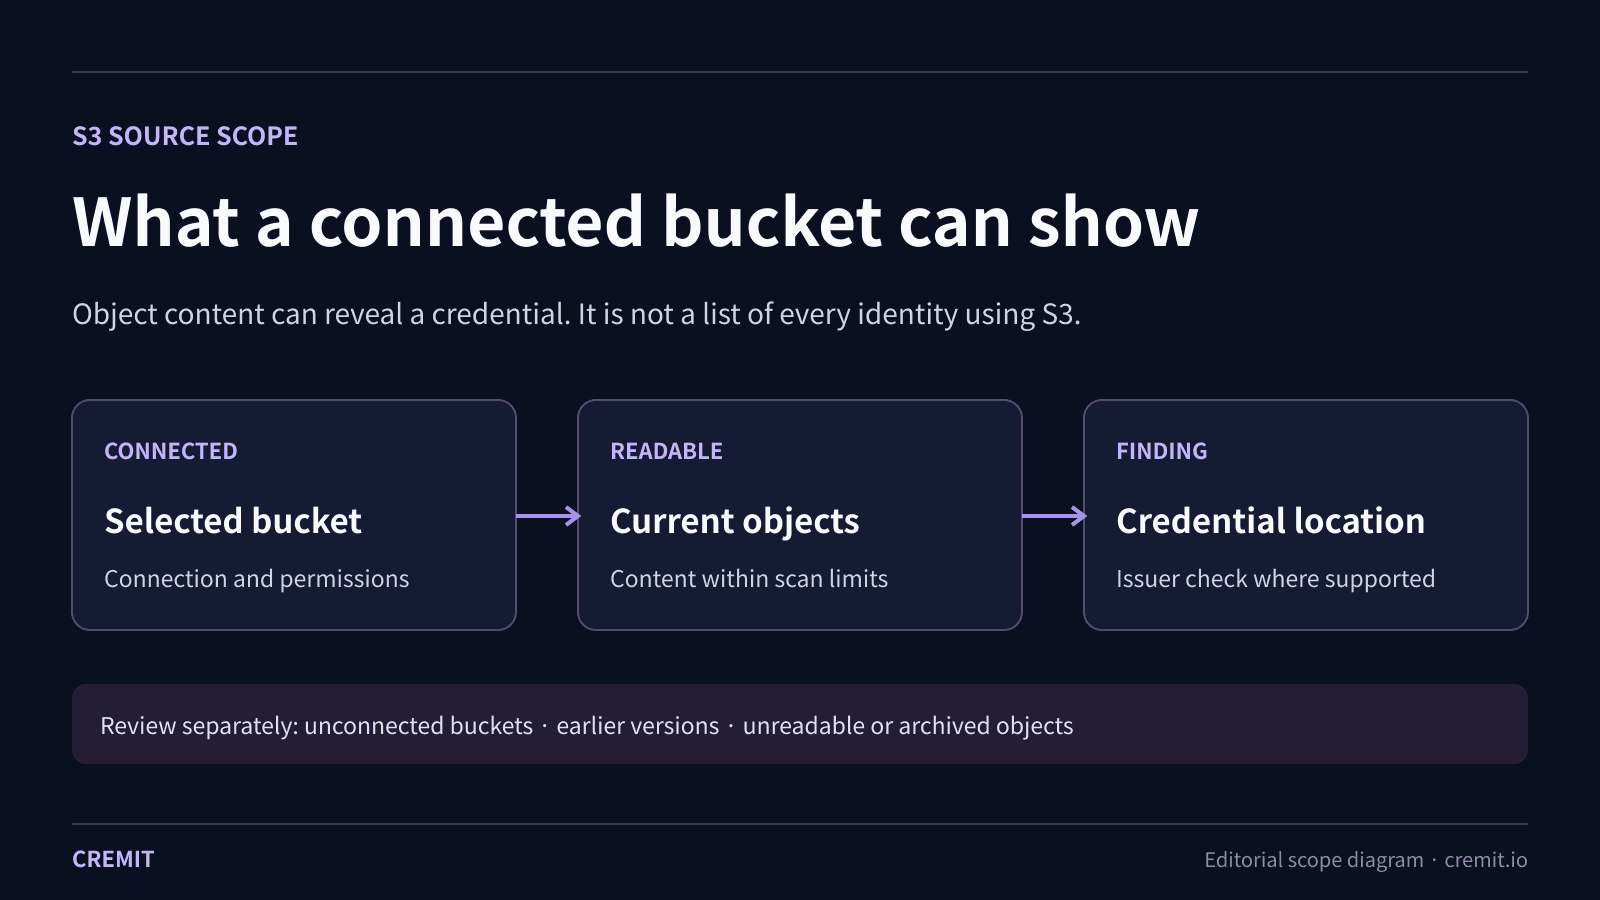
Cremit reads supported current objects in connected S3 buckets to locate credentials. Check access, skipped objects, earlier versions and the issuer separately.
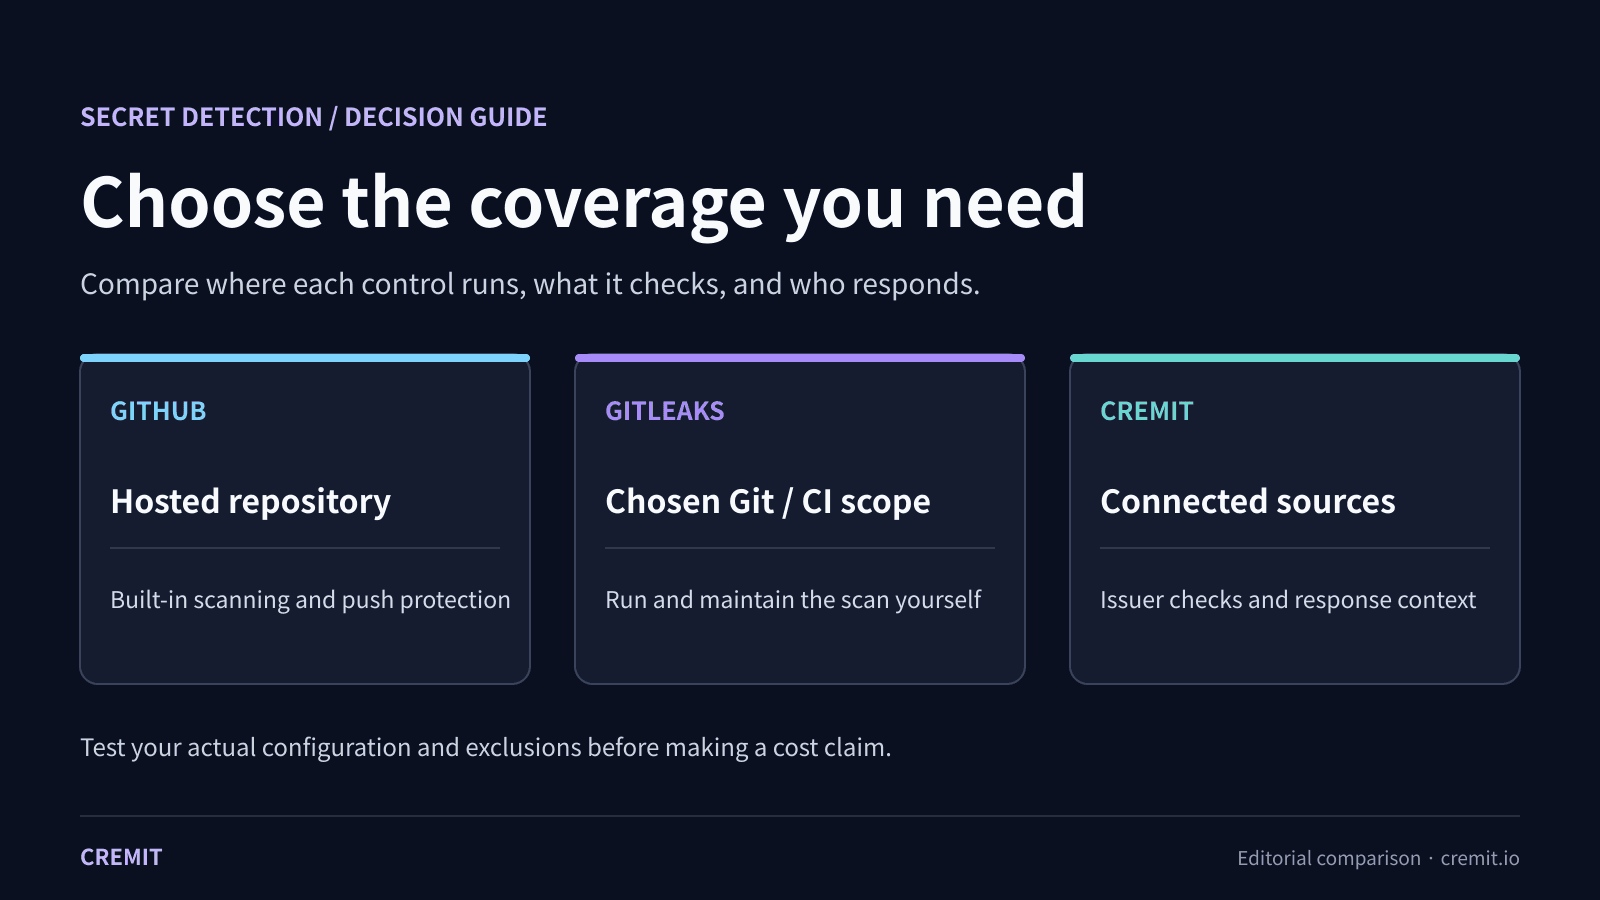
Start with the sources you need to inspect, the evidence each check returns, and who will revoke a live key. Compare GitHub, Gitleaks and Cremit by the work each covers.
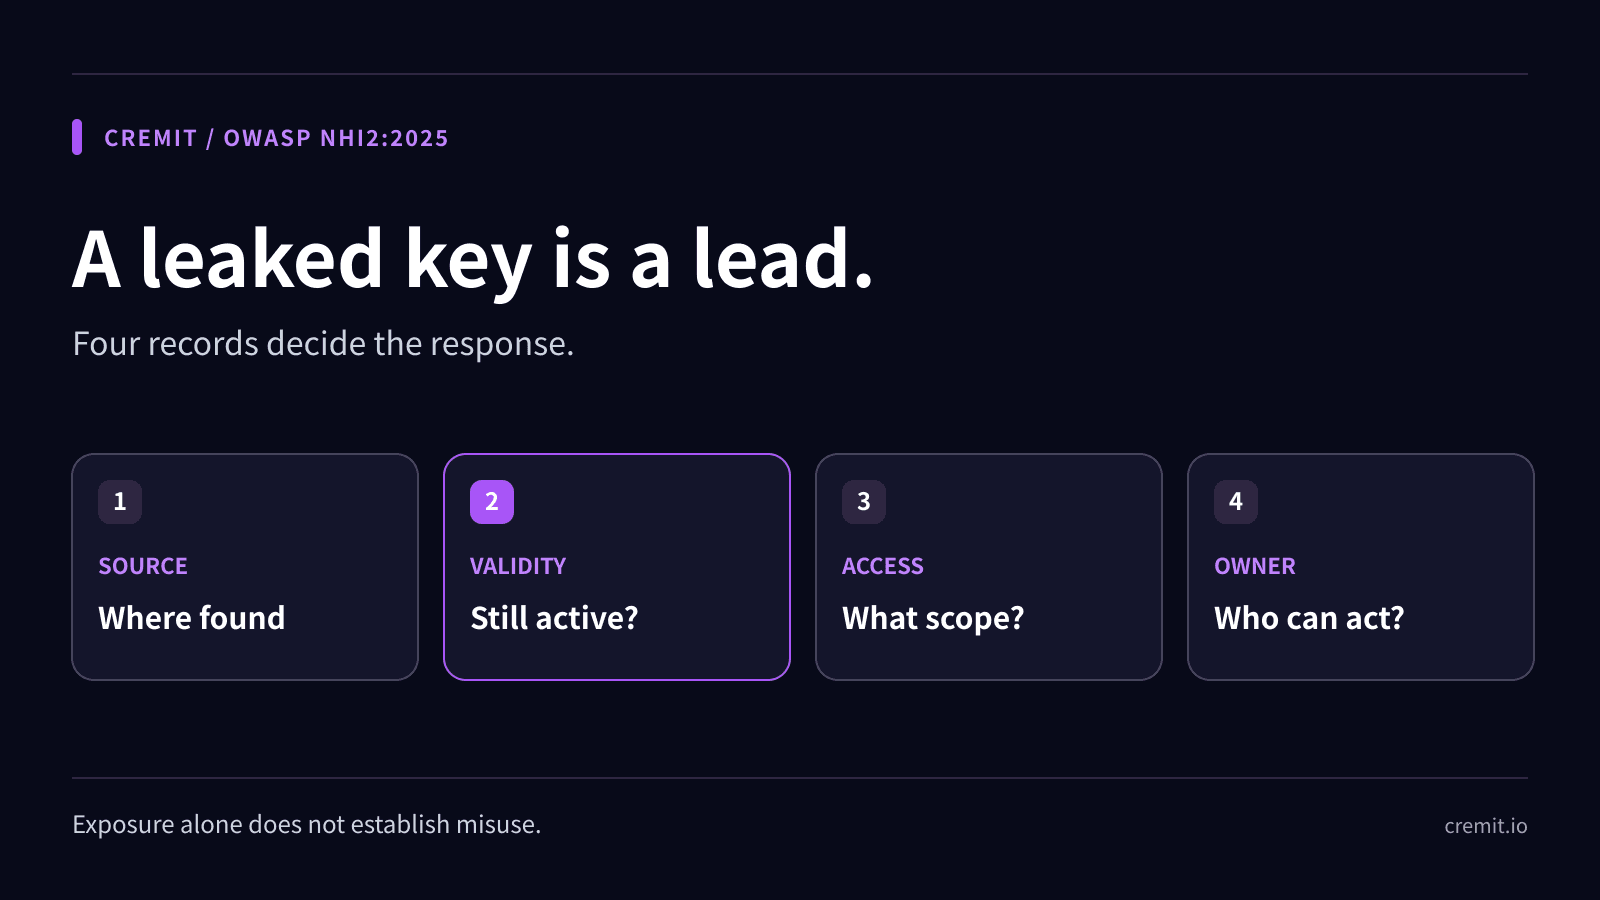
A leaked secret is a lead, not proof of misuse. Check its location, validity, access, and response owner before closing the exposure.
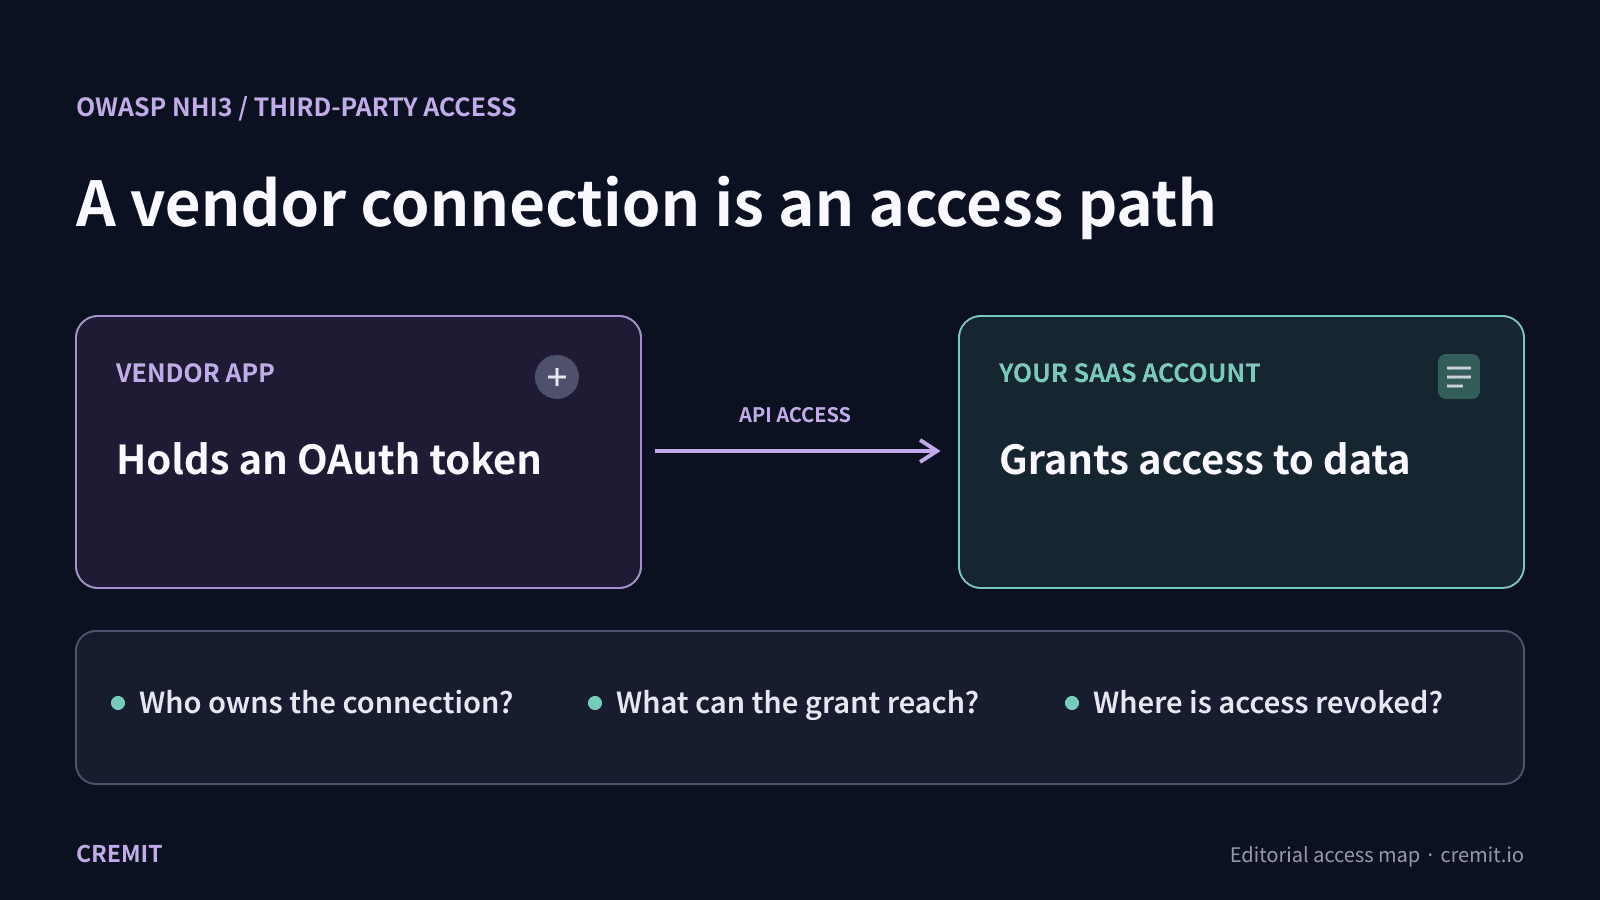
A vendor can hold a token that reaches your SaaS data. Use the Salesloft Drift incident and GitHub App controls to review the grant, owner, activity and revocation path.
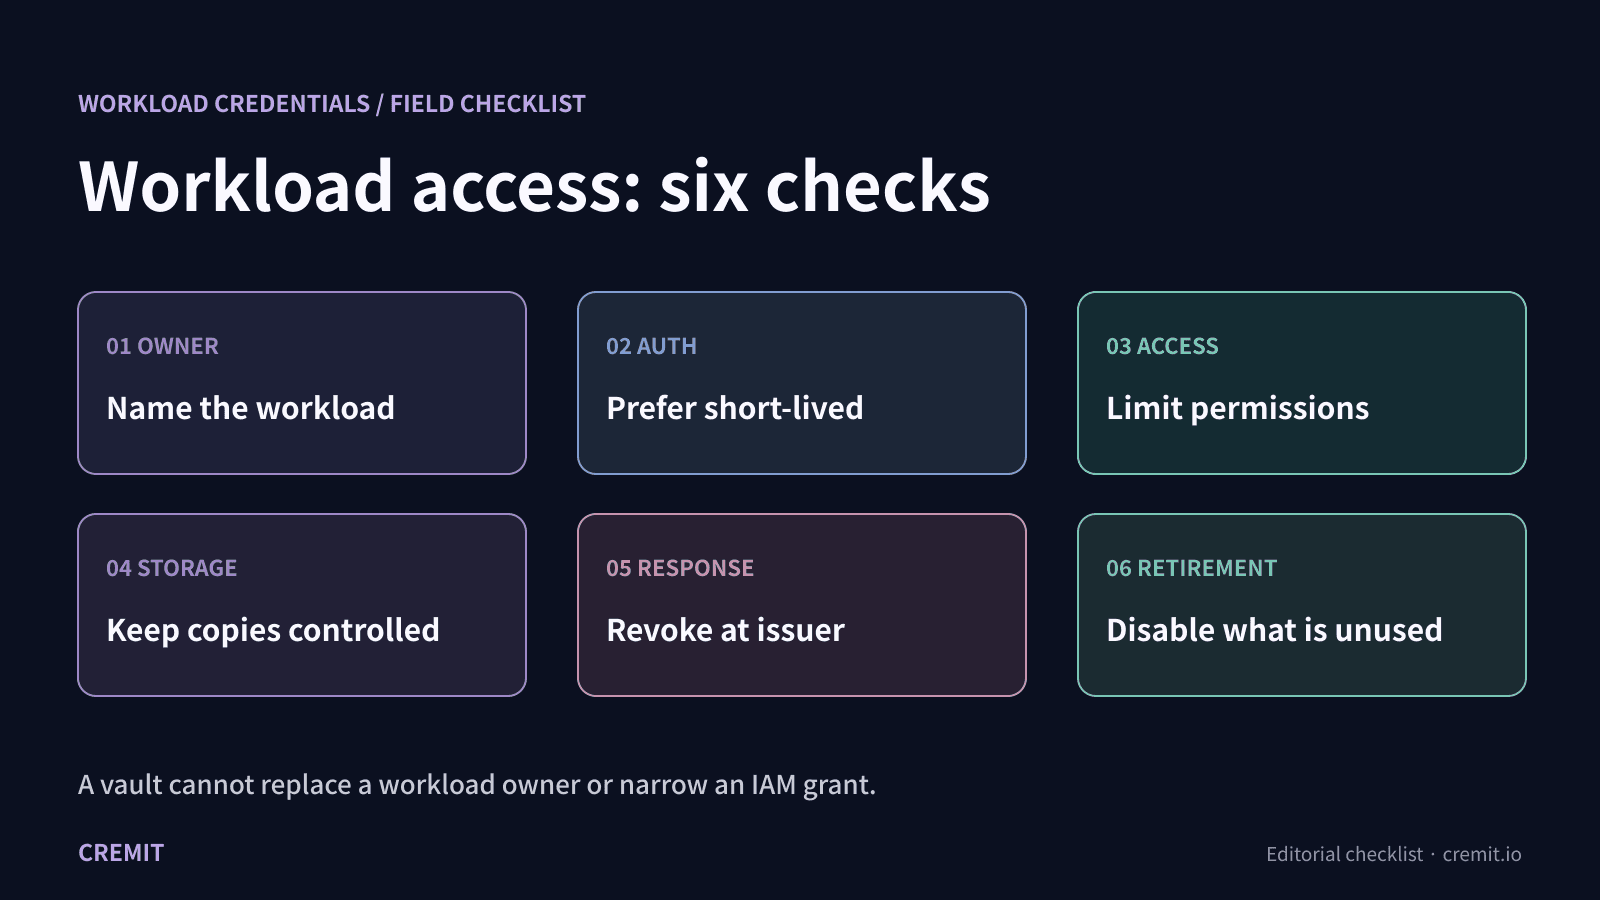
Before adding another key or vault entry, identify the workload, prefer temporary access, bound its permissions, plan exposure response and retire unused identities.
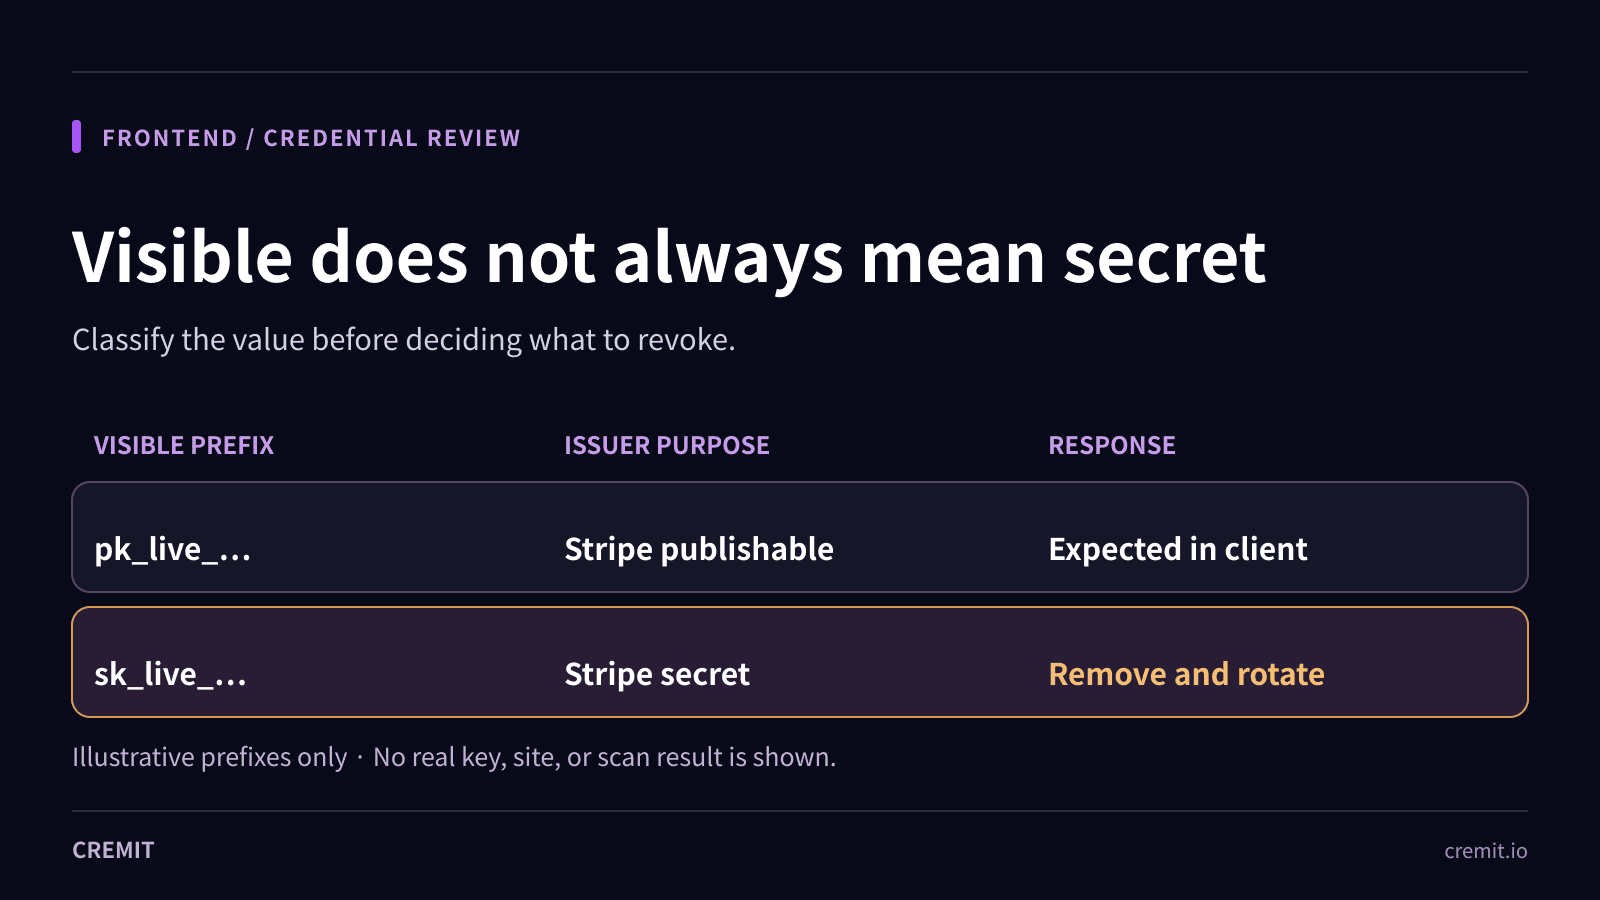
A browser-visible key may be public by design or an active secret. Use issuer key types, a documented Resend case, and build evidence to decide.
Cremit has joined the AWS SaaS Spotlight program for early-stage SaaS startups in Asia Pacific.
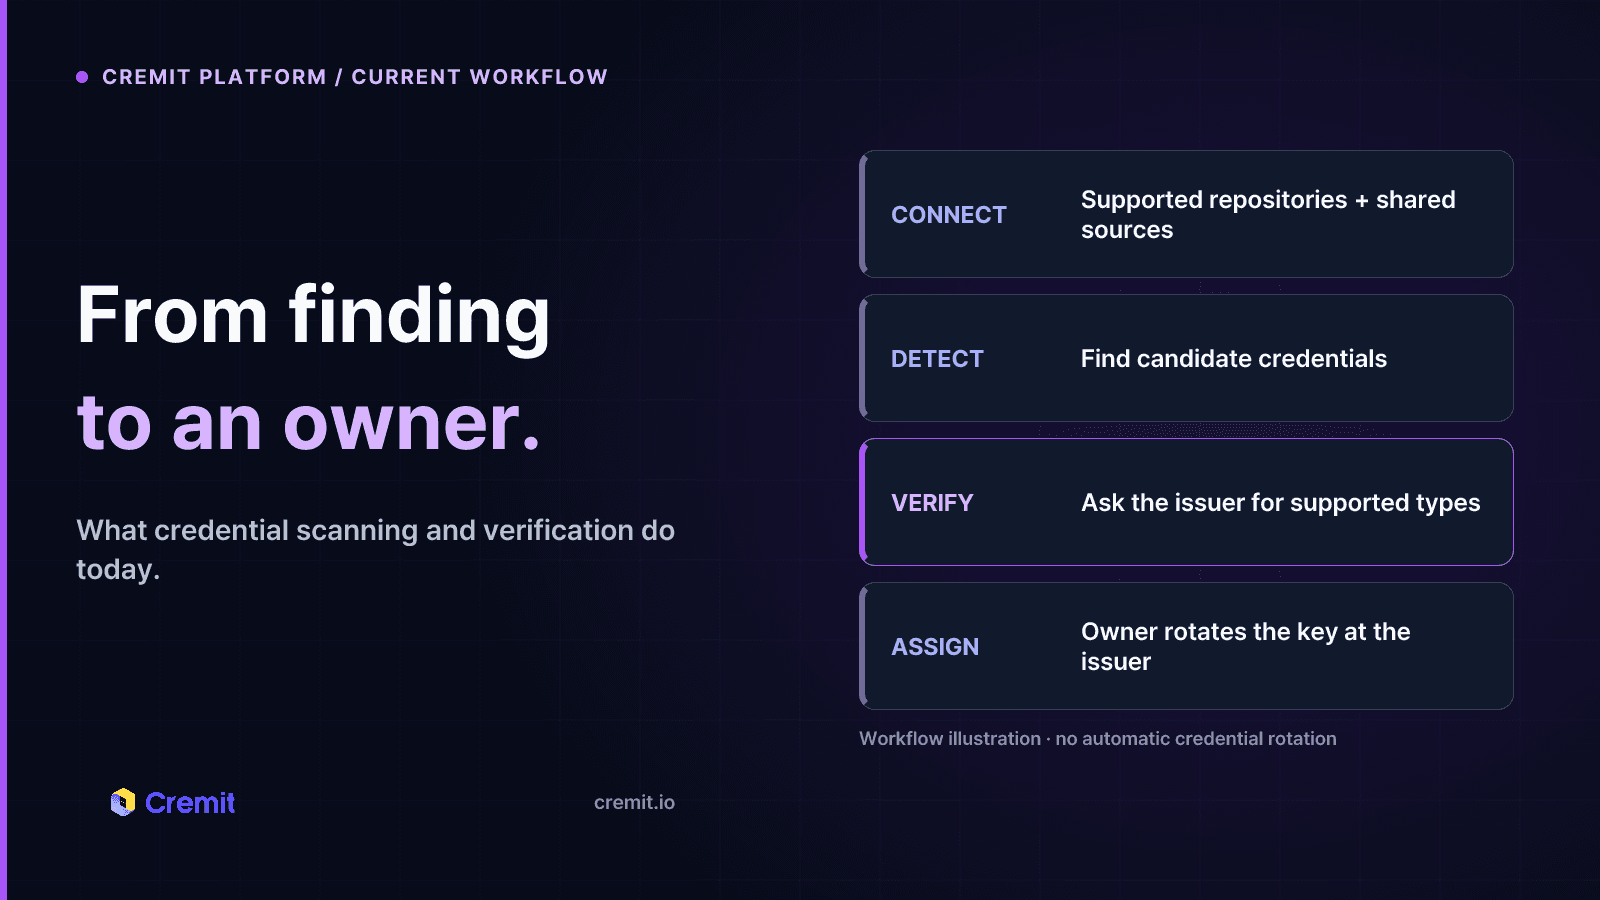
An updated guide to Cremit Platform’s scan sources, live credential checks, and remediation workflow, with current product limits.

The ten OWASP NHI risks explained through specific checks for service accounts, tokens, deployment systems, and owners.
A short monthly brief on credential security from Cremit.