Aug 28, 2025
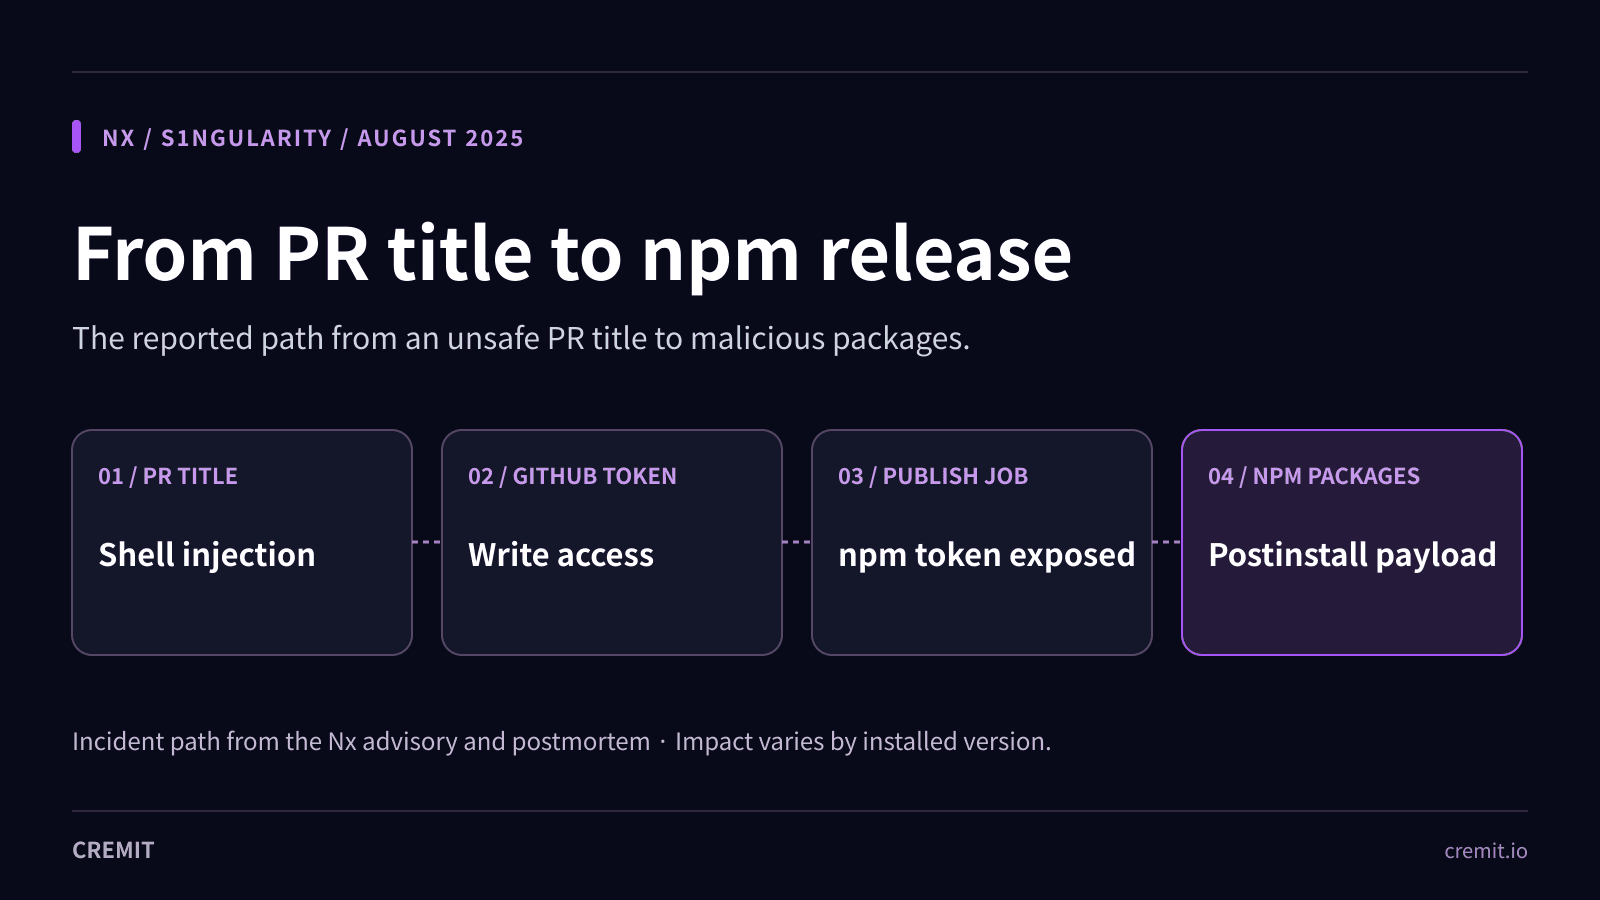
Nx S1ngularity Attack: The Workflow-to-npm Token Path
The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.

Ben Kim
Field studies, incident analyses and response guides from the Cremit research team, written from what we measured.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy
The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.
A sourced reading of the 2025 Verizon DBIR, with practical steps for credential inventory, leak prevention, and response.
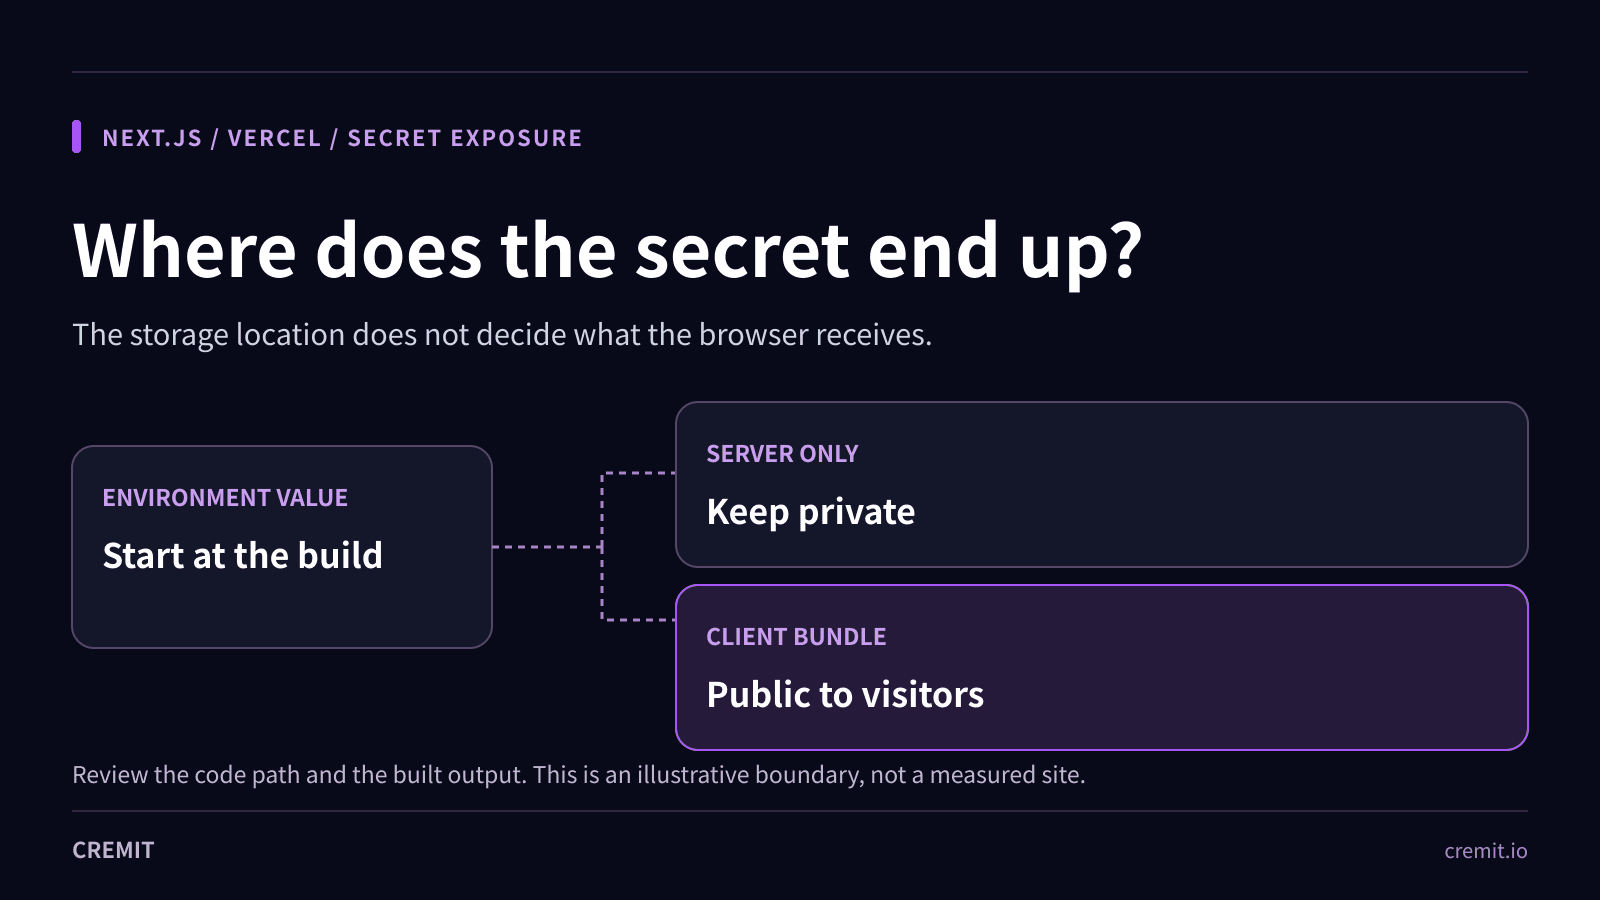
Find where Next.js puts environment values in client output, distinguish public and secret Stripe keys, and replace a key exposed in a deployment.
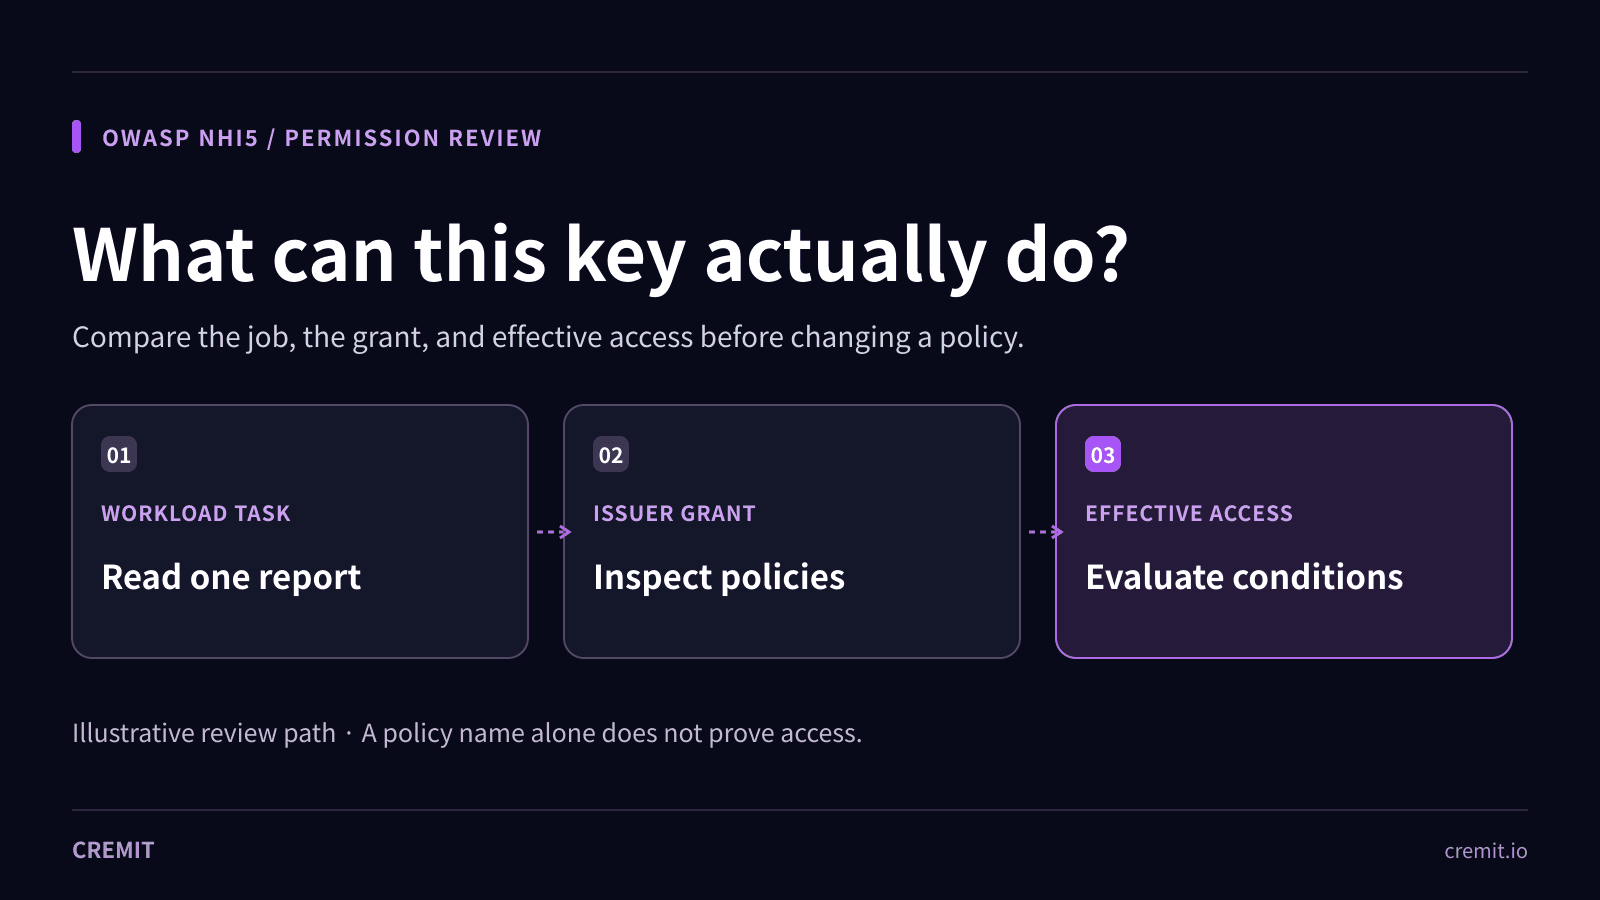
Compare workload needs, issuer grants, effective access, and observed use before reducing an NHI’s permissions.
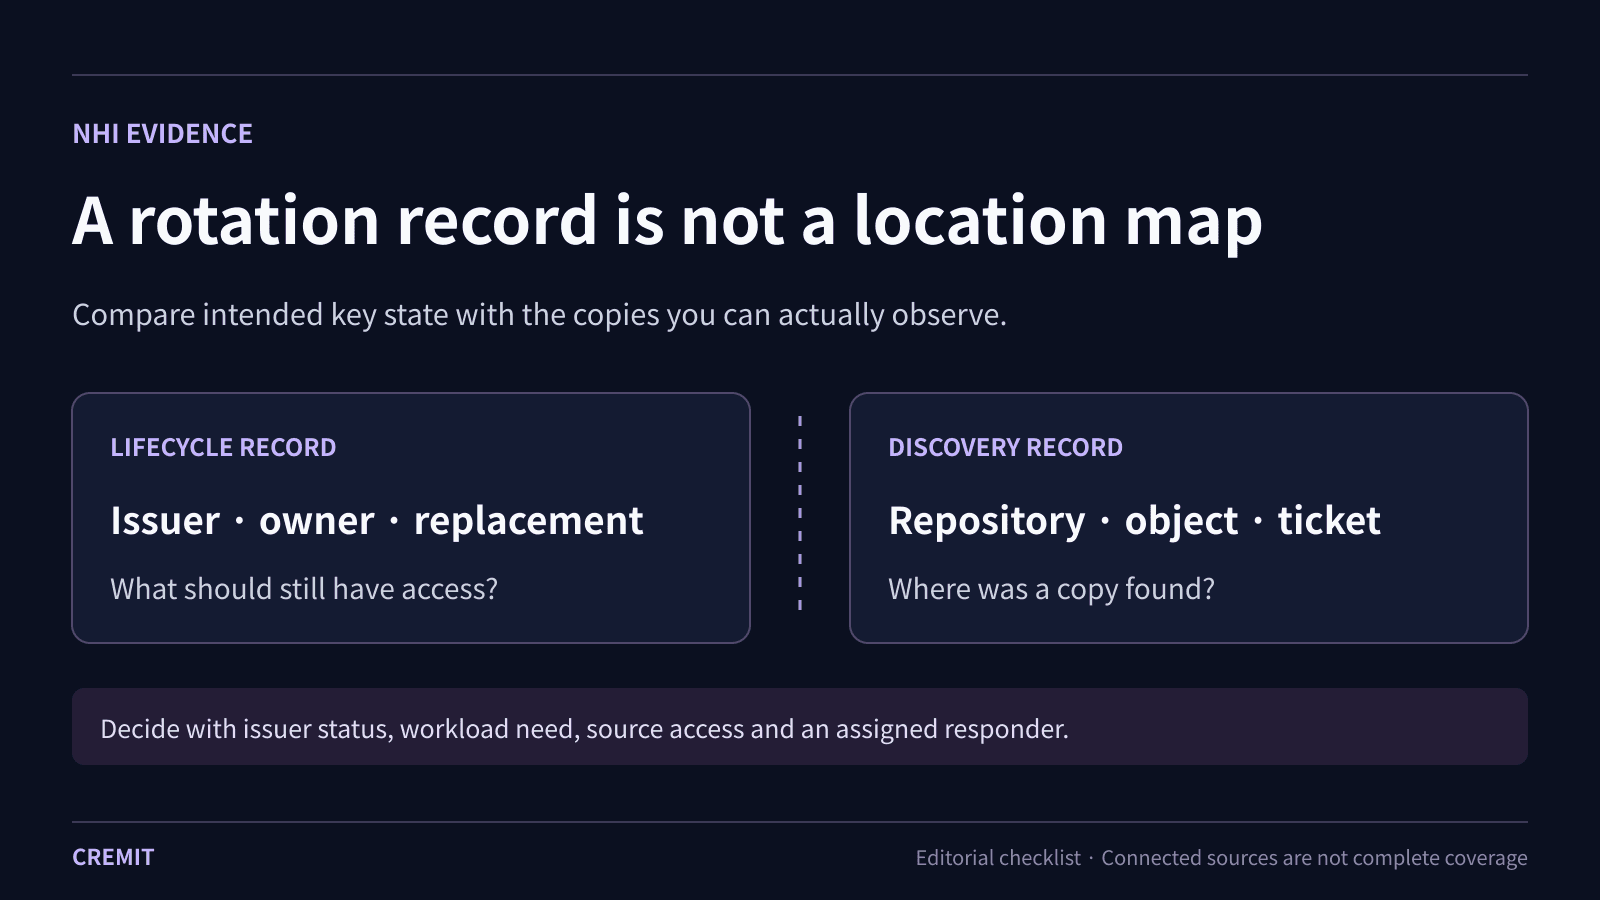
Lifecycle records show intended access. Secret findings show copies in scanned sources. Compare both before deciding who should replace a key.
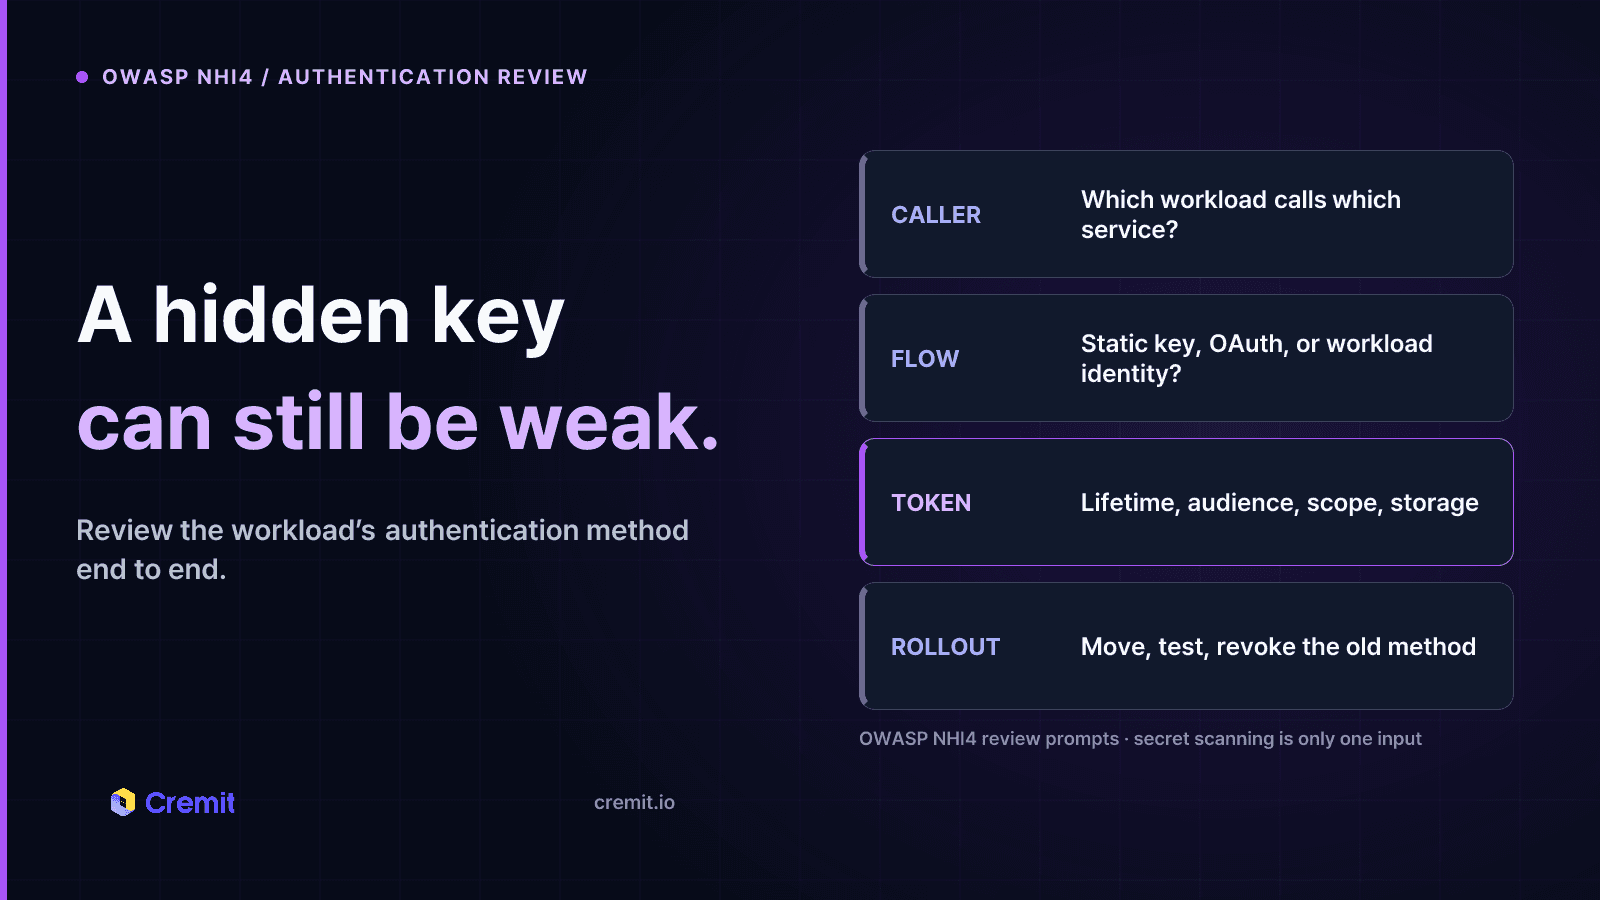
Insecure authentication is more than a leaked key. Review OAuth flows, static credentials, token scope, and the rollout path for safer workload access.
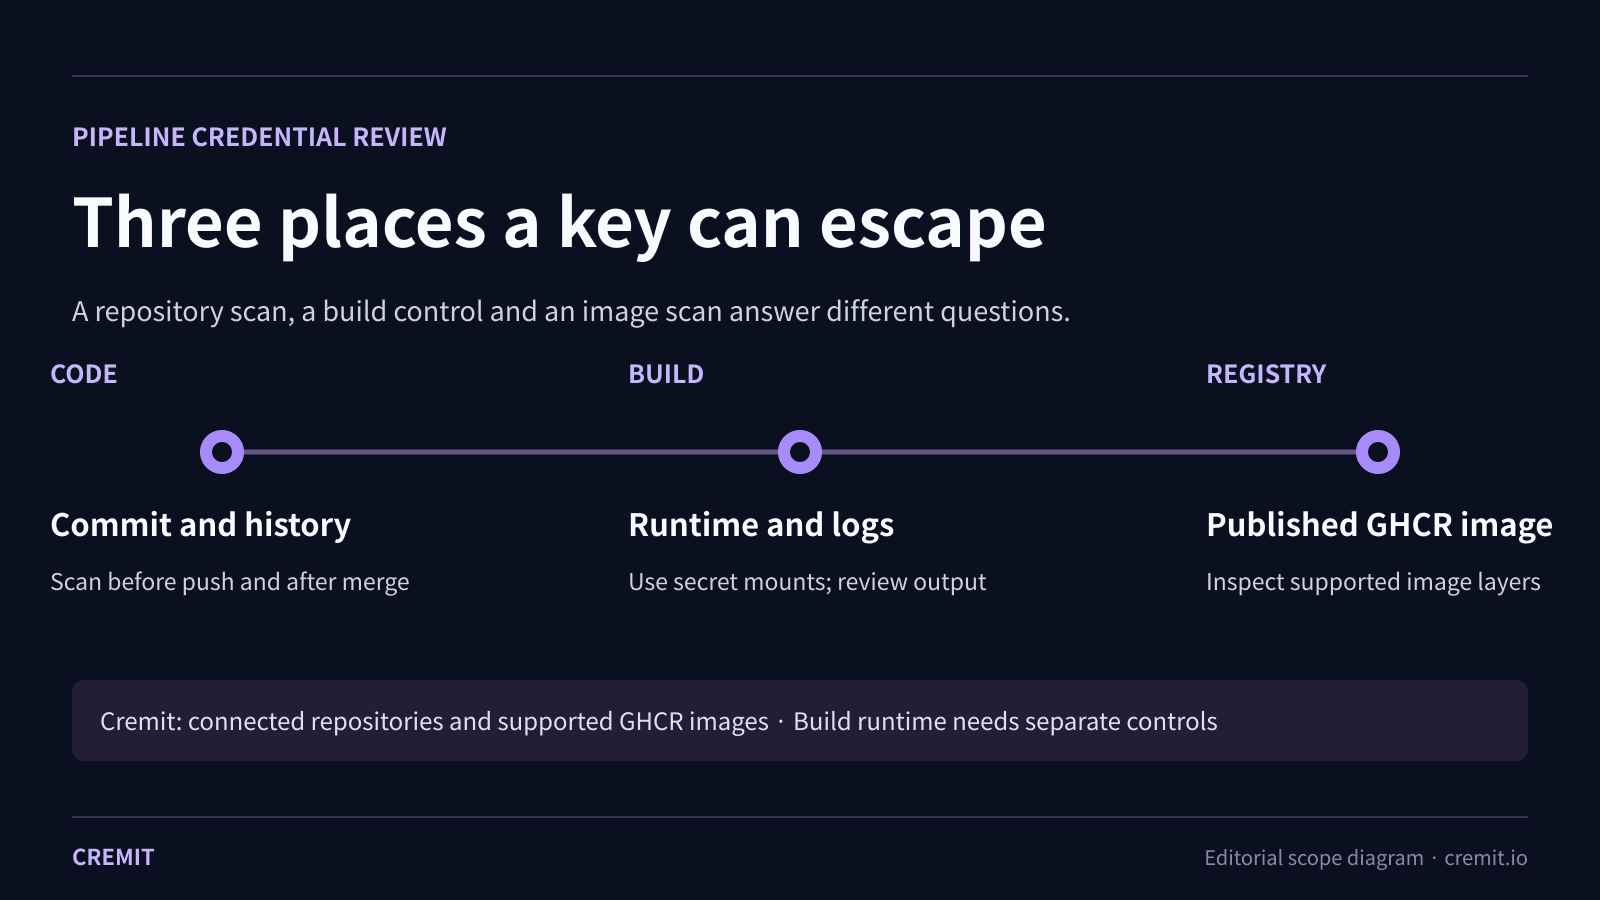
A key can land in Git history, build output or a published image. Use a different check at each boundary and verify any exposure at its issuer.
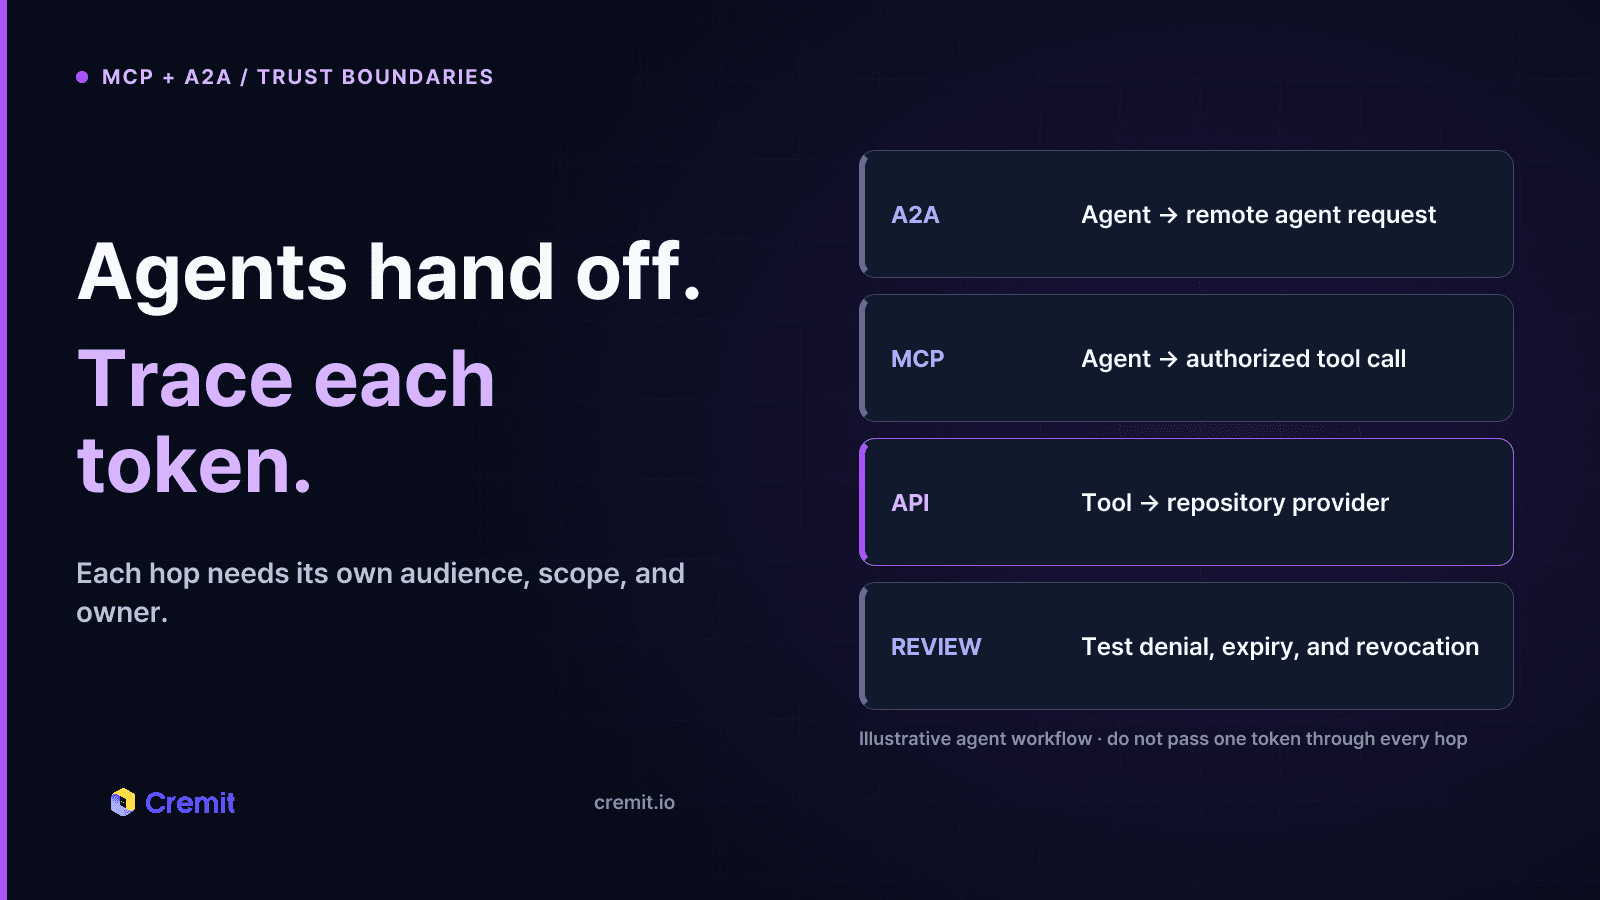
MCP connects agents to tools; A2A connects agents to each other. Map authentication, token scope, and exposed credentials at every hop.
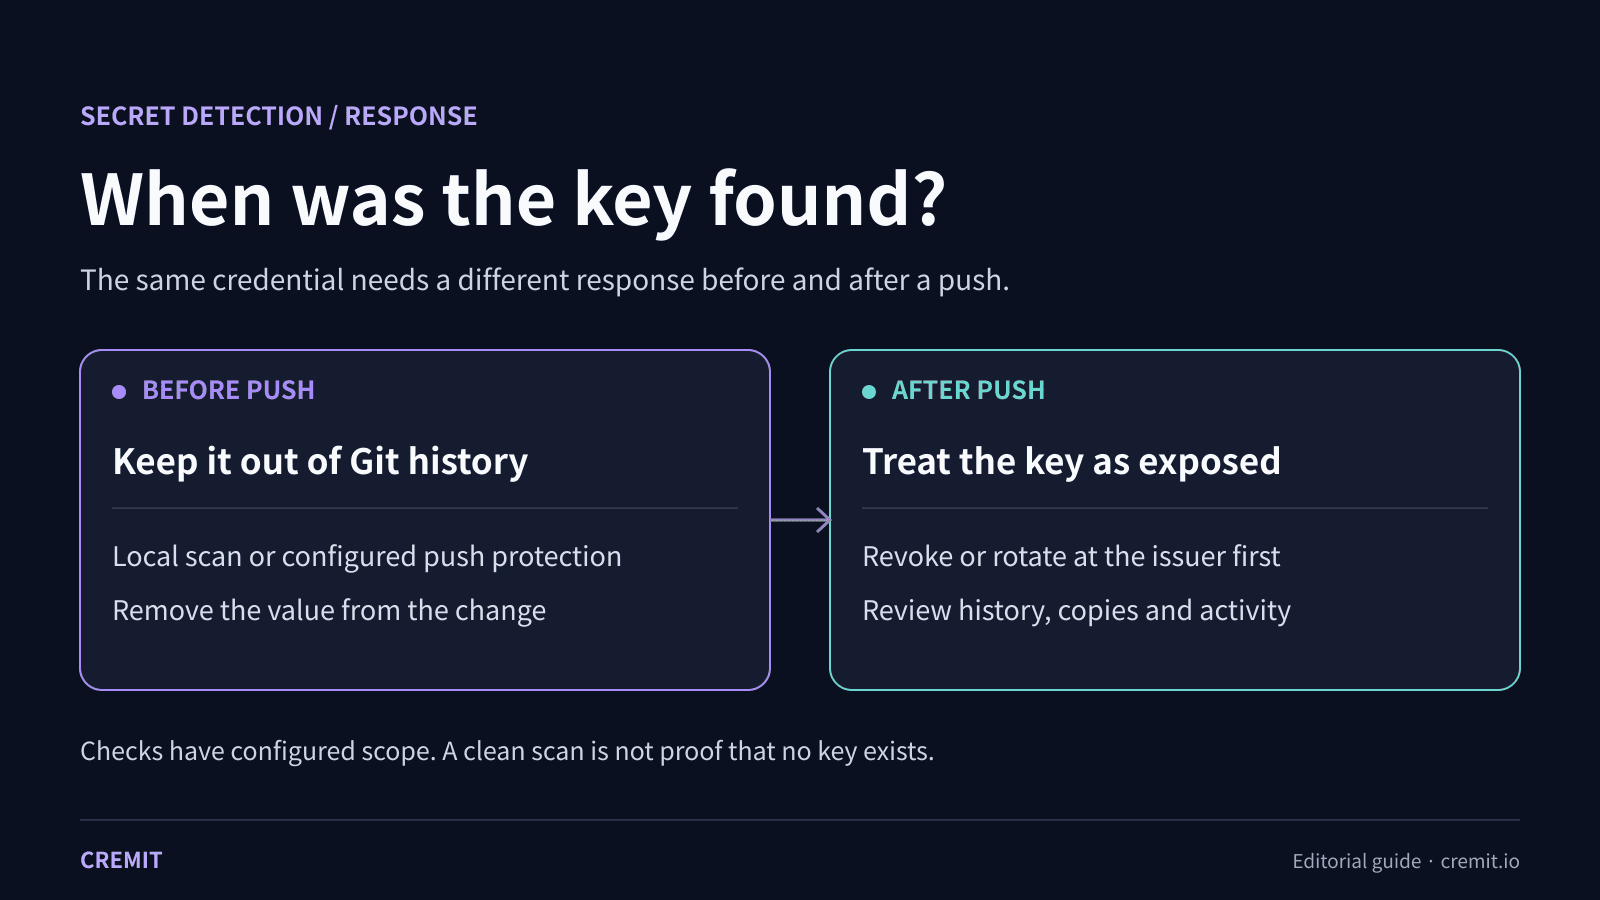
A key caught before push can be removed from the change. A key found afterward needs issuer-side revocation or rotation, even if the commit is deleted.
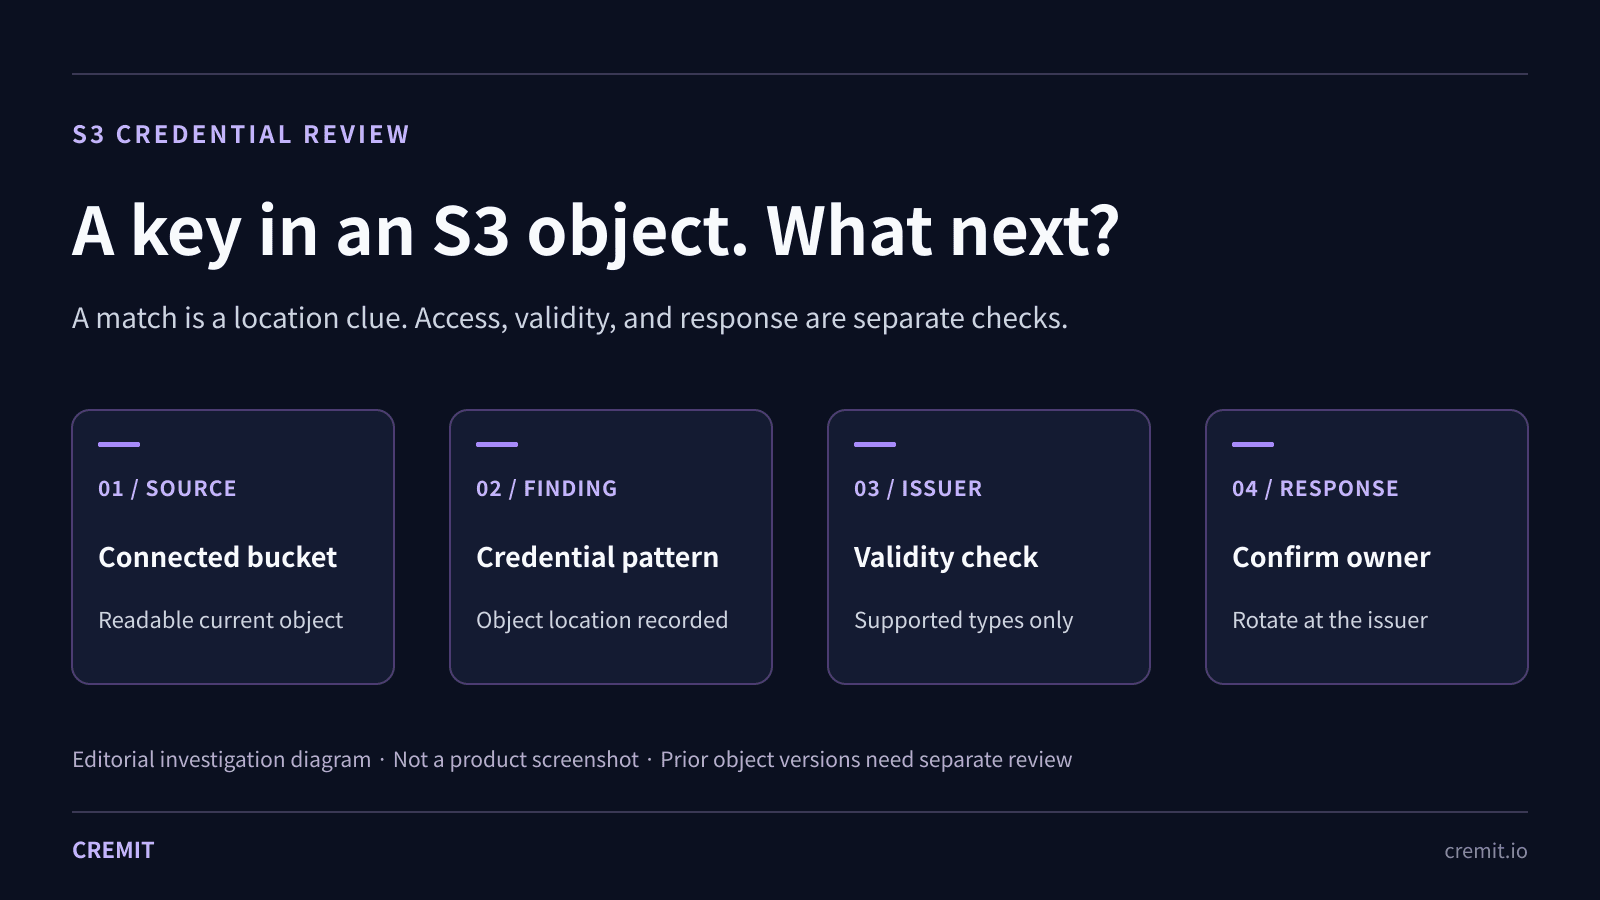
A key-shaped string in S3 does not prove public access, a live credential, or misuse. Check the object, issuer, scan coverage, and earlier versions.
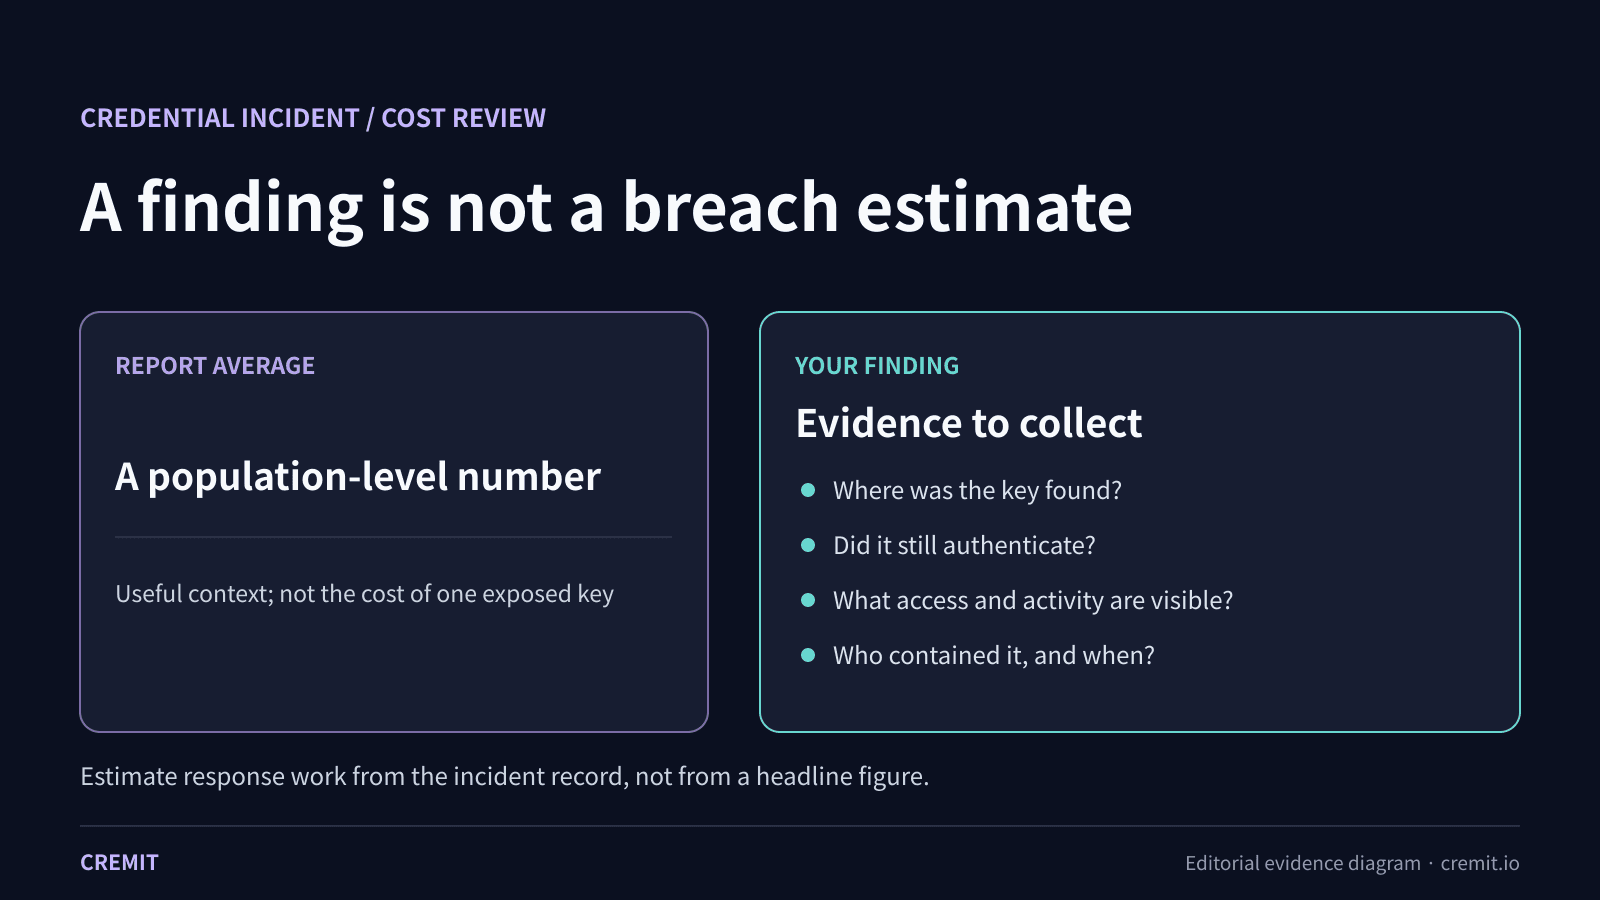
A breach-cost average cannot price one exposed credential. Record the key’s source, issuer status, available access and activity evidence, and response work before estimating impact.
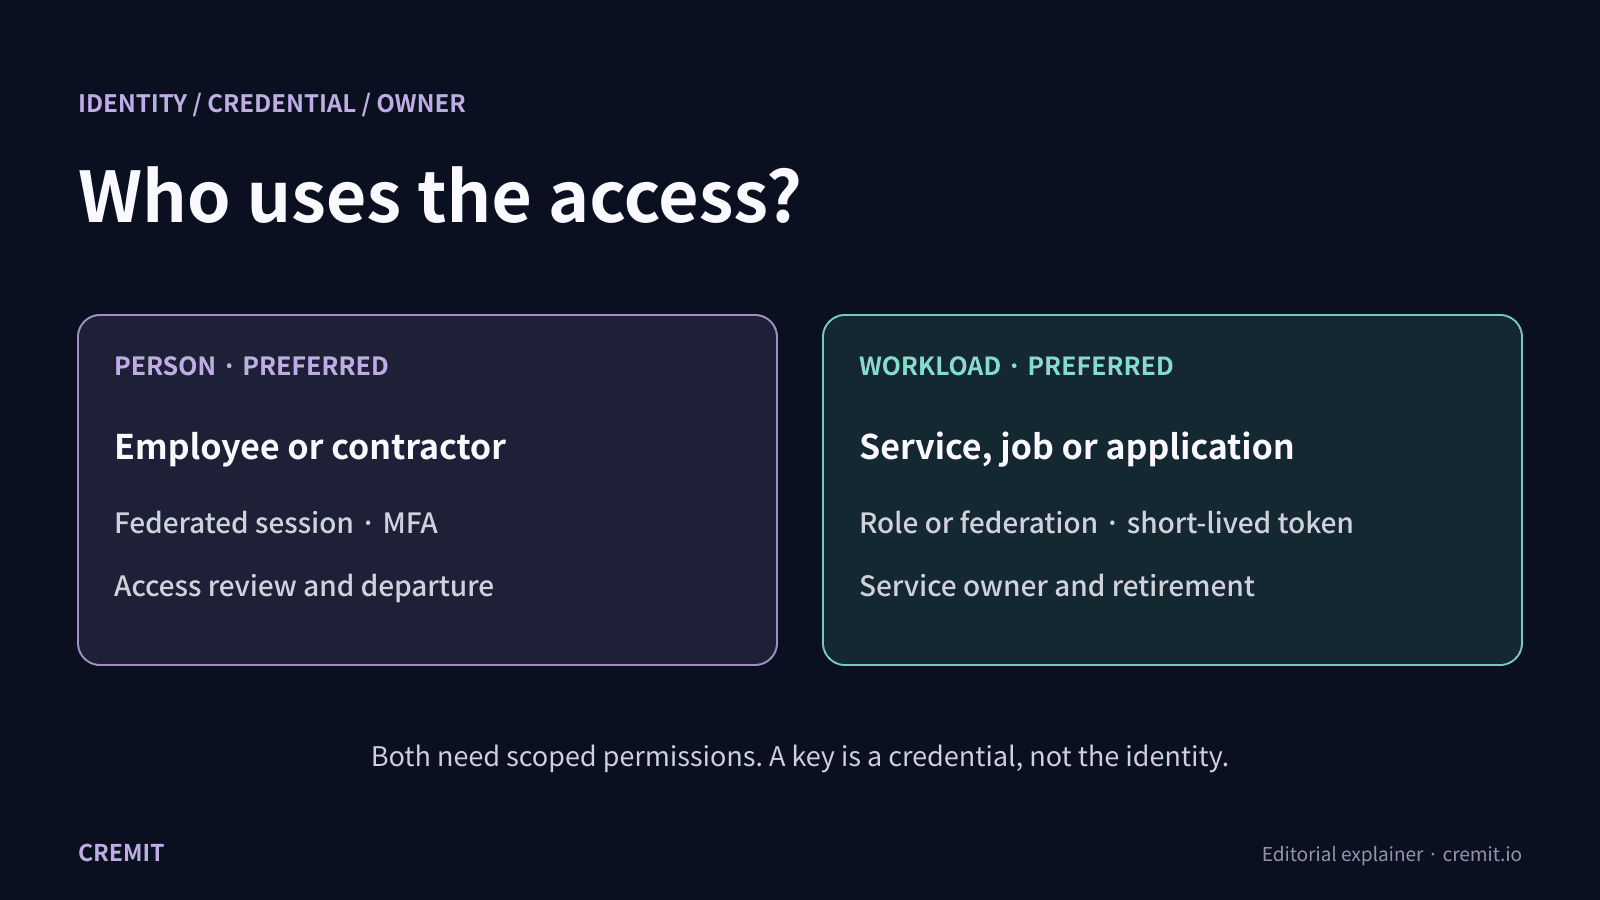
A person and a workload can both have privileged access. Compare the principal, credential, owner and offboarding record you need to review each one.
A short monthly brief on credential security from Cremit.