Mar 18, 2024
DevSecOps starts with a credential your team can actually fix
A practical rollout for credential detection across repositories and collaboration tools, with clear owners and honest scan timing.

Ben Kim
Field studies, incident analyses and response guides from the Cremit research team, written from what we measured.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy
A practical rollout for credential detection across repositories and collaboration tools, with clear owners and honest scan timing.

A conversation with the team at ENlighten, a Korean energy IT platform, about how they manage credentials and secrets and what led them to Cremit.
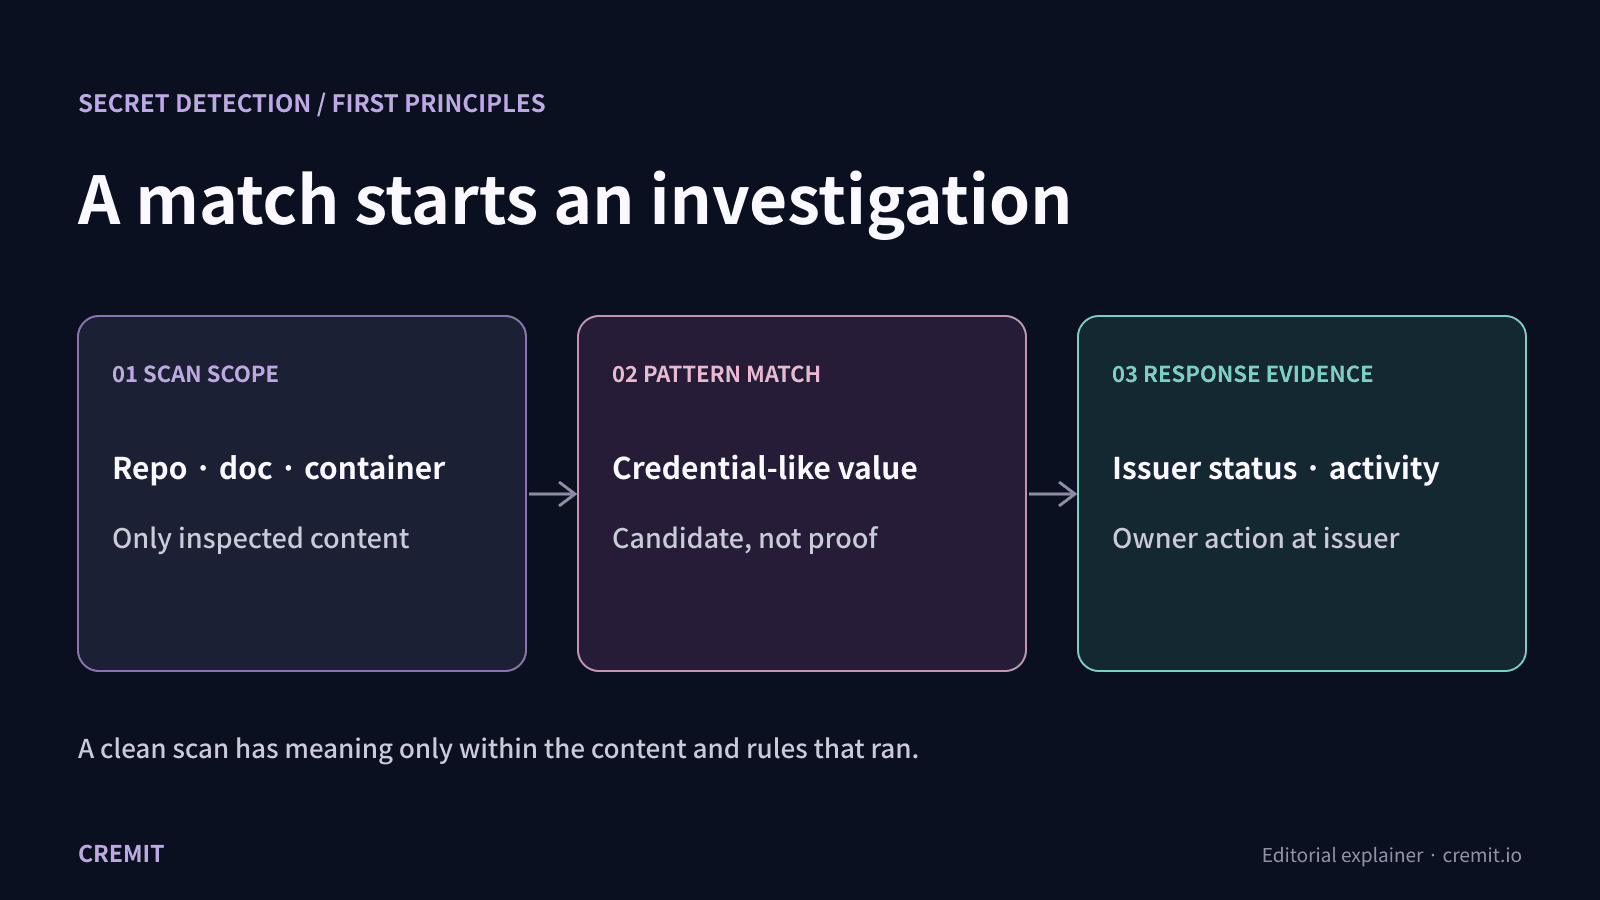
Secret detection finds possible credentials in content a tool actually inspects. Learn what a match proves, where scans run, and how to verify and contain an exposed key.
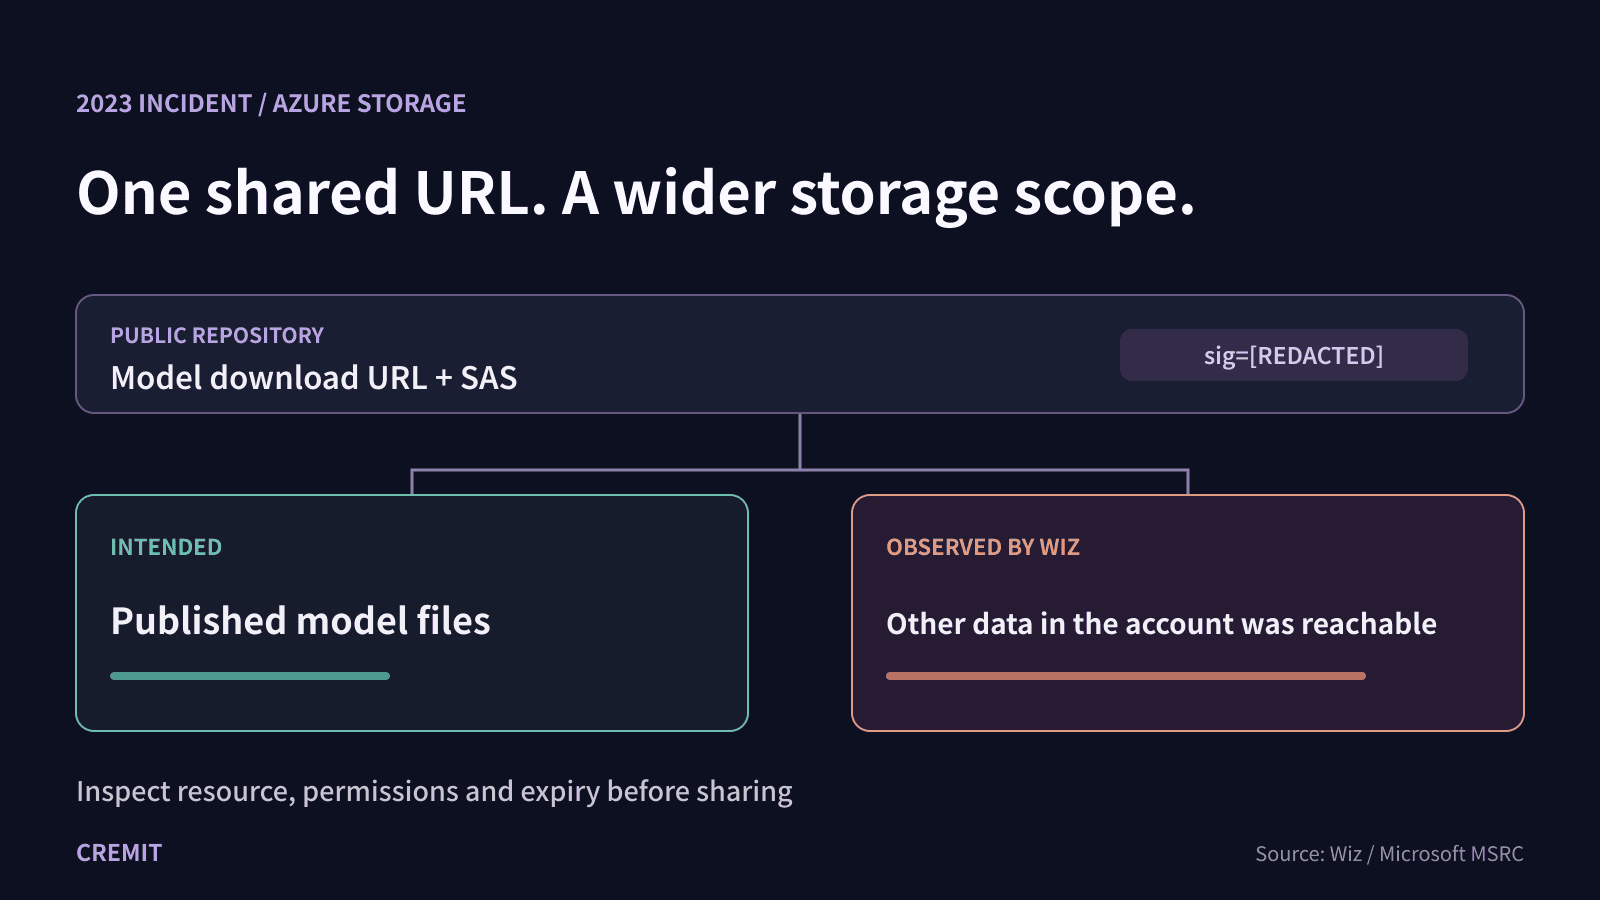
A public model download URL carried an Azure SAS token that reached other storage data. Microsoft and Wiz show why finding a URL, reviewing its scope, and investigating access are separate steps.
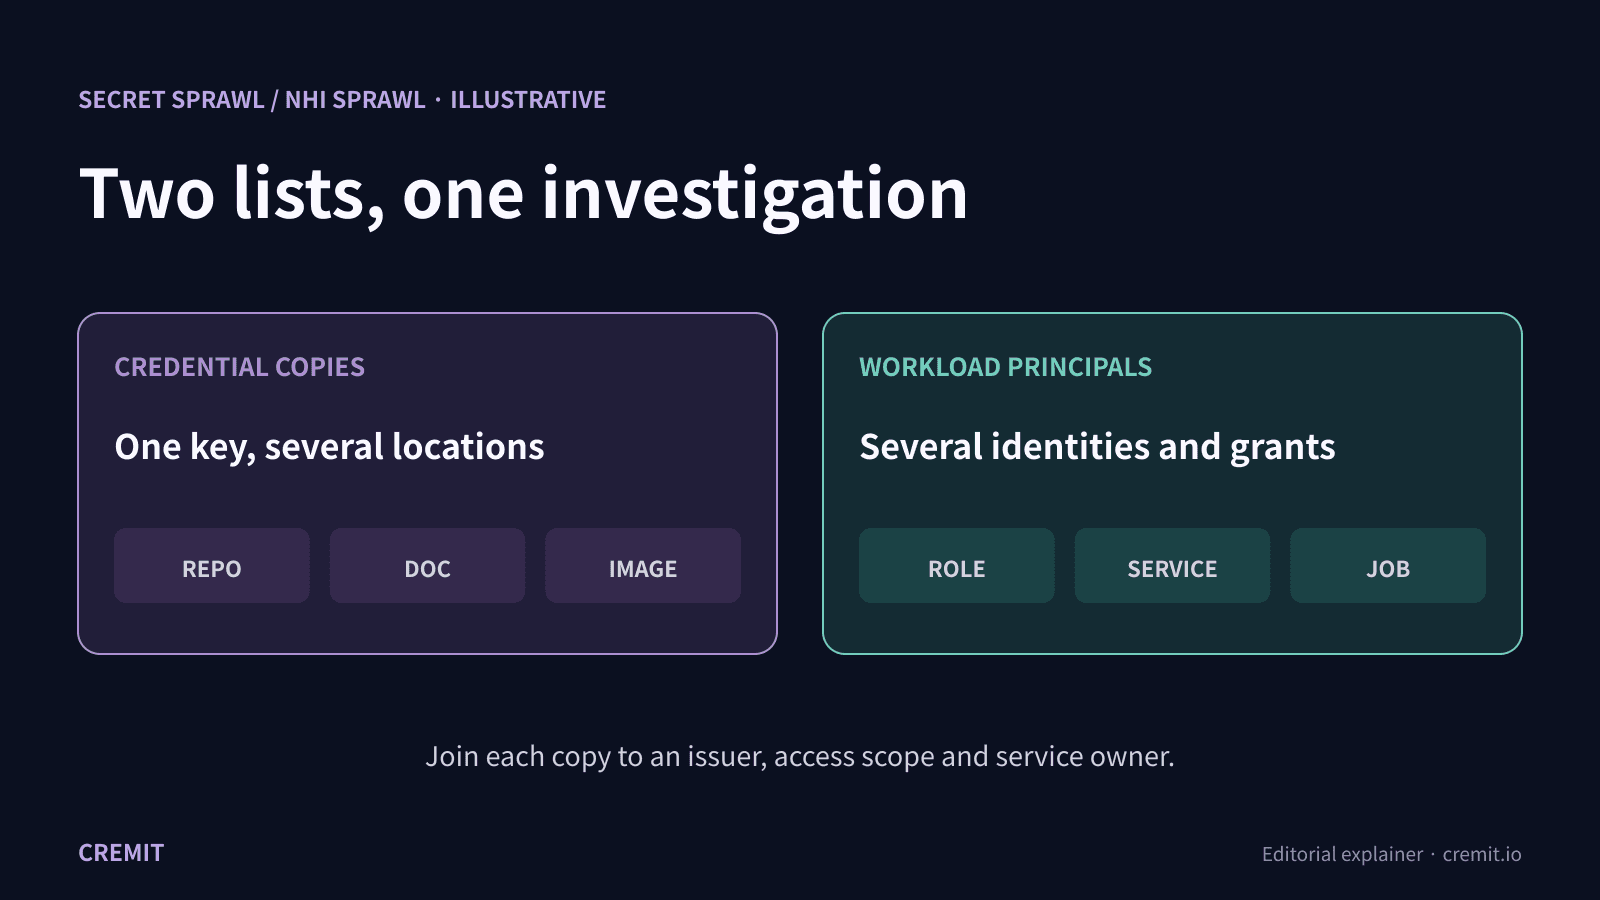
One credential can be copied to many places; many workload principals can accumulate grants. Keep separate records, then join the evidence for each investigation.
A short monthly brief on credential security from Cremit.