Secret sprawl and workload identity sprawl: two different lists
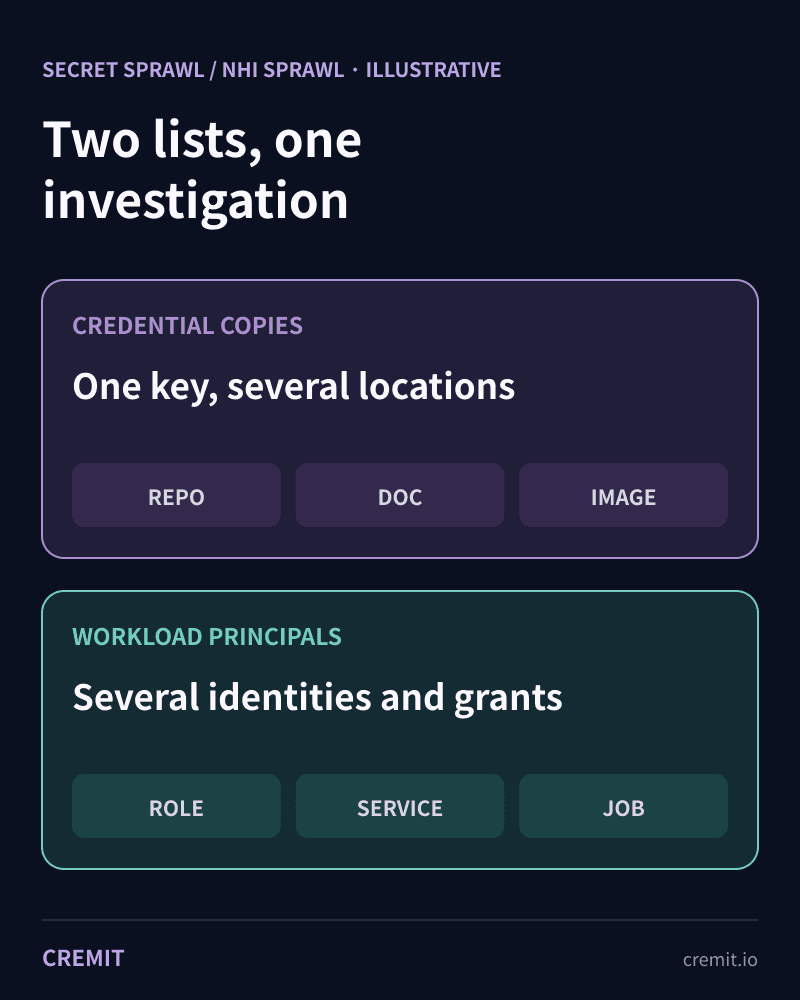
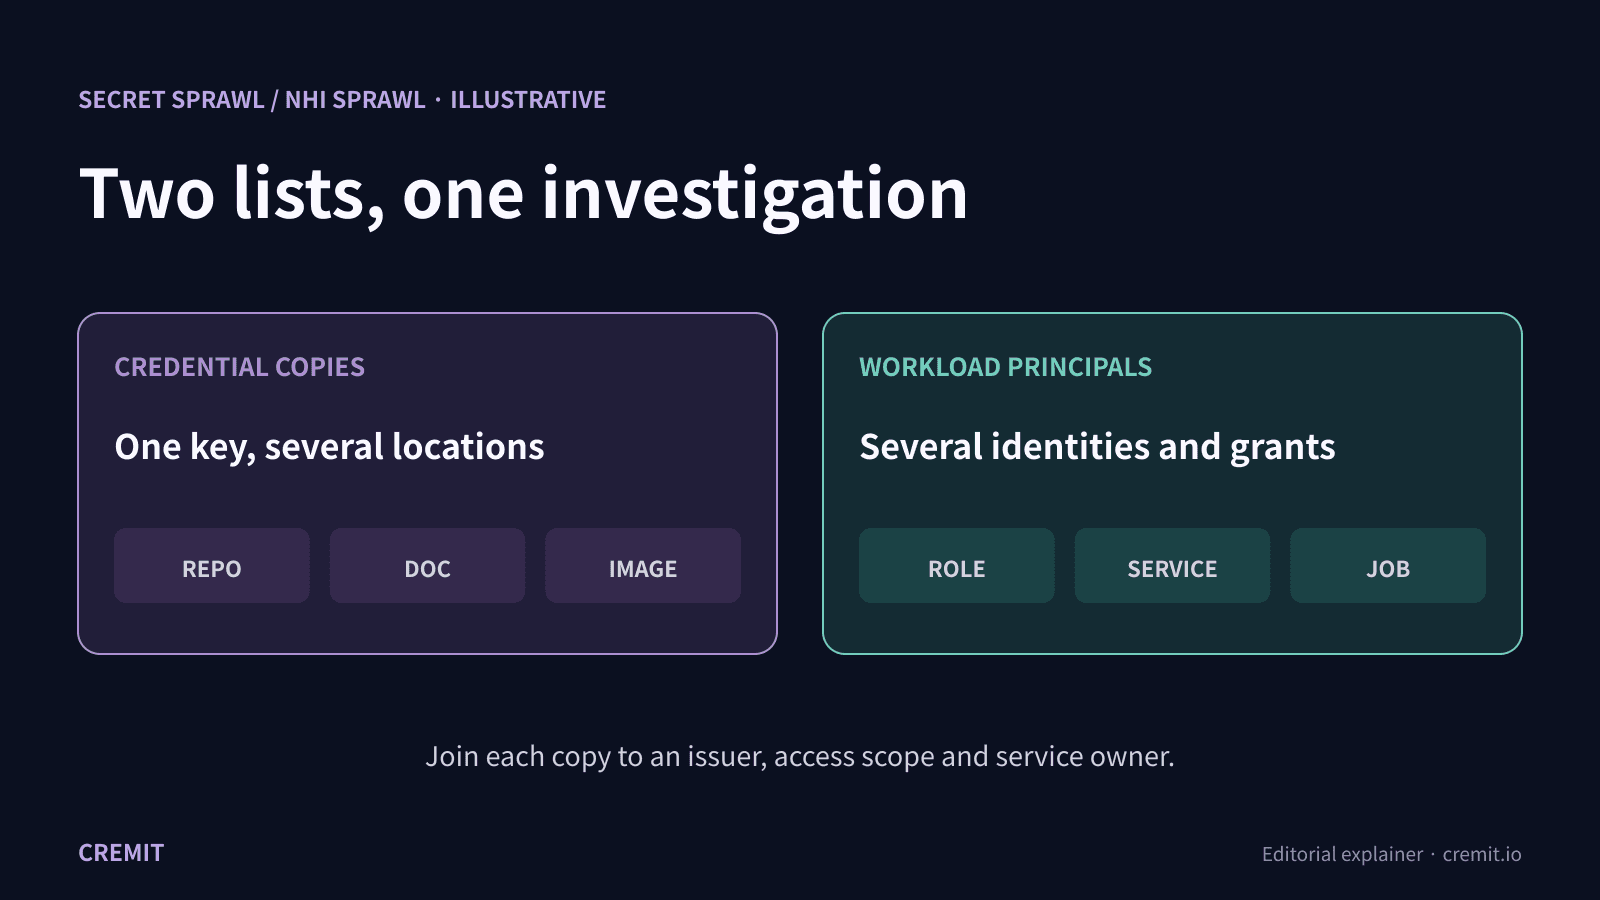
One credential can be copied to many places; many workload principals can accumulate grants. Keep separate records, then join the evidence for each investigation.

On this page(6)
Secret sprawl means copies of sensitive credentials accumulating across repositories, documents, images or other inspected sources. Workload identity sprawl means service accounts, roles or other machine principals and grants growing without clear ownership or retirement. A principal is the actor with access; a key or token is a credential it may use. The two problems can overlap, but counting credential copies does not count identities.
Two examples that lead to different work
Suppose one service account key appears in a repository, an internal document and a published image. That is one principal with several observed credential copies. Removing the repository line does not invalidate the key or erase the other copies. Confirm the issuing account, affected workload and access, replace or revoke the key at the issuer, and inspect the remaining locations. These locations are illustrative, not a claim about a particular customer or incident.
Now suppose several service accounts and roles retain permissions after their jobs have changed or ended. No exported key is found in the sources you inspected. The access and ownership problem still exists. A clean source scan says nothing about uninspected sources, and it cannot establish that every principal or grant is justified. Review the principal inventory and issuer activity separately.
Keep a copy record and a principal record
For each observed copy, record a masked identifier or protected fingerprint, source location, scan coverage and time, status, and any author clue. Never paste the raw secret into a tracking document. The author of a source change may help find a responder, but is not automatically the current service owner.
For each principal, record the issuer and principal ID, using service or job, environment, effective grants where available, responsible owner, last known activity and retirement decision. Join a copy to a principal through an issuer key ID or protected fingerprint when possible. If the issuer or principal is unknown, leave the link unresolved; a pattern match alone does not prove it. Google Cloud advises documenting the application and contact for service accounts, and AWS advises reviewing unused access and preferring temporary workload credentials.
Choose the issuer-side action
For a confirmed exposed credential, identify dependent workloads, replace or revoke it at the issuer, update those workloads, and inspect available activity and copies. For an unused principal, confirm dependencies, disable or delete it and remove grants according to the issuer’s procedure. One action does not close the other record: key rotation leaves unrelated stale principals, while deleting one principal does not remove other exposed keys. OWASP lists secret leakage and improper offboarding as distinct workload-identity risks.
Where Cremit fits
Cremit finds credential patterns in supported connected sources and checks issuer status for supported types. It can add available AWS or GCP access context and clues about a source author to a finding. It does not enumerate every live workload or every copy, establish the service owner, prove misuse, or automatically revoke a credential. Use the finding to start the two-record investigation, then confirm the owner and act at the issuer.
Primary documentation
Google Cloud: service account ownership and use
Google Cloud: managing service account keys
AWS IAM: security best practices
OWASP NHI Top 10: offboarding and secret leakage
Related reading
Read next
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.
MCP Servers Are Taking API Keys Through the Chat Window
We sent one initialize request to every remote MCP server in the official registry. 71.3% of 22,027 responding servers opened a session with no header authentication, and 3,705 credential fields sit in tool arguments. Three of them are marked secret.
Unlisted, Not Private
A September 2026 sweep of 33 public surfaces confirmed 23,912 active credentials. Privilege context was established for 7,468; 1,277 had permission to issue another key. Actual re-issuance was not tested.
Get the next one in your inbox
Monthly NHI security brief from Cremit. One email, high signal.