NEW · Blast Radius: a field playbook for leaked API keys on AWS, GCP and Azure
Back to Blog
Tag

Supply Chain Attack

8 posts
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
Oct 11, 2026

GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History

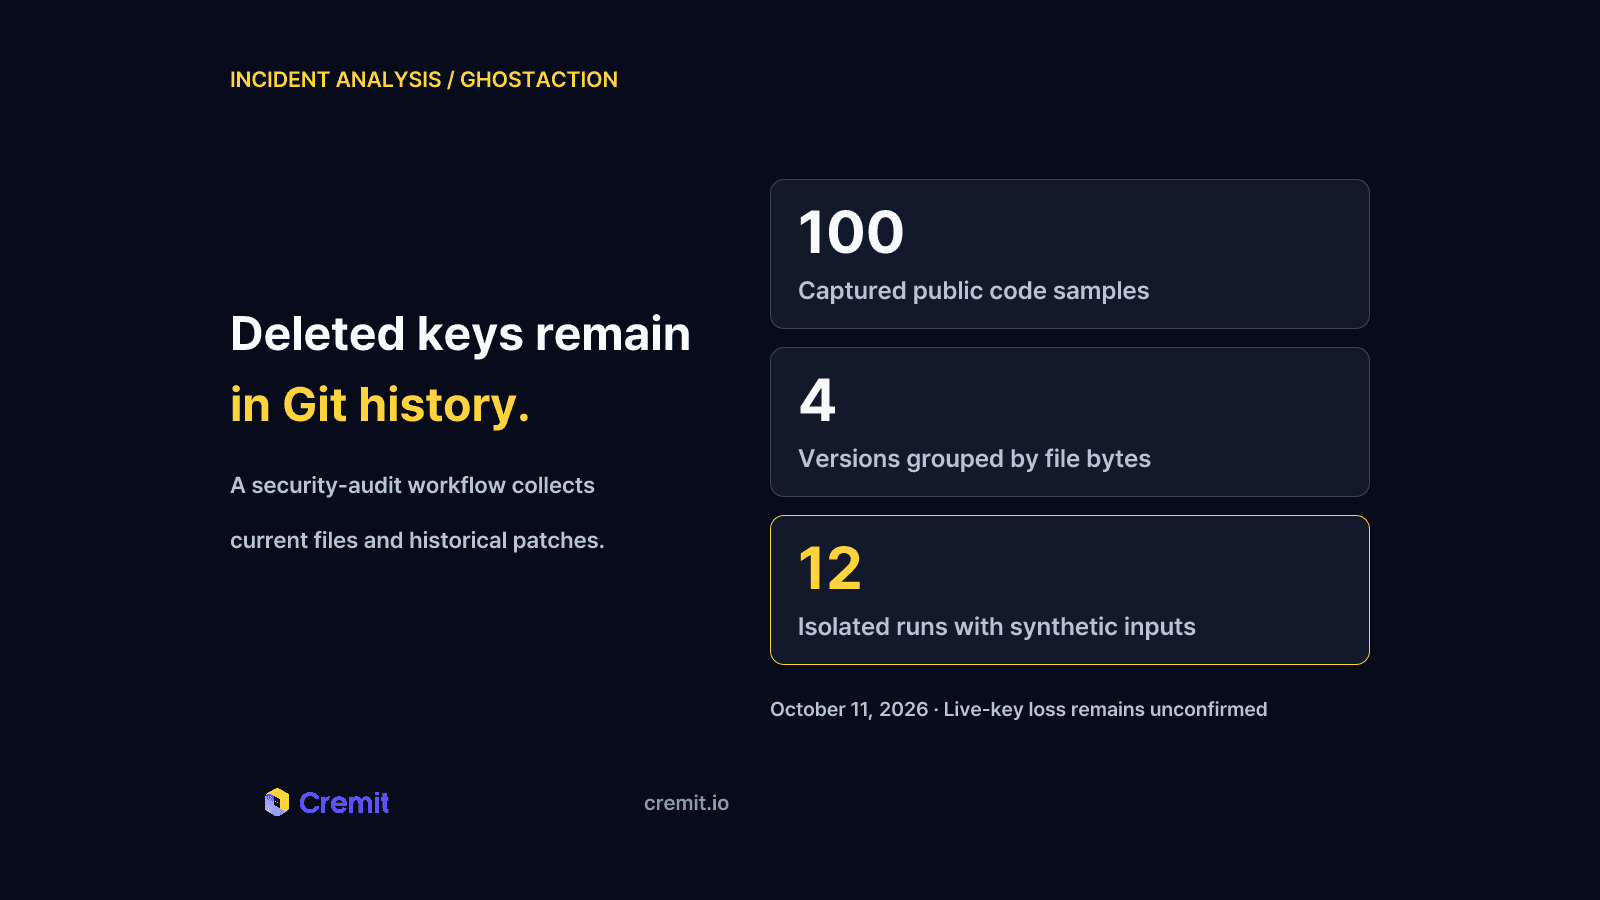
A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.

Ben Kim
Ben Kim
AITU CTF Final 2026 Writeup
Apr 29, 2026

AITU CTF Final 2026 Writeup

Full writeup of the AITU CTF Final (April 25-26, 2026), a HackCity-format competition. We walk through exploiting DMZ hosts via XXE, SSTI, and SQLi, pivoting into the DEV segment through AD lateral movement, escaping a privileged Docker container via cgroup abuse, and breaching a healthcare system through JWT JKU header injection.

Ethan Kim
Ethan Kim
Bitwarden CLI npm compromise: affected systems and response
Apr 25, 2026

Bitwarden CLI npm compromise: affected systems and response

A malicious CLI package was available on npm for 93 minutes on April 22, 2026. Check who installed it, what researchers found, and Bitwarden’s response steps.

Ben Kim
Ben Kim
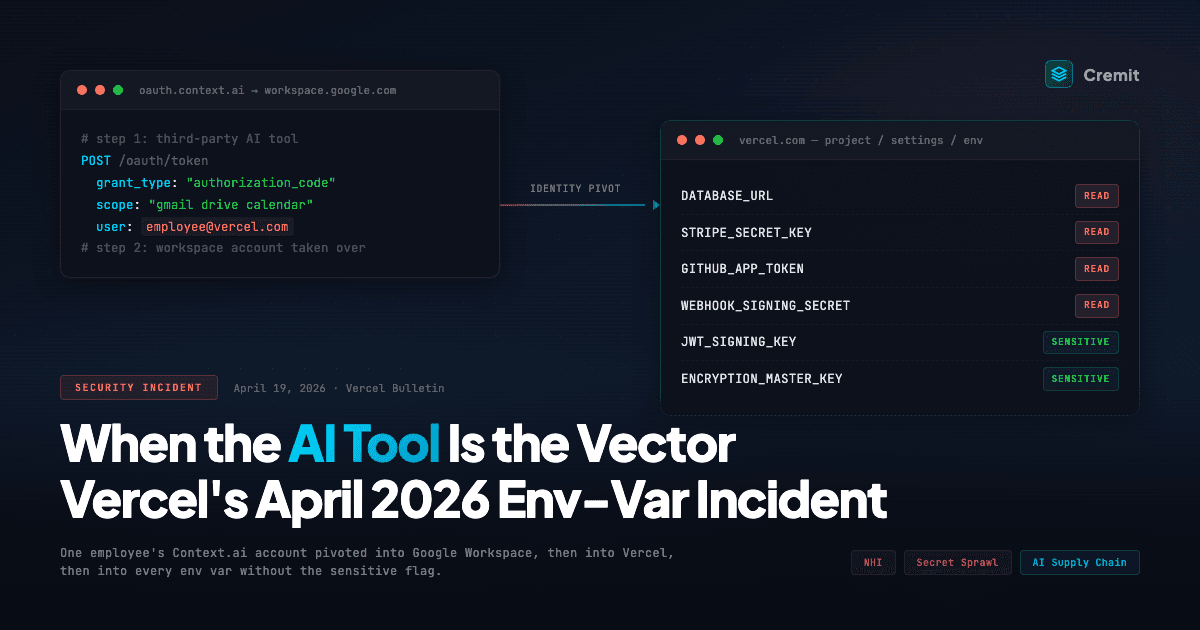
Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why
Apr 20, 2026

Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why

Vercel confirmed an unauthorized-access incident on April 19, 2026 that started in a third-party AI tool, pivoted through Google Workspace, and reached environment variables in a subset of customer projects. The exposure surface is every env var that was not marked sensitive. Here is what is confirmed, what is noise, and what to rotate first.

Ben Kim
Ben Kim
Long-exposed credentials: what a 90-day source record tells you
Apr 10, 2026

Long-exposed credentials: what a 90-day source record tells you

An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.

Ben Kim
Ben Kim
When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack
Mar 25, 2026

When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.

Ben Kim
Ben Kim
Clinejection: prompt injection and the unauthorized Cline CLI release
Mar 7, 2026

Clinejection: prompt injection and the unauthorized Cline CLI release

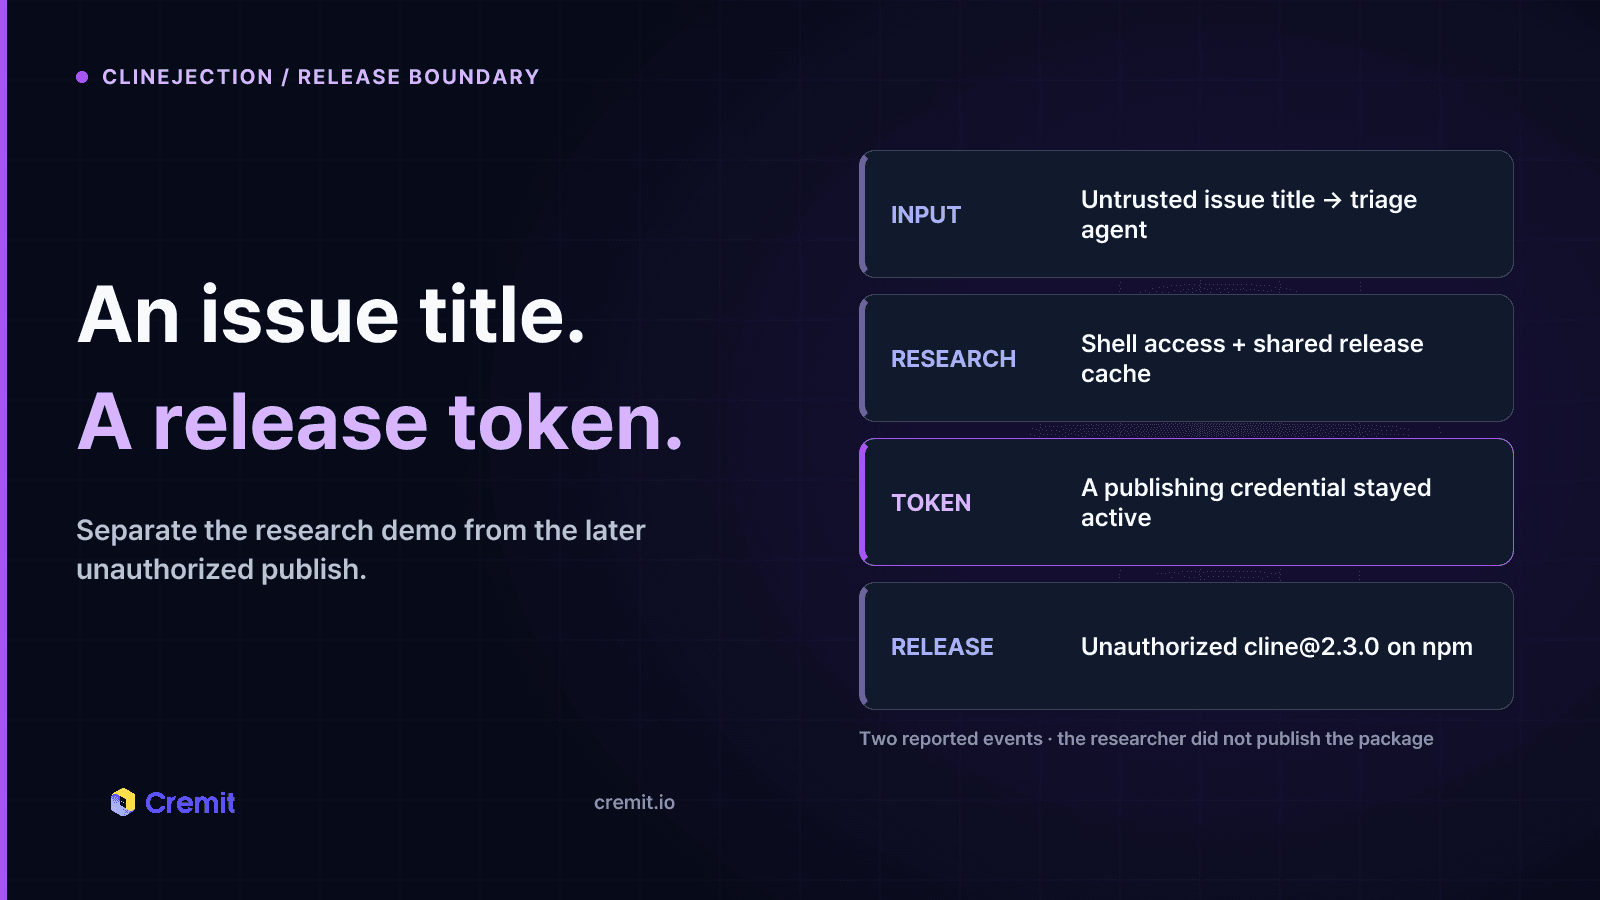
Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.

Ben Kim
Ben Kim
Nx S1ngularity Attack: The Workflow-to-npm Token Path
Aug 28, 2025

Nx S1ngularity Attack: The Workflow-to-npm Token Path

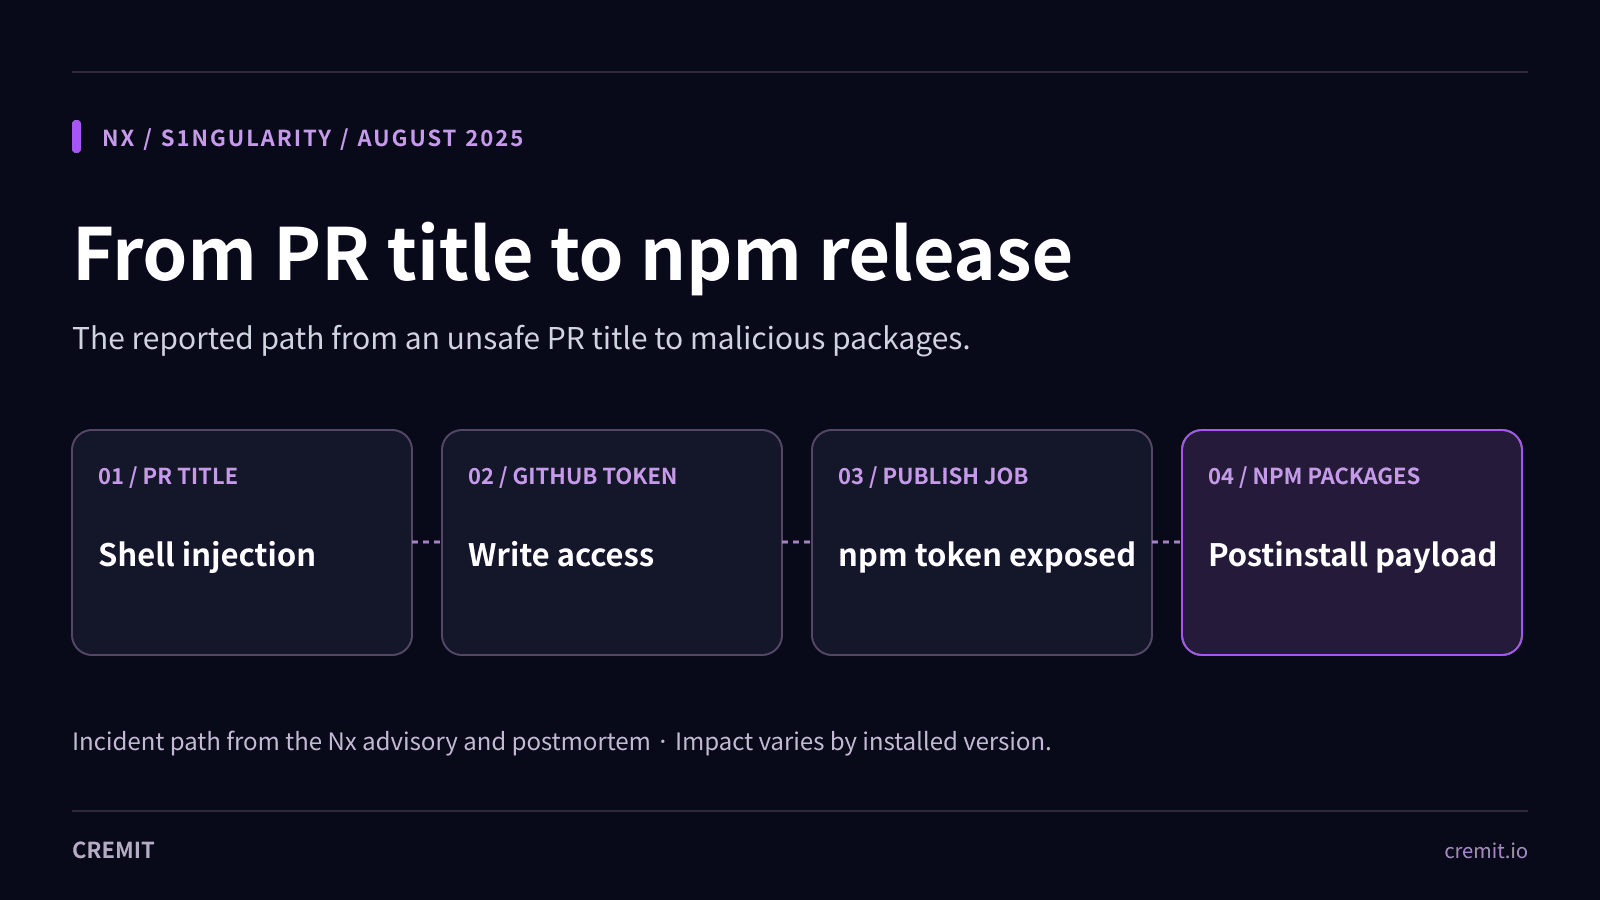
The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.

Ben Kim
Ben Kim
Supply Chain Attack | Cremit Blog | Cremit