NEW · Blast Radius: a field playbook for leaked API keys on AWS, GCP and Azure
Back to Blog
Category

Security Incidents

Analysis of security breaches and cyber attacks

13 posts
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
Oct 11, 2026

GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History

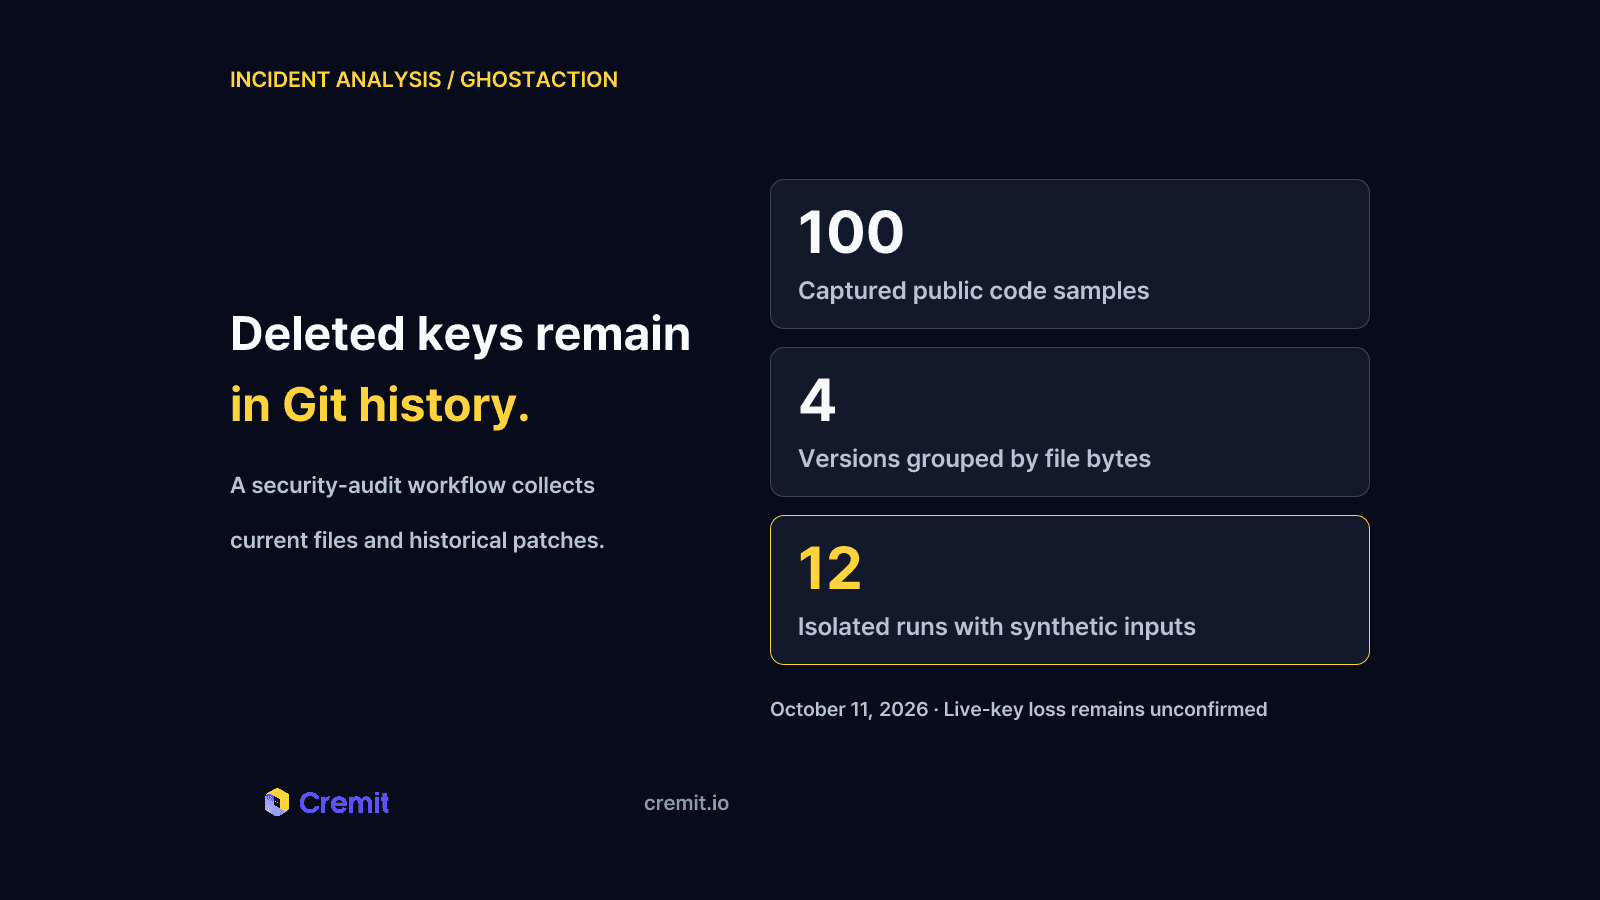
A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.

Ben Kim
Ben Kim
The machine access behind an exposed API key
Jul 15, 2026

The machine access behind an exposed API key

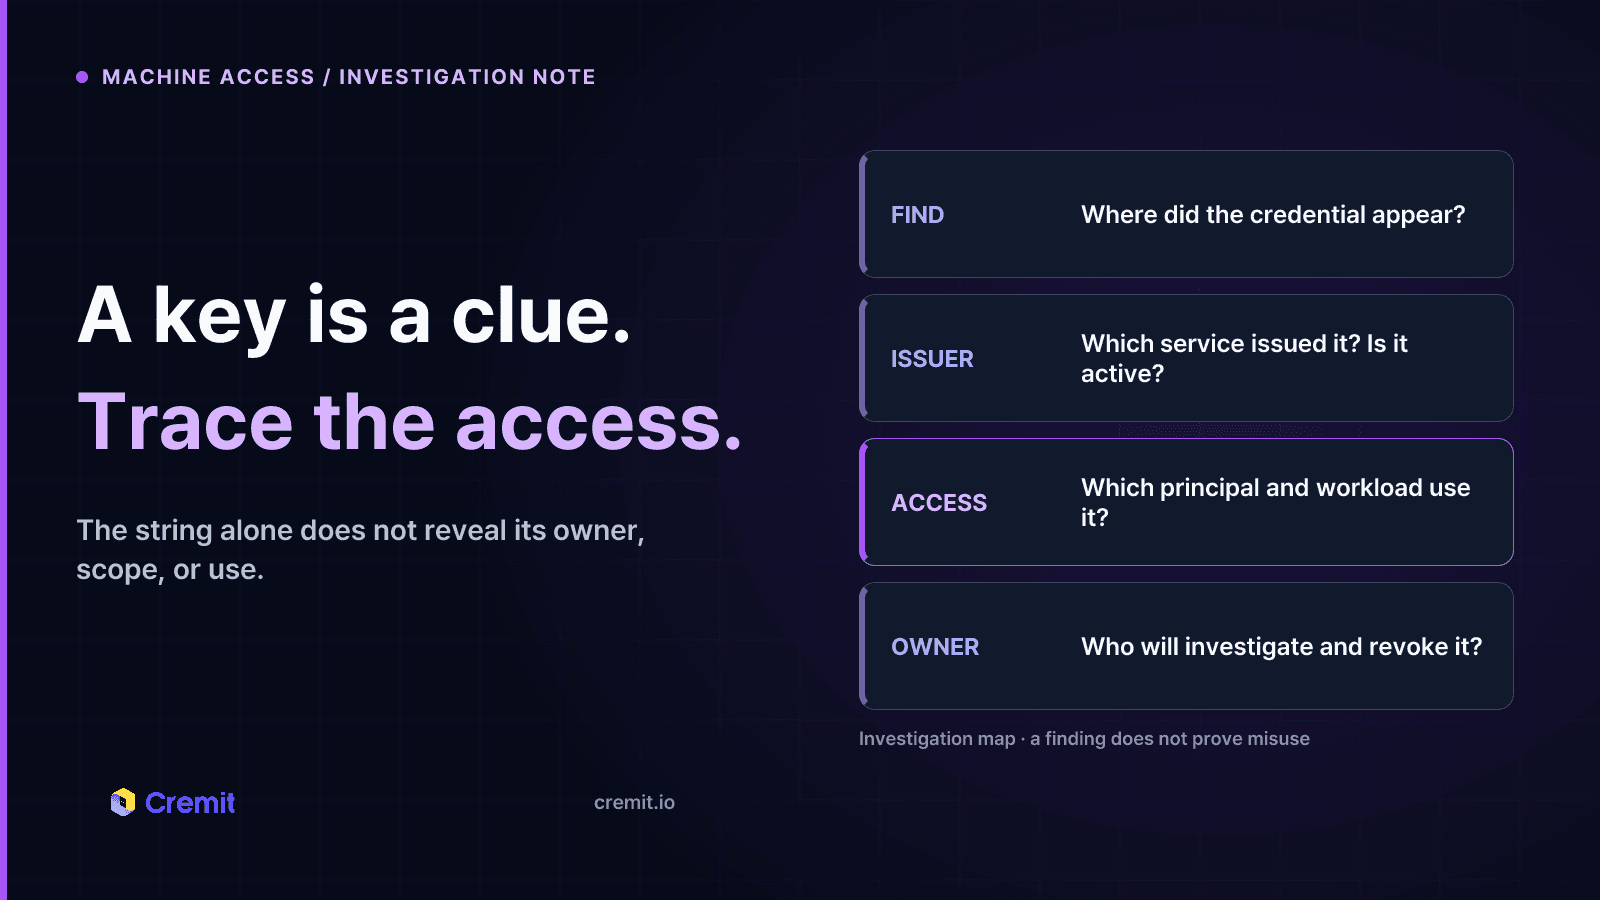
An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.

Ben Kim
Ben Kim
AntV npm compromise: what the package evidence shows
May 19, 2026

AntV npm compromise: what the package evidence shows

Socket and SafeDep documented hundreds of malicious AntV-related npm releases. Compare exact versions, understand the two execution paths, and scope credentials exposed on affected hosts.

Ben Kim
Ben Kim
Bitwarden CLI npm compromise: affected systems and response
Apr 25, 2026

Bitwarden CLI npm compromise: affected systems and response

A malicious CLI package was available on npm for 93 minutes on April 22, 2026. Check who installed it, what researchers found, and Bitwarden’s response steps.

Ben Kim
Ben Kim
Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why
Apr 20, 2026

Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why

Vercel confirmed an unauthorized-access incident on April 19, 2026 that started in a third-party AI tool, pivoted through Google Workspace, and reached environment variables in a subset of customer projects. The exposure surface is every env var that was not marked sensitive. Here is what is confirmed, what is noise, and what to rotate first.

Ben Kim
Ben Kim
The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure
Apr 15, 2026

The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure

An organization's core credentials sat in public repositories for years. The security industry's answer: "Out of scope."

Ben Kim
Ben Kim
When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack
Mar 25, 2026

When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.

Ben Kim
Ben Kim
Clinejection: prompt injection and the unauthorized Cline CLI release
Mar 7, 2026

Clinejection: prompt injection and the unauthorized Cline CLI release

Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.

Ben Kim
Ben Kim
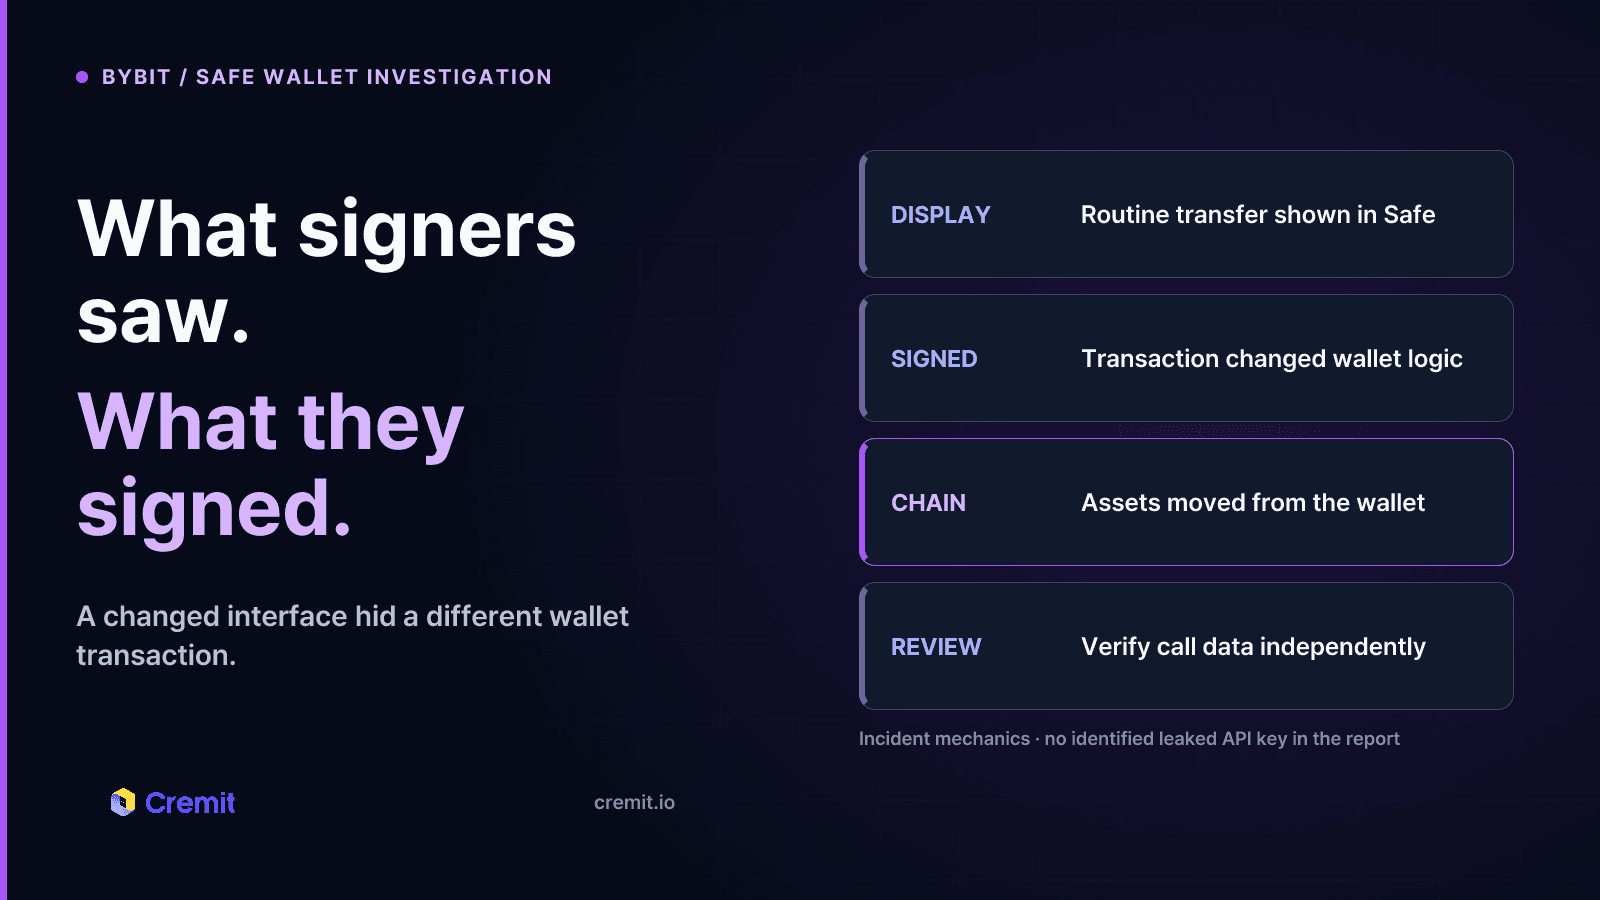
Bybit Hack: What the Safe Wallet Investigation Found
Jan 25, 2026

Bybit Hack: What the Safe Wallet Investigation Found

The February 2025 theft involved a compromised Safe developer and a manipulated transaction interface. Here is what investigators confirmed and what remains unknown.

Ben Kim
Ben Kim
Can You Prove a Leaked API Key Was Sold?
Dec 26, 2025

Can You Prove a Leaked API Key Was Sold?

A public leak, a valid key, and evidence of misuse are different findings. Here is how to investigate each without claiming a sale you cannot prove.

Ben Kim
Ben Kim
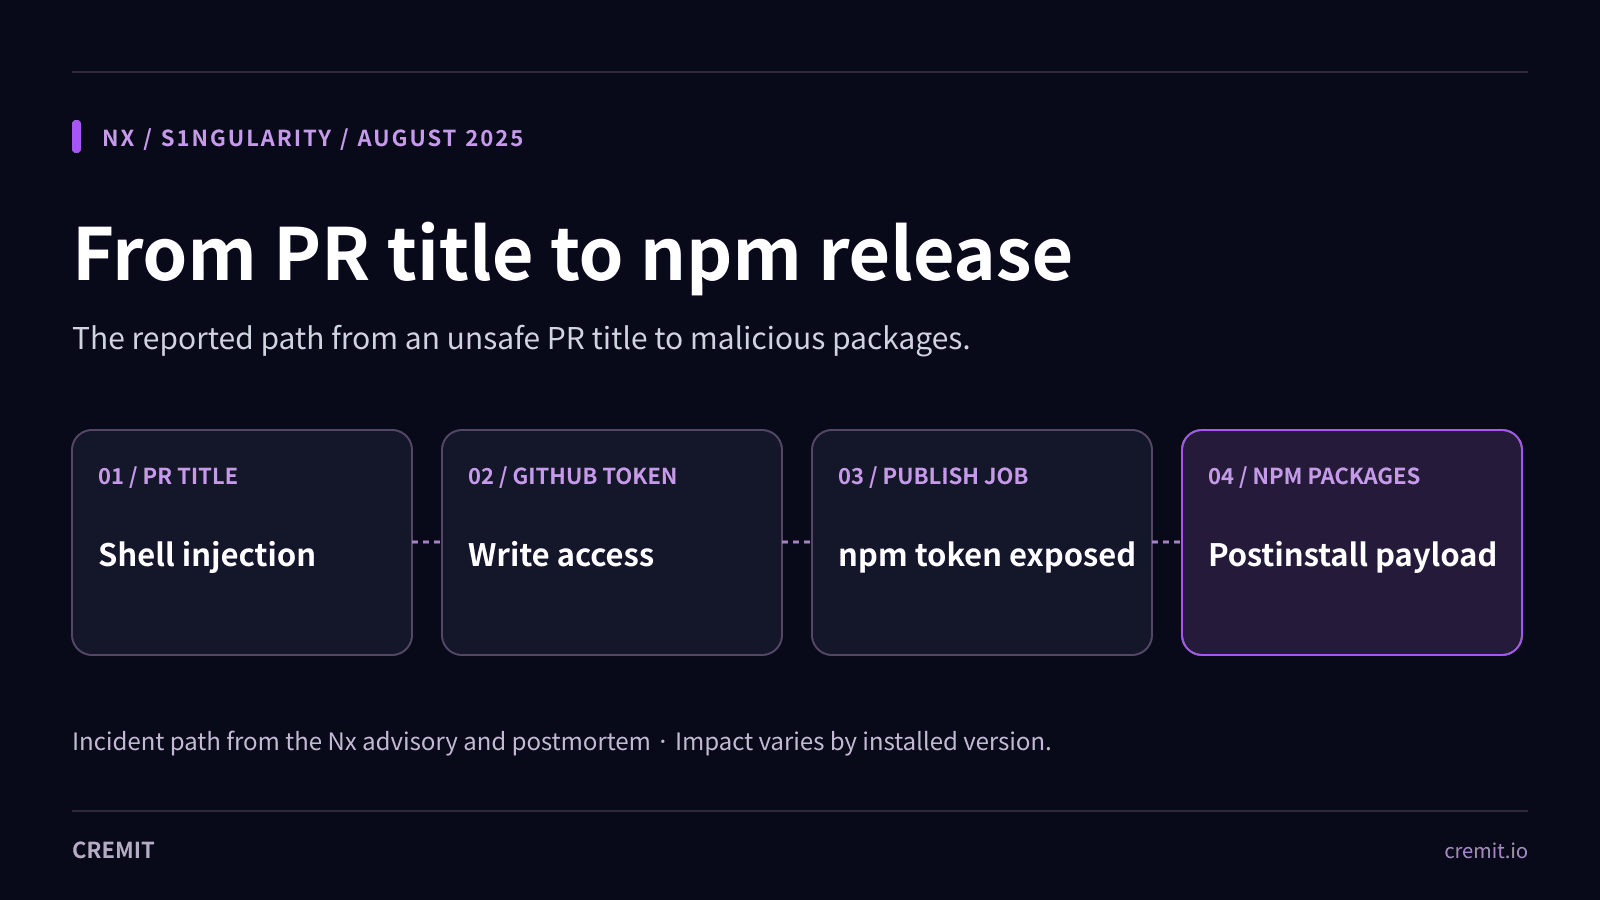
Nx S1ngularity Attack: The Workflow-to-npm Token Path
Aug 28, 2025

Nx S1ngularity Attack: The Workflow-to-npm Token Path

The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.

Ben Kim
Ben Kim
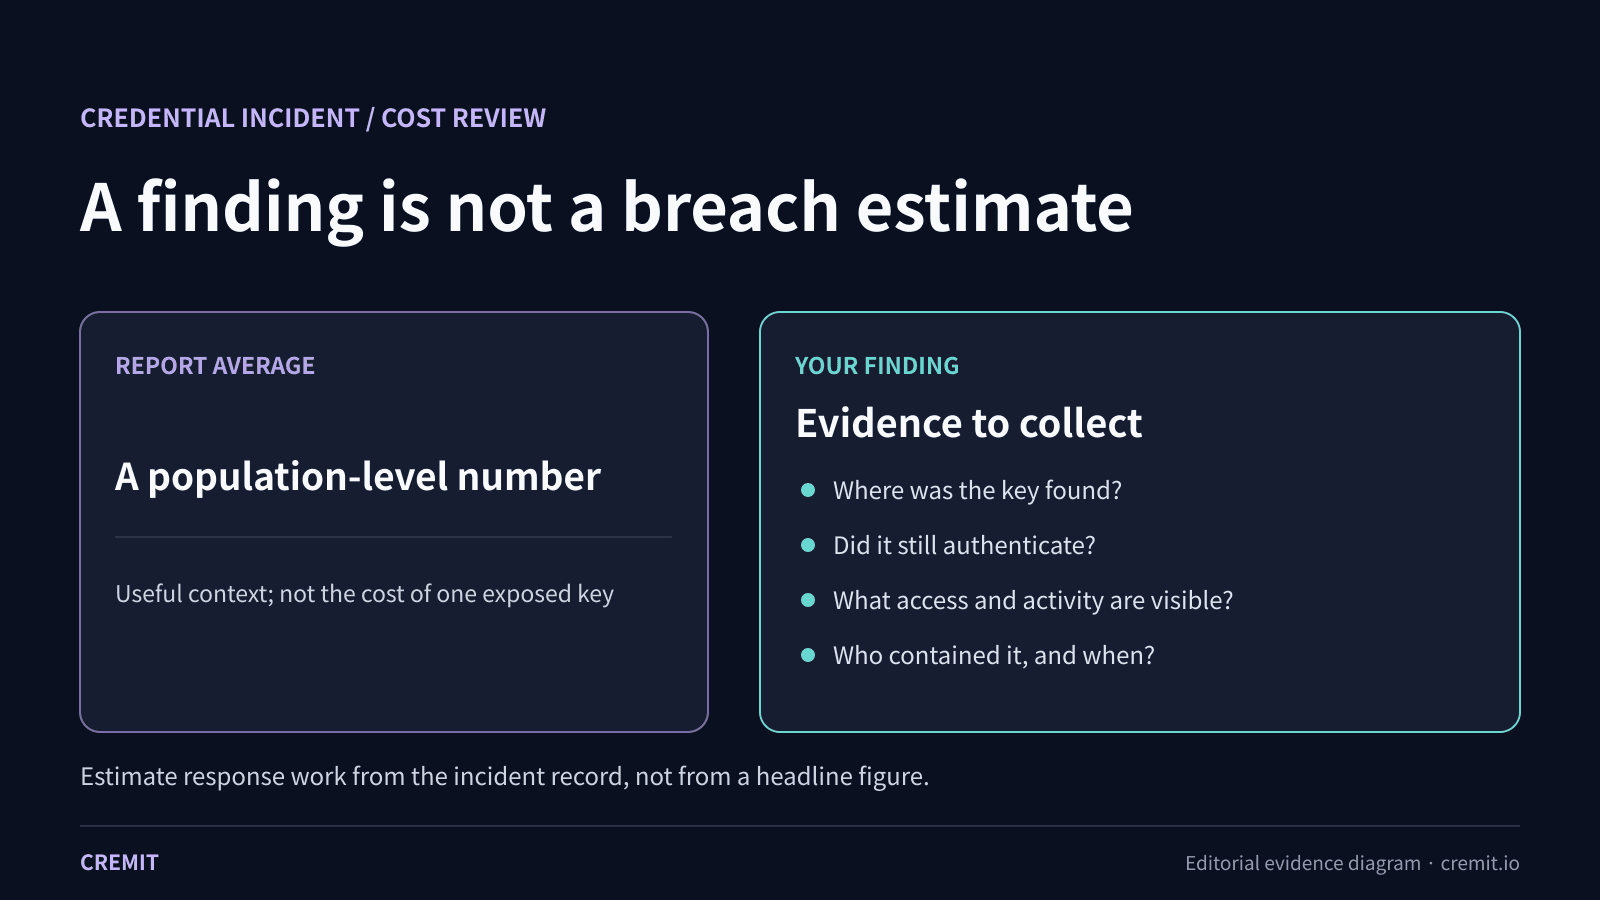
Data breach costs: what an exposed key finding can tell you
Apr 4, 2025

Data breach costs: what an exposed key finding can tell you

A breach-cost average cannot price one exposed credential. Record the key’s source, issuer status, available access and activity evidence, and response work before estimating impact.

Ben Kim
Ben Kim
Microsoft’s exposed SAS URL: what one repository link opened
Oct 23, 2023

Microsoft’s exposed SAS URL: what one repository link opened

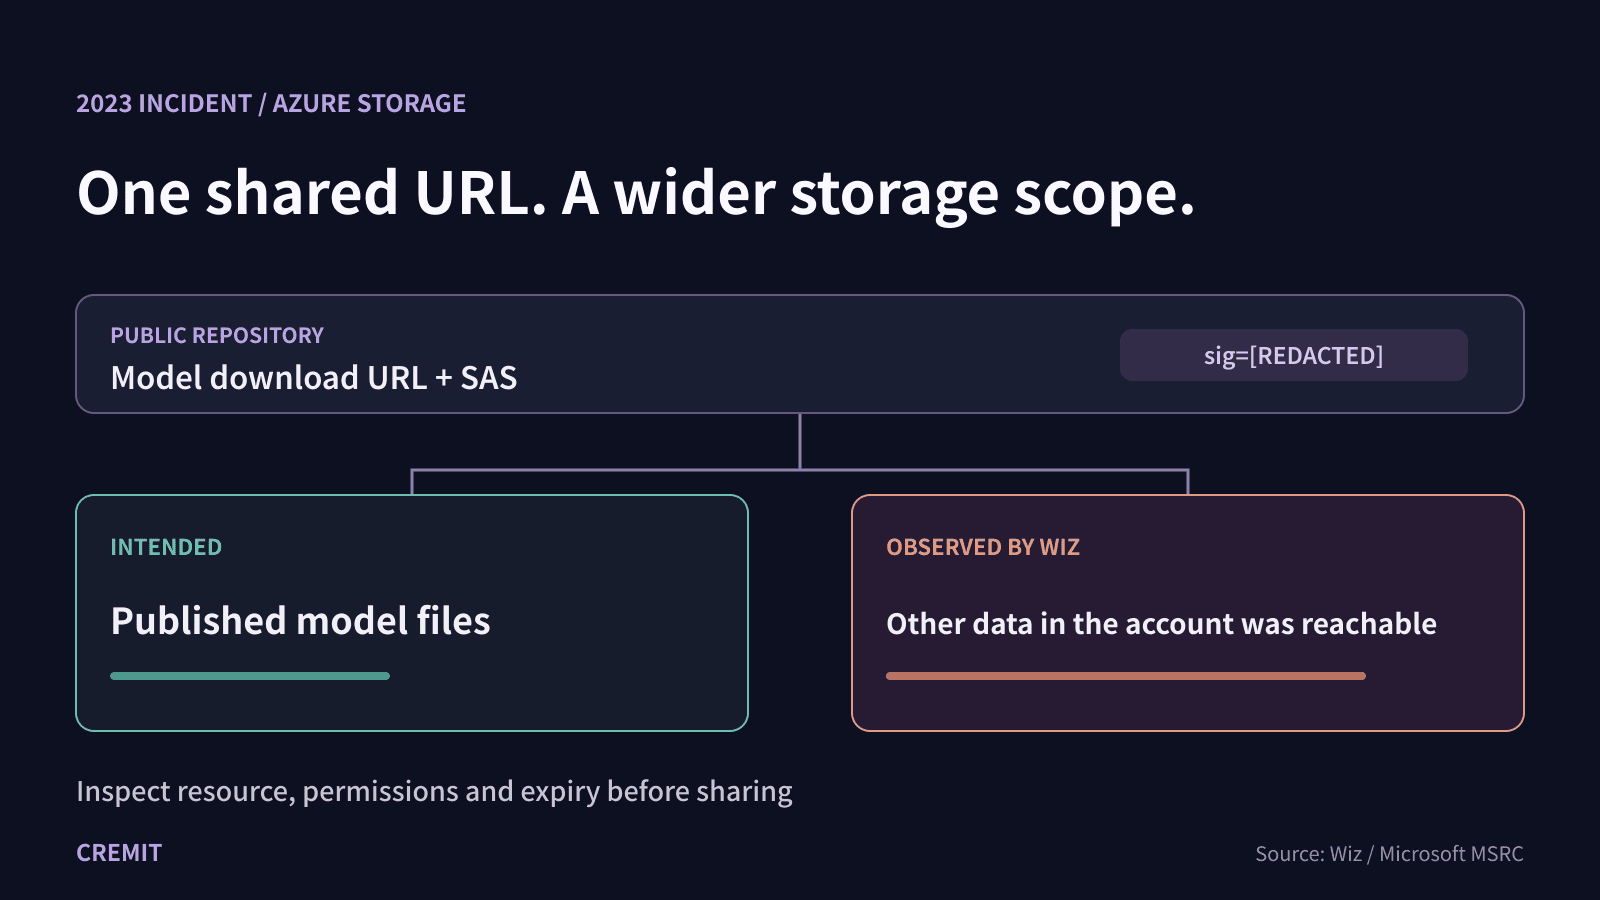
A public model download URL carried an Azure SAS token that reached other storage data. Microsoft and Wiz show why finding a URL, reviewing its scope, and investigating access are separate steps.

Ben Kim
Ben Kim
Security Incidents | Cremit Blog | Cremit