Apr 25, 2025
OWASP NHI5: How to Review Excess Machine Permissions
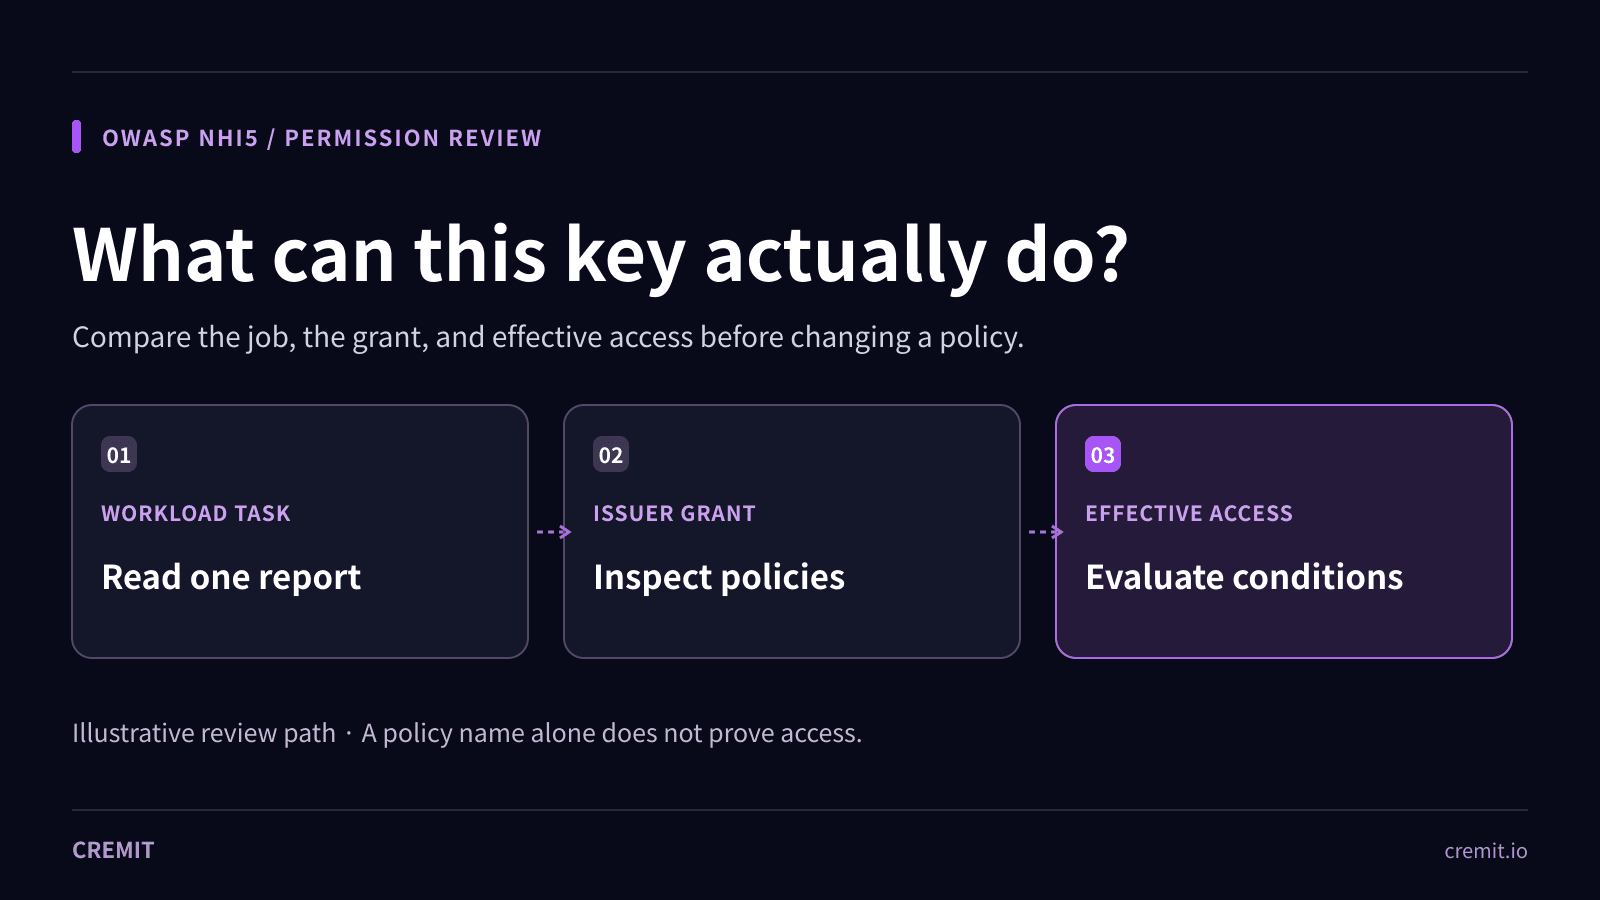
Compare workload needs, issuer grants, effective access, and observed use before reducing an NHI’s permissions.

Ben Kim
Compare workload needs, issuer grants, effective access, and observed use before reducing an NHI’s permissions.
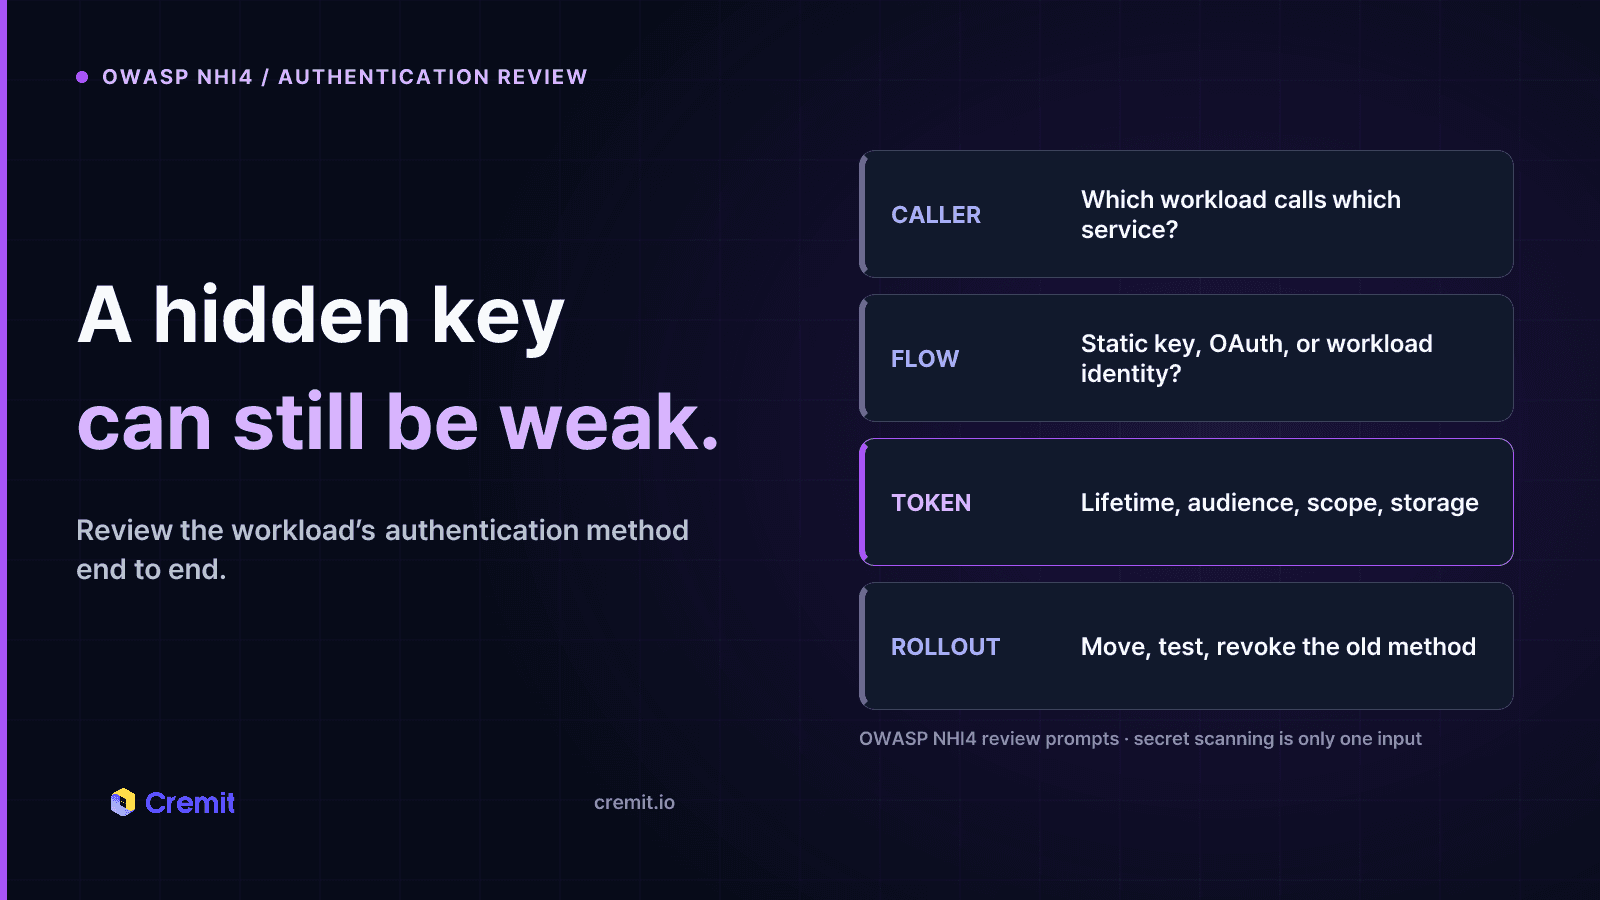
Insecure authentication is more than a leaked key. Review OAuth flows, static credentials, token scope, and the rollout path for safer workload access.
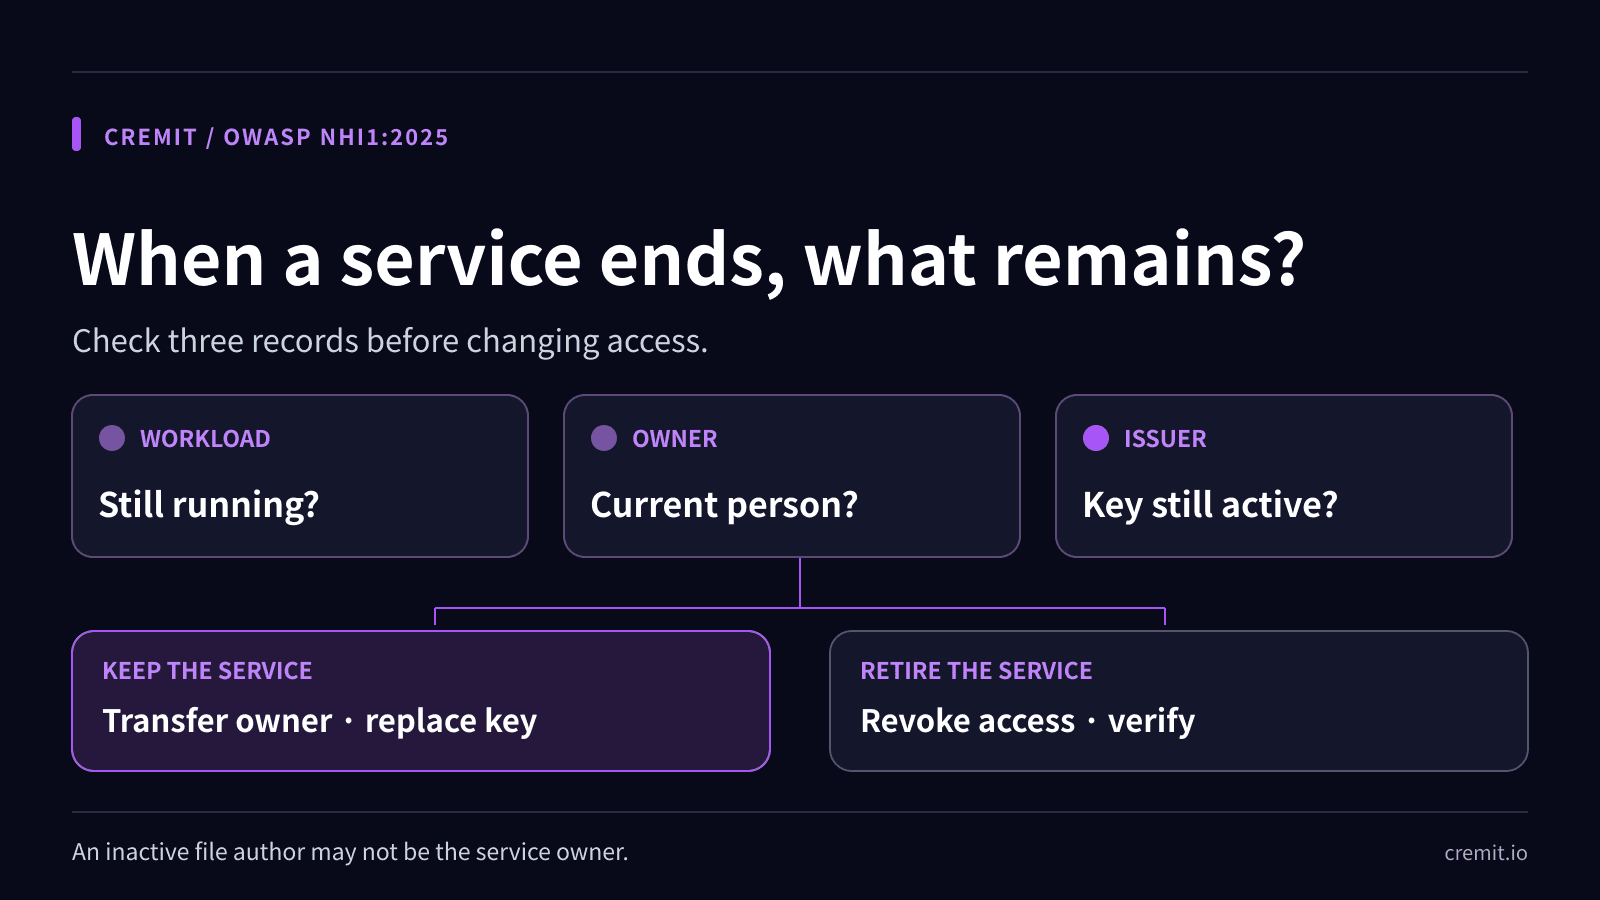
When a service ends or its owner leaves, decide what still runs, transfer responsibility or revoke access, and verify the old key no longer works.
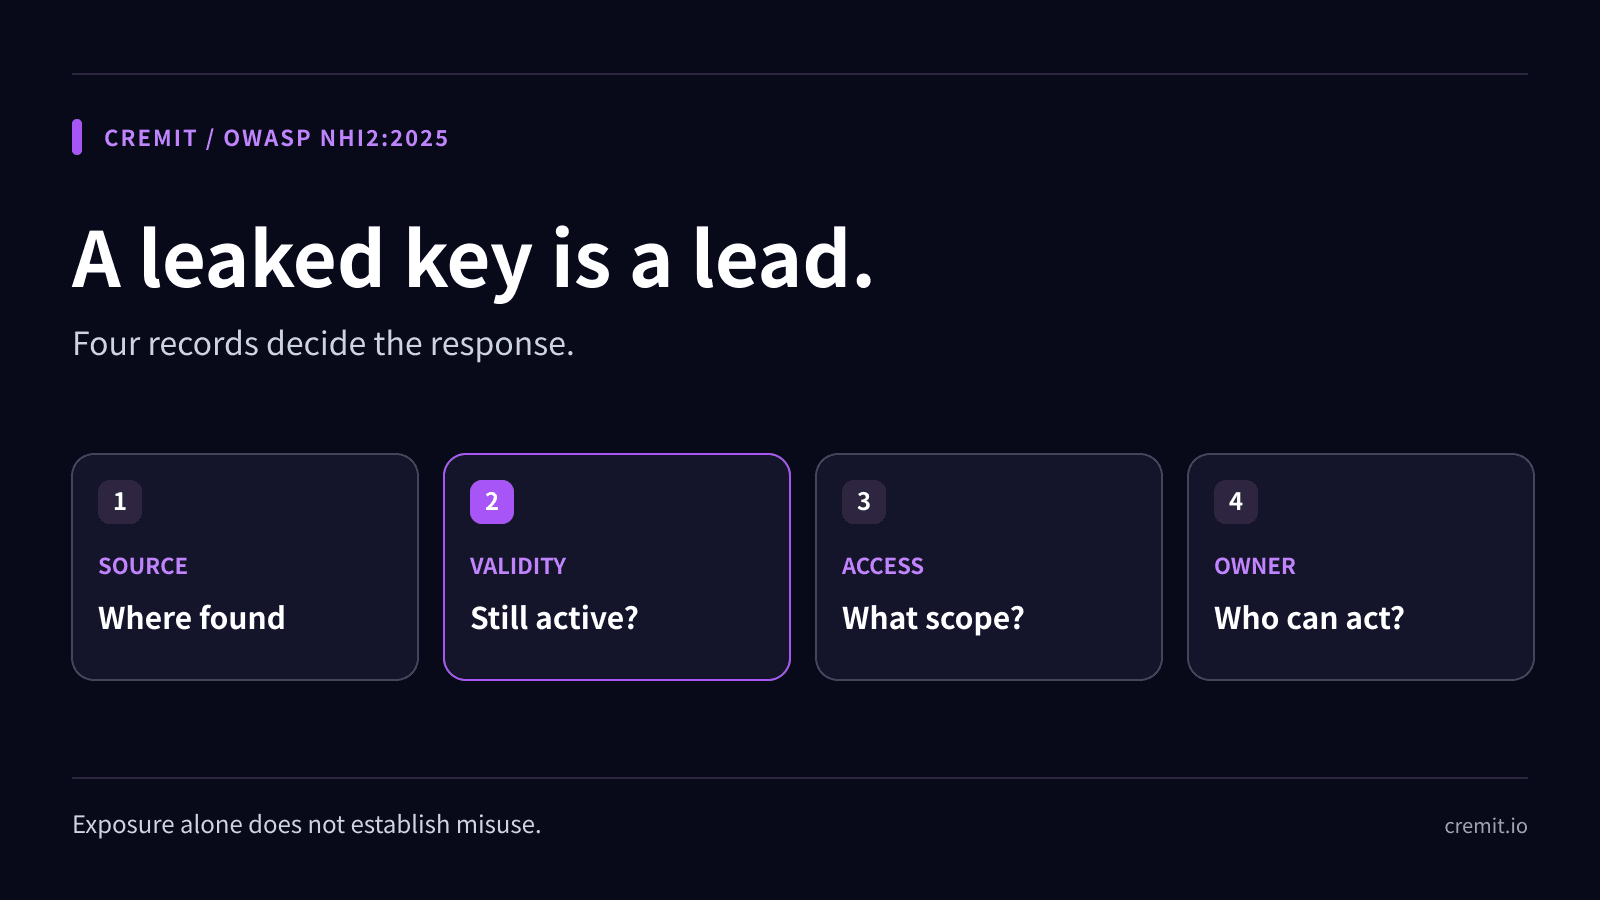
A leaked secret is a lead, not proof of misuse. Check its location, validity, access, and response owner before closing the exposure.
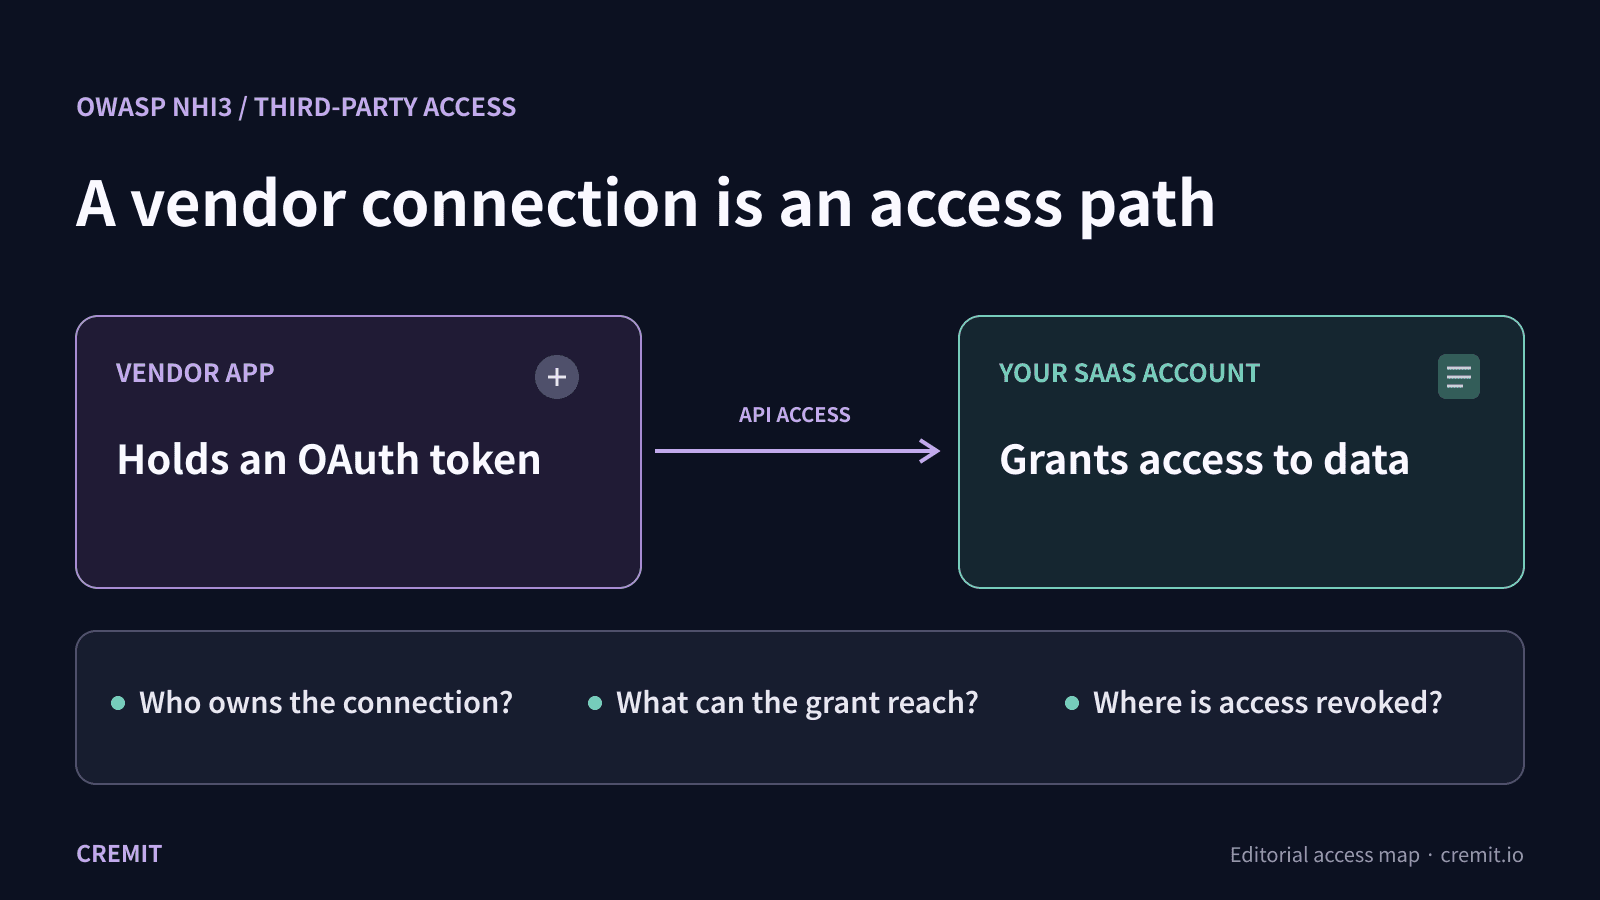
A vendor can hold a token that reaches your SaaS data. Use the Salesloft Drift incident and GitHub App controls to review the grant, owner, activity and revocation path.

The ten OWASP NHI risks explained through specific checks for service accounts, tokens, deployment systems, and owners.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy