NEW · Blast Radius: a field playbook for leaked API keys on AWS, GCP and Azure
Back to Blog
Tag

API Keys

14 posts
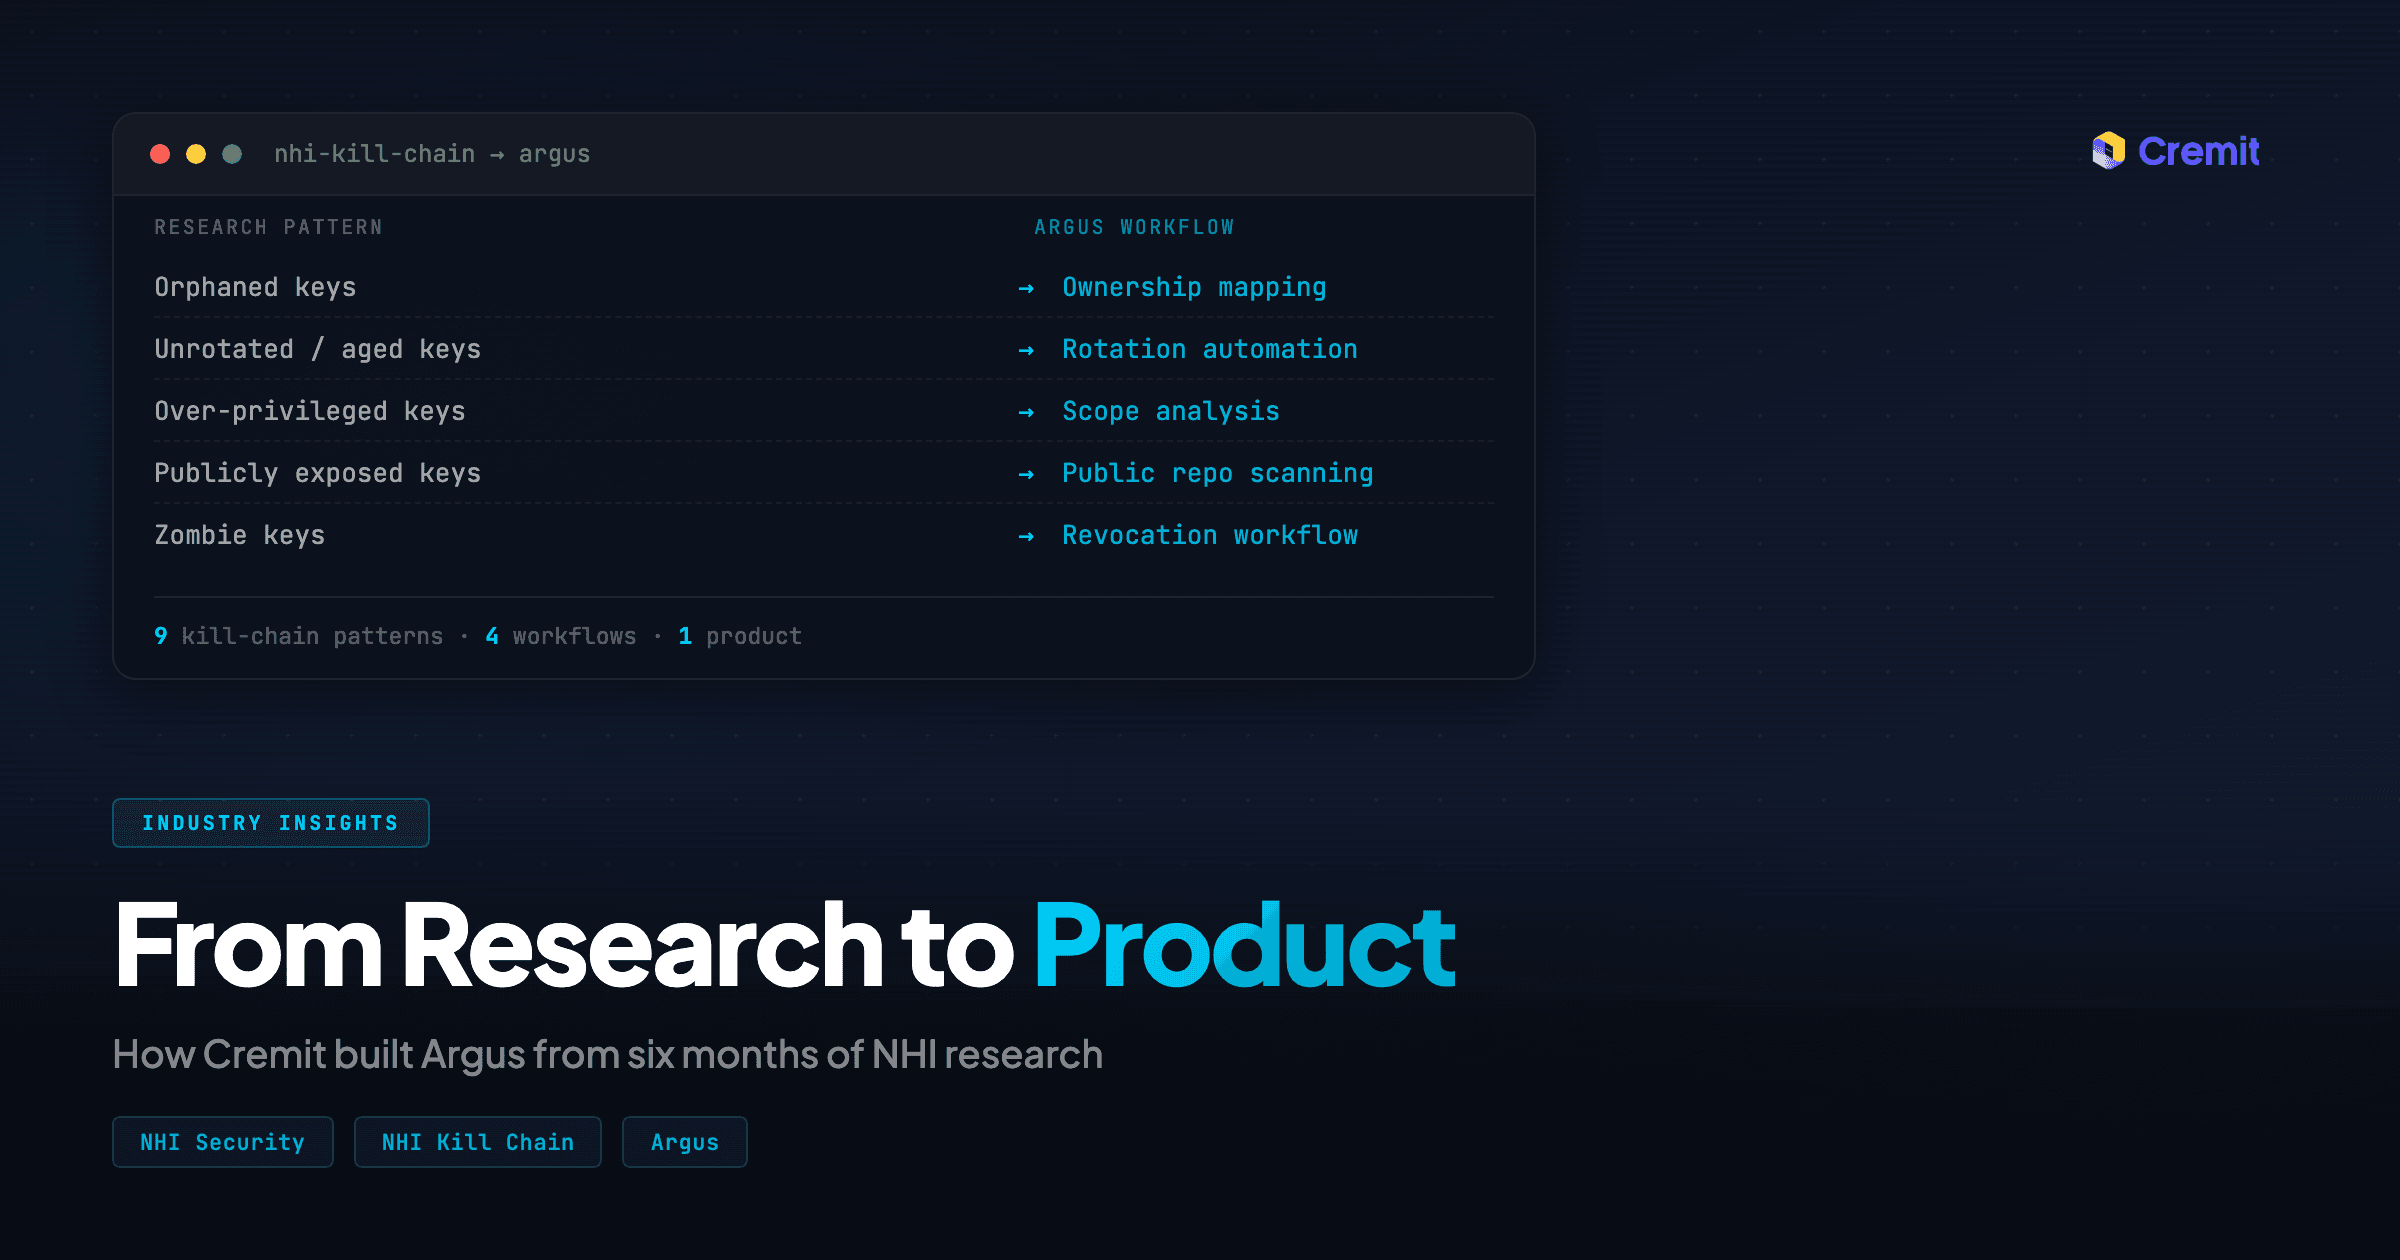
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
Oct 11, 2026

GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History

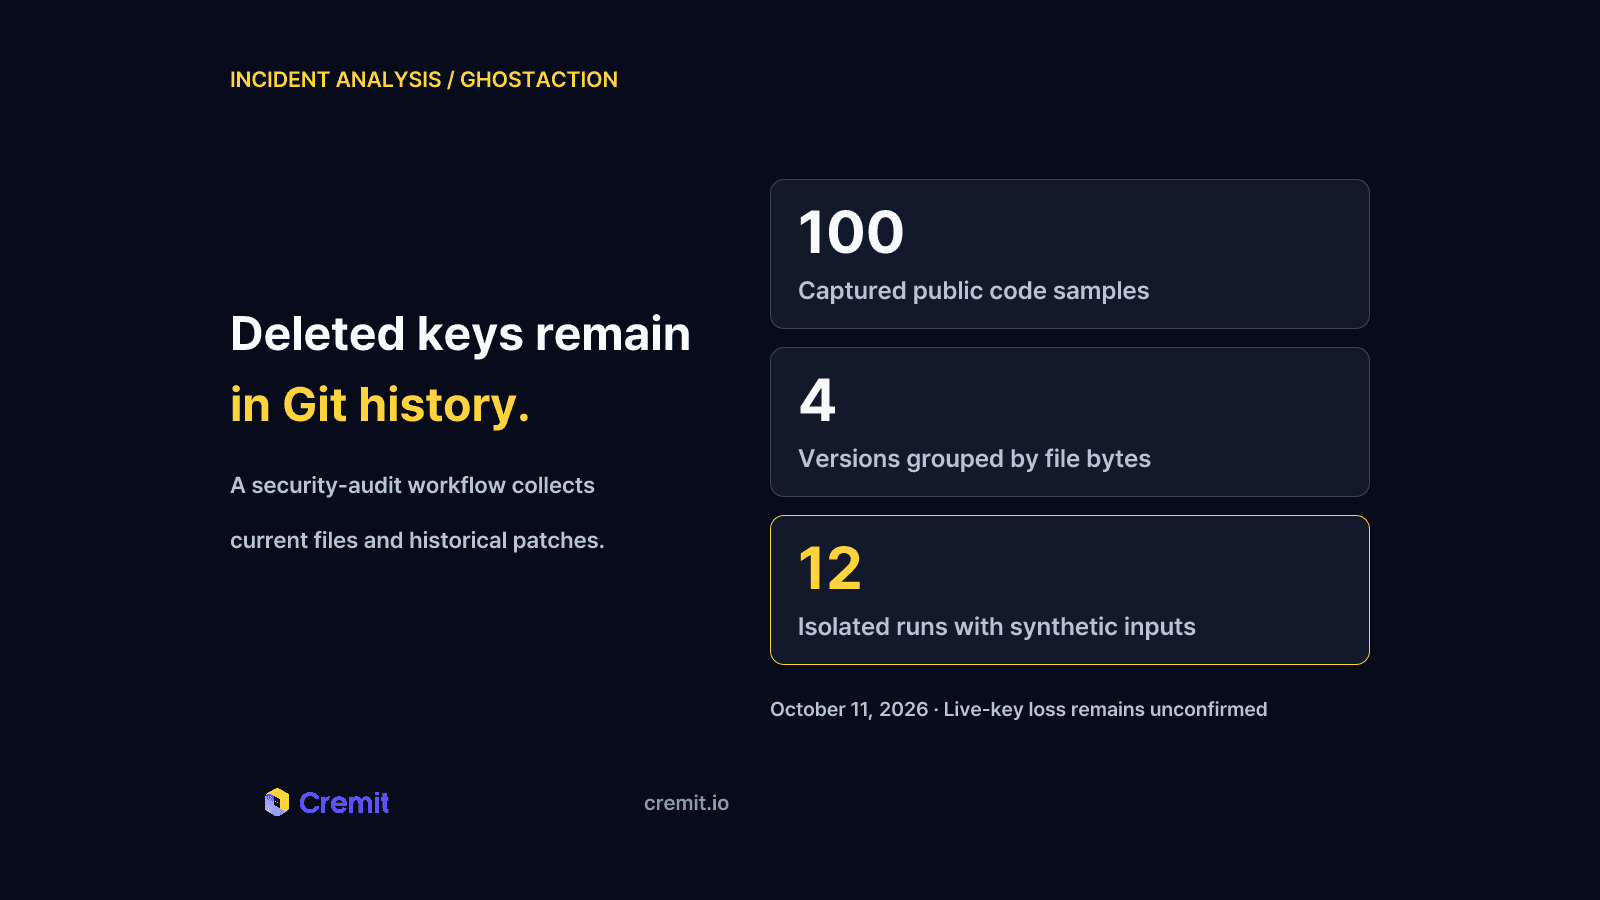
A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.

Ben Kim
Ben Kim
MCP Servers Are Taking API Keys Through the Chat Window
Oct 7, 2026

MCP Servers Are Taking API Keys Through the Chat Window

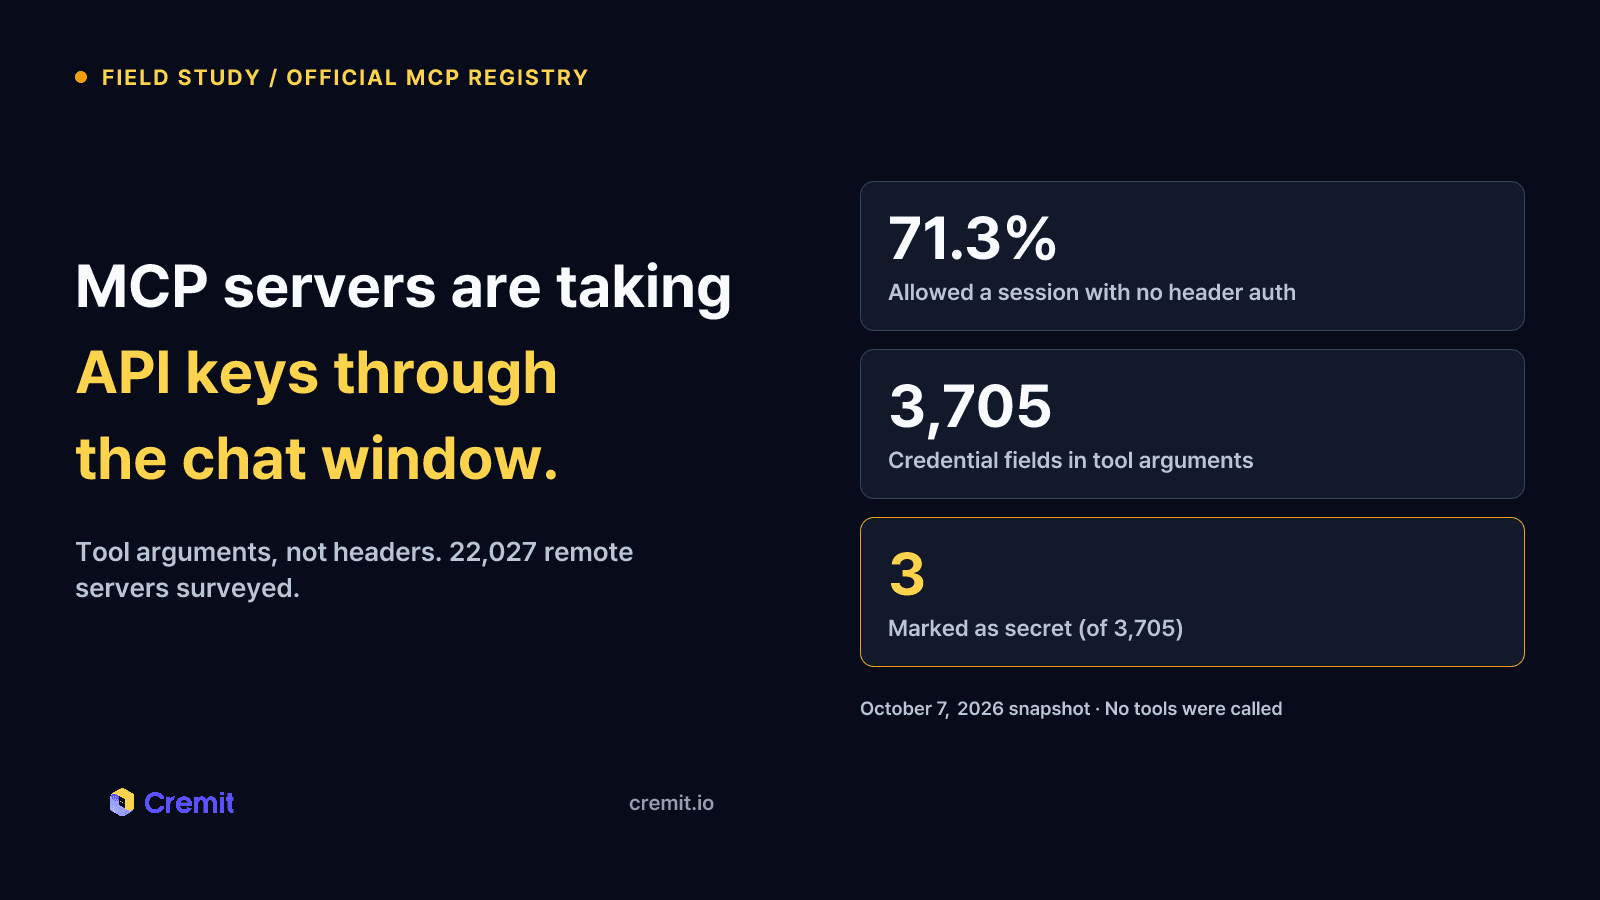
We sent one initialize request to every remote MCP server in the official registry. 71.3% of 22,027 responding servers opened a session with no header authentication, and 3,705 credential fields sit in tool arguments. Three of them are marked secret.

Ben Kim
Ben Kim
How to count live credentials without confusing matches and keys
Aug 5, 2026

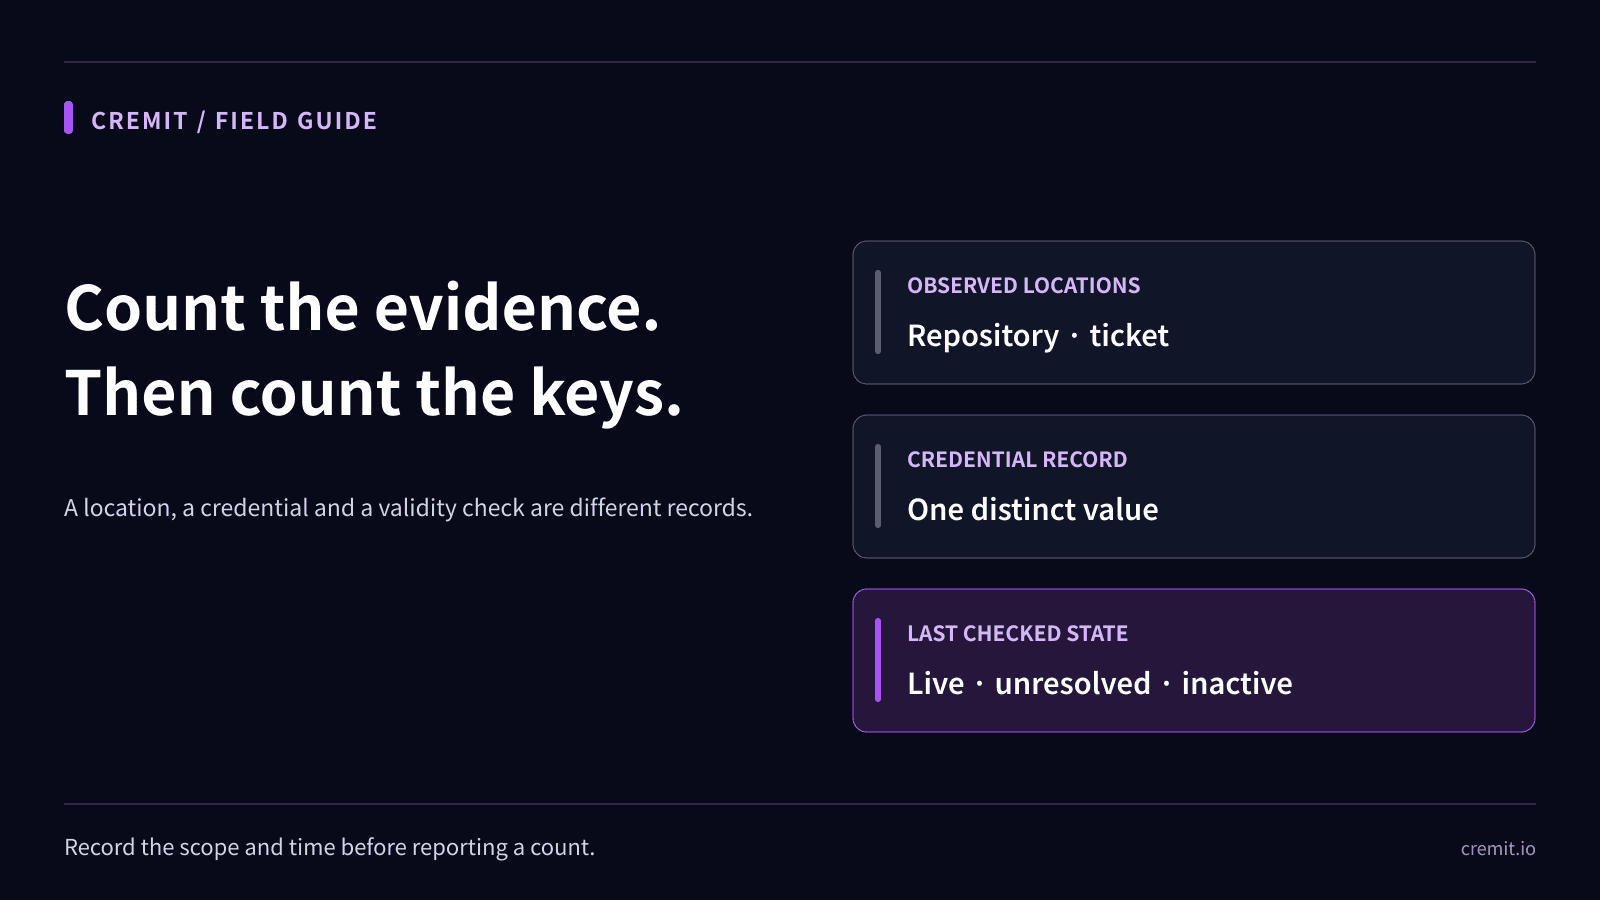
How to count live credentials without confusing matches and keys

Count observed locations, distinct credential records and verification states separately. Define scope and check time before reporting exposure.

Ben Kim
Ben Kim
From exposed credentials to Cremit Platform: the workflow we support
Jul 28, 2026

From exposed credentials to Cremit Platform: the workflow we support

How Cremit Platform finds exposed credentials, verifies supported types, and routes findings to an owner, with clear limits.

Ben Kim
Ben Kim
AI agent credentials: trace the tool, issuer and responder
Jul 19, 2026

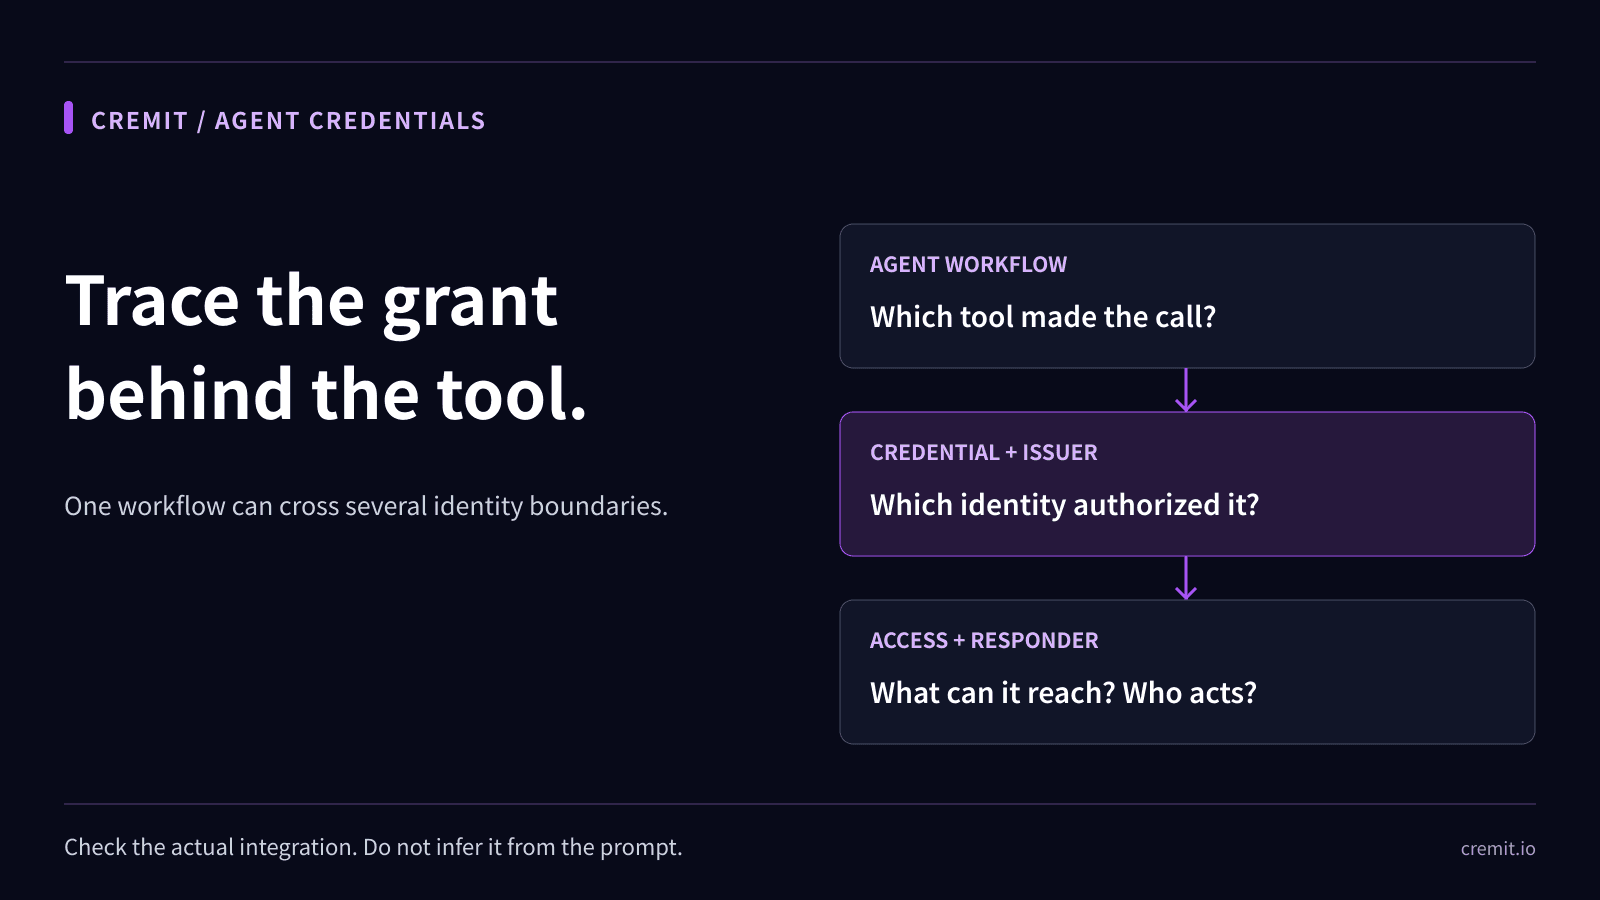
AI agent credentials: trace the tool, issuer and responder

An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.

Ben Kim
Ben Kim
The machine access behind an exposed API key
Jul 15, 2026

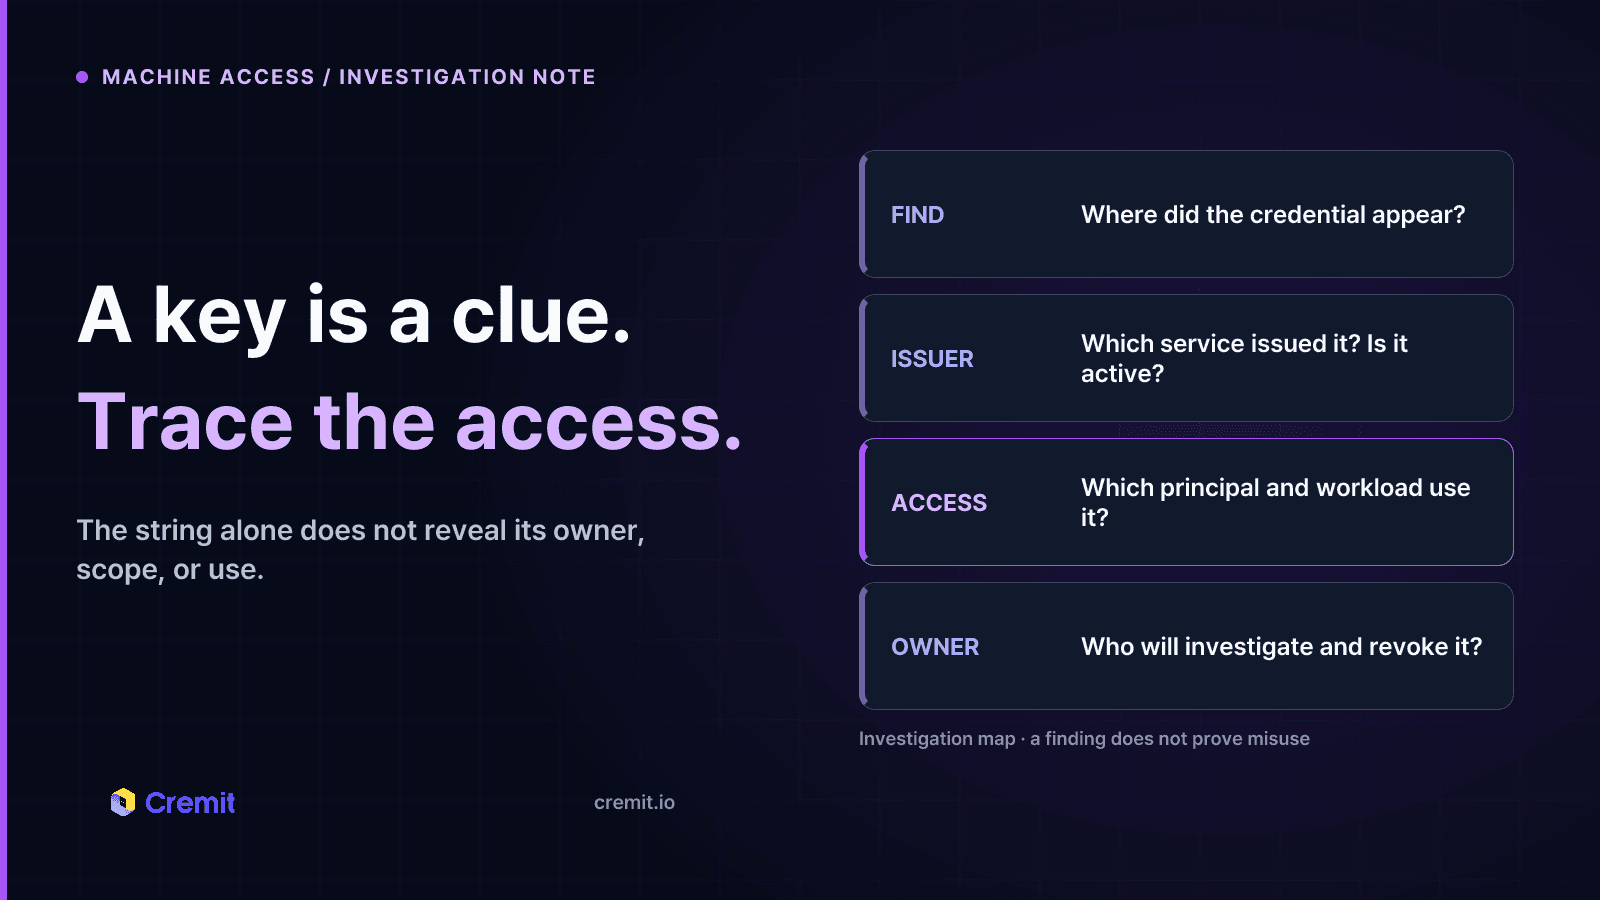
The machine access behind an exposed API key

An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.

Ben Kim
Ben Kim
When an exposed credential has no clear owner
Apr 20, 2026

When an exposed credential has no clear owner

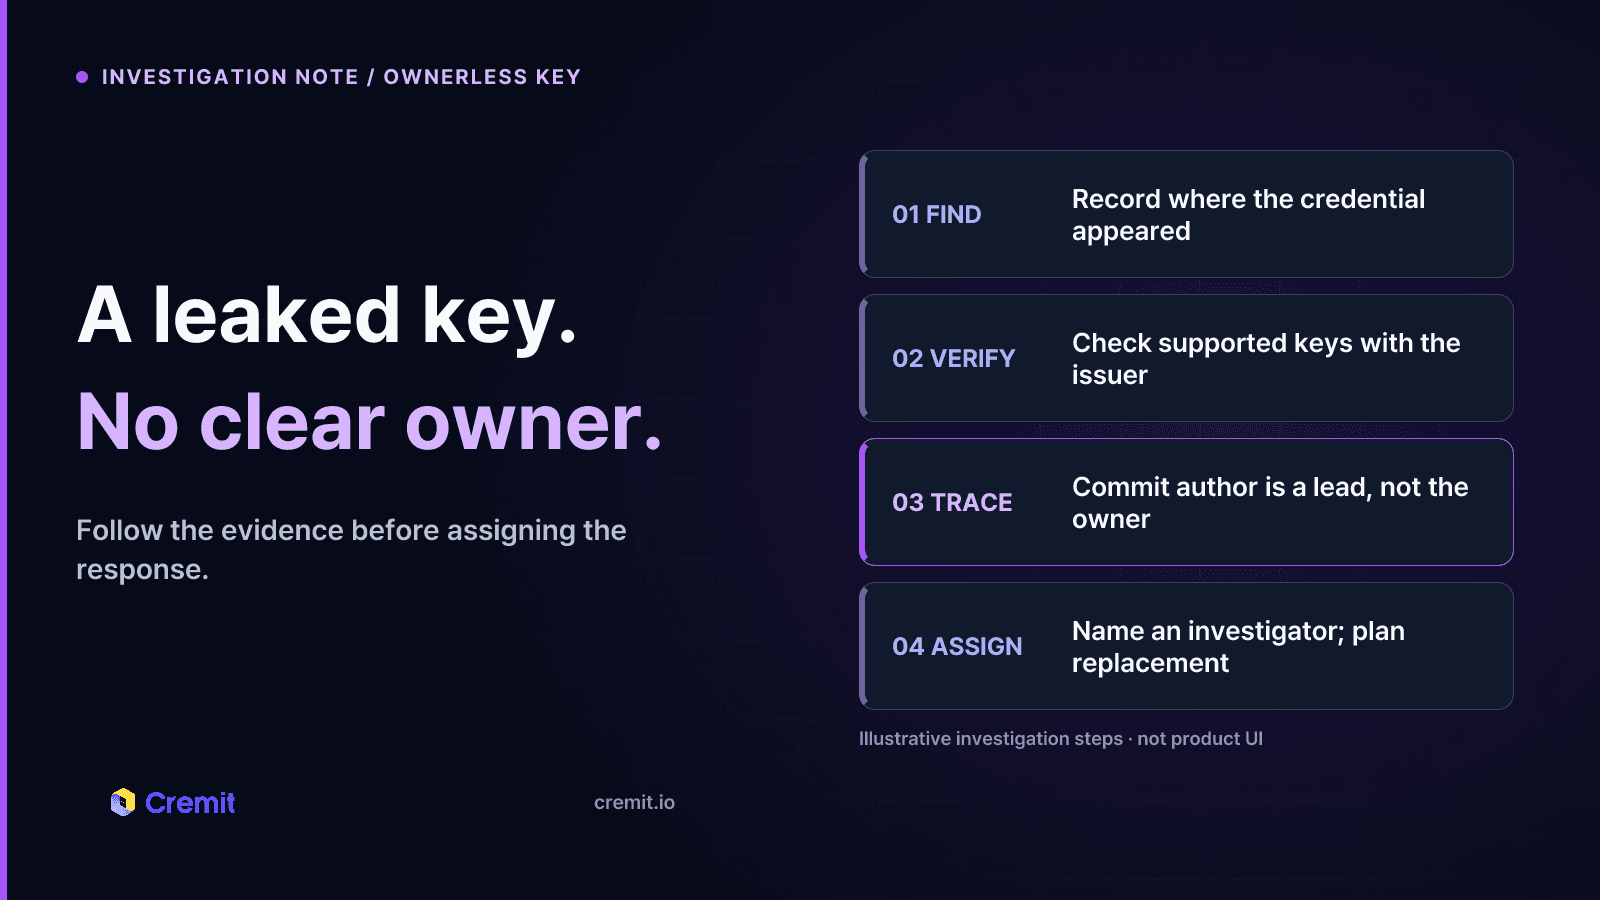
How to verify, investigate, assign, and replace an exposed credential when the service owner is unclear.

Ben Kim
Ben Kim
The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure
Apr 15, 2026

The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure

An organization's core credentials sat in public repositories for years. The security industry's answer: "Out of scope."

Ben Kim
Ben Kim
One API key in three repositories: investigating shared credentials
Apr 11, 2026

One API key in three repositories: investigating shared credentials

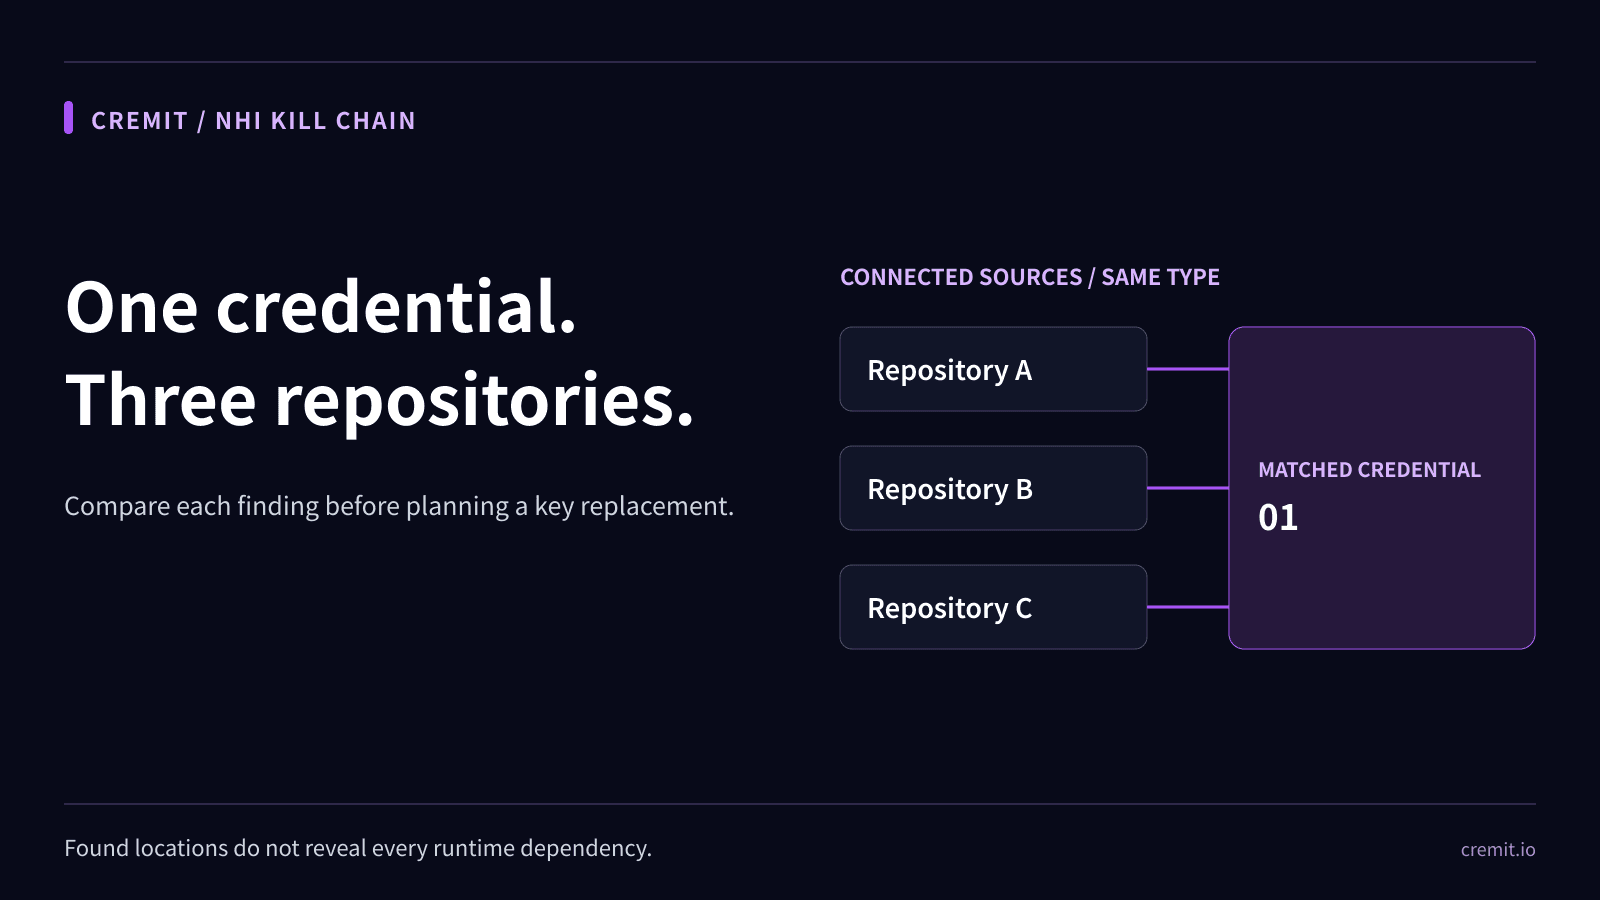
Three observed locations are not a complete dependency map. Check key type, issuer status, permissions, and actual consumers before replacement.

Ben Kim
Ben Kim
Long-exposed credentials: what a 90-day source record tells you
Apr 10, 2026

Long-exposed credentials: what a 90-day source record tells you

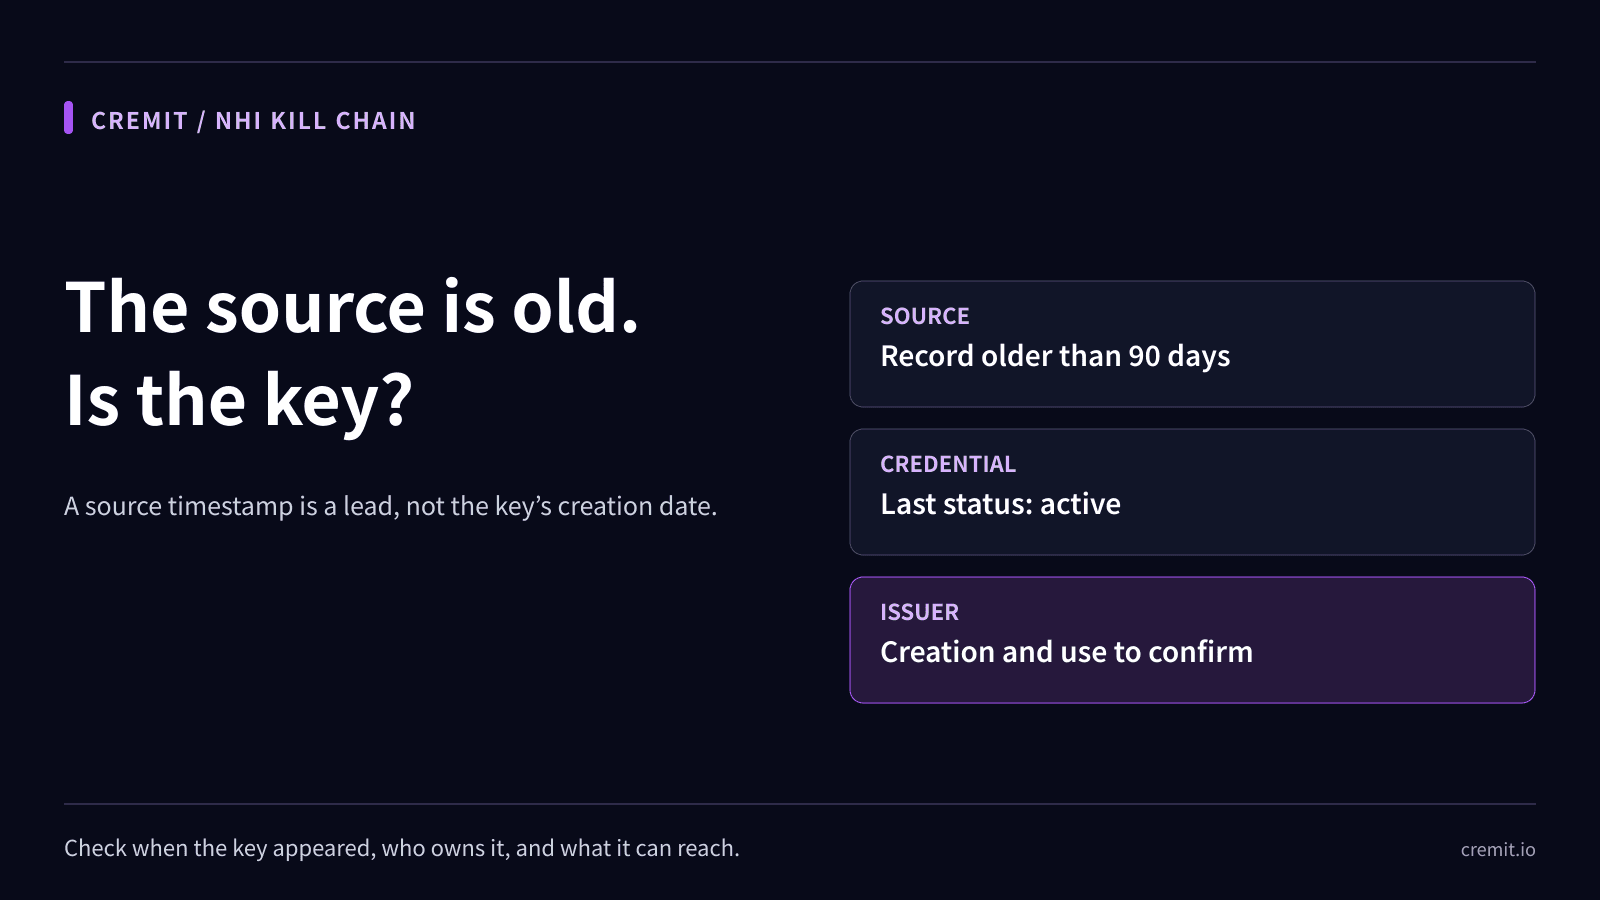
An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.

Ben Kim
Ben Kim
Orphaned API keys after offboarding: what the evidence shows
Apr 2, 2026

Orphaned API keys after offboarding: what the evidence shows

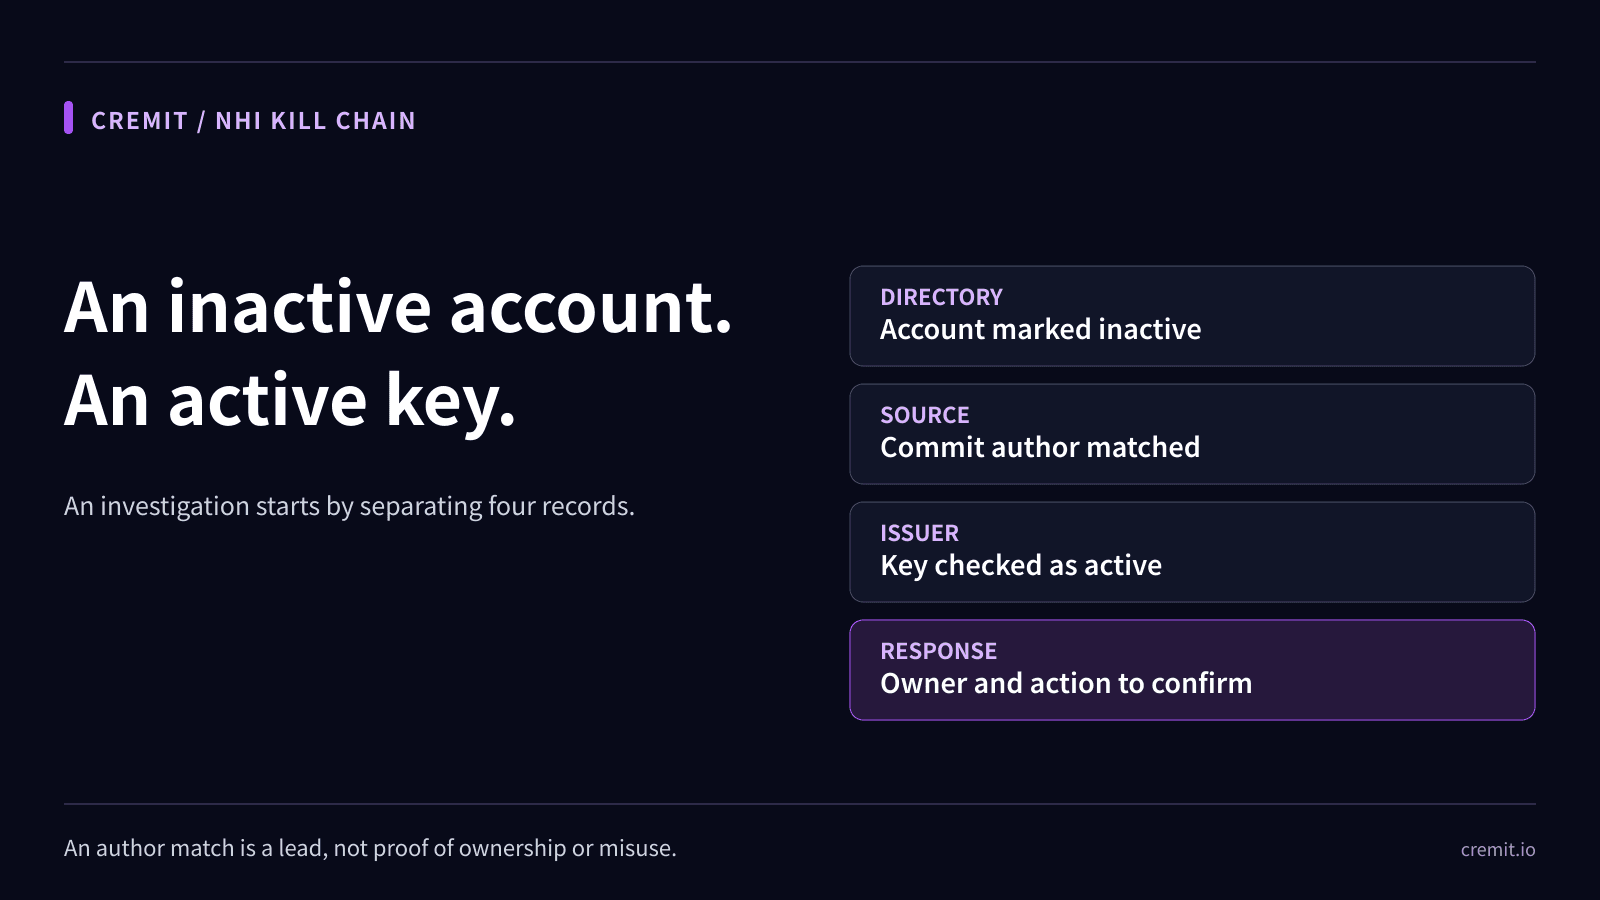
An active key linked to an inactive author is a lead. Check the directory, source, issuer, and current service owner before deciding what happened.

Ben Kim
Ben Kim
Public API key in a repository: what to check first
Mar 17, 2026

Public API key in a repository: what to check first

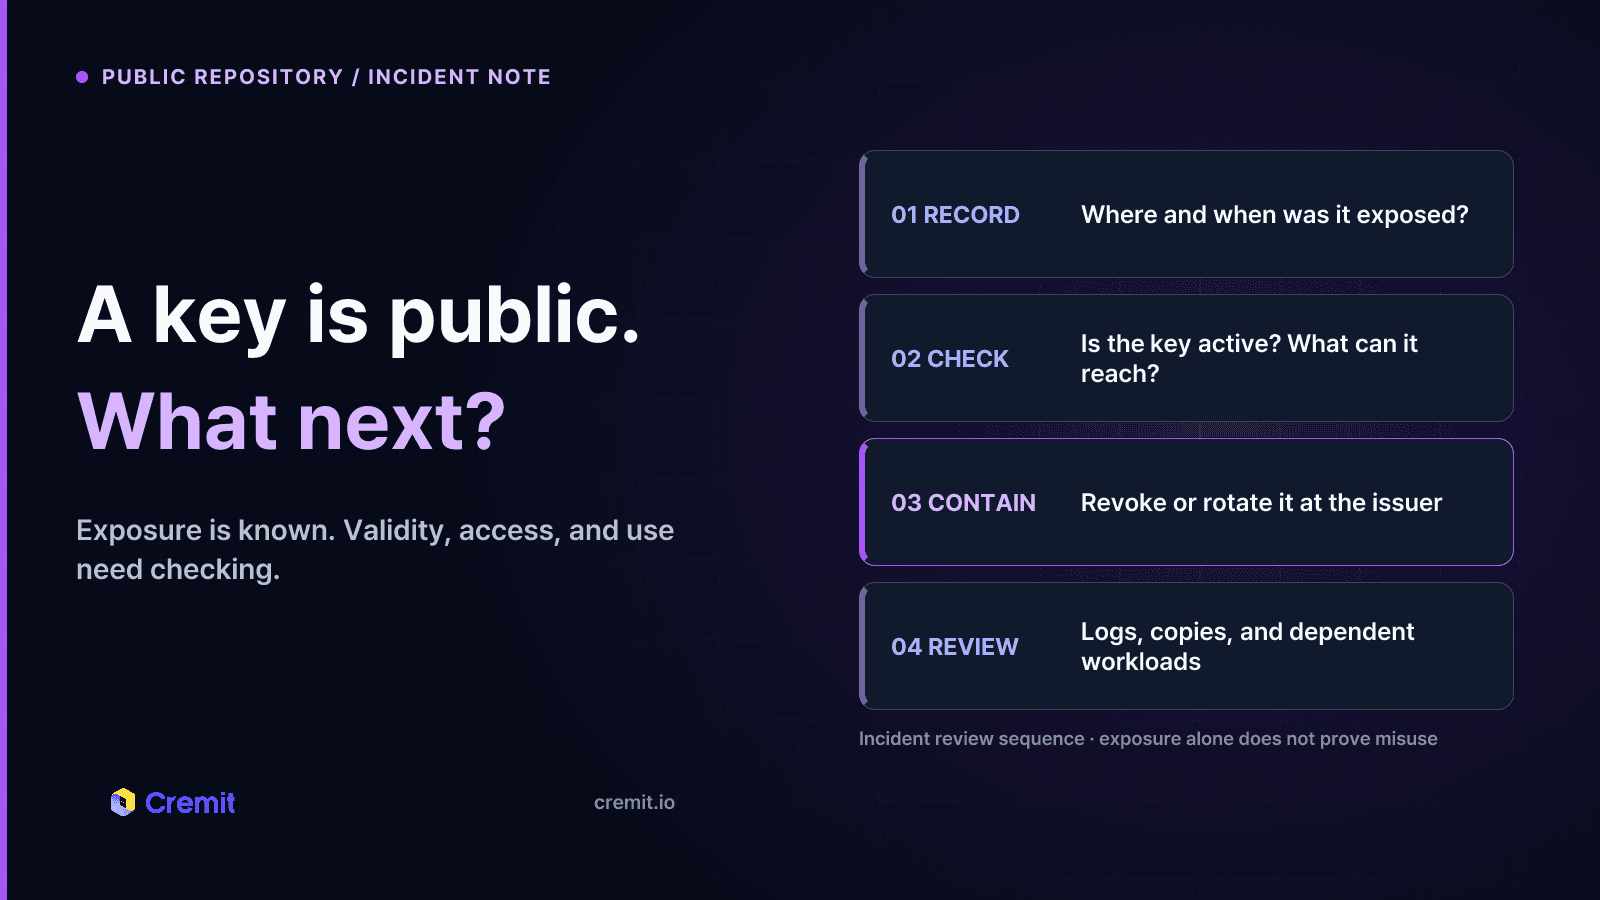
A public commit proves exposure, not misuse. Check validity, permissions, issuer logs, and dependent workloads before closing the incident.

Ben Kim
Ben Kim
Clinejection: prompt injection and the unauthorized Cline CLI release
Mar 7, 2026

Clinejection: prompt injection and the unauthorized Cline CLI release

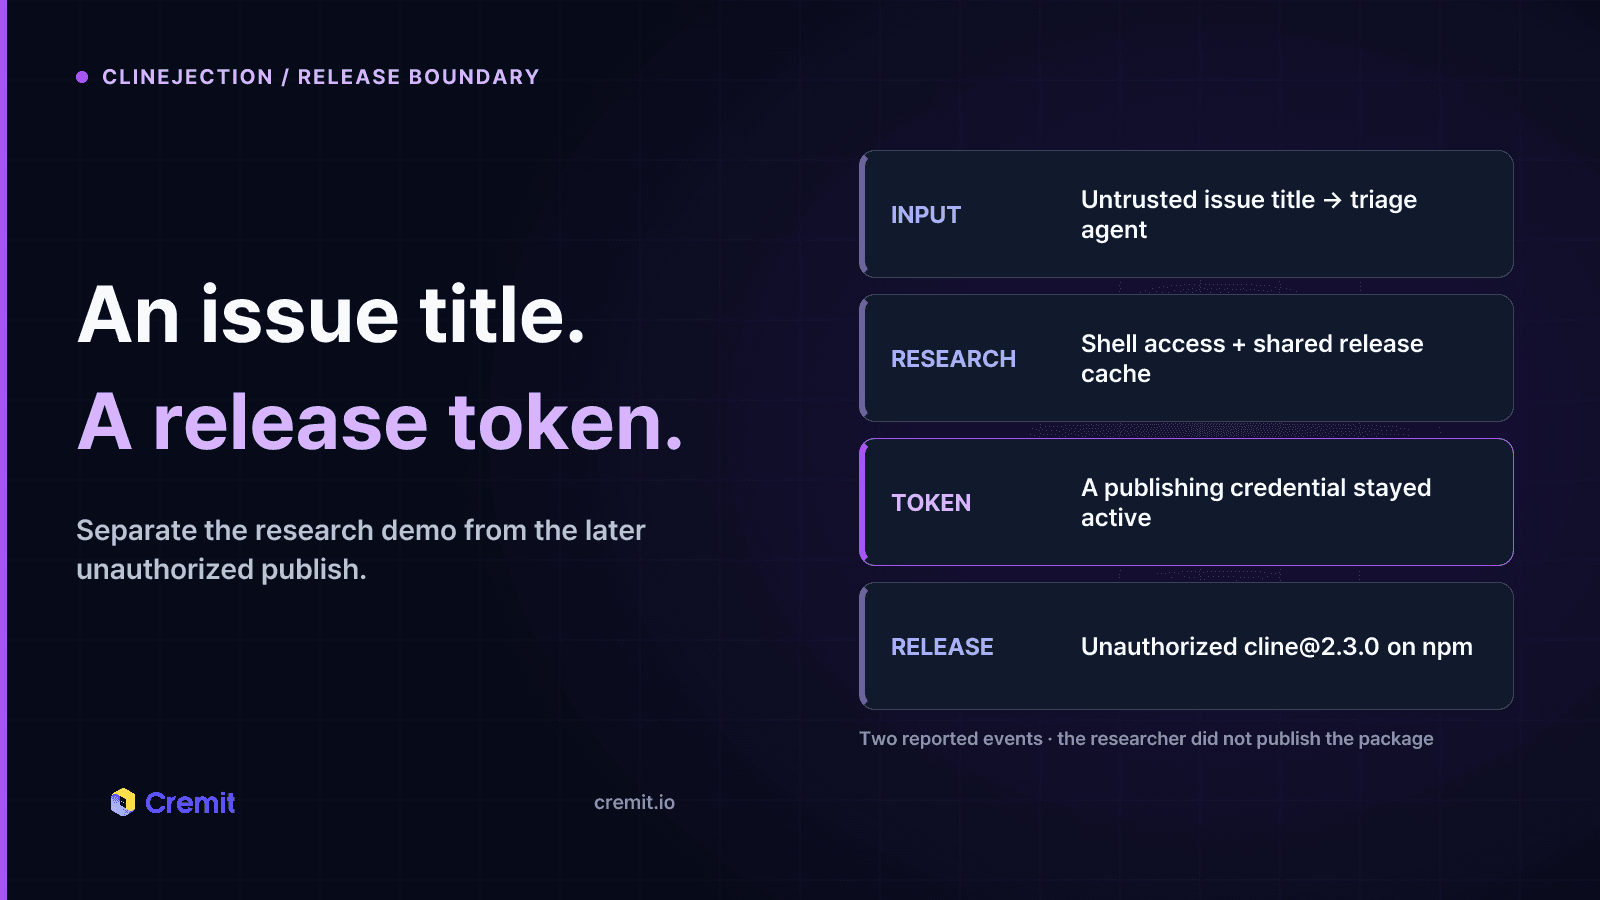
Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.

Ben Kim
Ben Kim
Can You Prove a Leaked API Key Was Sold?
Dec 26, 2025

Can You Prove a Leaked API Key Was Sold?

A public leak, a valid key, and evidence of misuse are different findings. Here is how to investigate each without claiming a sale you cannot prove.

Ben Kim
Ben Kim
API Keys | Cremit Blog | Cremit