Jul 15, 2026
The machine access behind an exposed API key
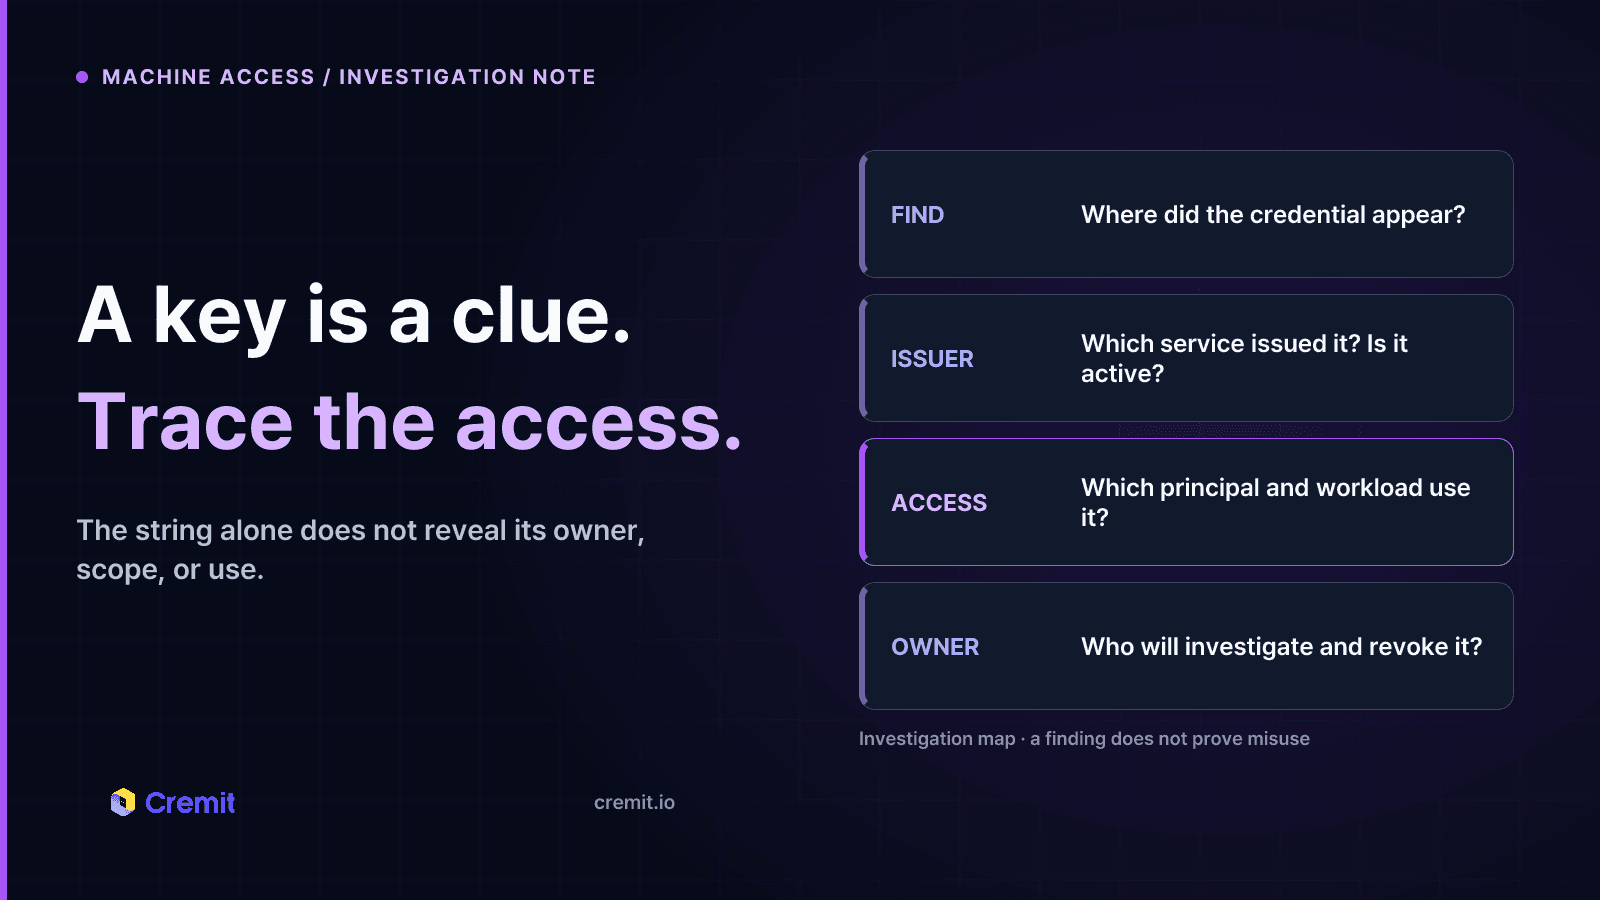
An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.

Ben Kim
An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.
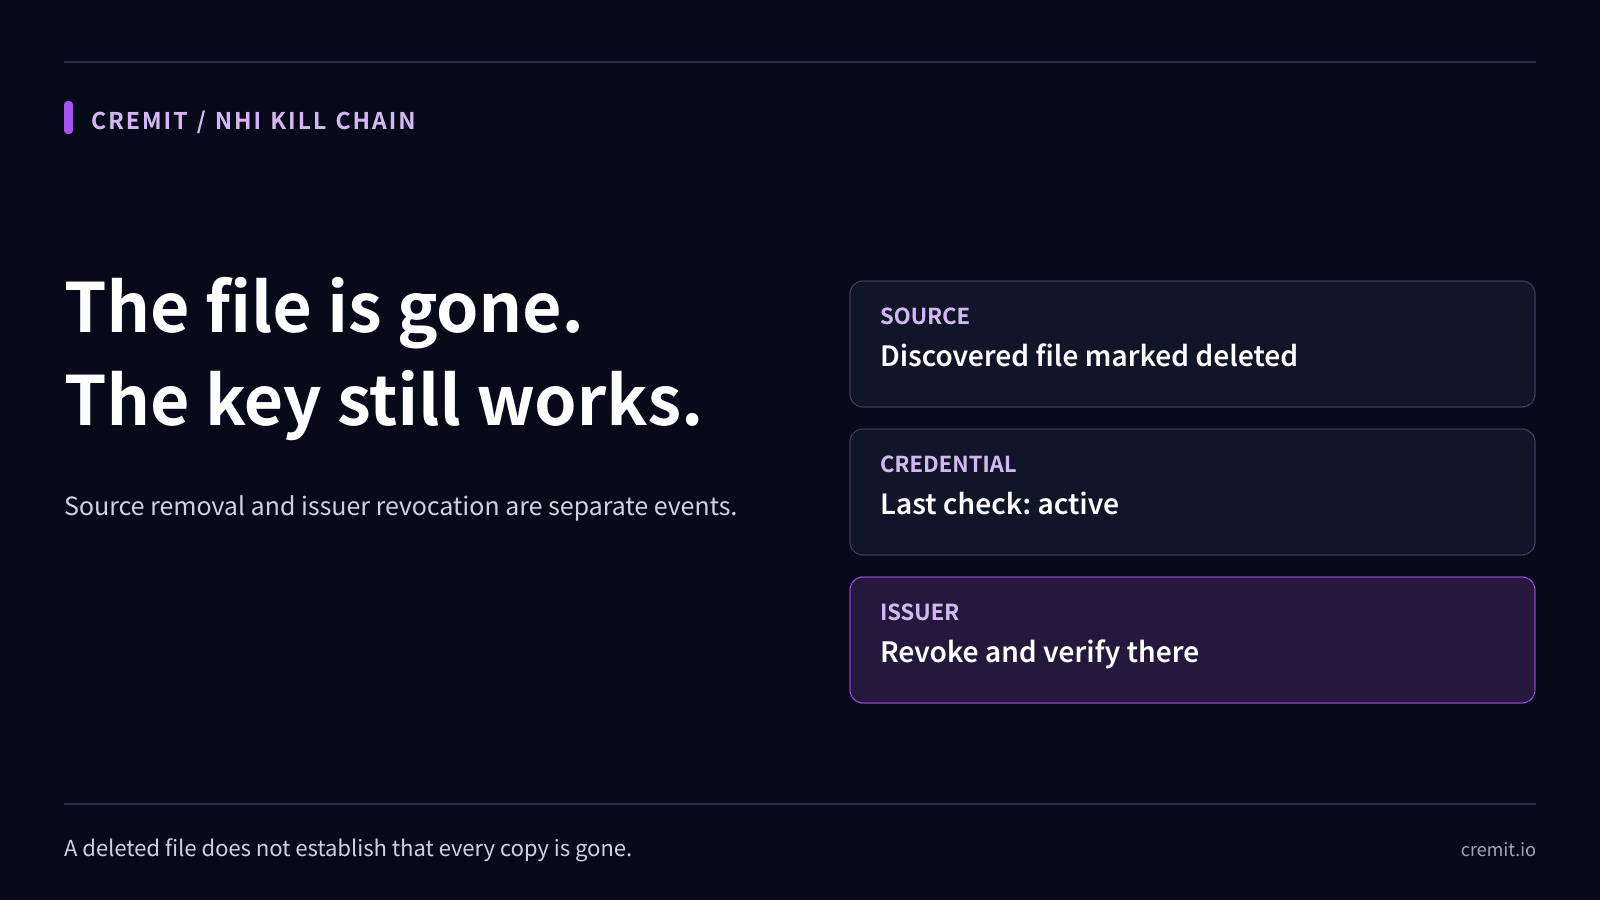
Source removal does not revoke a credential. Check the issuer, Git history, current owner, and last verification before closing the finding.
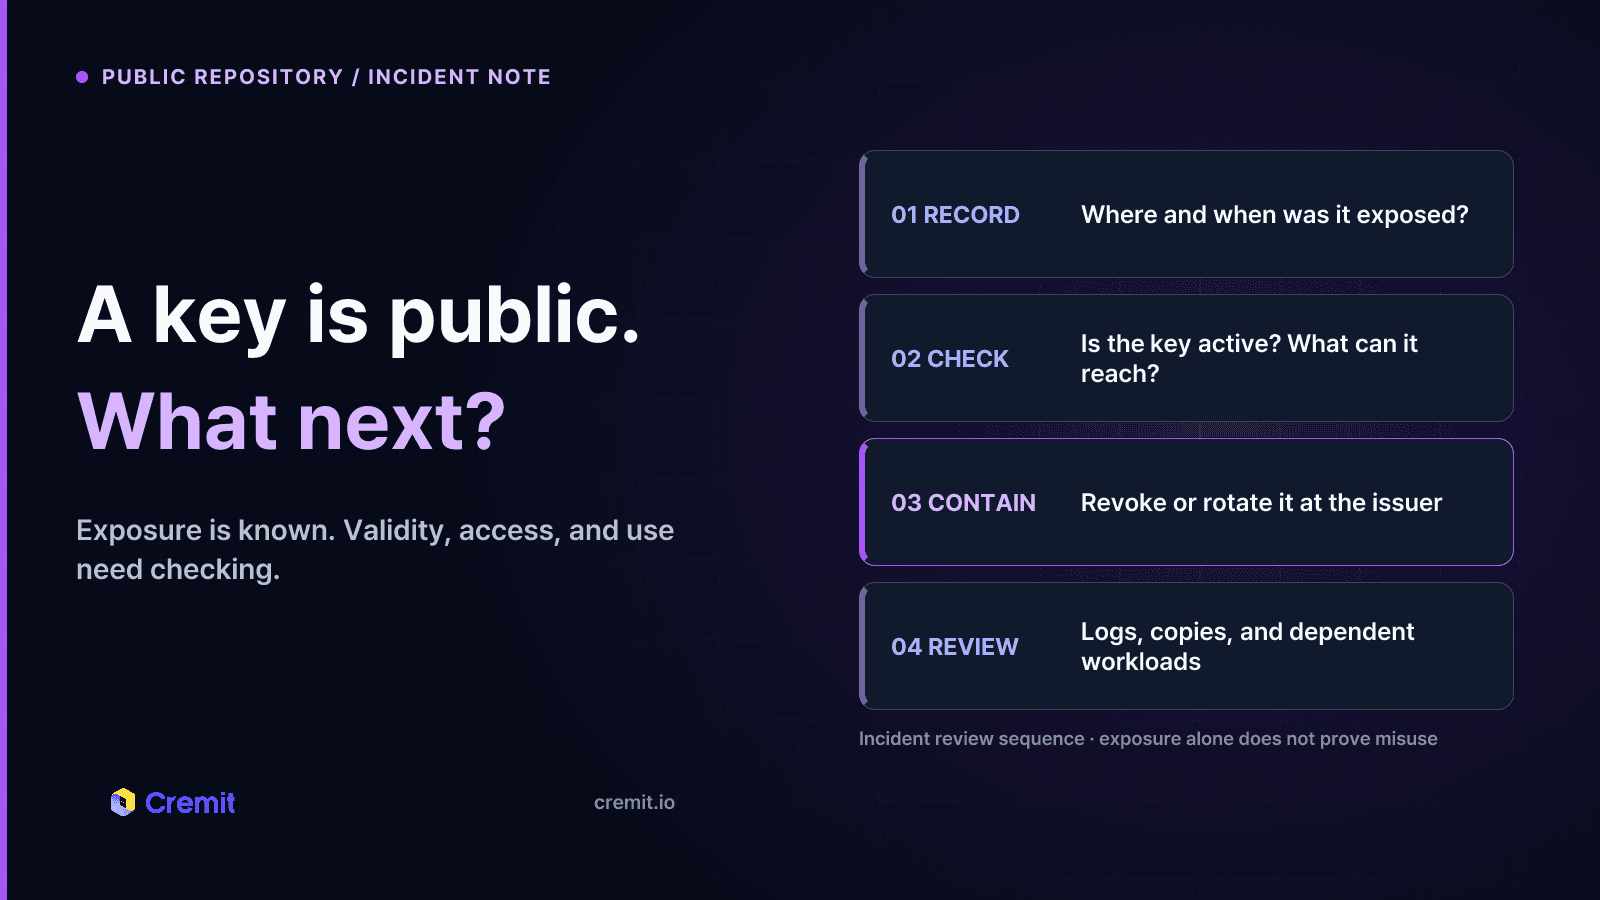
A public commit proves exposure, not misuse. Check validity, permissions, issuer logs, and dependent workloads before closing the incident.
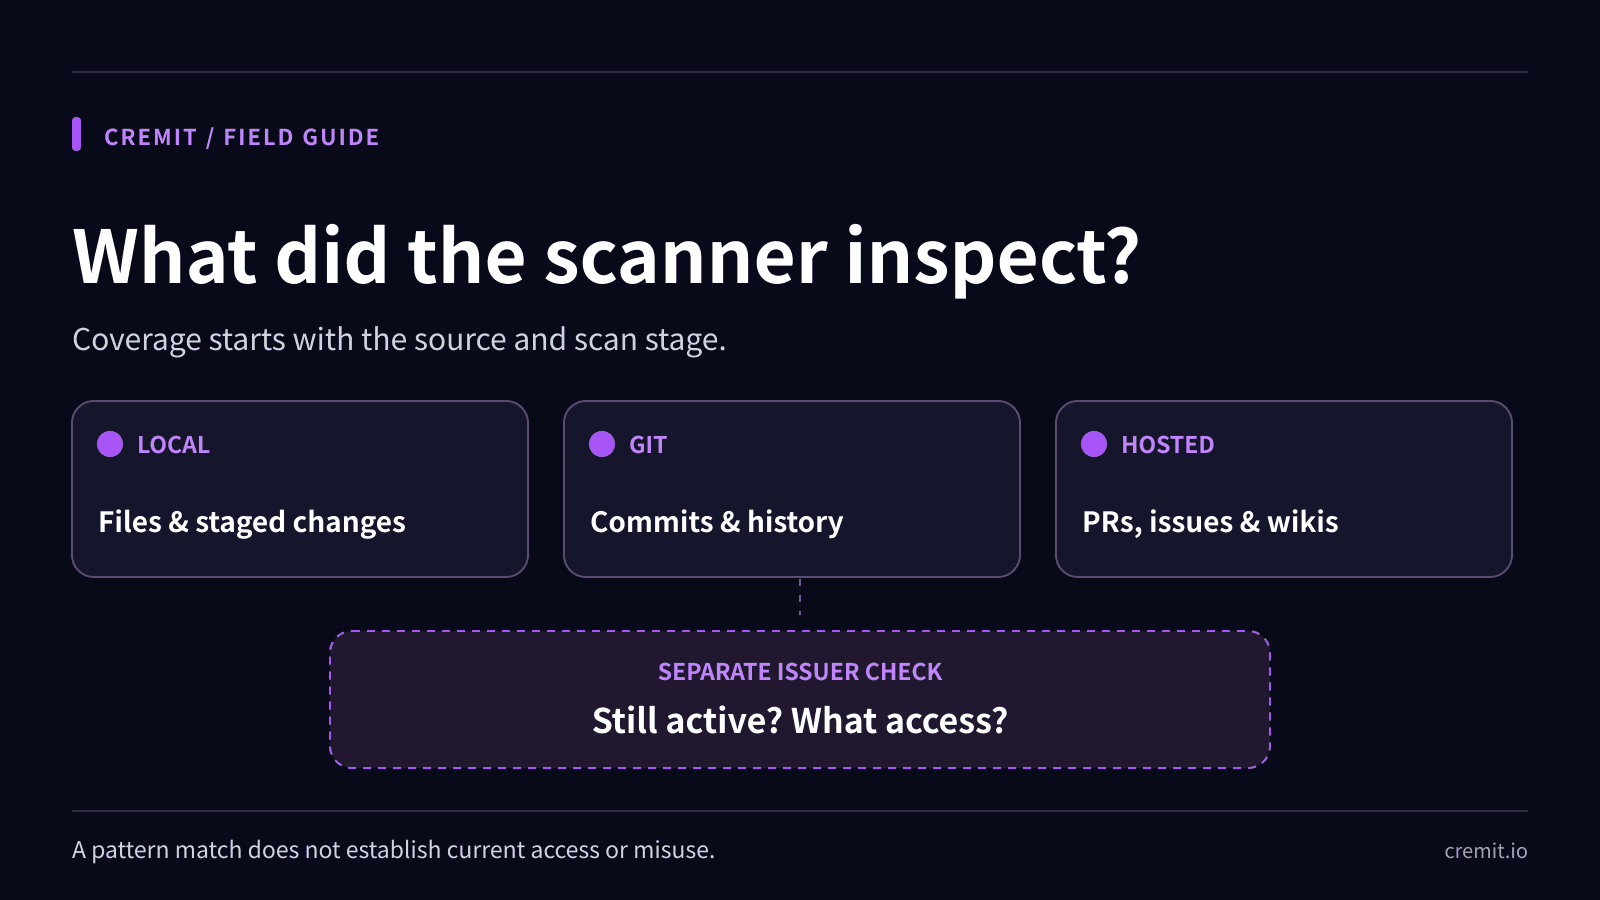
A practical guide to push protection, history scans, validity checks, and issuer-side response, with GitHub, GitLab, and Gitleaks source links.
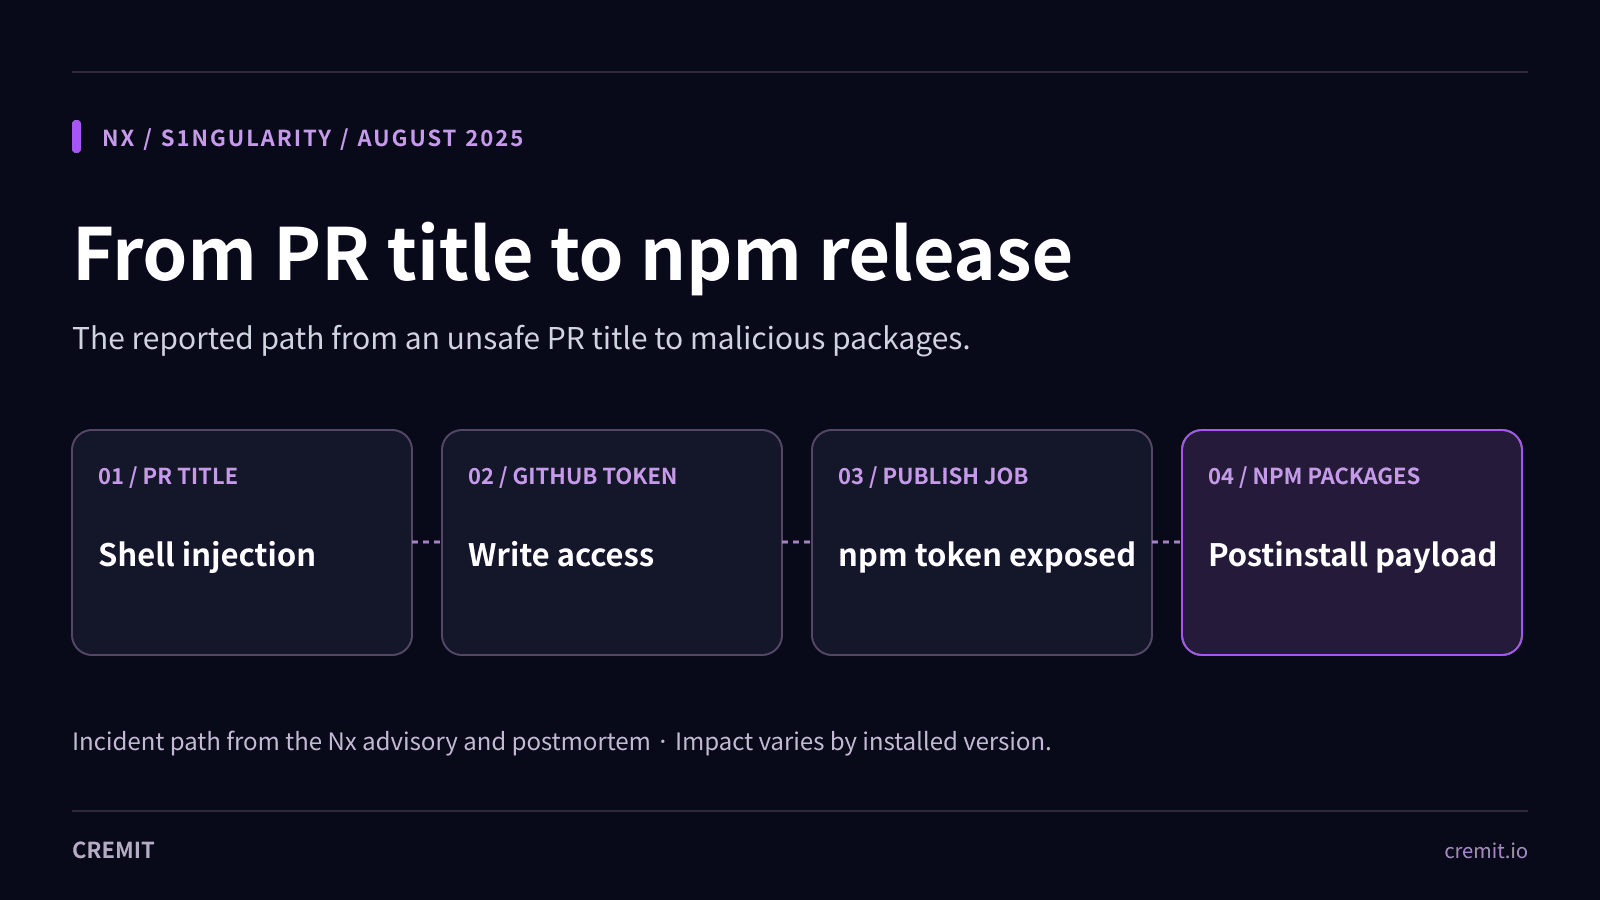
The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy