ProductSecret context graph
Trace one secret through its evidence.
Start with a detected key. Its graph links the locations where it appeared, who authored those source records, the current owner status, and any available permission or incident context. Each link answers a different question.
- Incident responder
- Security analyst
- Service owner
Who does the work
The people this feature hands work to, and what each of them does with it.
Incident responder
Follows recorded locations to investigate copies while arranging prompt containment.
Security analyst
Reads the permission context to judge how far a leak could reach.
Service owner
Checks which services depend on the key before it is replaced.
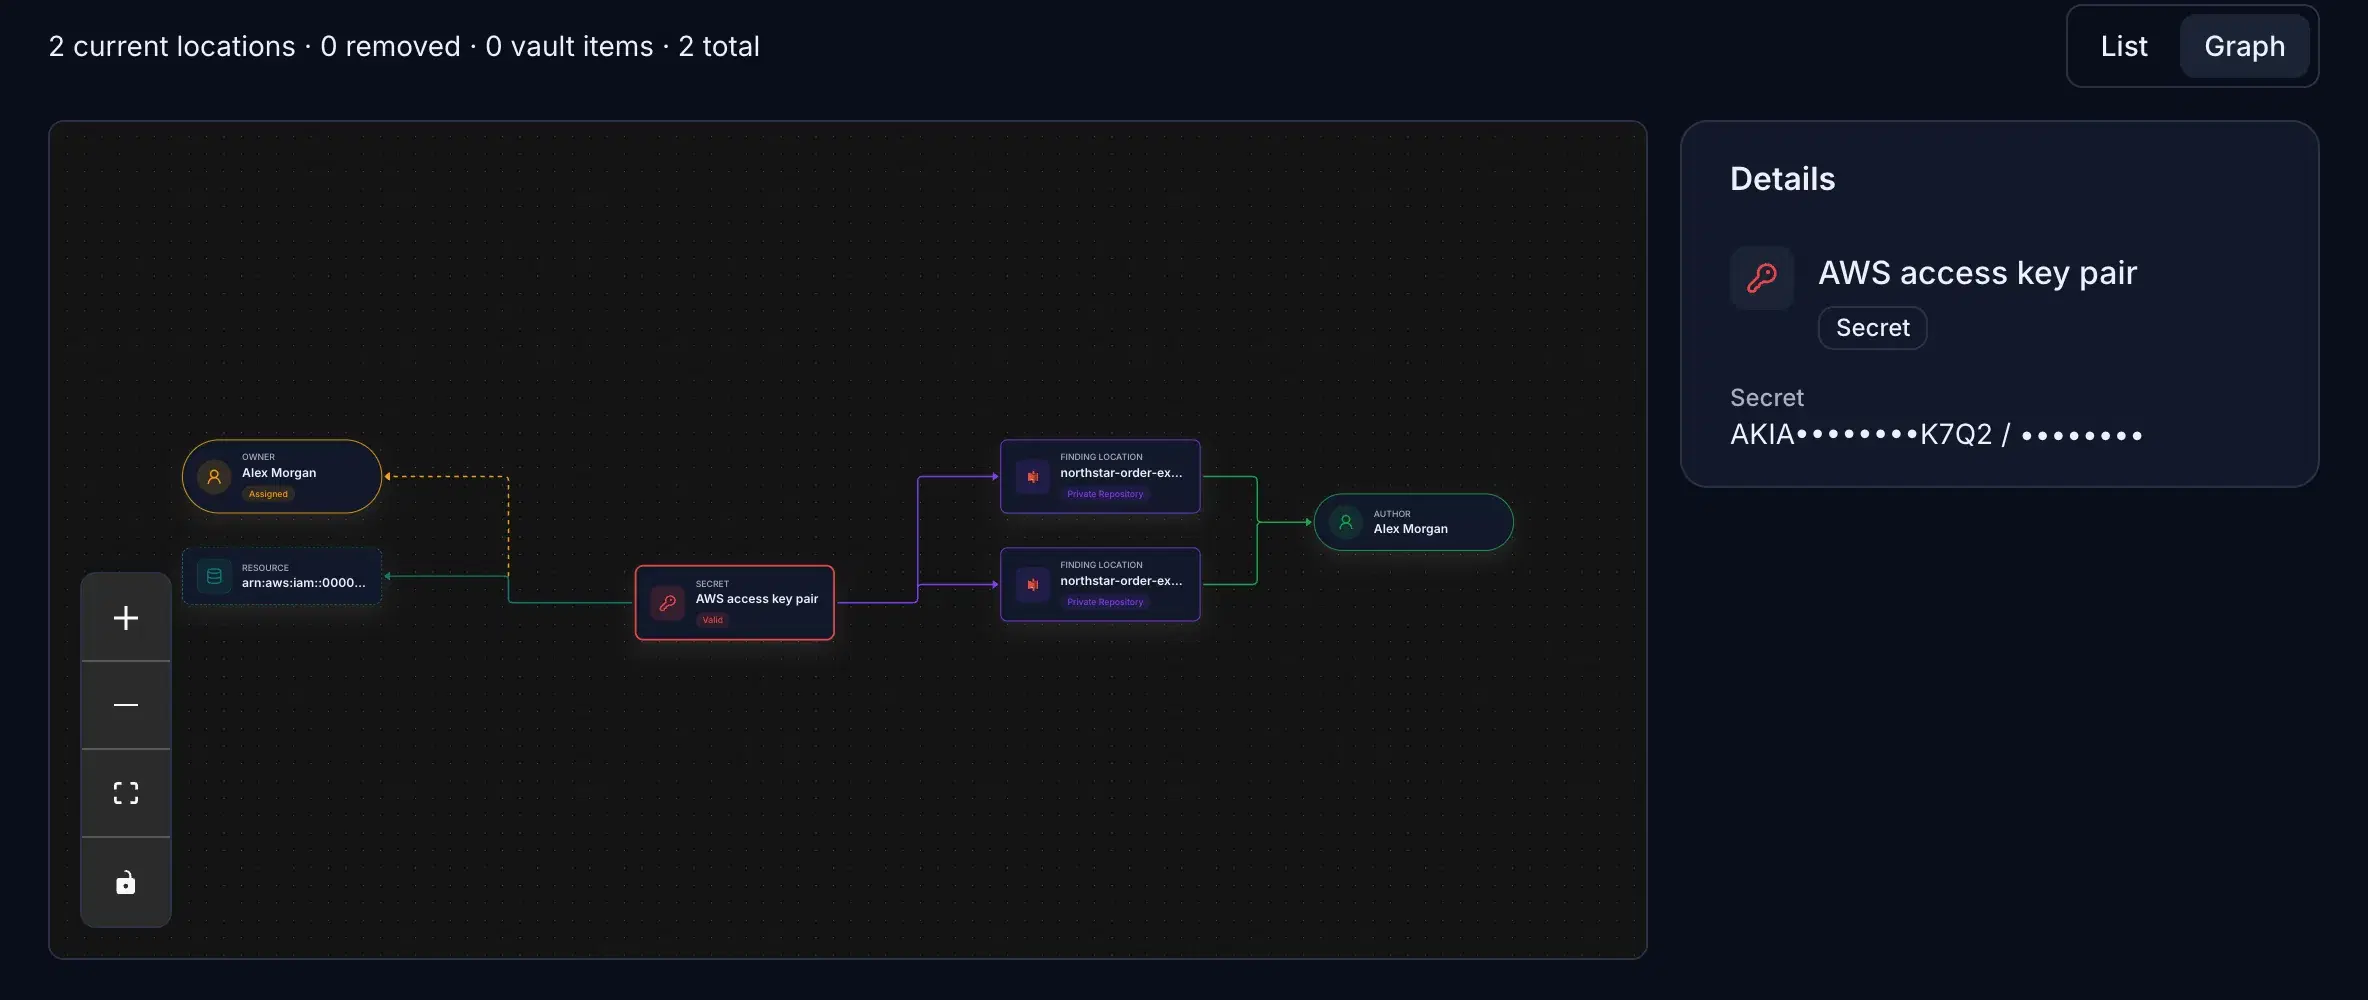
Relationships around one secret
FOUND_INDetected locationA connected source record where the secret was found.
AUTHORED_BYSource authorThe person or account recorded on a location; not necessarily today’s owner.
OWNED_BYOwner statusA suggested candidate or an explicit assignment; check which one you have.
CAN_ACCESSPermission contextAvailable principal or API-target data from supported analysis, when present.
RELATED_INCIDENTLinked responseAn incident connected to the secret, if one exists.
Read the links before making a decision
The graph groups clues for an investigation. It does not replace issuer records or a confirmed service owner.
01
Where was the secret found?
Open the connected source location and note its visibility and observation time. A source author describes that record; it may not identify who runs the dependent service.
02
Who is responsible now?
Distinguish an inferred owner from a person explicitly assigned to the secret. If the record is unassigned or points to an inactive account, confirm the current responder.
03
What access is supported by evidence?
For AWS access keys and GCP API keys, inspect available permission analysis with the required integration. Resource nodes may describe a principal or an API target; issuer logs are needed to establish actual use.
04
What happens after review?
If a sensitive key is clearly exposed, contain it at the issuer without waiting for a complete graph. Assign the response, update dependent services, record the action and recheck supported validity results.
Follow one real finding
Open a detected secret and separate the location, author, owner, permission and response links before deciding what to do.