NEW · Blast Radius: a field playbook for leaked API keys on AWS, GCP and Azure
Back to Blog
Tag

NHI Security

42 posts
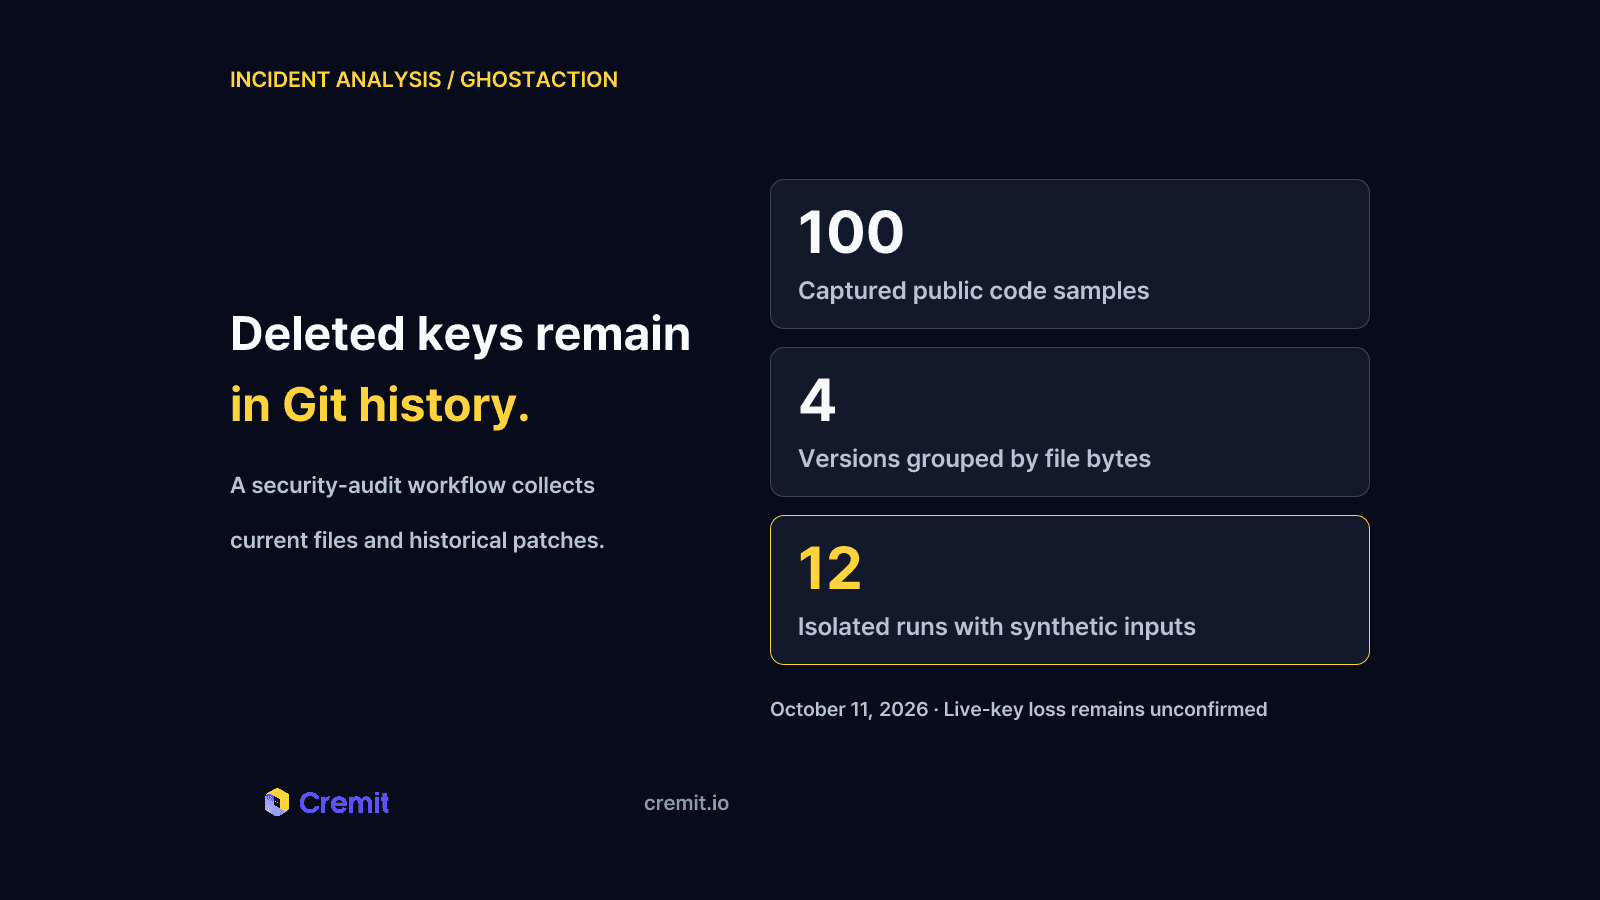
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
Oct 11, 2026

GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History

A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.

Ben Kim
Ben Kim
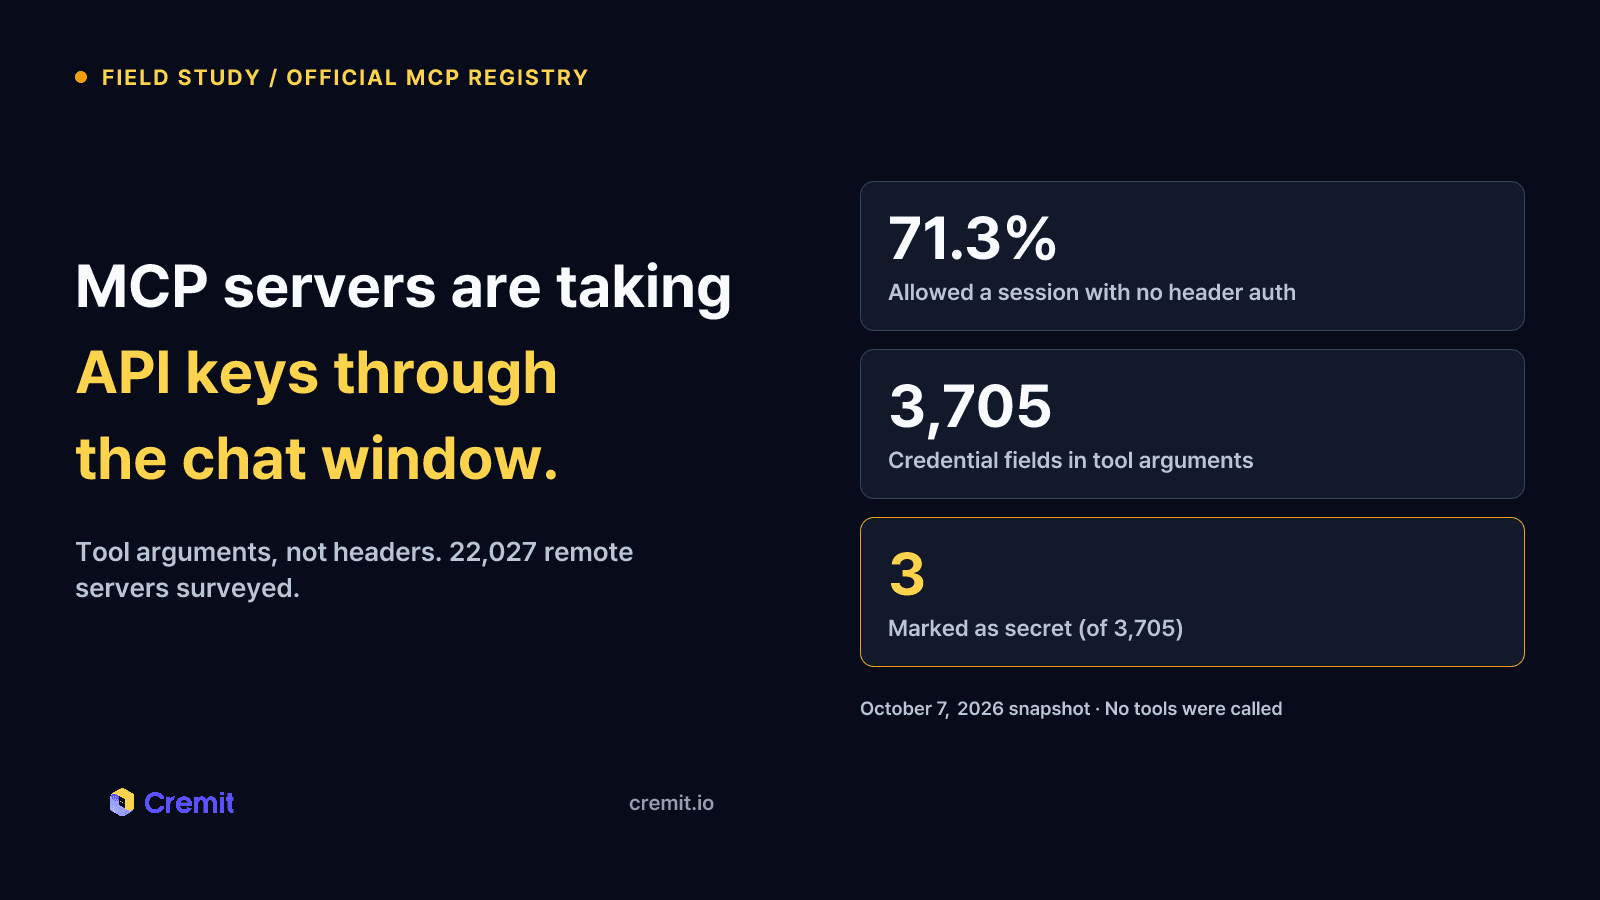
MCP Servers Are Taking API Keys Through the Chat Window
Oct 7, 2026

MCP Servers Are Taking API Keys Through the Chat Window

We sent one initialize request to every remote MCP server in the official registry. 71.3% of 22,027 responding servers opened a session with no header authentication, and 3,705 credential fields sit in tool arguments. Three of them are marked secret.

Ben Kim
Ben Kim
Unlisted, Not Private
Sep 18, 2026

Unlisted, Not Private

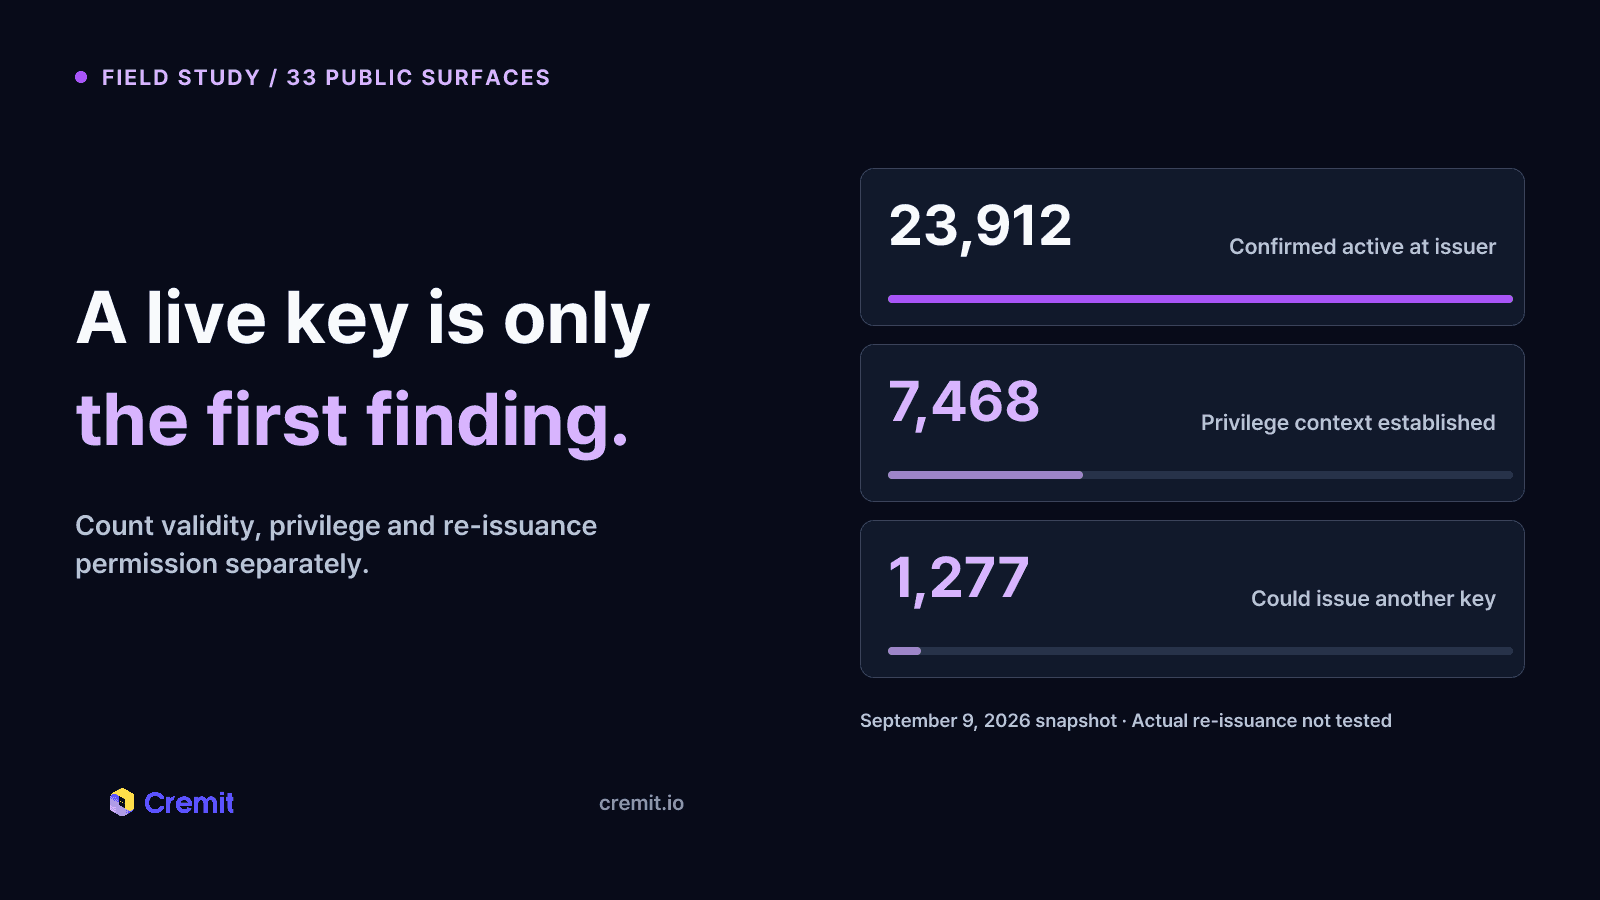
A September 2026 sweep of 33 public surfaces confirmed 23,912 active credentials. Privilege context was established for 7,468; 1,277 had permission to issue another key. Actual re-issuance was not tested.

Ben Kim
Ben Kim
How to count live credentials without confusing matches and keys
Aug 5, 2026

How to count live credentials without confusing matches and keys

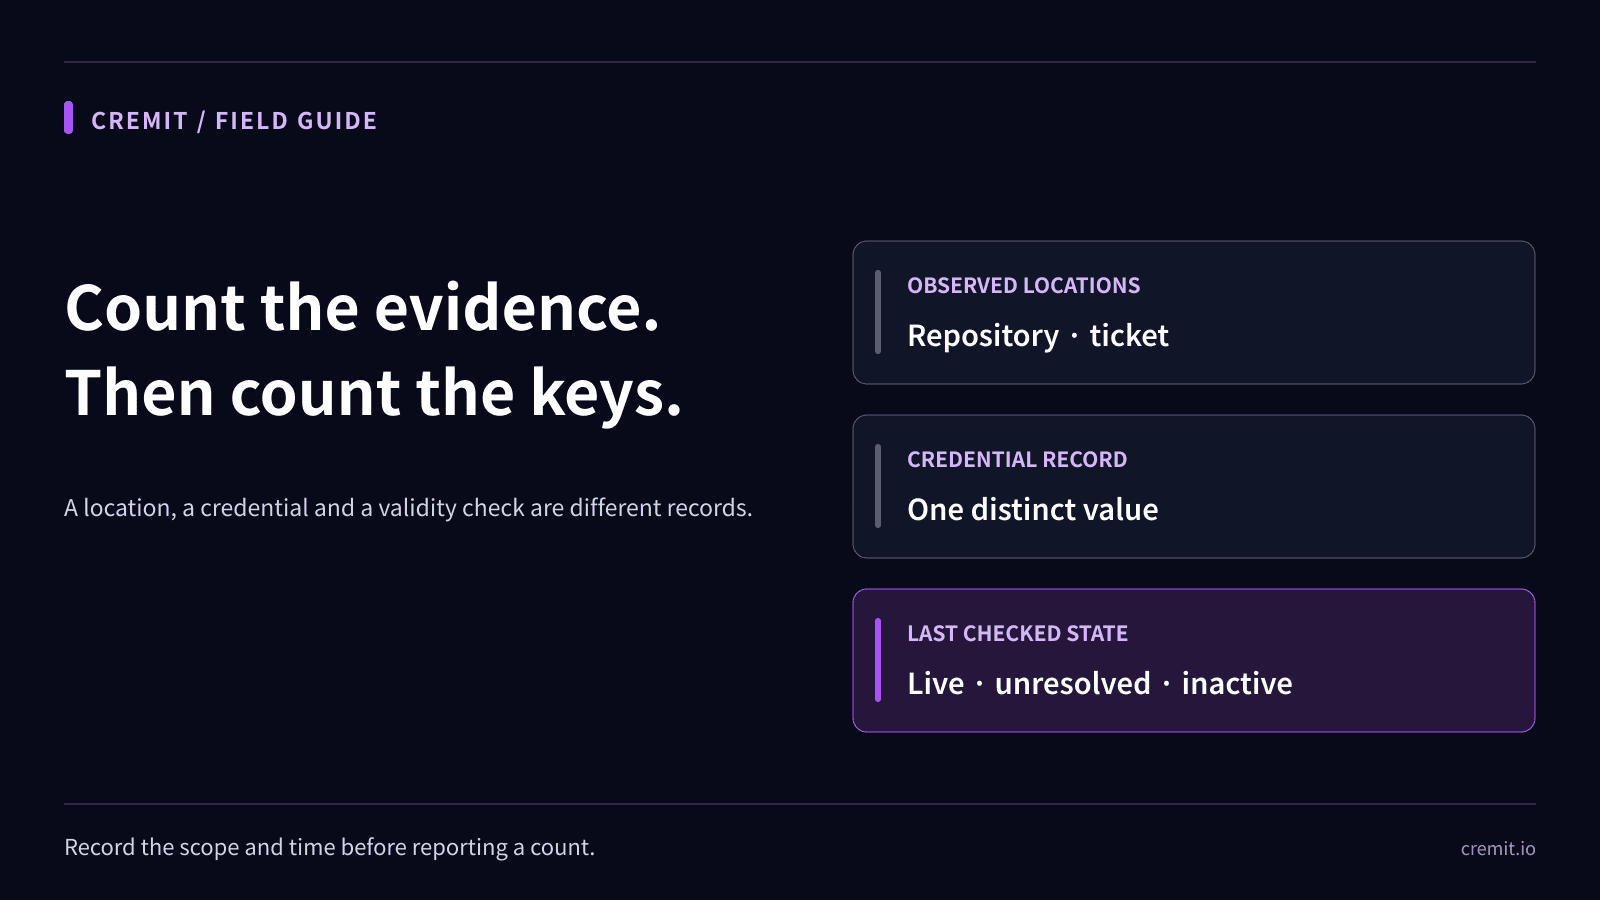
Count observed locations, distinct credential records and verification states separately. Define scope and check time before reporting exposure.

Ben Kim
Ben Kim
From exposed credentials to Cremit Platform: the workflow we support
Jul 28, 2026

From exposed credentials to Cremit Platform: the workflow we support

How Cremit Platform finds exposed credentials, verifies supported types, and routes findings to an owner, with clear limits.

Ben Kim
Ben Kim
AI agent credentials: trace the tool, issuer and responder
Jul 19, 2026

AI agent credentials: trace the tool, issuer and responder

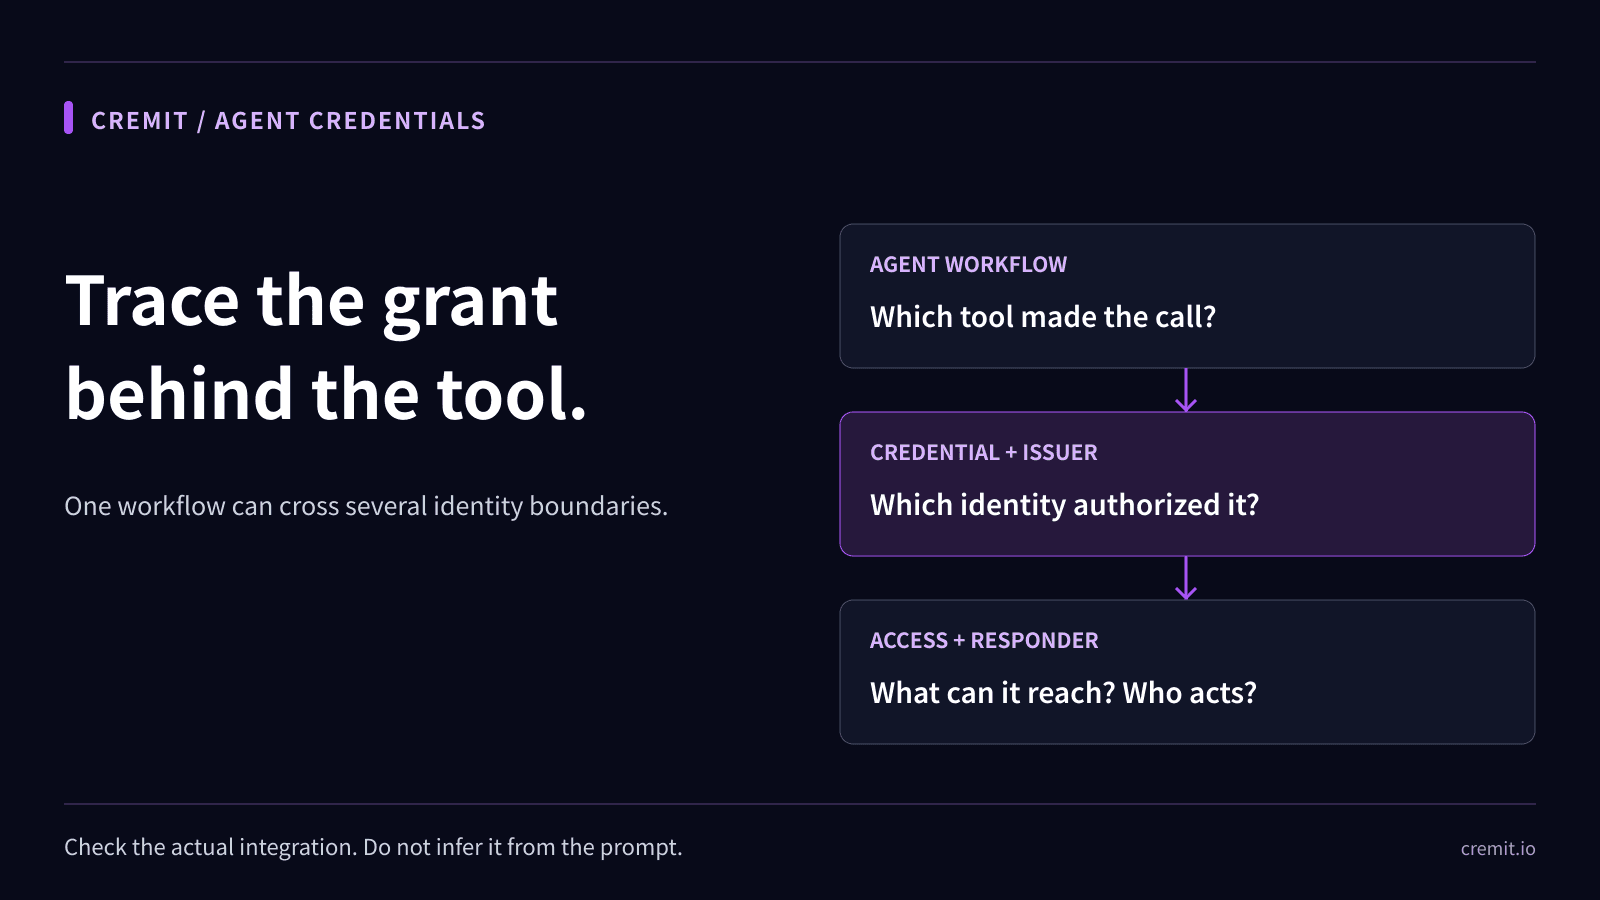
An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.

Ben Kim
Ben Kim
The machine access behind an exposed API key
Jul 15, 2026

The machine access behind an exposed API key

An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.

Ben Kim
Ben Kim
Your Slack Webhook Is Write-Only, Until an AI Agent Reads the Channel
Jun 13, 2026

Your Slack Webhook Is Write-Only, Until an AI Agent Reads the Channel

A leaked Slack incoming webhook is usually triaged as low severity: write-only, one channel, no data access. The moment an AI agent reads that channel and can act with tools, that write-only primitive becomes an indirect prompt injection path into the agent's privileges. Here is the full kill chain, the exact preconditions, and how to defend it.

Ben Kim
Ben Kim
AntV npm compromise: what the package evidence shows
May 19, 2026

AntV npm compromise: what the package evidence shows

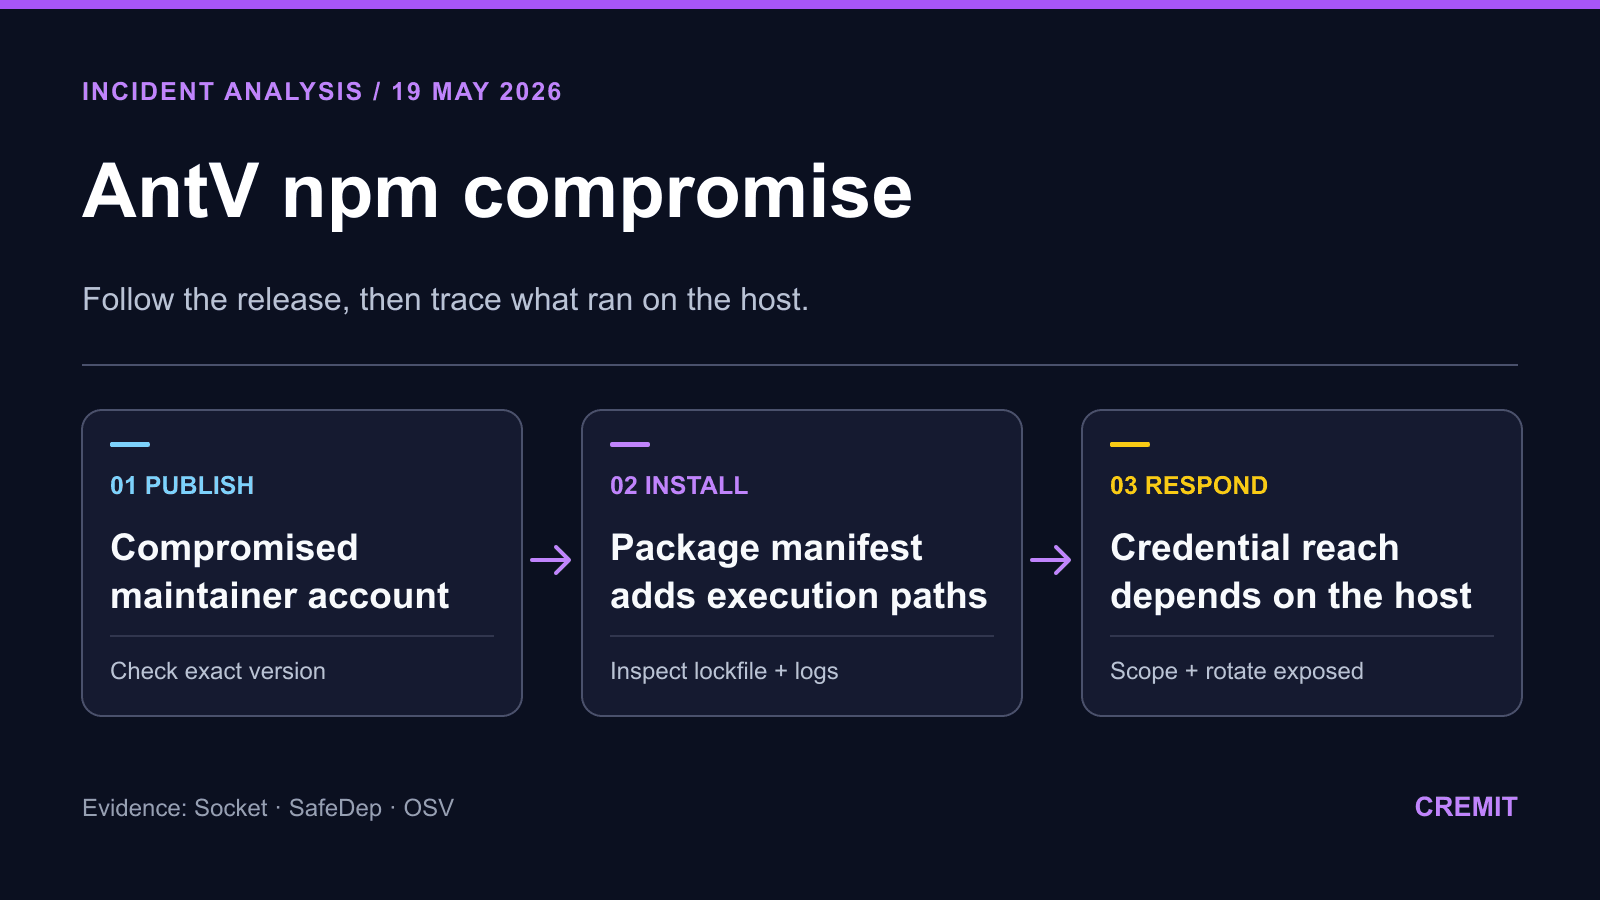
Socket and SafeDep documented hundreds of malicious AntV-related npm releases. Compare exact versions, understand the two execution paths, and scope credentials exposed on affected hosts.

Ben Kim
Ben Kim
Eight credential exposure patterns and how to respond
Apr 30, 2026

Eight credential exposure patterns and how to respond

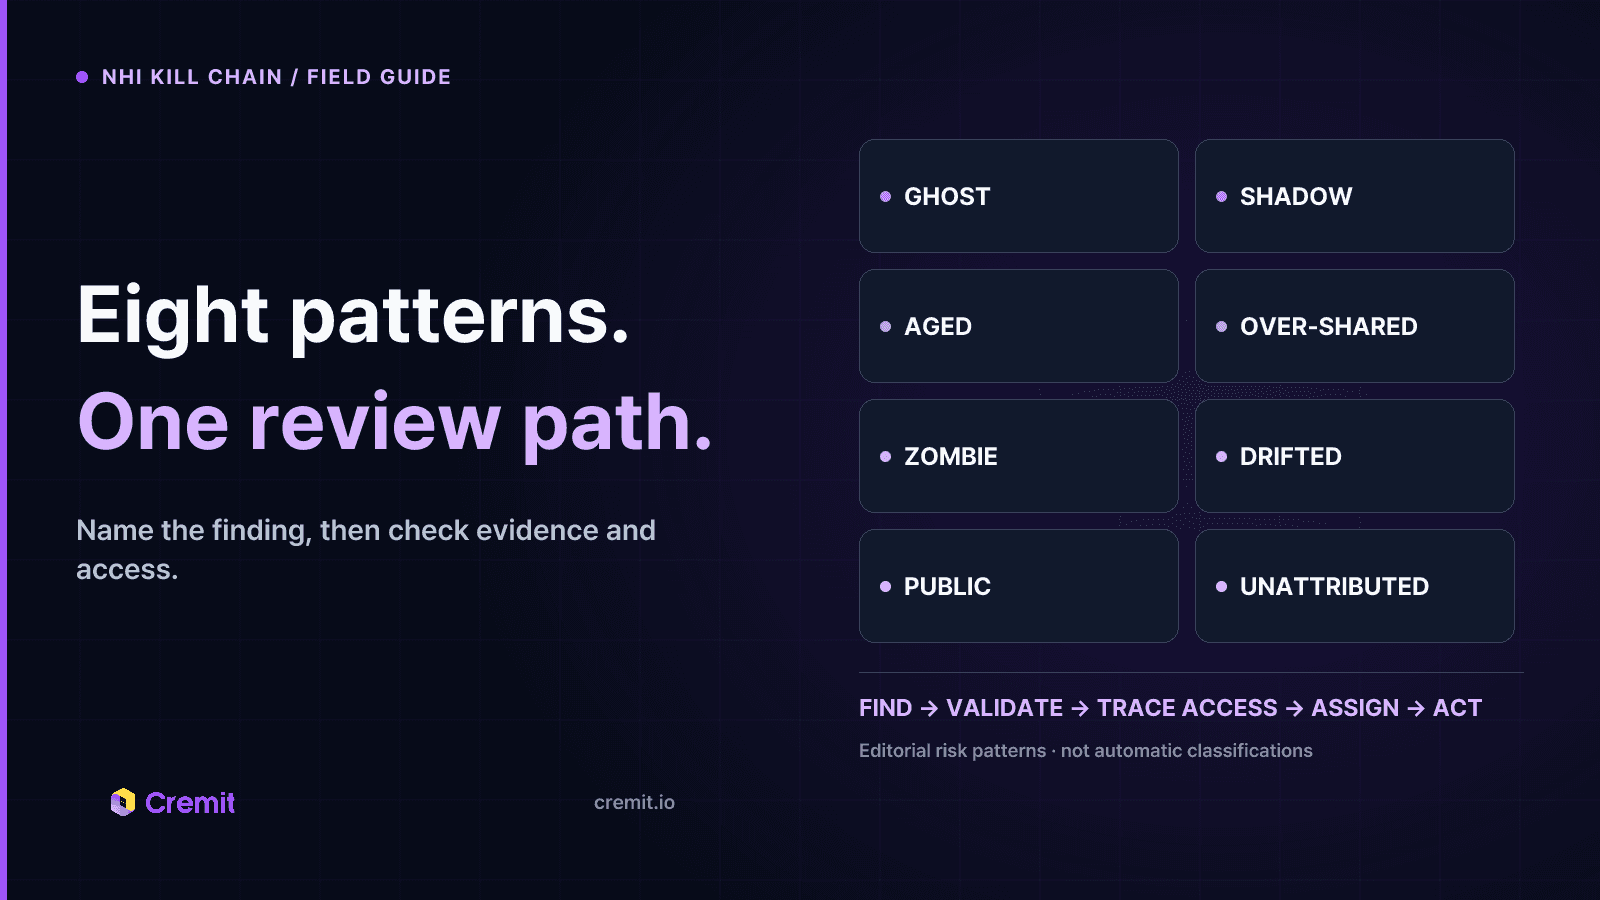
A practical summary of eight NHI credential exposure patterns, the evidence to check, and what Cremit Platform can help investigate.

Ben Kim
Ben Kim
Bitwarden CLI npm compromise: affected systems and response
Apr 25, 2026

Bitwarden CLI npm compromise: affected systems and response

A malicious CLI package was available on npm for 93 minutes on April 22, 2026. Check who installed it, what researchers found, and Bitwarden’s response steps.

Ben Kim
Ben Kim
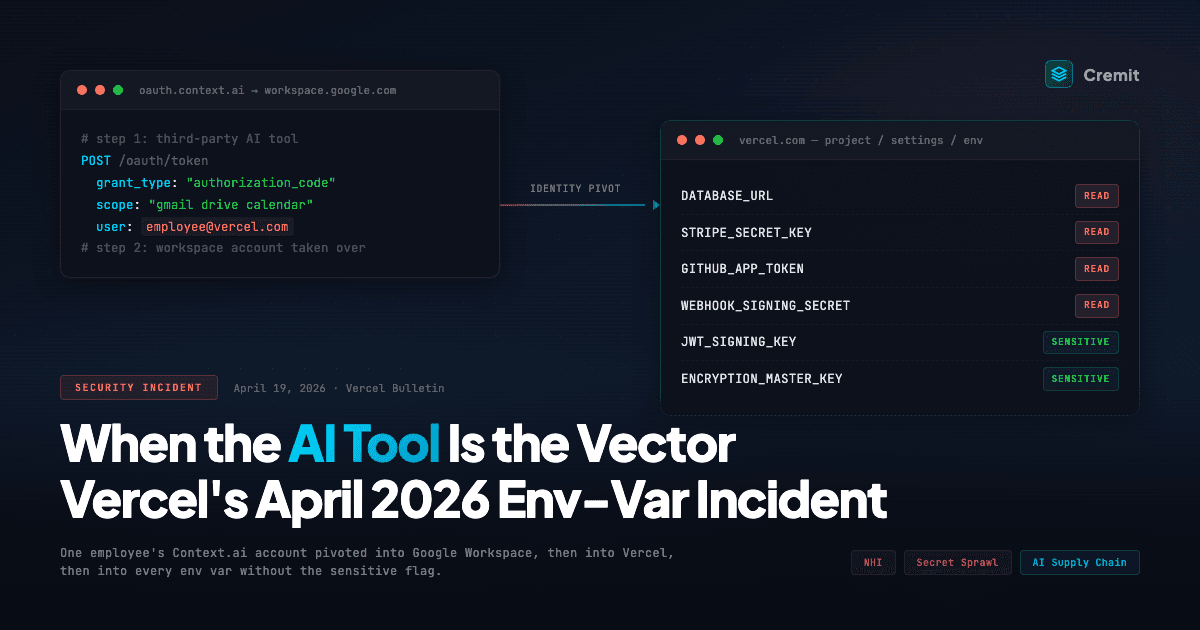
Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why
Apr 20, 2026

Vercel's April 2026 Incident Is a Textbook NHI Problem: What to Rotate and Why

Vercel confirmed an unauthorized-access incident on April 19, 2026 that started in a third-party AI tool, pivoted through Google Workspace, and reached environment variables in a subset of customer projects. The exposure surface is every env var that was not marked sensitive. Here is what is confirmed, what is noise, and what to rotate first.

Ben Kim
Ben Kim
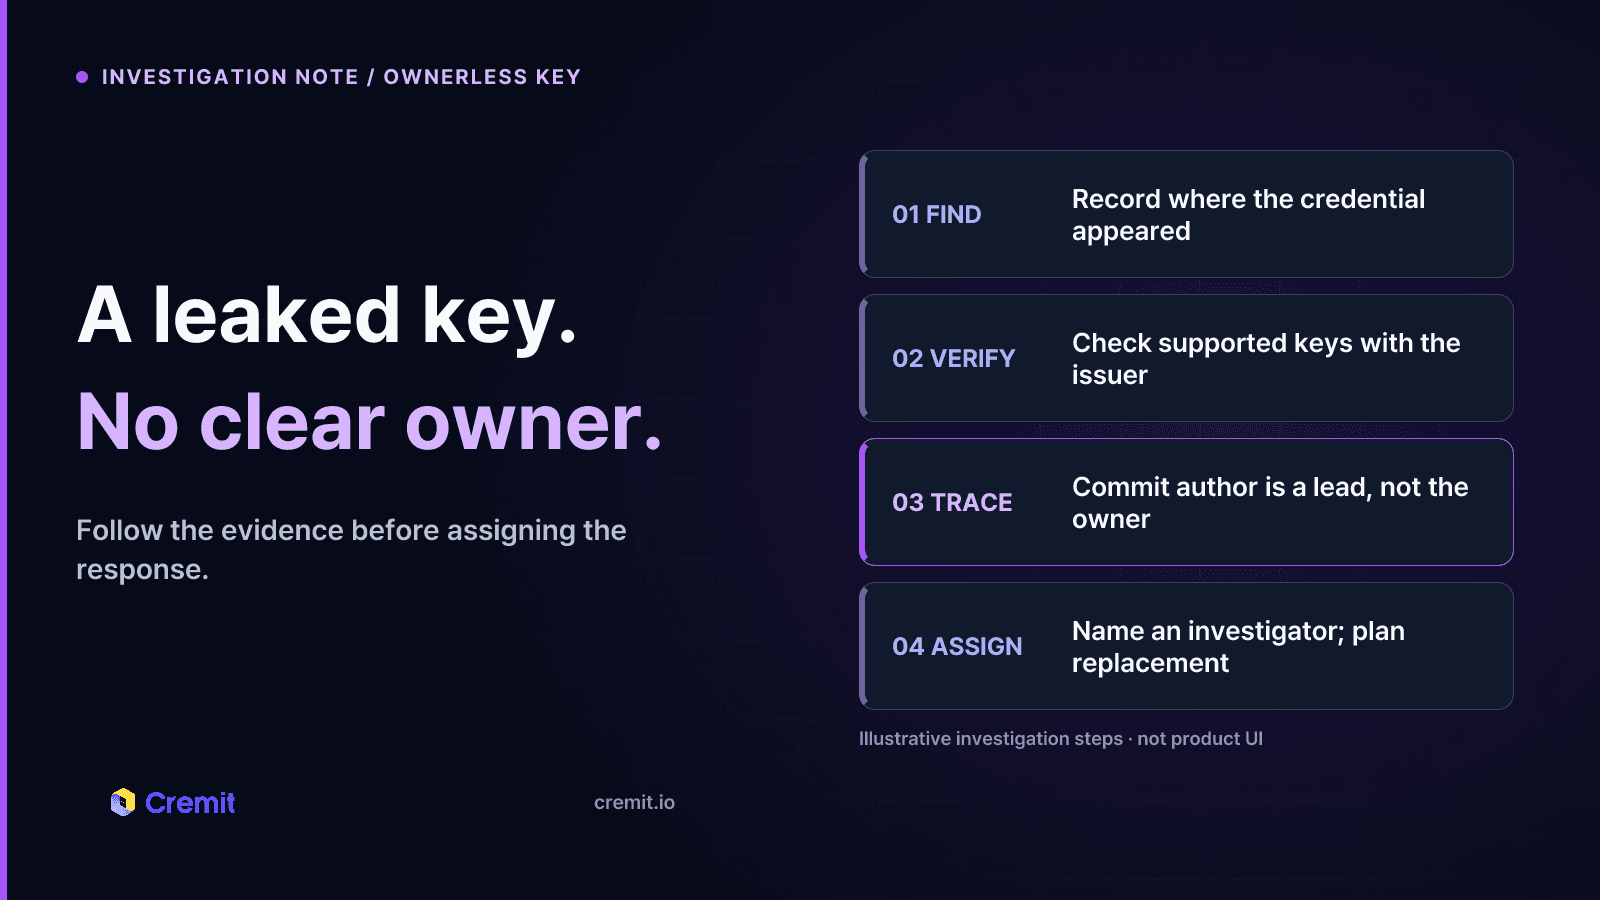
When an exposed credential has no clear owner
Apr 20, 2026

When an exposed credential has no clear owner

How to verify, investigate, assign, and replace an exposed credential when the service owner is unclear.

Ben Kim
Ben Kim
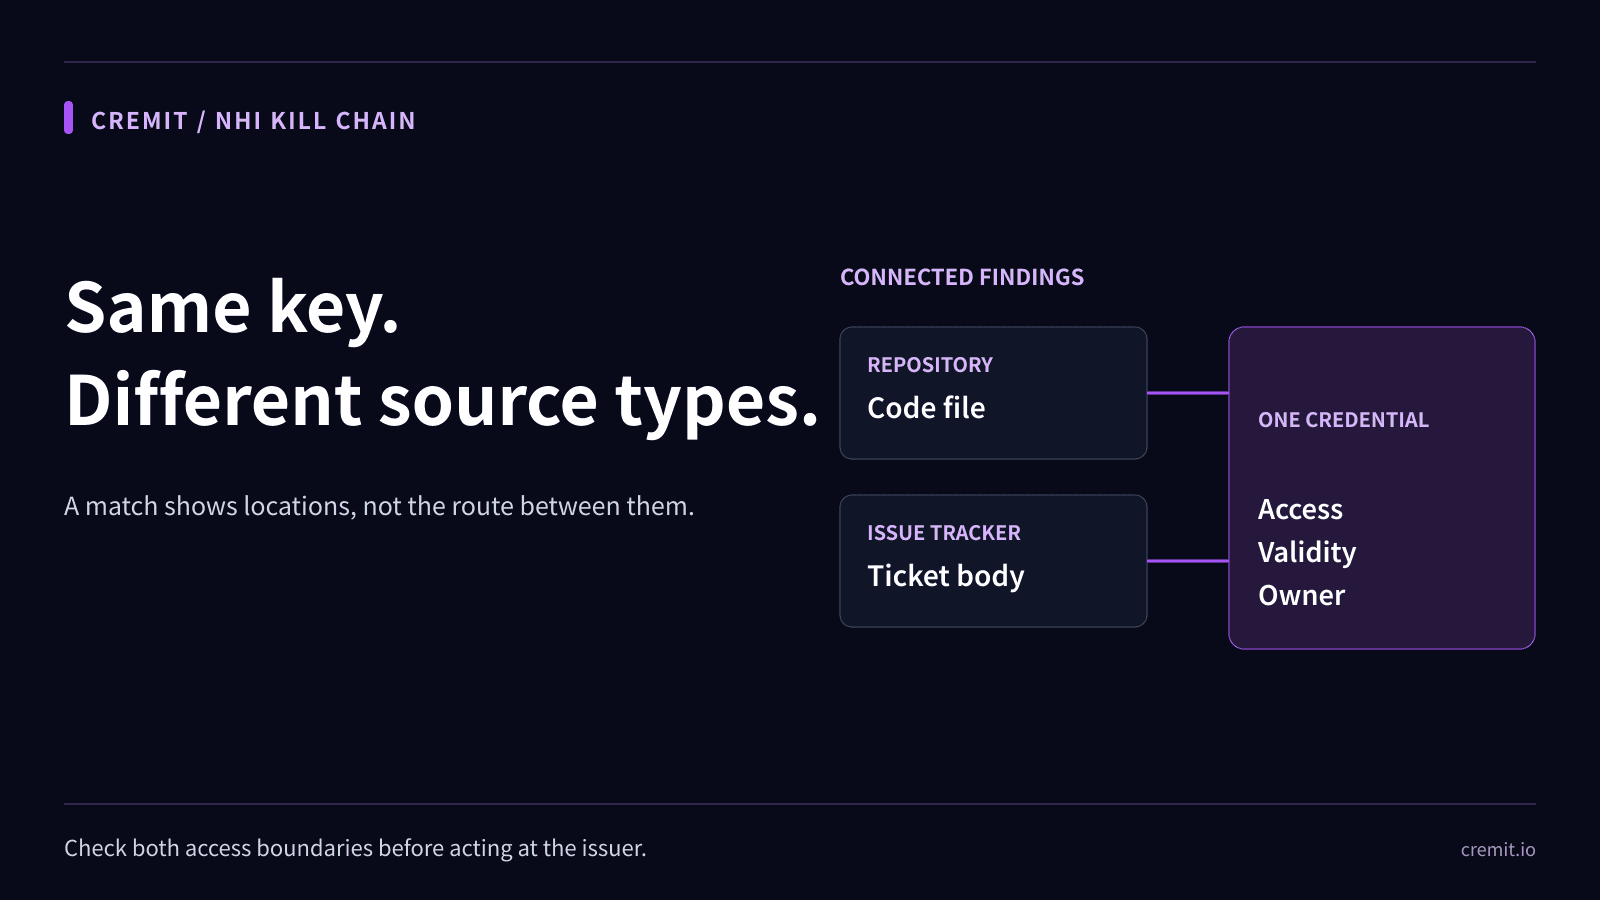
Same key in a repository and ticket: investigating cross-platform findings
Apr 17, 2026

Same key in a repository and ticket: investigating cross-platform findings

Two source types show two observed locations, not how a credential moved. Check access, issuer status, owner, and actual consumers.

Ben Kim
Ben Kim
The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure
Apr 15, 2026

The "Out of Scope" Loophole: Why Bug Bounties Look Away From Credential Exposure

An organization's core credentials sat in public repositories for years. The security industry's answer: "Out of scope."

Ben Kim
Ben Kim
Deleted file, active credential: investigating a Zombie Key
Apr 14, 2026

Deleted file, active credential: investigating a Zombie Key

Source removal does not revoke a credential. Check the issuer, Git history, current owner, and last verification before closing the finding.

Ben Kim
Ben Kim
One API key in three repositories: investigating shared credentials
Apr 11, 2026

One API key in three repositories: investigating shared credentials

Three observed locations are not a complete dependency map. Check key type, issuer status, permissions, and actual consumers before replacement.

Ben Kim
Ben Kim
Long-exposed credentials: what a 90-day source record tells you
Apr 10, 2026

Long-exposed credentials: what a 90-day source record tells you

An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.

Ben Kim
Ben Kim
API keys in incident chats and tickets: what to investigate
Apr 5, 2026

API keys in incident chats and tickets: what to investigate

A credential outside a repository needs a source-access review, issuer check, owner, and verified response. A finding alone does not prove misuse.

Ben Kim
Ben Kim
Orphaned API keys after offboarding: what the evidence shows
Apr 2, 2026

Orphaned API keys after offboarding: what the evidence shows

An active key linked to an inactive author is a lead. Check the directory, source, issuer, and current service owner before deciding what happened.

Ben Kim
Ben Kim
When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack
Mar 25, 2026

When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.

Ben Kim
Ben Kim
Public API key in a repository: what to check first
Mar 17, 2026

Public API key in a repository: what to check first

A public commit proves exposure, not misuse. Check validity, permissions, issuer logs, and dependent workloads before closing the incident.

Ben Kim
Ben Kim
Clinejection: prompt injection and the unauthorized Cline CLI release
Mar 7, 2026

Clinejection: prompt injection and the unauthorized Cline CLI release

Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.

Ben Kim
Ben Kim
Bybit Hack: What the Safe Wallet Investigation Found
Jan 25, 2026

Bybit Hack: What the Safe Wallet Investigation Found

The February 2025 theft involved a compromised Safe developer and a manipulated transaction interface. Here is what investigators confirmed and what remains unknown.

Ben Kim
Ben Kim
2025 DBIR: what credential abuse and third-party breaches mean for teams
May 29, 2025

2025 DBIR: what credential abuse and third-party breaches mean for teams

A sourced reading of the 2025 Verizon DBIR, with practical steps for credential inventory, leak prevention, and response.

Ben Kim
Ben Kim
OWASP NHI5: How to Review Excess Machine Permissions
Apr 25, 2025

OWASP NHI5: How to Review Excess Machine Permissions

Compare workload needs, issuer grants, effective access, and observed use before reducing an NHI’s permissions.

Ben Kim
Ben Kim
A rotation record is not a map of leaked credentials
Apr 23, 2025

A rotation record is not a map of leaked credentials

Lifecycle records show intended access. Secret findings show copies in scanned sources. Compare both before deciding who should replace a key.

Ben Kim
Ben Kim
OWASP NHI4:2025 — how to review insecure authentication
Apr 22, 2025

OWASP NHI4:2025 — how to review insecure authentication

Insecure authentication is more than a leaked key. Review OAuth flows, static credentials, token scope, and the rollout path for safer workload access.

Ben Kim
Ben Kim
MCP and A2A security: trace the credentials between agents and tools
Apr 16, 2025

MCP and A2A security: trace the credentials between agents and tools

MCP connects agents to tools; A2A connects agents to each other. Map authentication, token scope, and exposed credentials at every hop.

Ben Kim
Ben Kim
Human vs. non-human identity: what changes in access review?
Apr 1, 2025

Human vs. non-human identity: what changes in access review?

A person and a workload can both have privileged access. Compare the principal, credential, owner and offboarding record you need to review each one.

Ben Kim
Ben Kim
Wake-Up Call: tj-actions/changed-files Compromised NHIs
Mar 25, 2025

Wake-Up Call: tj-actions/changed-files Compromised NHIs

A GitHub Action used by more than 23,000 repositories was altered and its version tags retagged, leaking CI/CD secrets into build logs. The incident read as an NHI failure.

Ben Kim
Ben Kim
How to find hidden credentials in code and shared tools
Mar 18, 2025

How to find hidden credentials in code and shared tools

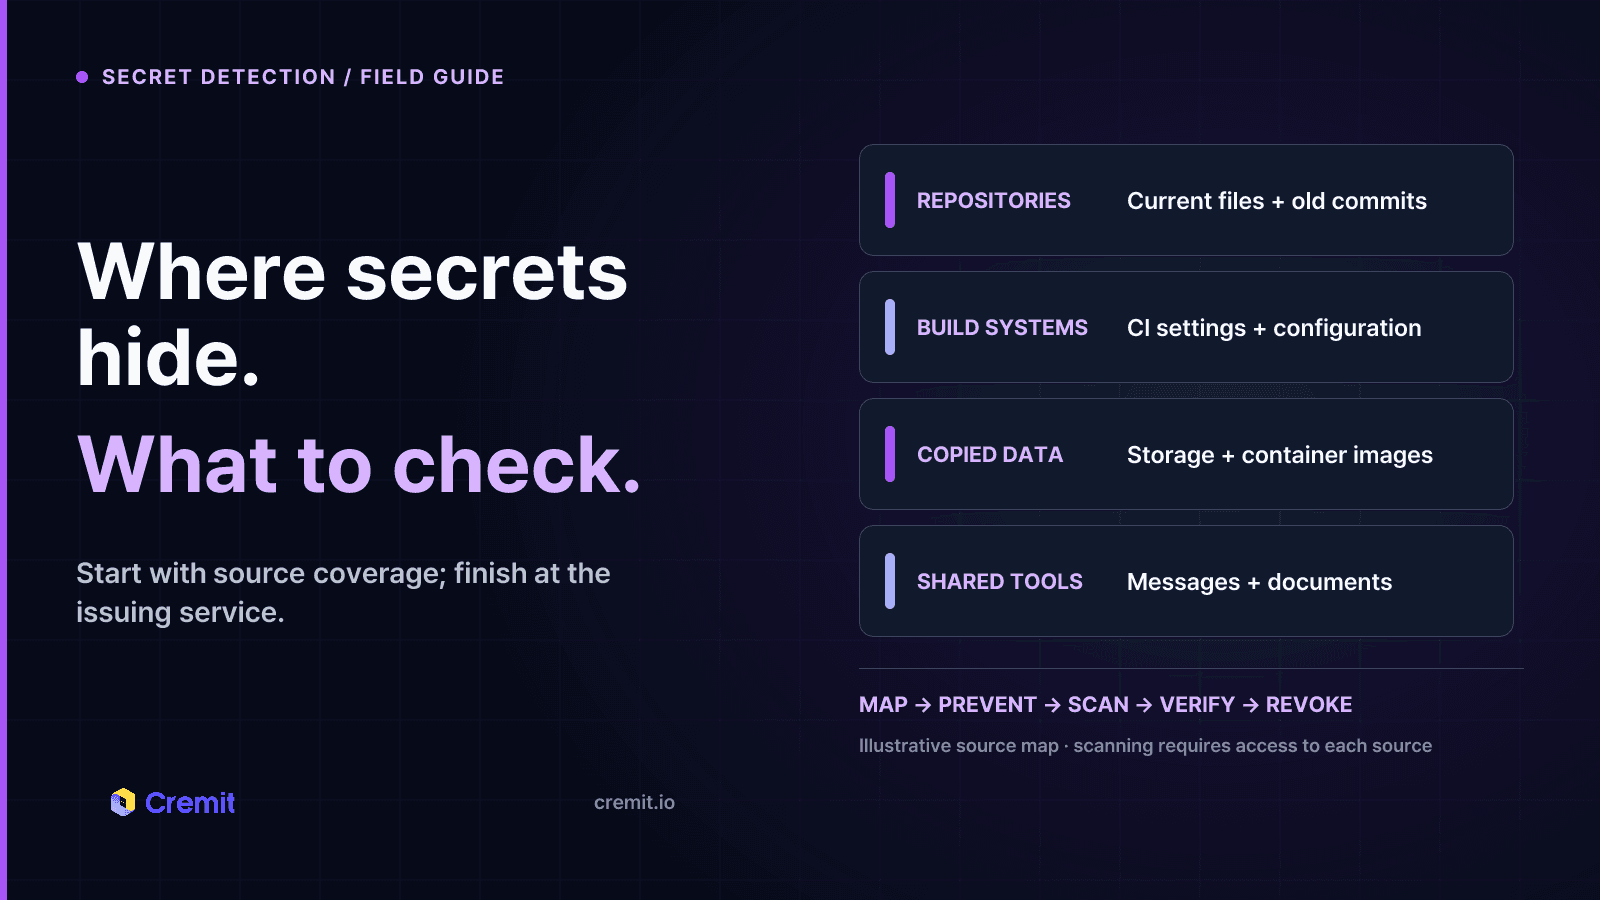
A practical workflow for preventing, finding, verifying, and replacing exposed credentials across code and shared tools.

Ben Kim
Ben Kim
OWASP NHI1: Offboard machine access without breaking a service
Mar 3, 2025

OWASP NHI1: Offboard machine access without breaking a service

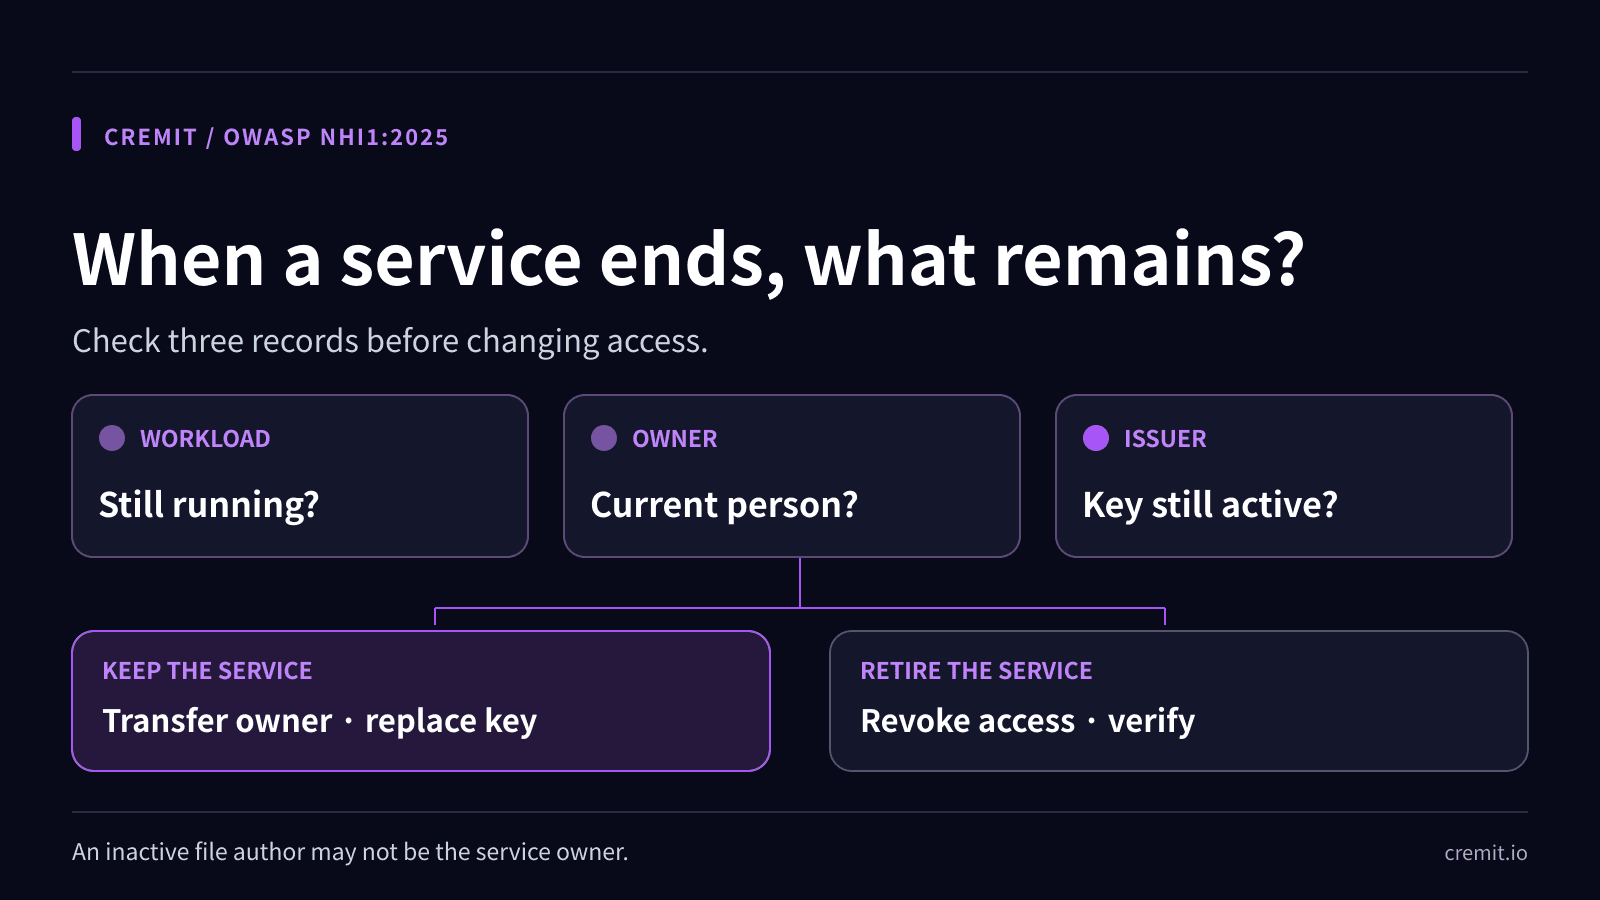
When a service ends or its owner leaves, decide what still runs, transfer responsibility or revoke access, and verify the old key no longer works.

Ben Kim
Ben Kim
AWS S3 secret scanning: what a connected bucket shows
Feb 25, 2025

AWS S3 secret scanning: what a connected bucket shows

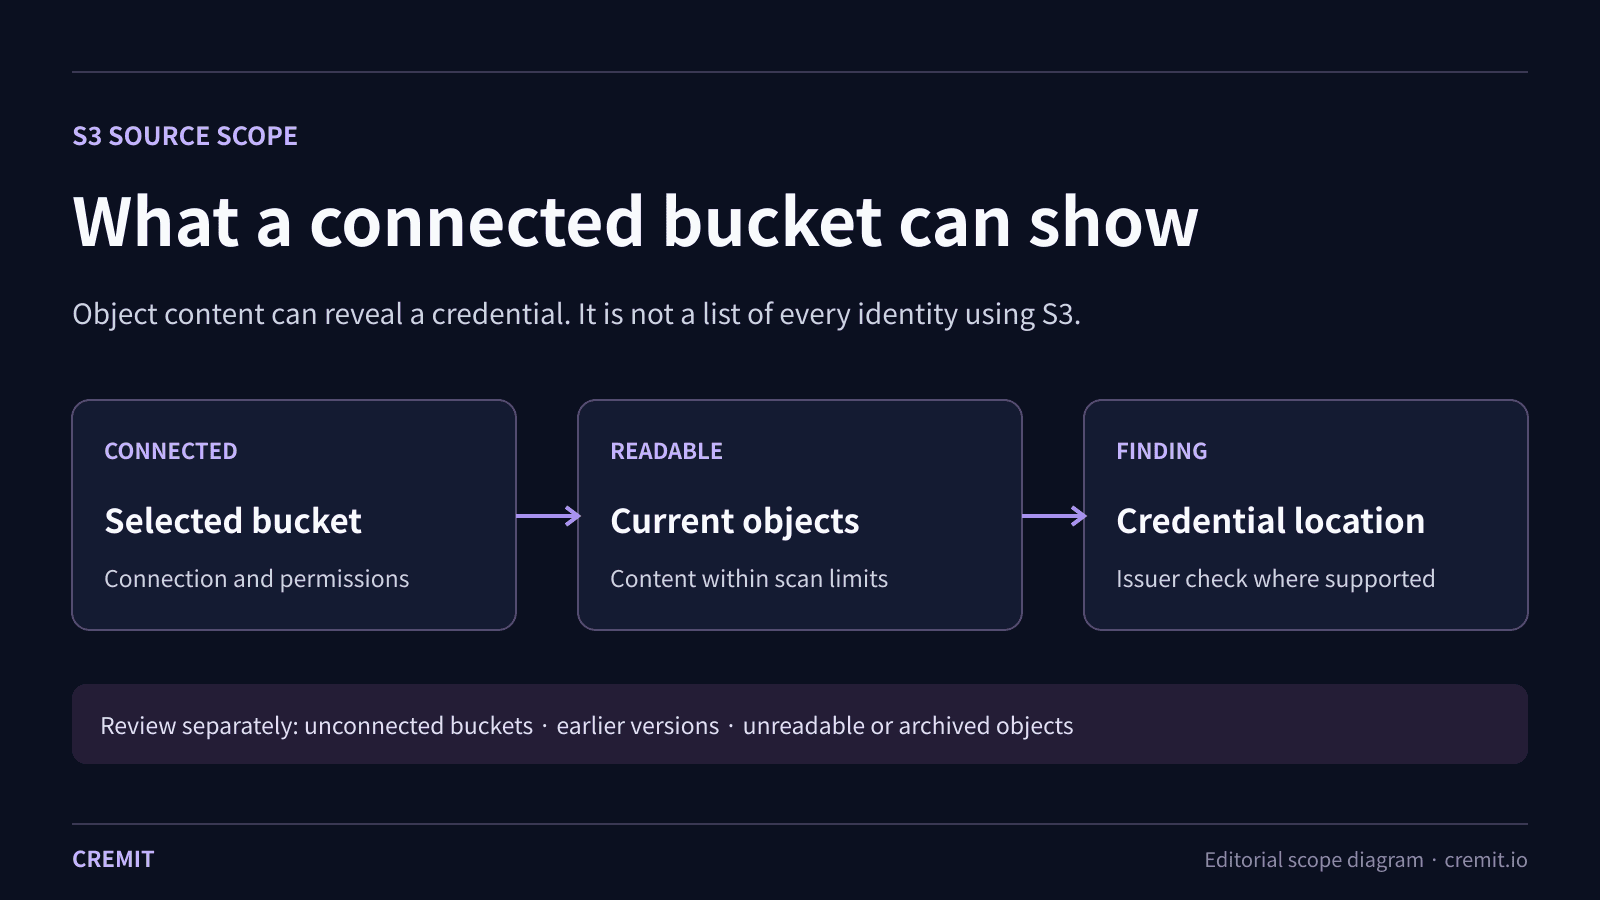
Cremit reads supported current objects in connected S3 buckets to locate credentials. Check access, skipped objects, earlier versions and the issuer separately.

Ben Kim
Ben Kim
Secret scanning: when to use built-in, open-source or connected-source checks
Feb 25, 2025

Secret scanning: when to use built-in, open-source or connected-source checks

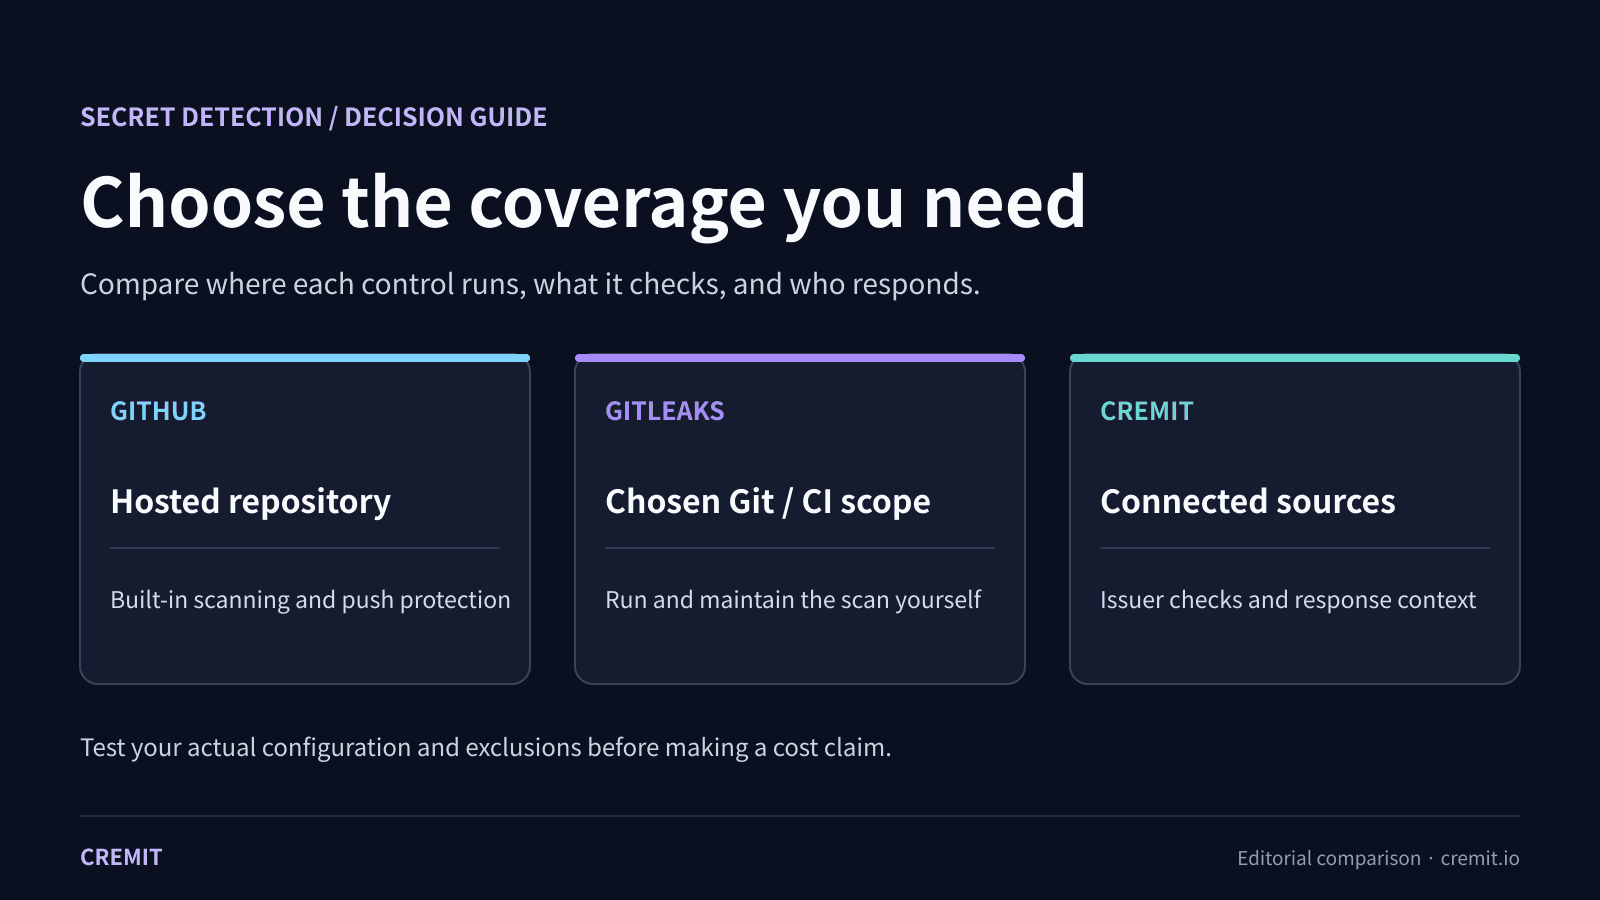
Start with the sources you need to inspect, the evidence each check returns, and who will revoke a live key. Compare GitHub, Gitleaks and Cremit by the work each covers.

Ben Kim
Ben Kim
OWASP NHI2: Secret leakage and the four checks after discovery
Feb 18, 2025

OWASP NHI2: Secret leakage and the four checks after discovery

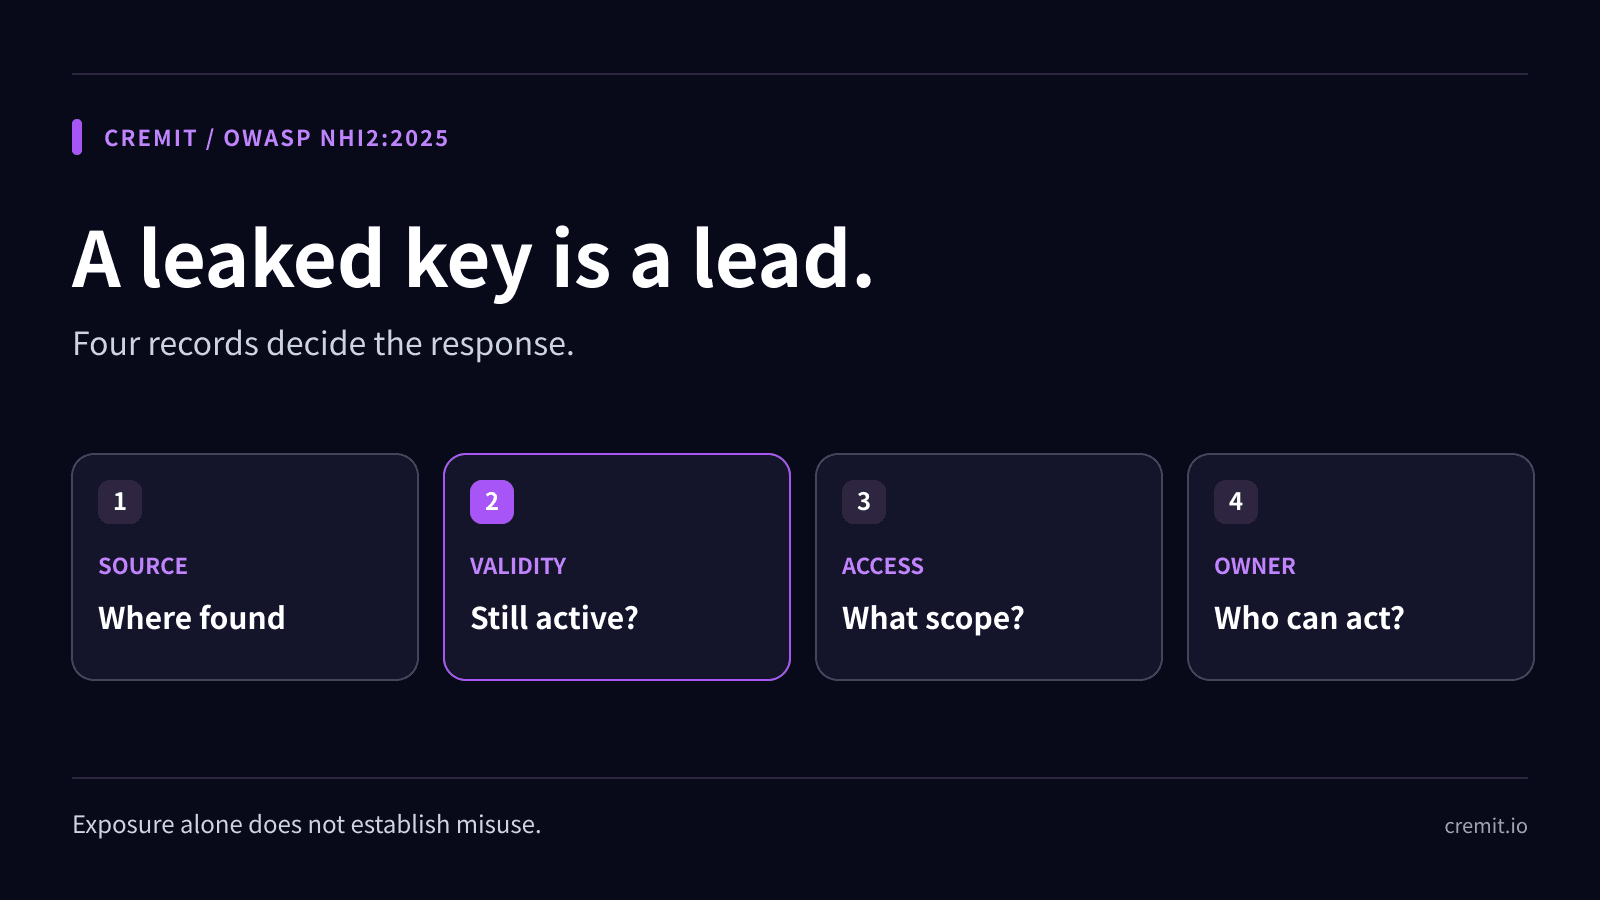
A leaked secret is a lead, not proof of misuse. Check its location, validity, access, and response owner before closing the exposure.

Ben Kim
Ben Kim
OWASP NHI3: reviewing access held by a third-party integration
Feb 4, 2025

OWASP NHI3: reviewing access held by a third-party integration

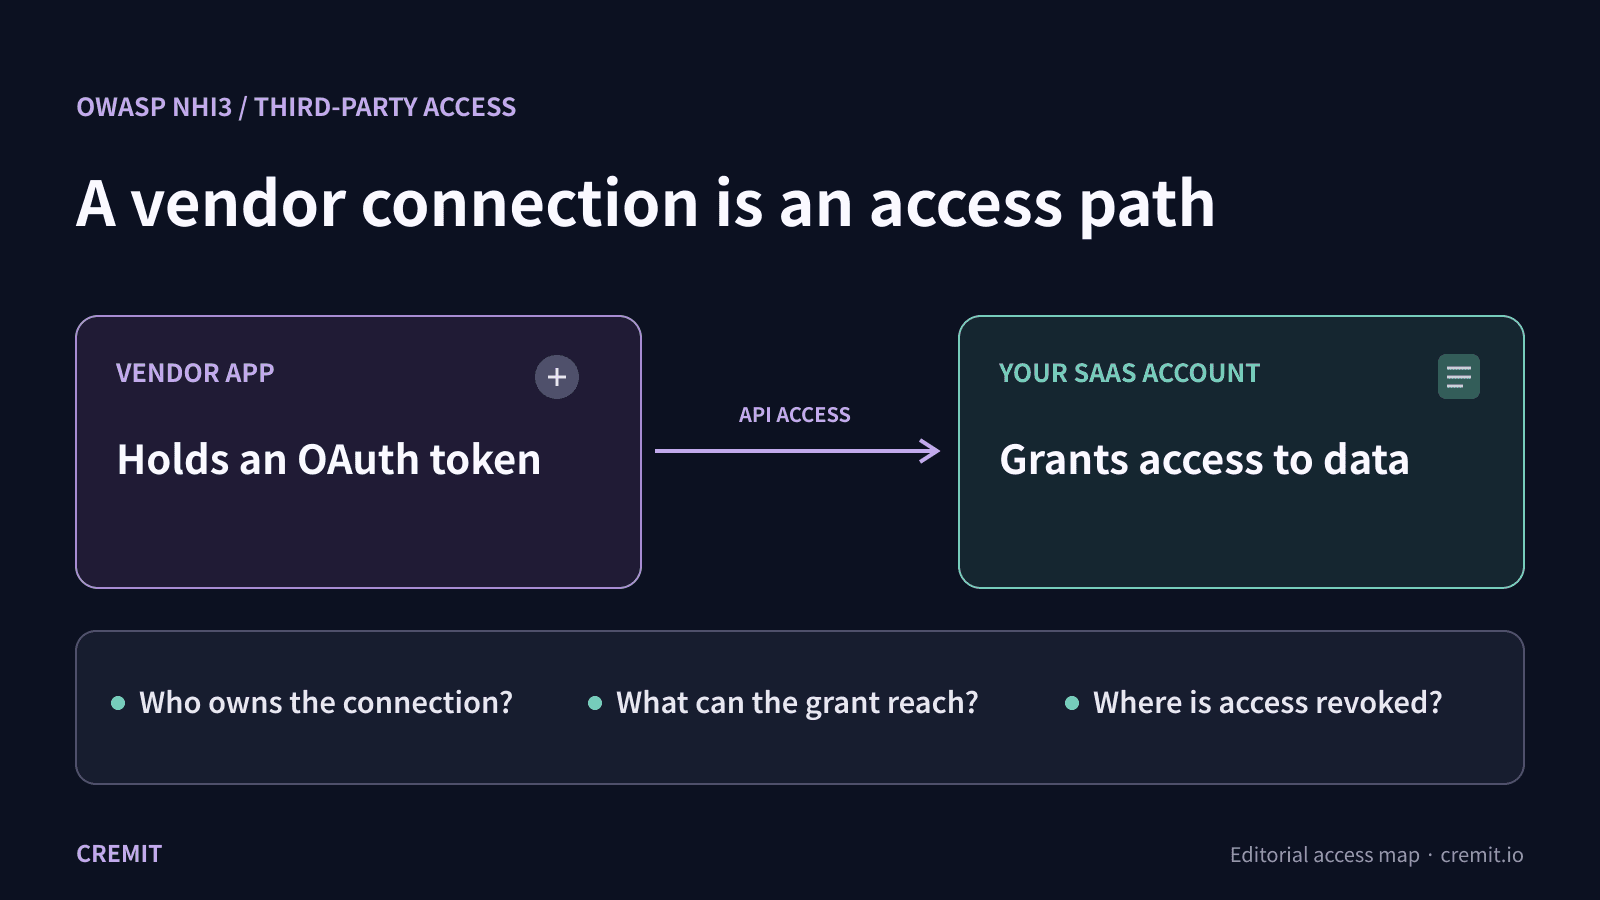
A vendor can hold a token that reaches your SaaS data. Use the Salesloft Drift incident and GitHub App controls to review the grant, owner, activity and revocation path.

Ben Kim
Ben Kim
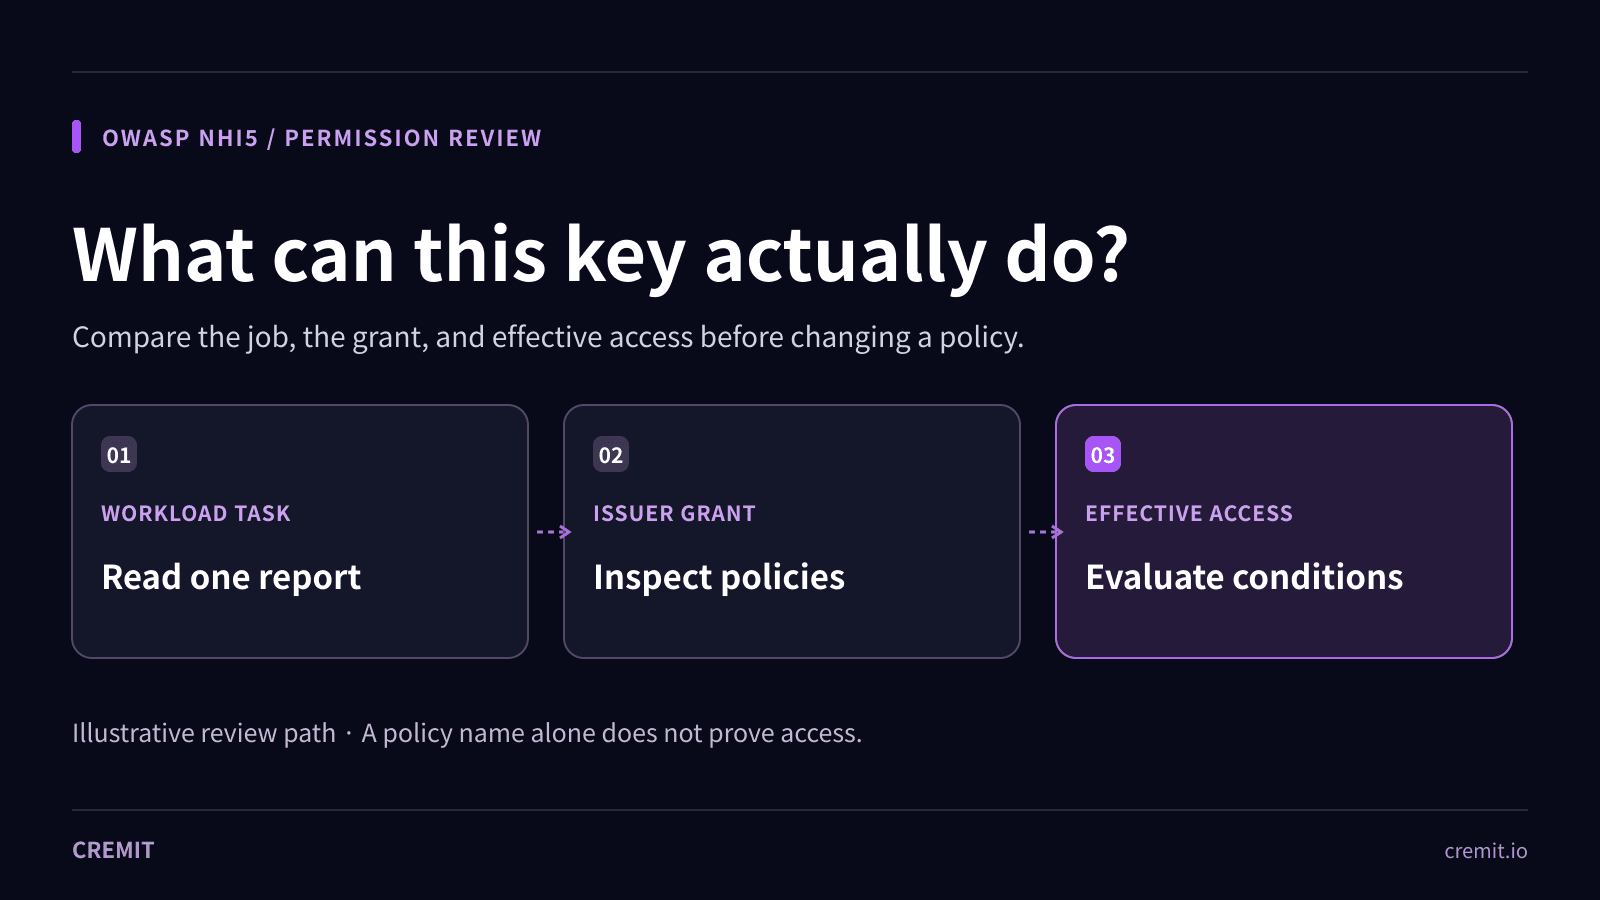
Six checks for securing workload credentials
Dec 5, 2024

Six checks for securing workload credentials

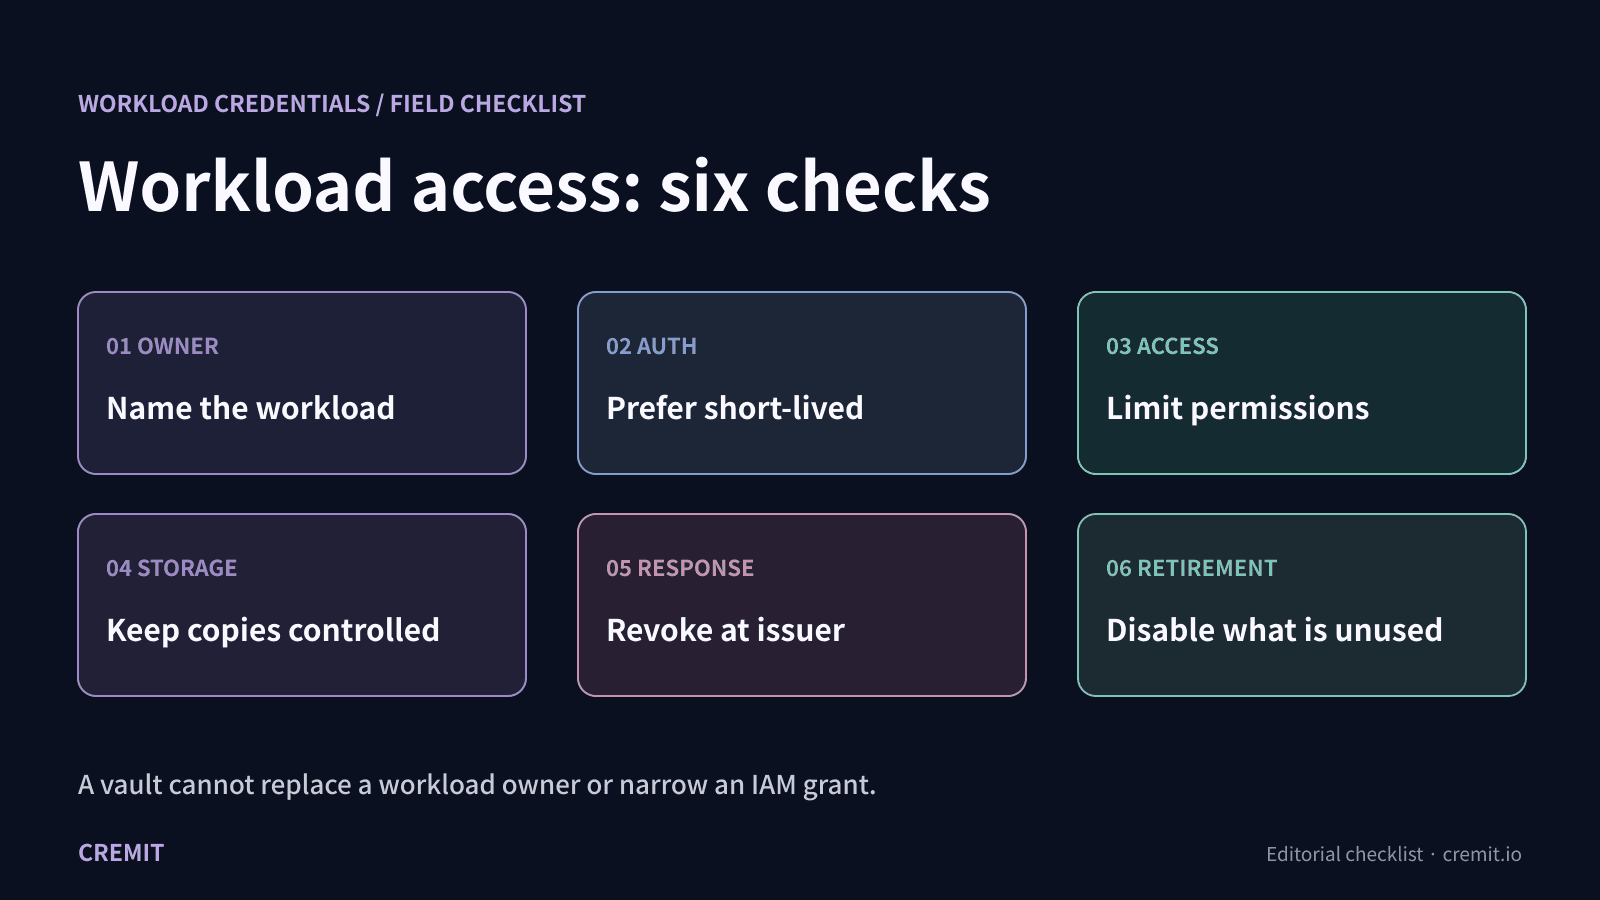
Before adding another key or vault entry, identify the workload, prefer temporary access, bound its permissions, plan exposure response and retire unused identities.

Ben Kim
Ben Kim
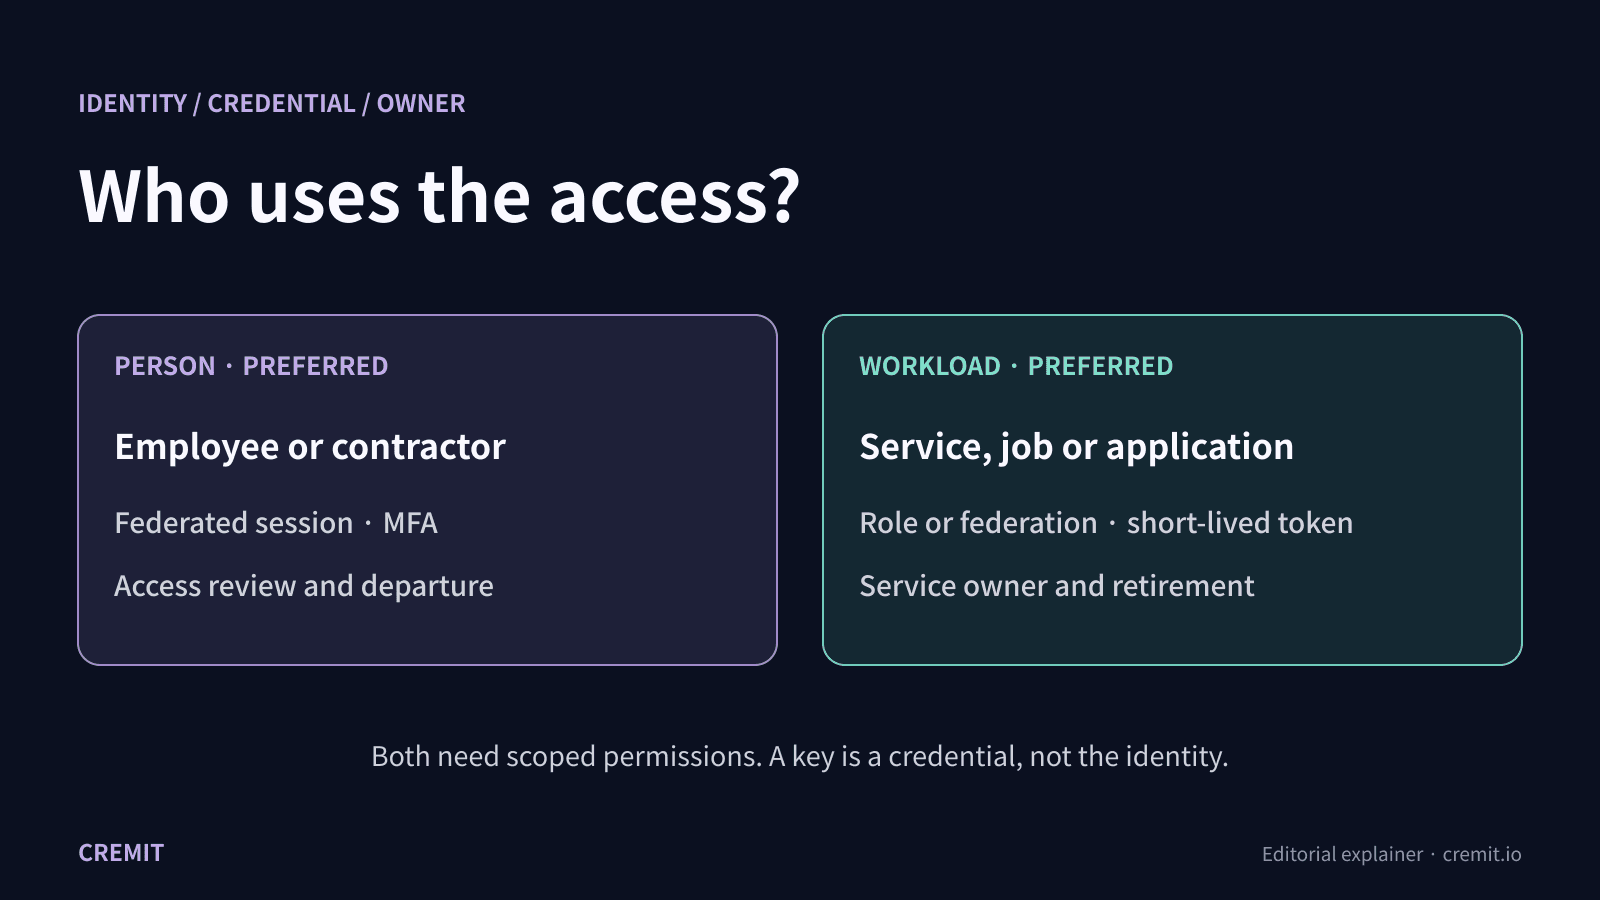
Probe to Cremit Platform: what credential scanning does today
Aug 3, 2024

Probe to Cremit Platform: what credential scanning does today

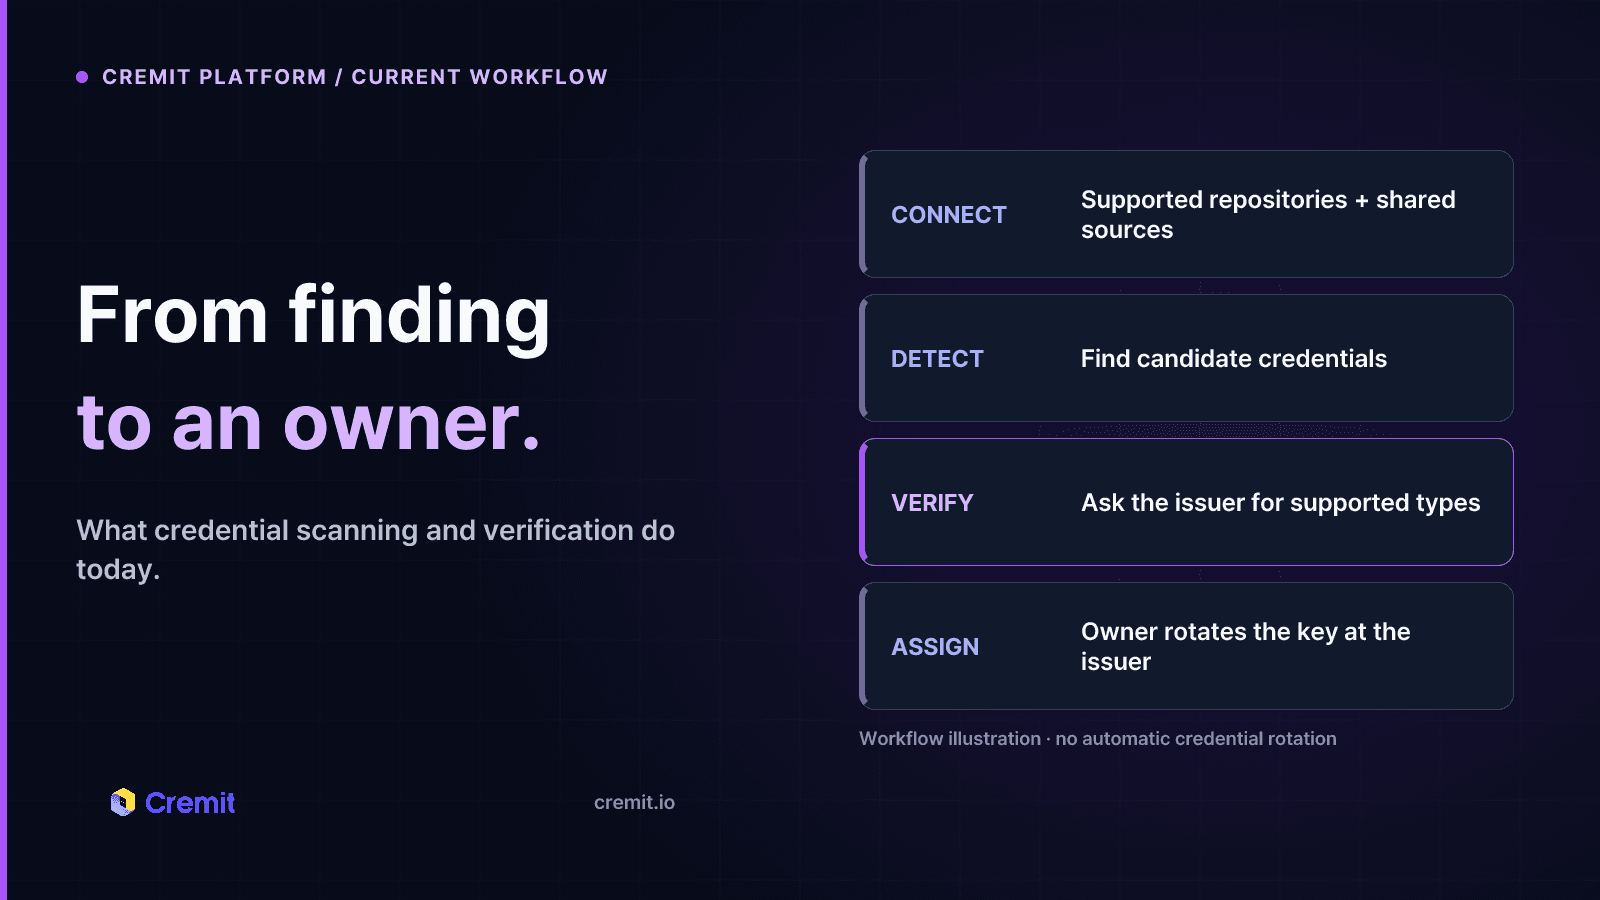
An updated guide to Cremit Platform’s scan sources, live credential checks, and remediation workflow, with current product limits.

Ben Kim
Ben Kim
OWASP NHI Top 10: what to check for each machine identity risk
Apr 9, 2024

OWASP NHI Top 10: what to check for each machine identity risk

The ten OWASP NHI risks explained through specific checks for service accounts, tokens, deployment systems, and owners.

Ben Kim
Ben Kim
Customer Interview: Insights from ENlighten
Mar 4, 2024

Customer Interview: Insights from ENlighten

A conversation with the team at ENlighten, a Korean energy IT platform, about how they manage credentials and secrets and what led them to Cremit.

Ben Kim
Ben Kim
Secret sprawl and workload identity sprawl: two different lists
Oct 22, 2023

Secret sprawl and workload identity sprawl: two different lists

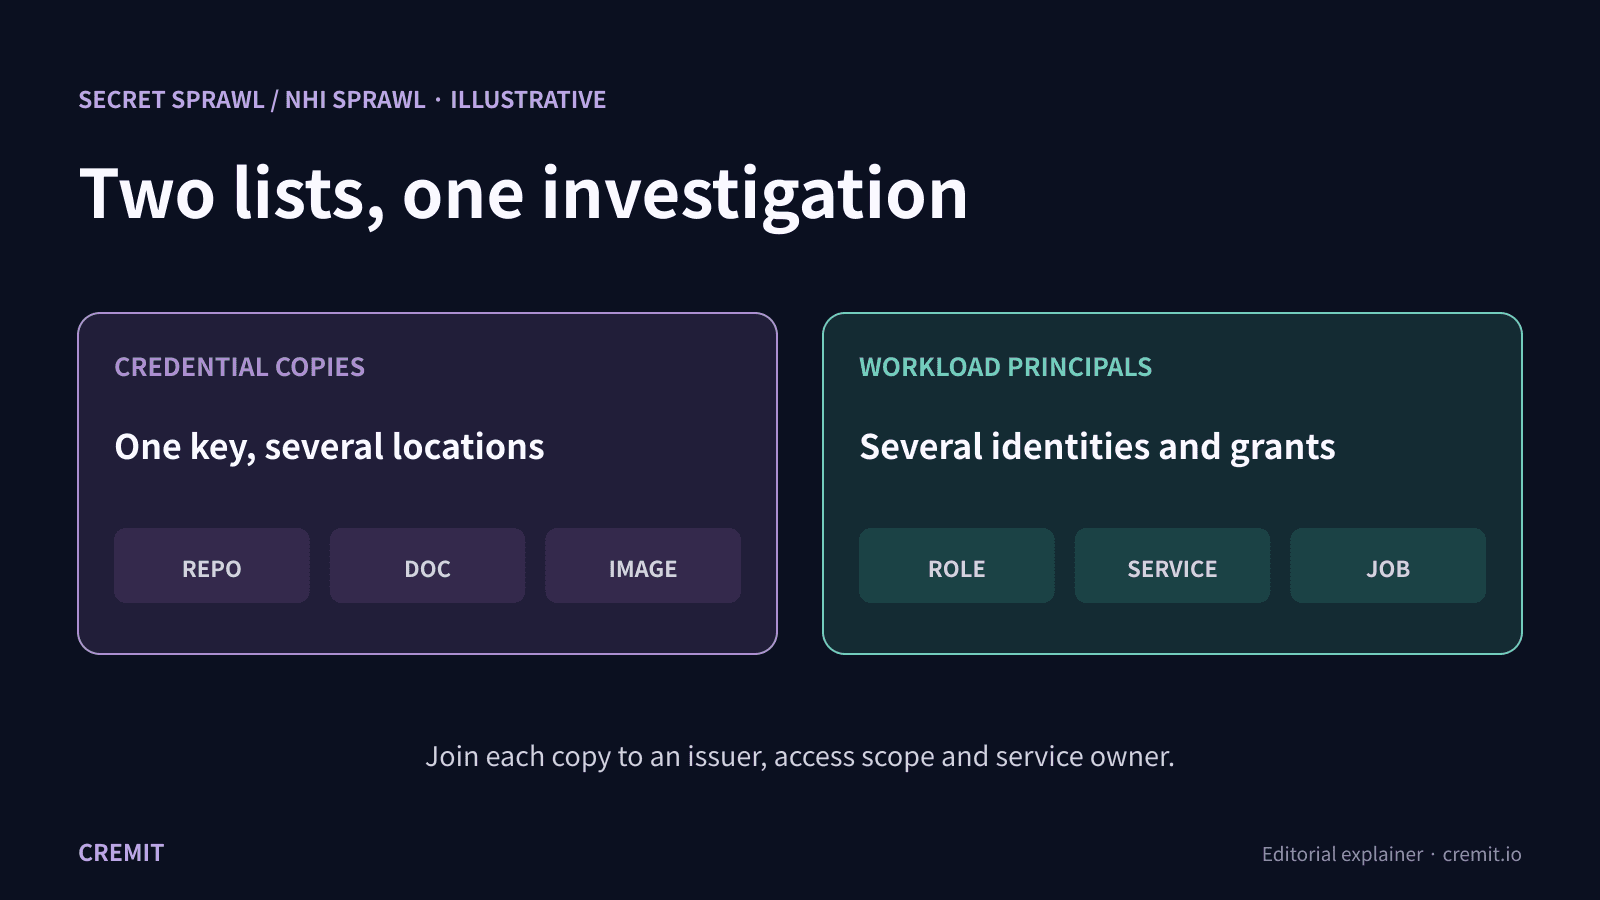
One credential can be copied to many places; many workload principals can accumulate grants. Keep separate records, then join the evidence for each investigation.

Ben Kim
Ben Kim
NHI Security | Cremit Blog | Cremit