Jul 19, 2026
AI agent credentials: trace the tool, issuer and responder
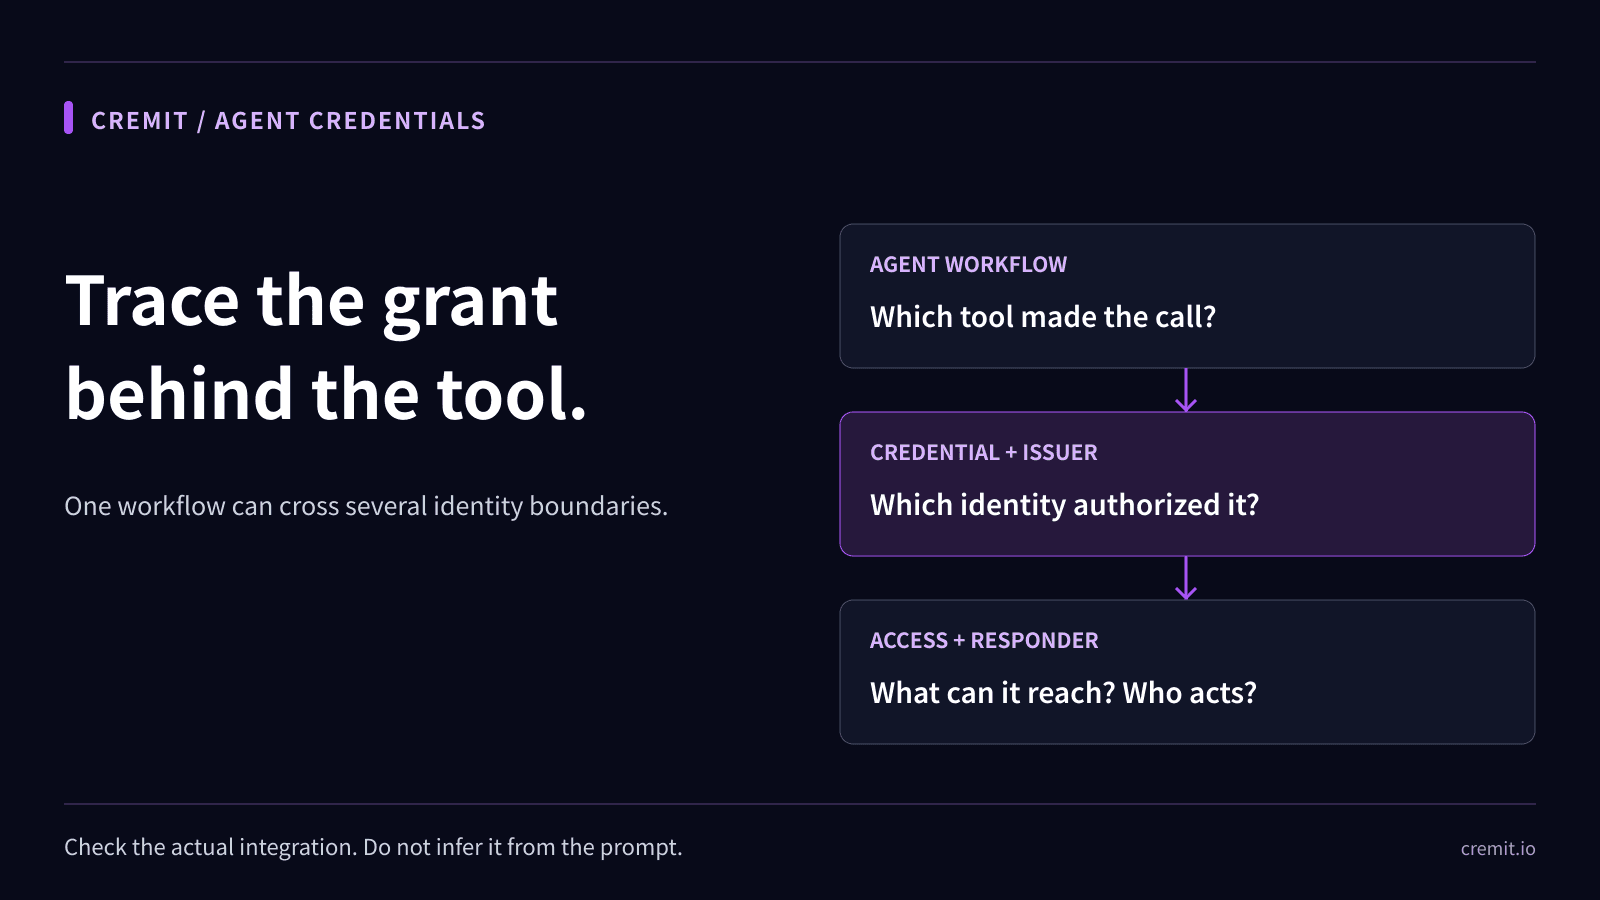
An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.

Ben Kim
An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.
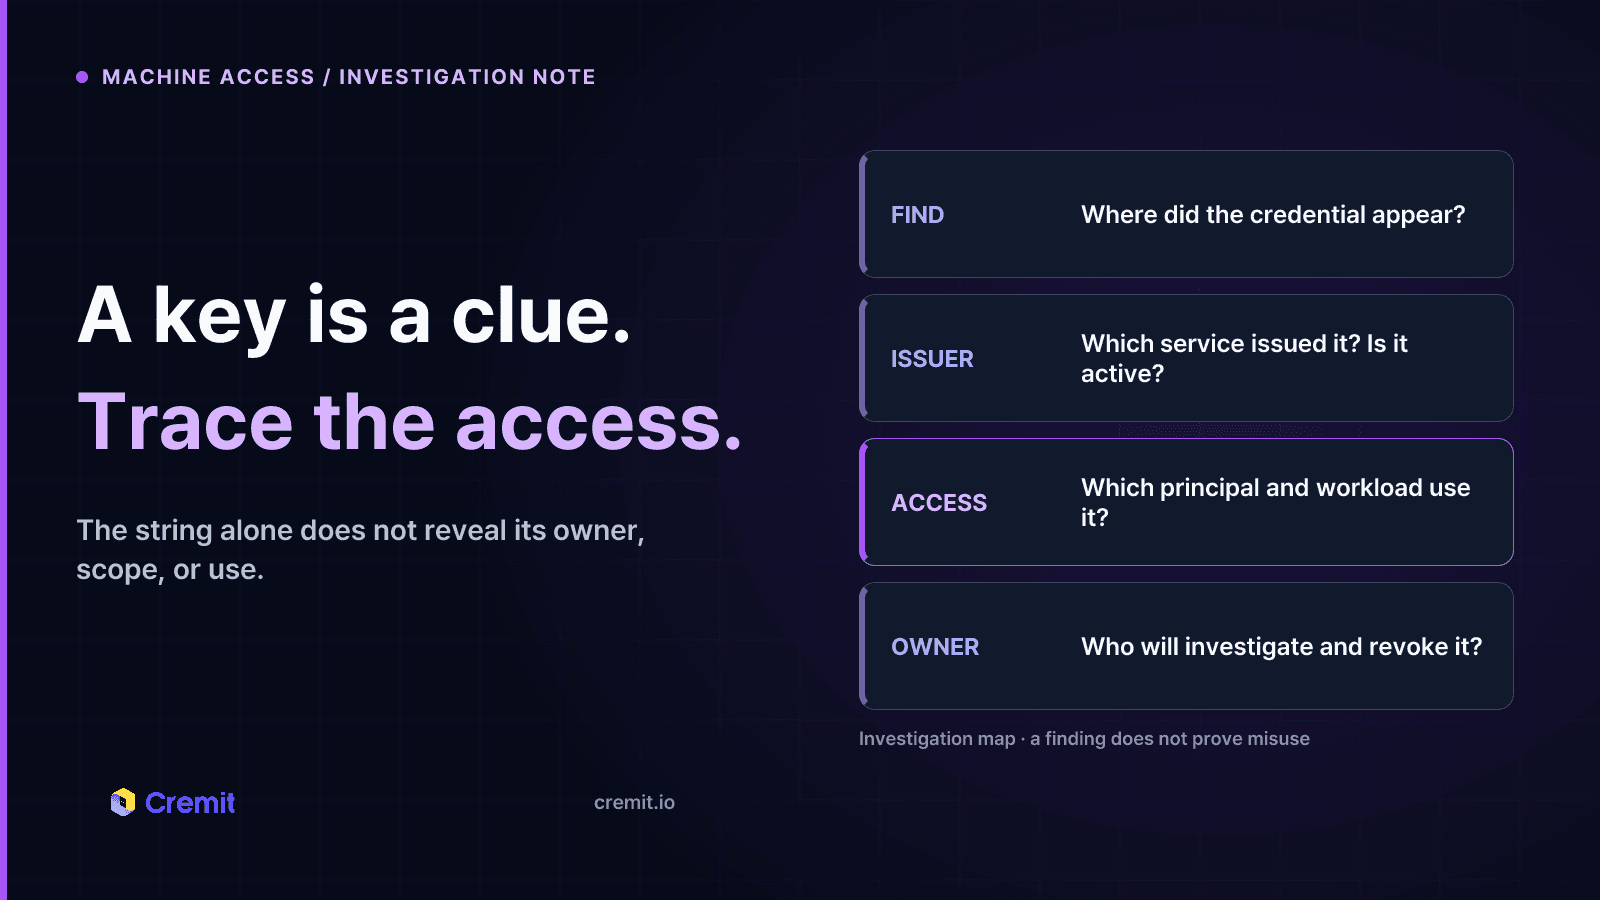
An exposed key is a lead. Connect it to its issuer, principal, permissions, workload, and owner before closing the access path.
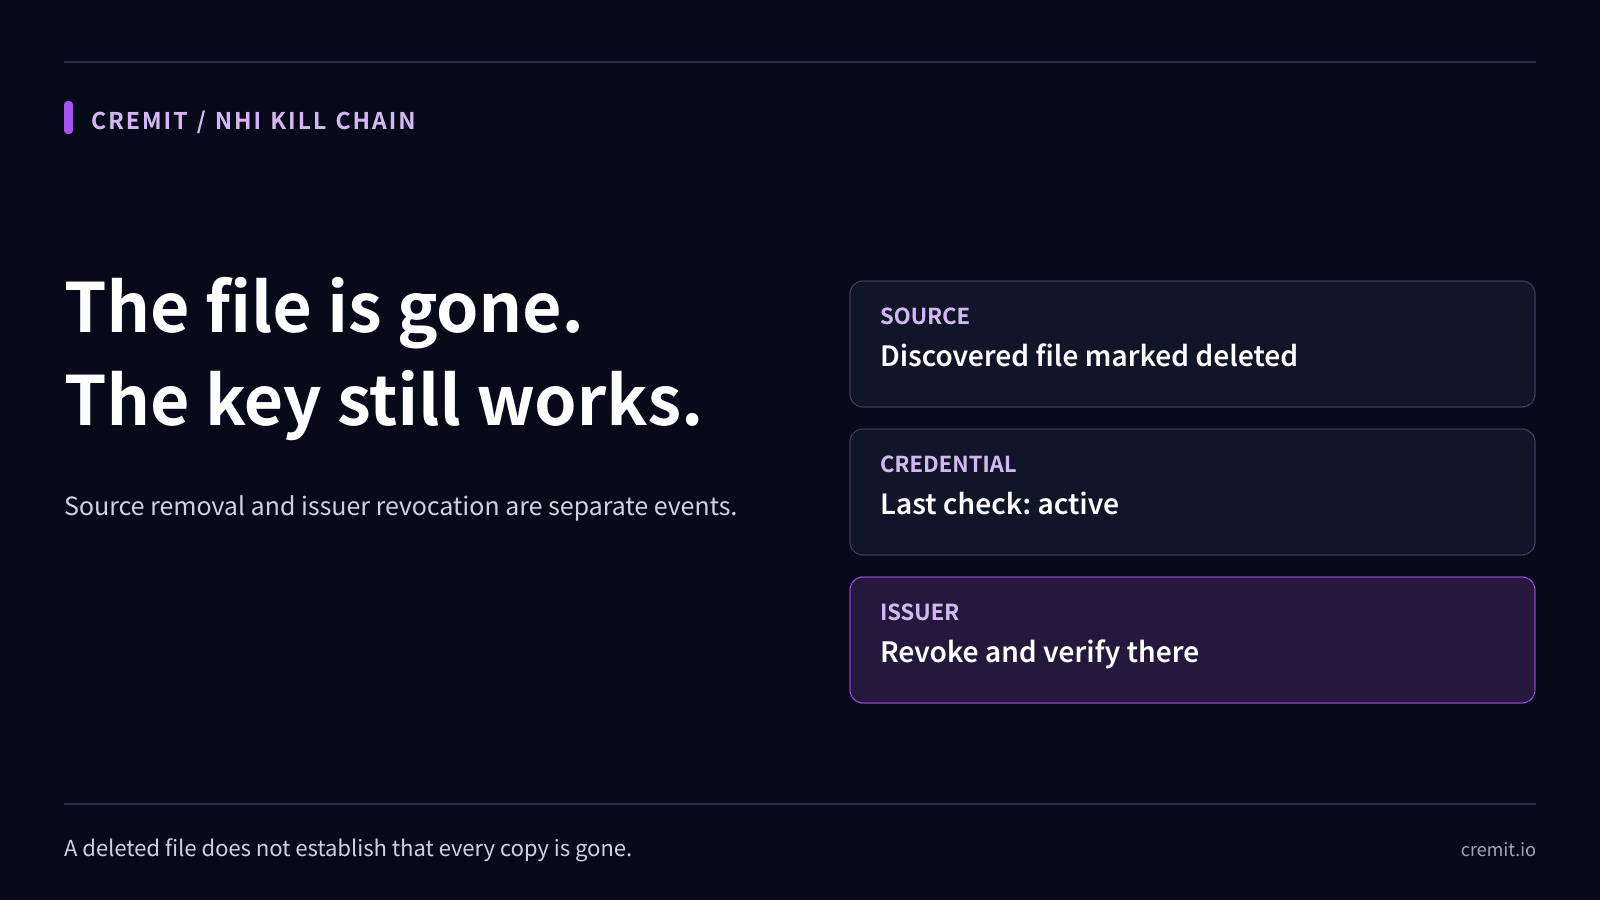
Source removal does not revoke a credential. Check the issuer, Git history, current owner, and last verification before closing the finding.

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.
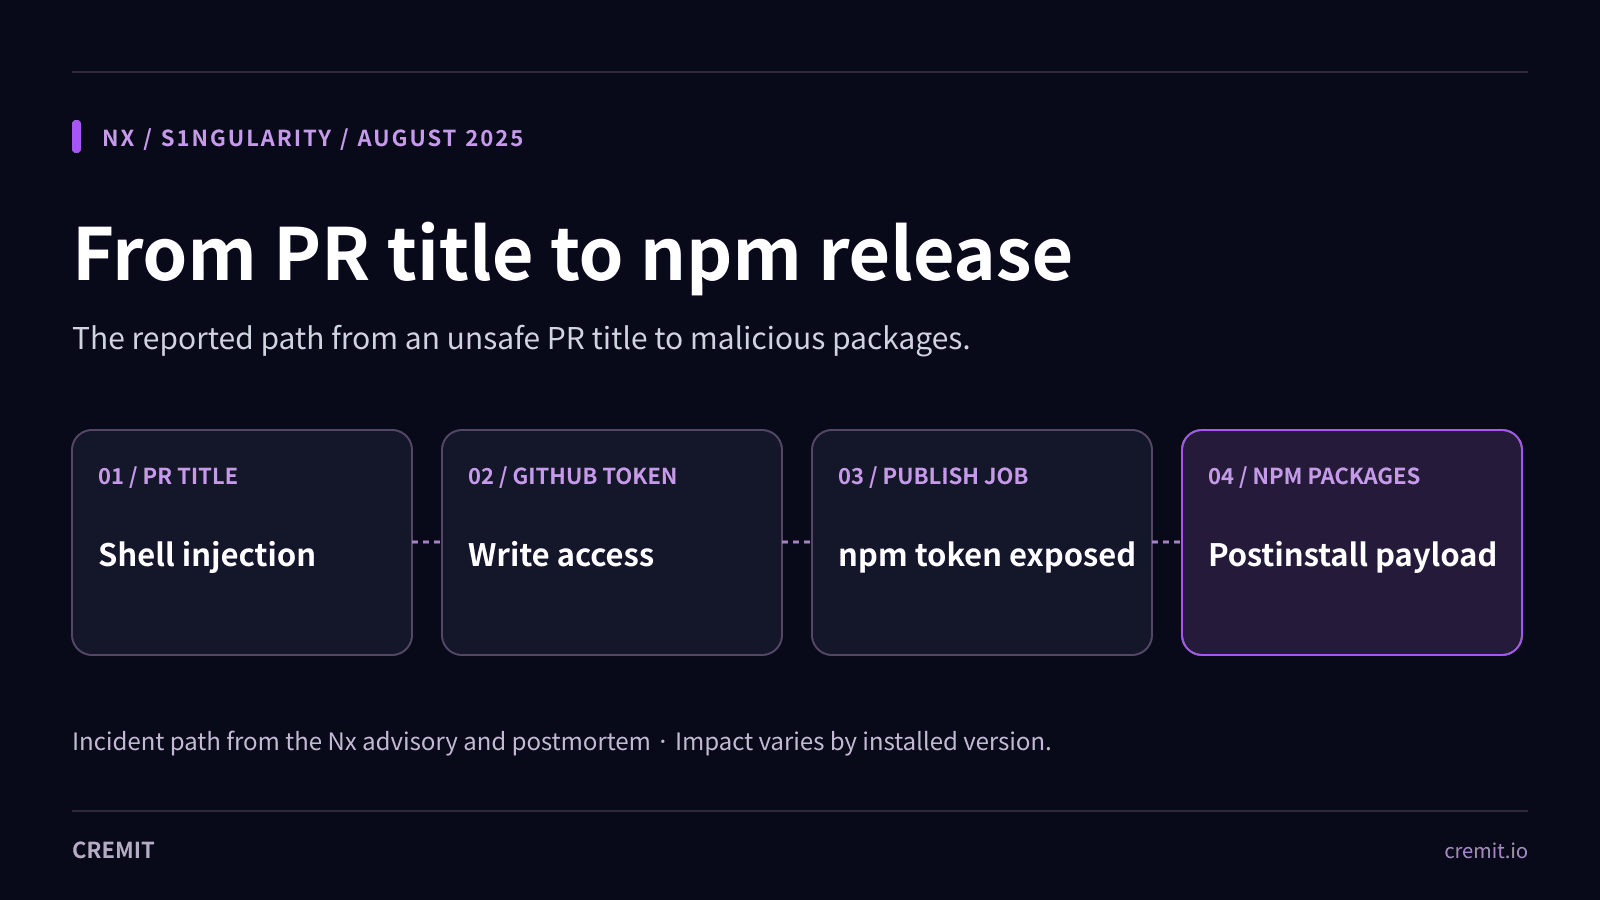
The documented August 2025 Nx attack path, exact affected versions, workstation indicators, and issuer-side response—without an invented victim count.
Find where Next.js puts environment values in client output, distinguish public and secret Stripe keys, and replace a key exposed in a deployment.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy