Jul 19, 2026
AI agent credentials: trace the tool, issuer and responder
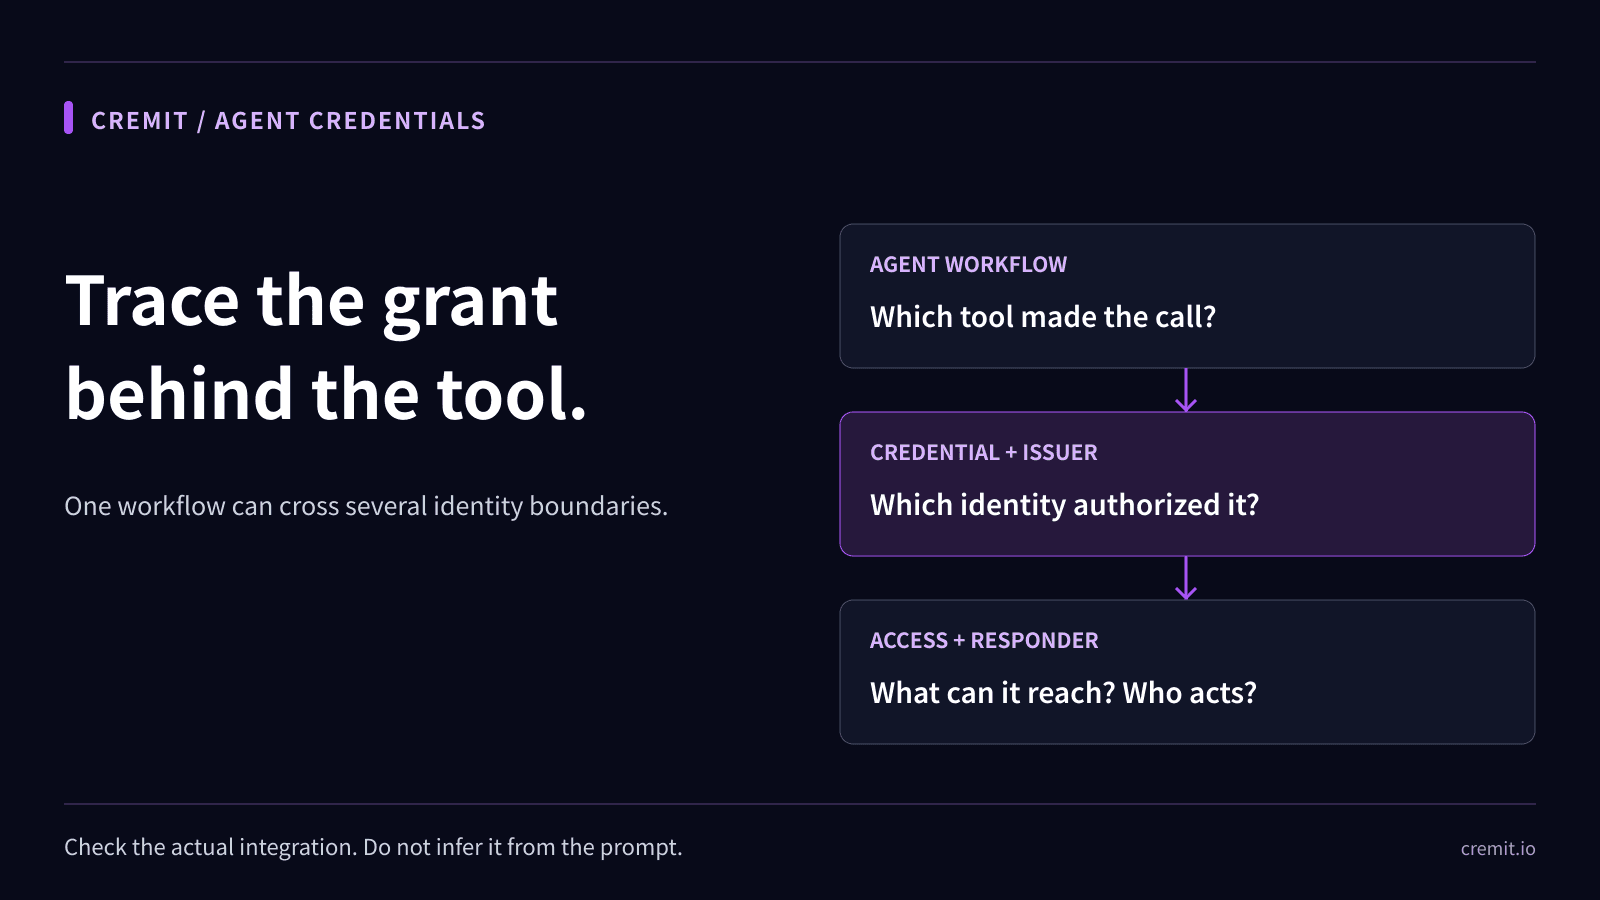
An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.

Ben Kim
An agent workflow may cross several identity boundaries. Trace the actual grant, source location, permissions and owner before judging a leaked key.
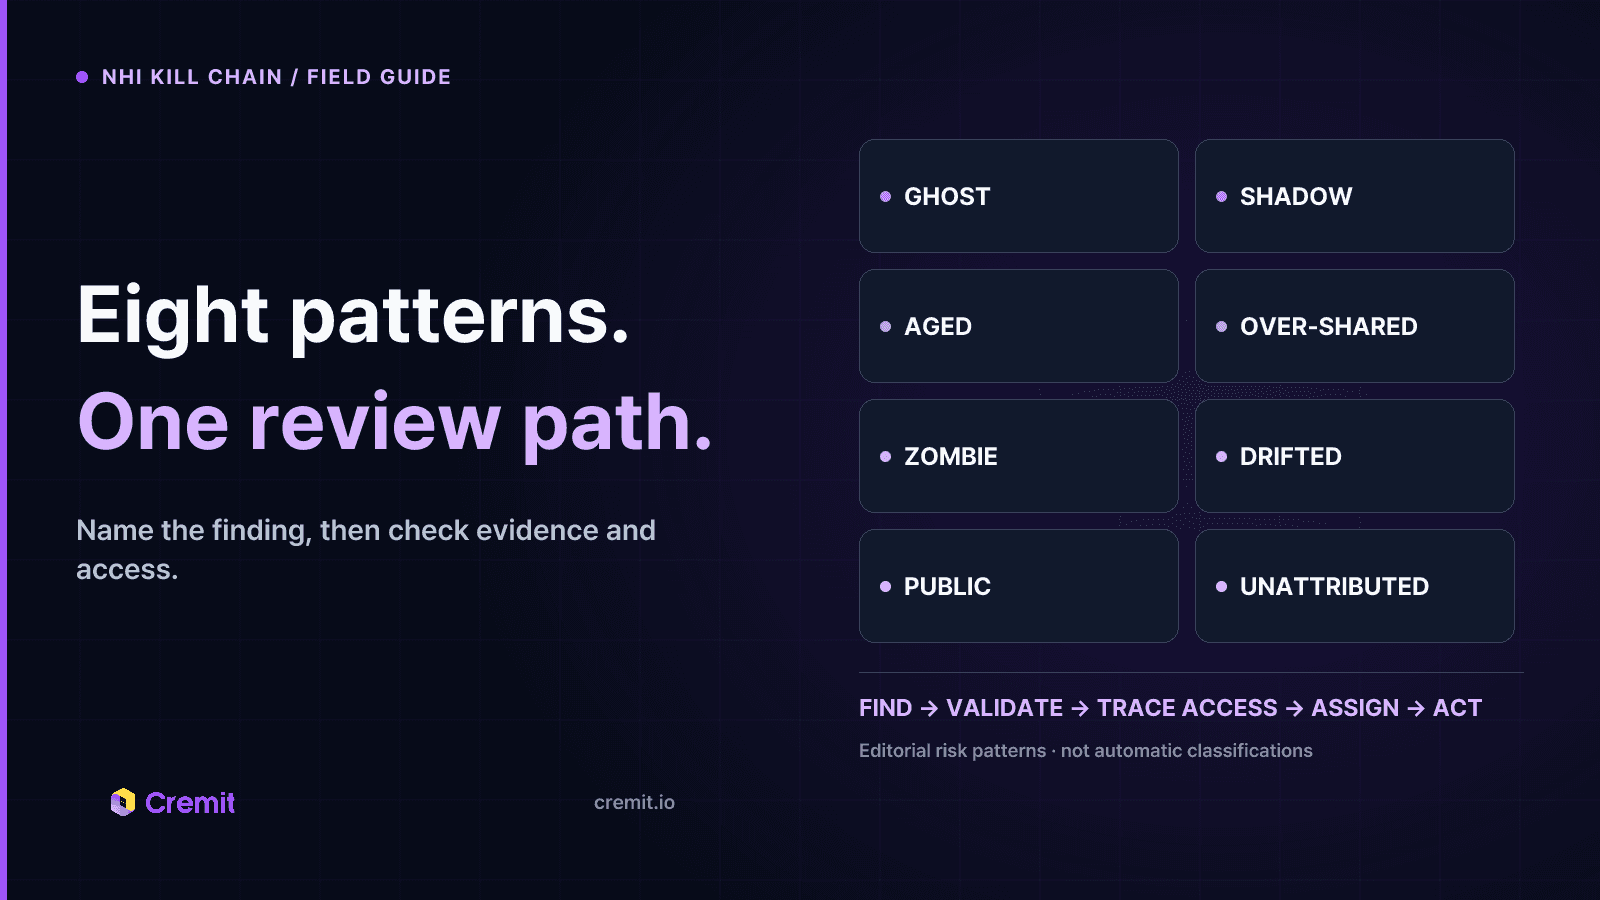
A practical summary of eight NHI credential exposure patterns, the evidence to check, and what Cremit Platform can help investigate.
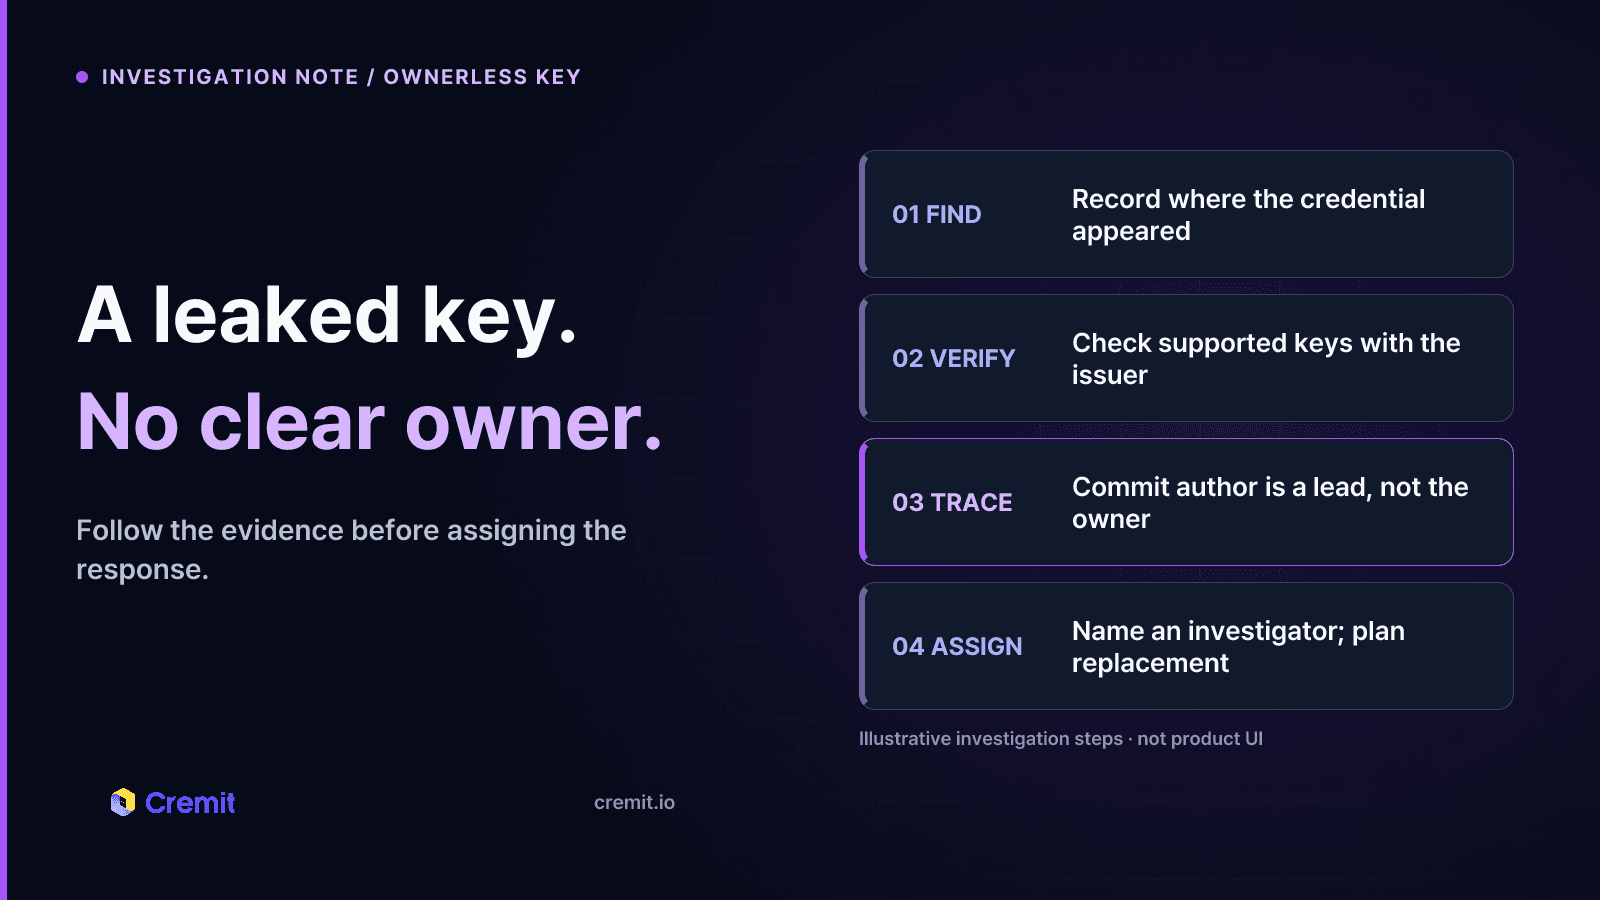
How to verify, investigate, assign, and replace an exposed credential when the service owner is unclear.
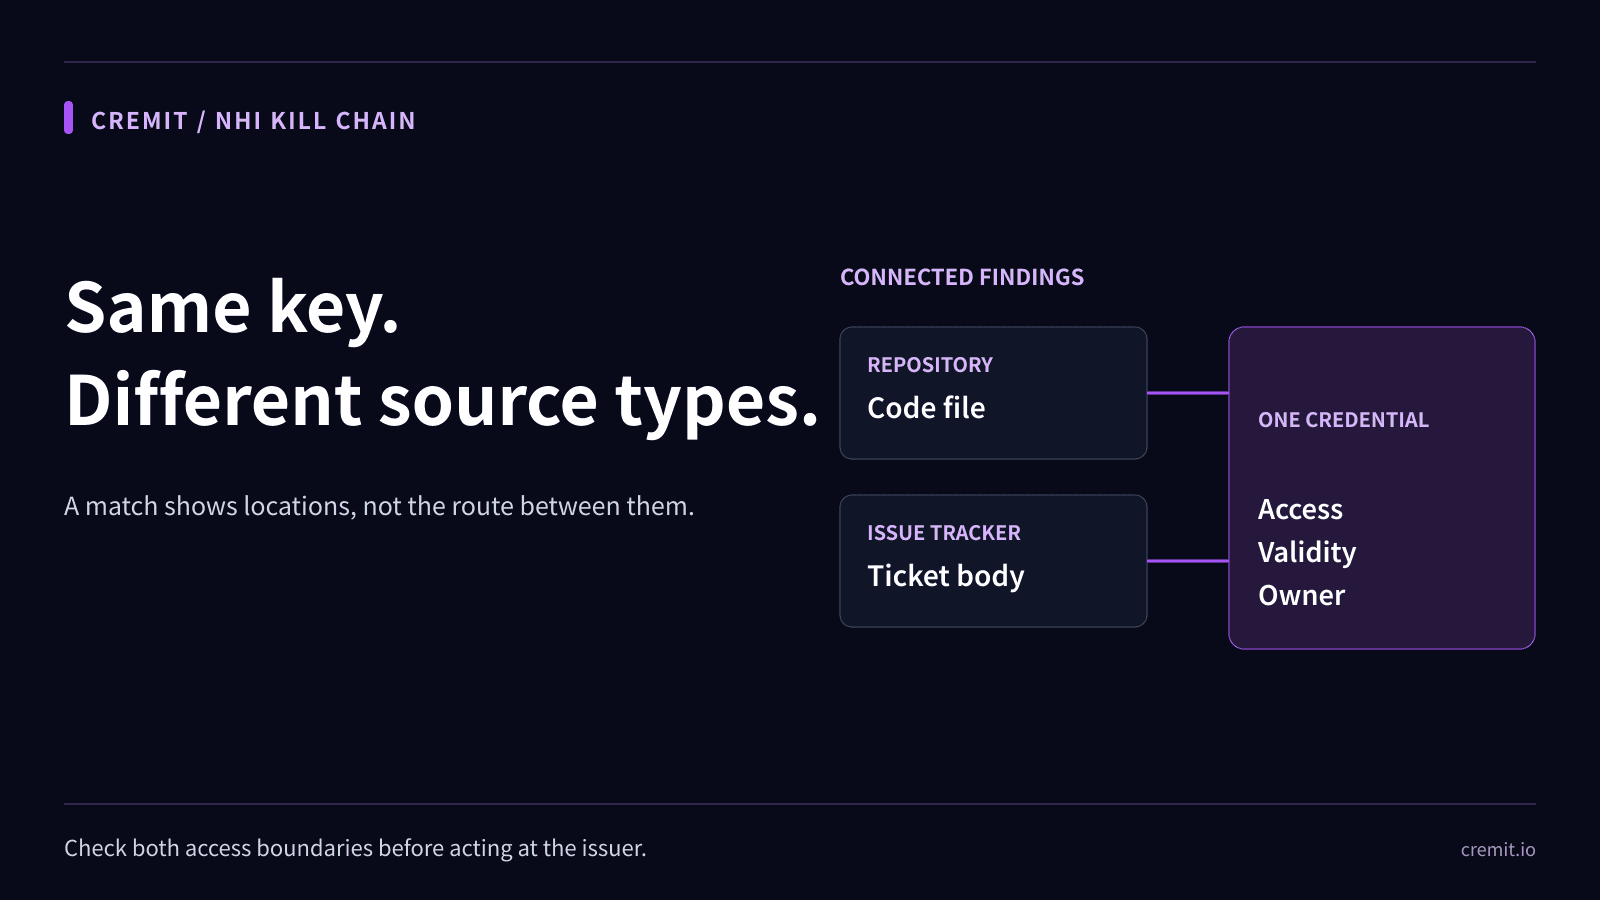
Two source types show two observed locations, not how a credential moved. Check access, issuer status, owner, and actual consumers.
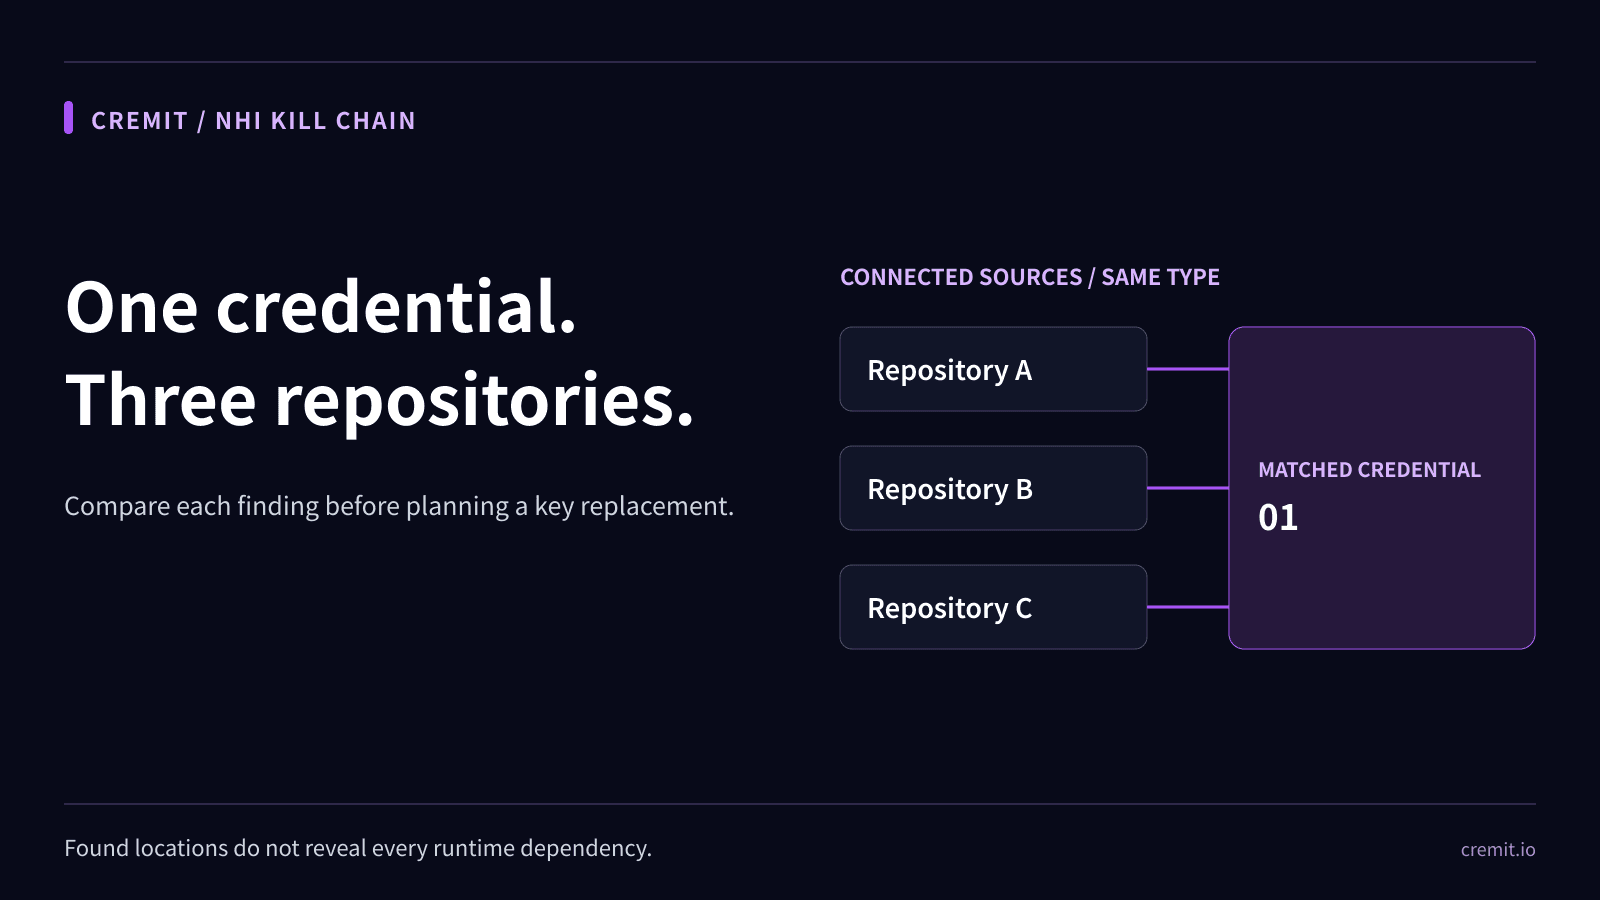
Three observed locations are not a complete dependency map. Check key type, issuer status, permissions, and actual consumers before replacement.
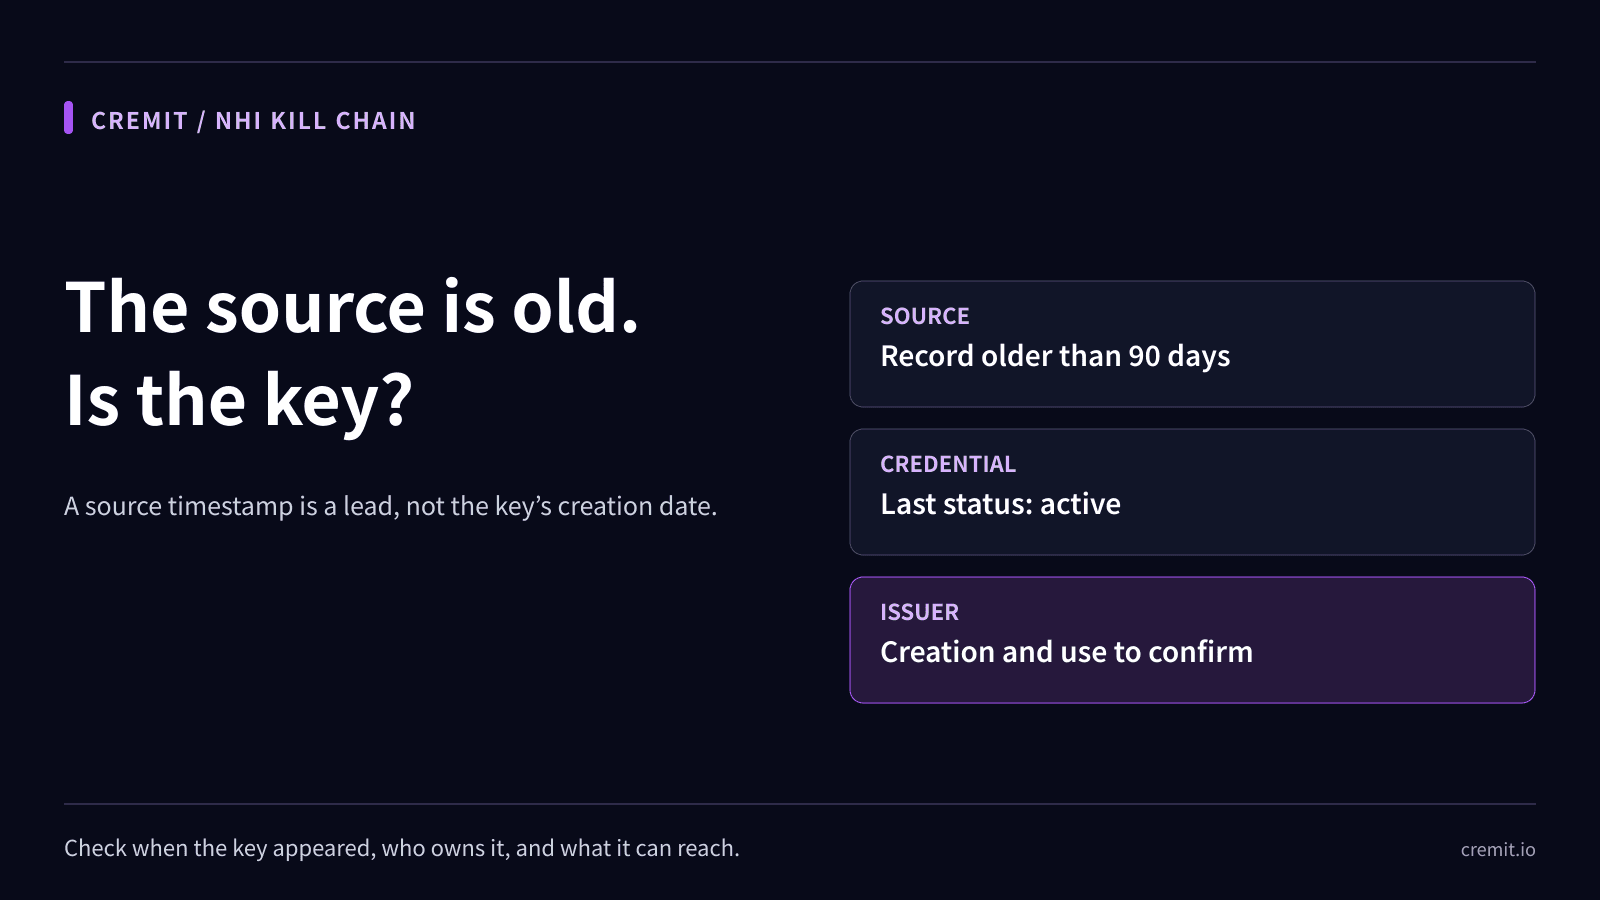
An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.
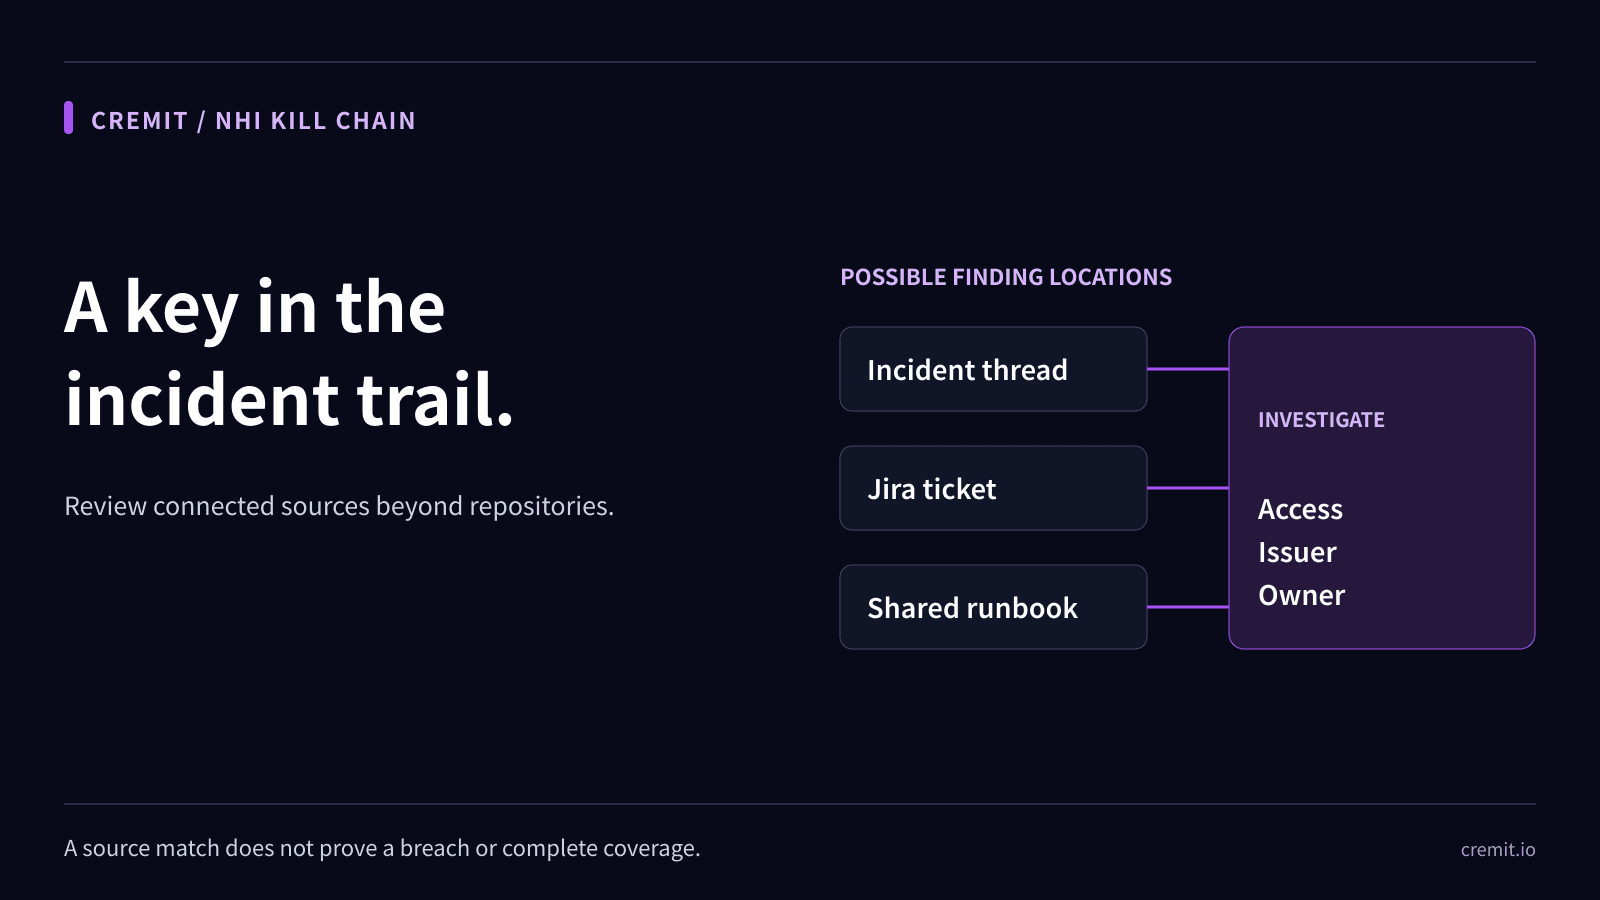
A credential outside a repository needs a source-access review, issuer check, owner, and verified response. A finding alone does not prove misuse.
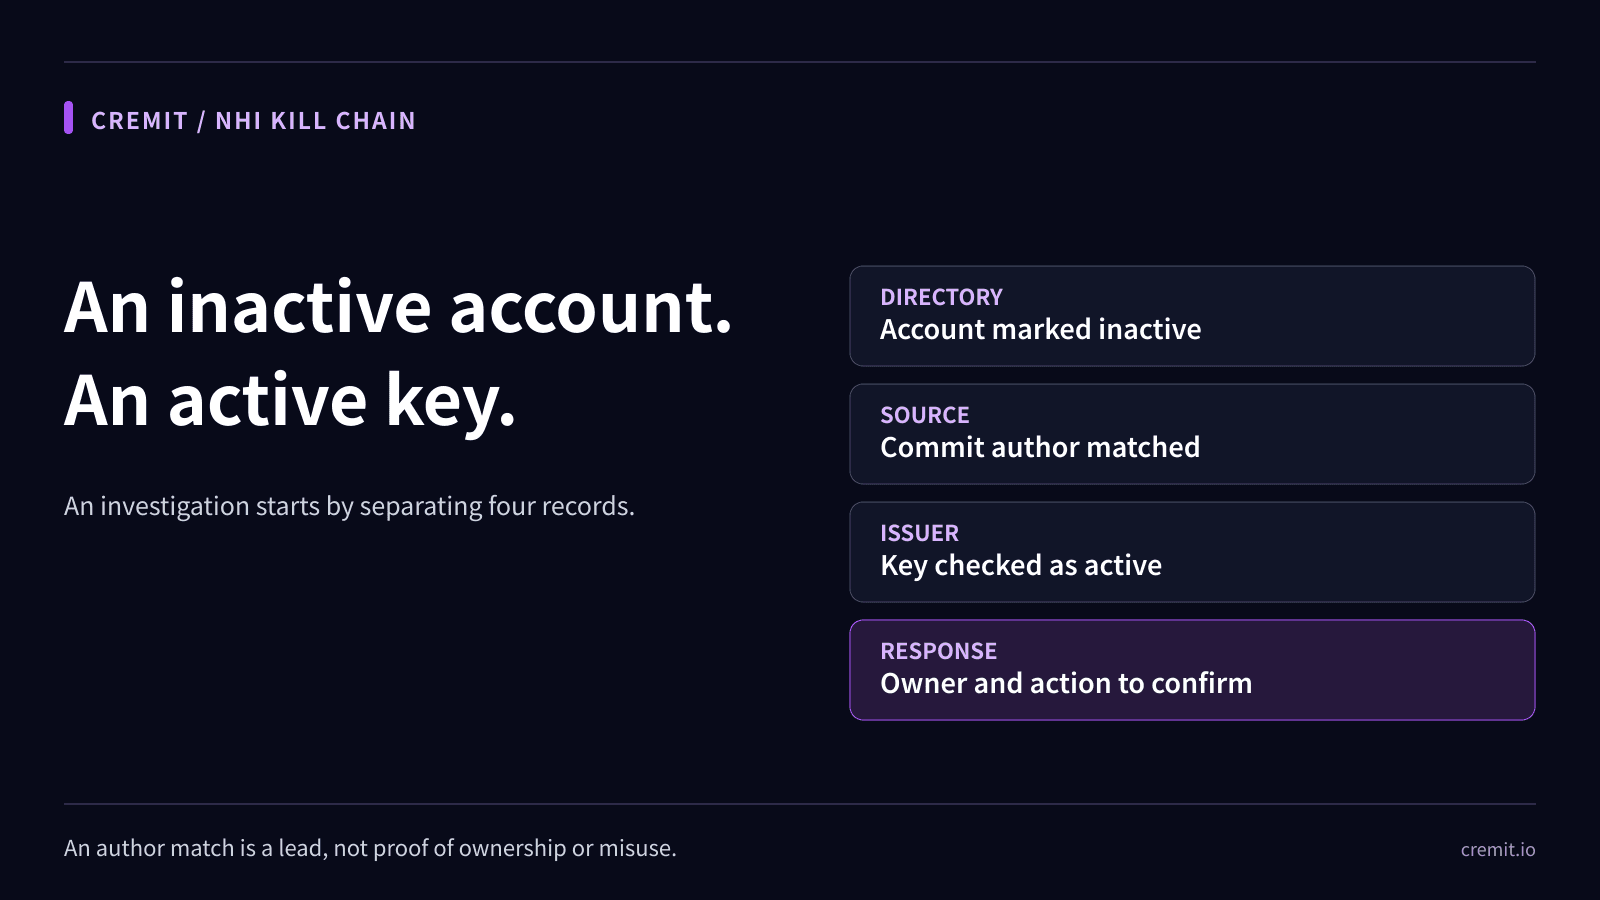
An active key linked to an inactive author is a lead. Check the directory, source, issuer, and current service owner before deciding what happened.

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.
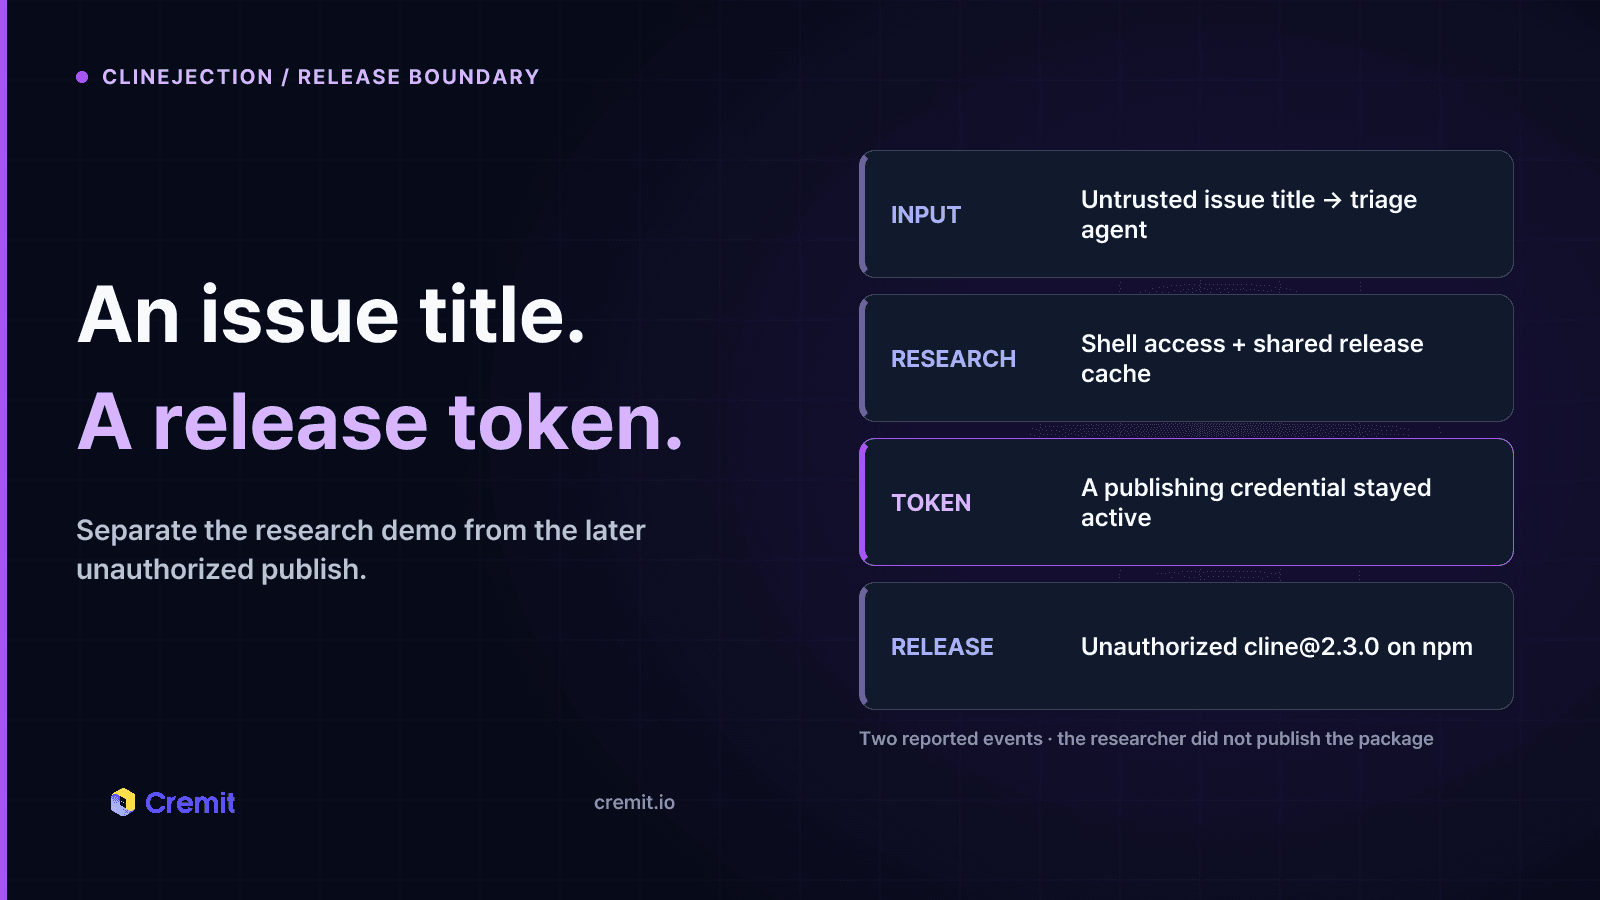
Cline’s issue-triage agent exposed a path to publishing credentials. A later unauthorized CLI release installed OpenClaw; Cline found no user data theft.
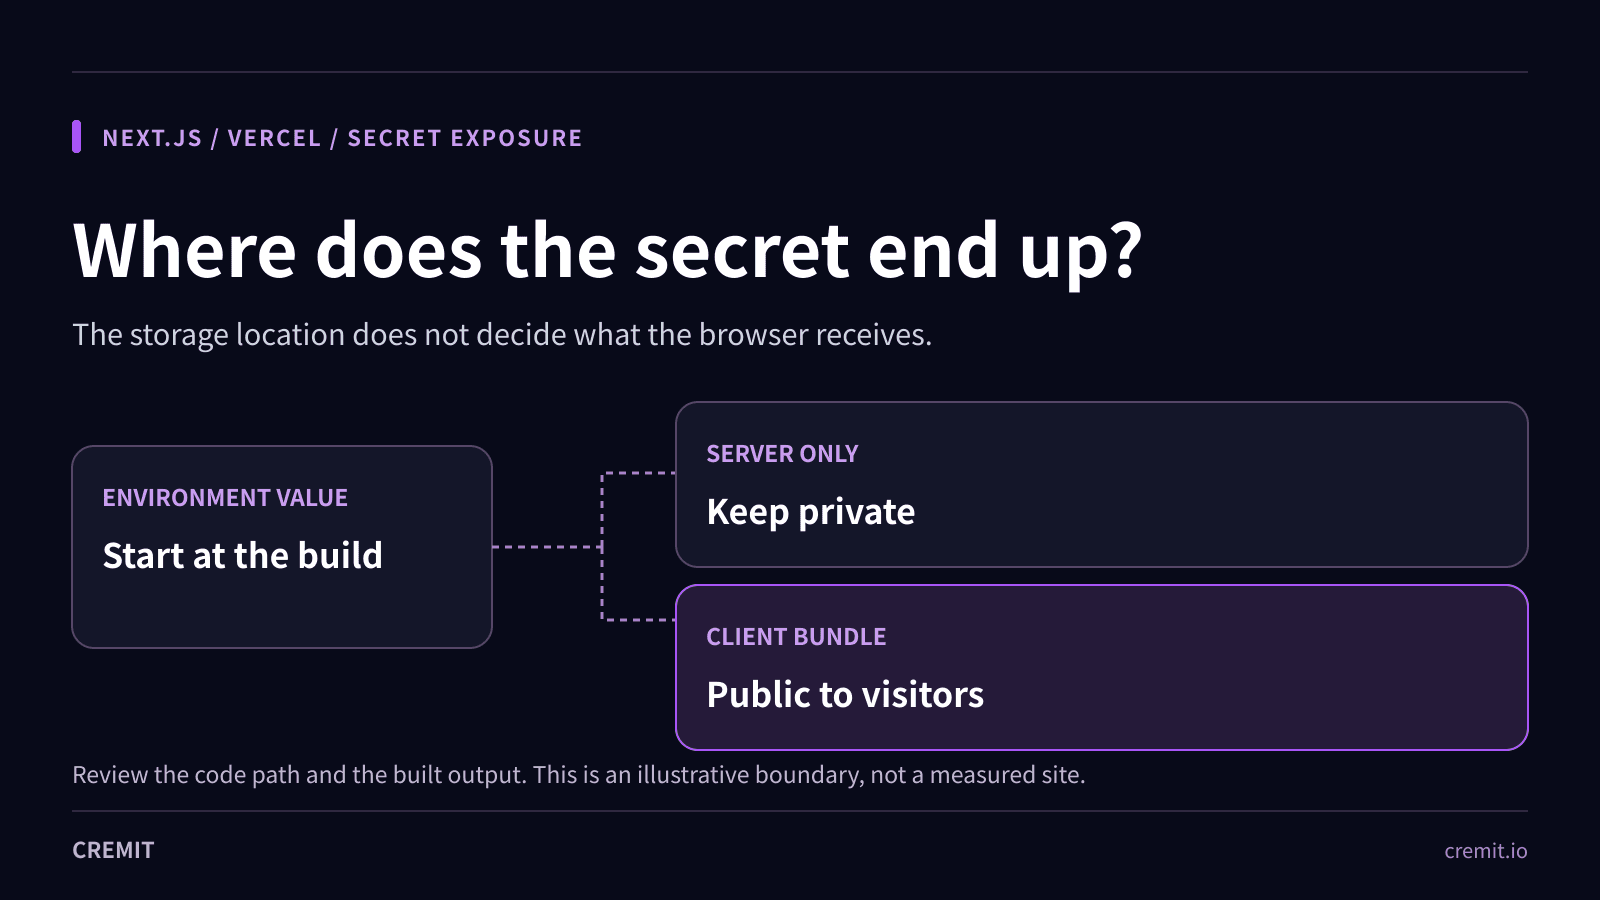
Find where Next.js puts environment values in client output, distinguish public and secret Stripe keys, and replace a key exposed in a deployment.
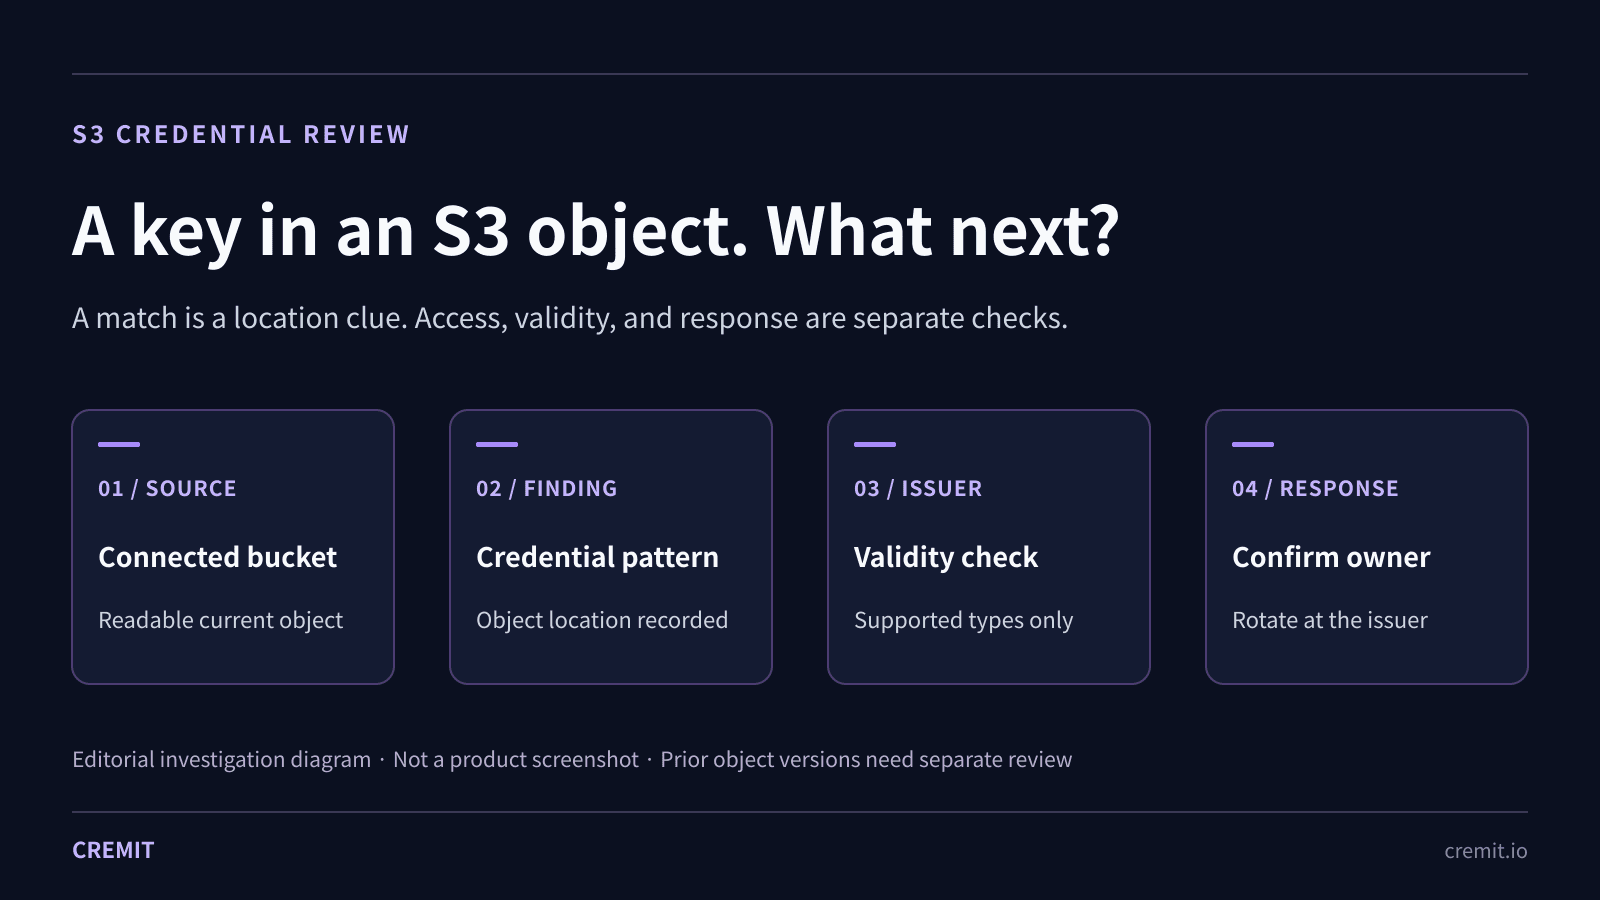
A key-shaped string in S3 does not prove public access, a live credential, or misuse. Check the object, issuer, scan coverage, and earlier versions.
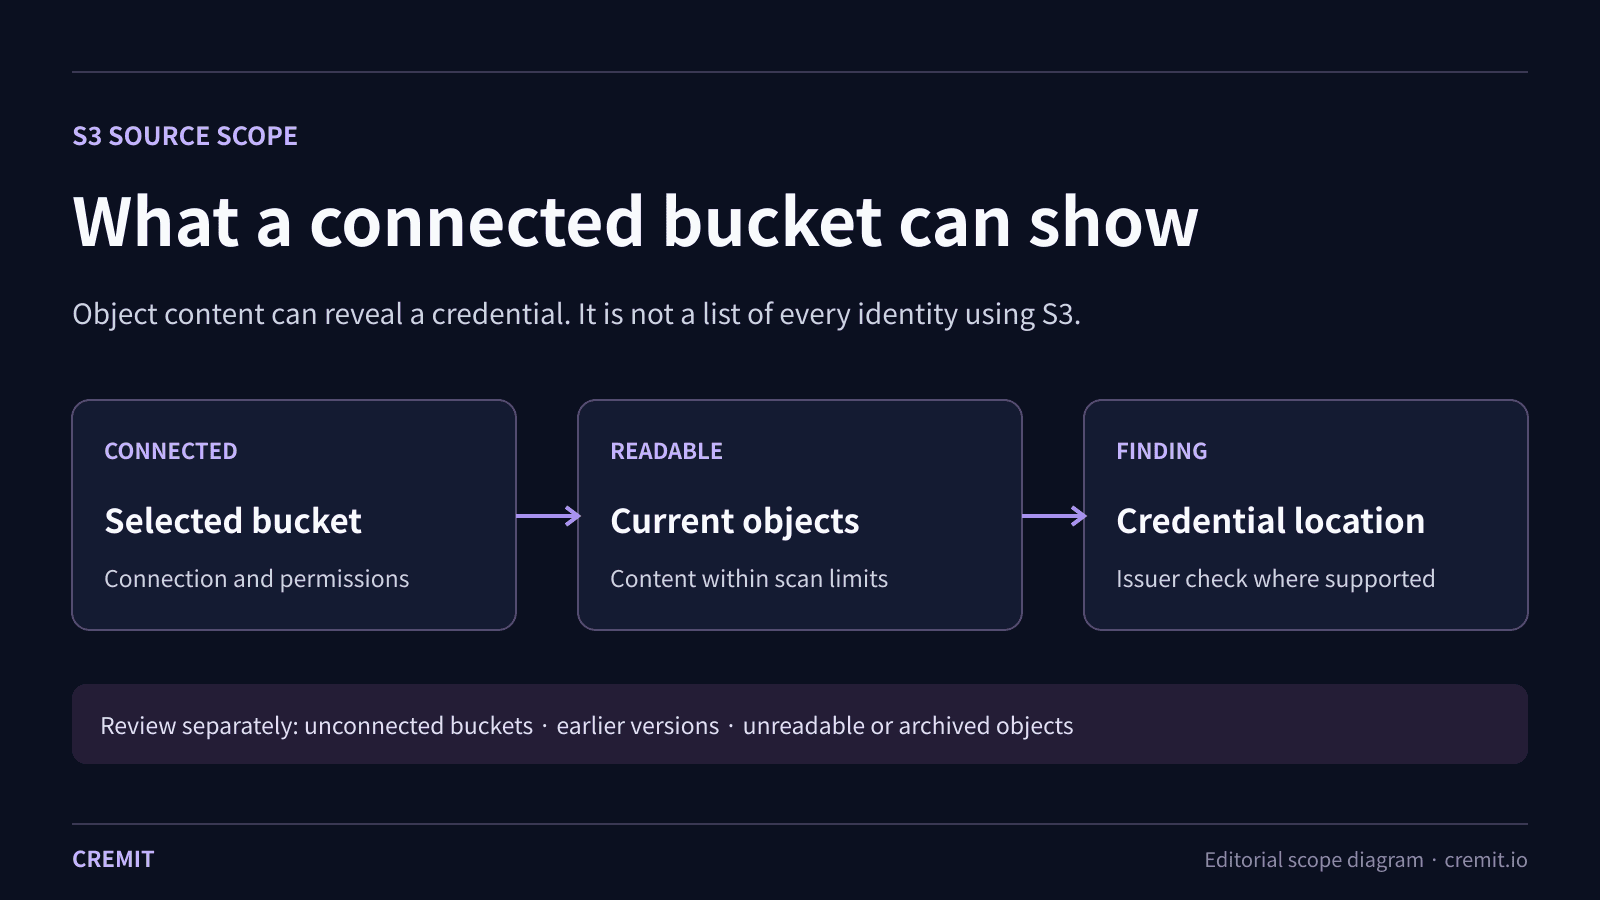
Cremit reads supported current objects in connected S3 buckets to locate credentials. Check access, skipped objects, earlier versions and the issuer separately.
Cremit has joined the AWS SaaS Spotlight program for early-stage SaaS startups in Asia Pacific.
Optional cookies count visits, identify visiting companies, and measure ads. You can decline. Cookie policy