NEW · Blast Radius: a field playbook for leaked API keys on AWS, GCP and Azure
Back to Blog
Tag

CI/CD Security

9 posts
GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History
Oct 11, 2026

GhostAction Analysis: How a Malicious Workflow Collects Keys from Git History

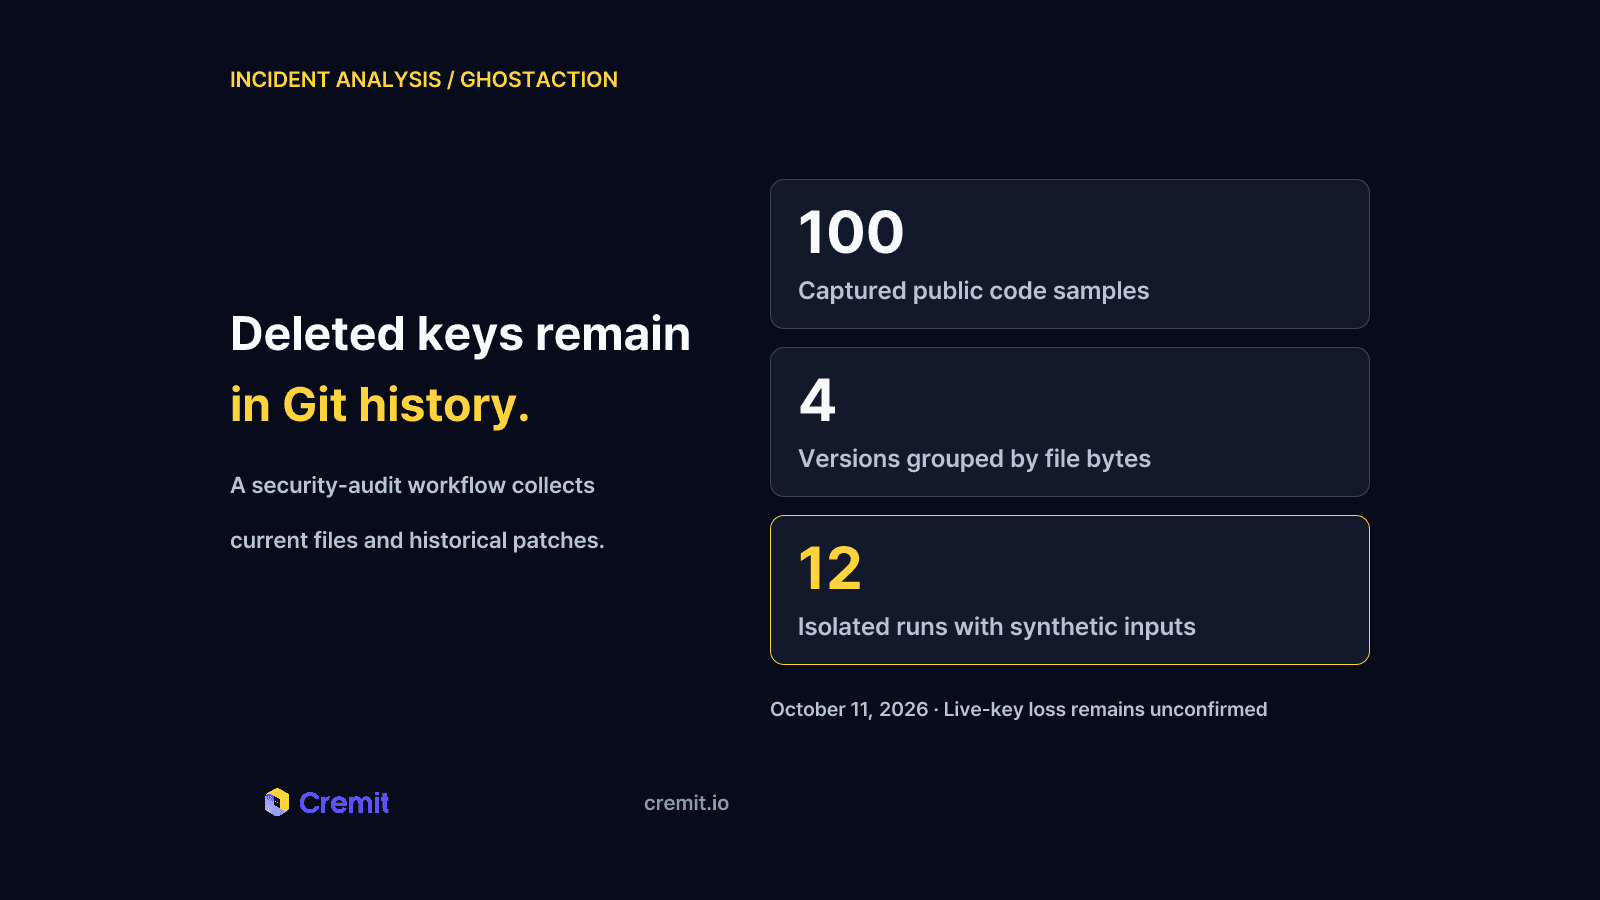
A review of 100 public workflow samples and Uber repository events shows four collector versions. We examine deleted-key collection through Git patches, successful exits after transfer failure, and credential-based response priorities.

Ben Kim
Ben Kim
Your Slack Webhook Is Write-Only, Until an AI Agent Reads the Channel
Jun 13, 2026

Your Slack Webhook Is Write-Only, Until an AI Agent Reads the Channel

A leaked Slack incoming webhook is usually triaged as low severity: write-only, one channel, no data access. The moment an AI agent reads that channel and can act with tools, that write-only primitive becomes an indirect prompt injection path into the agent's privileges. Here is the full kill chain, the exact preconditions, and how to defend it.

Ben Kim
Ben Kim
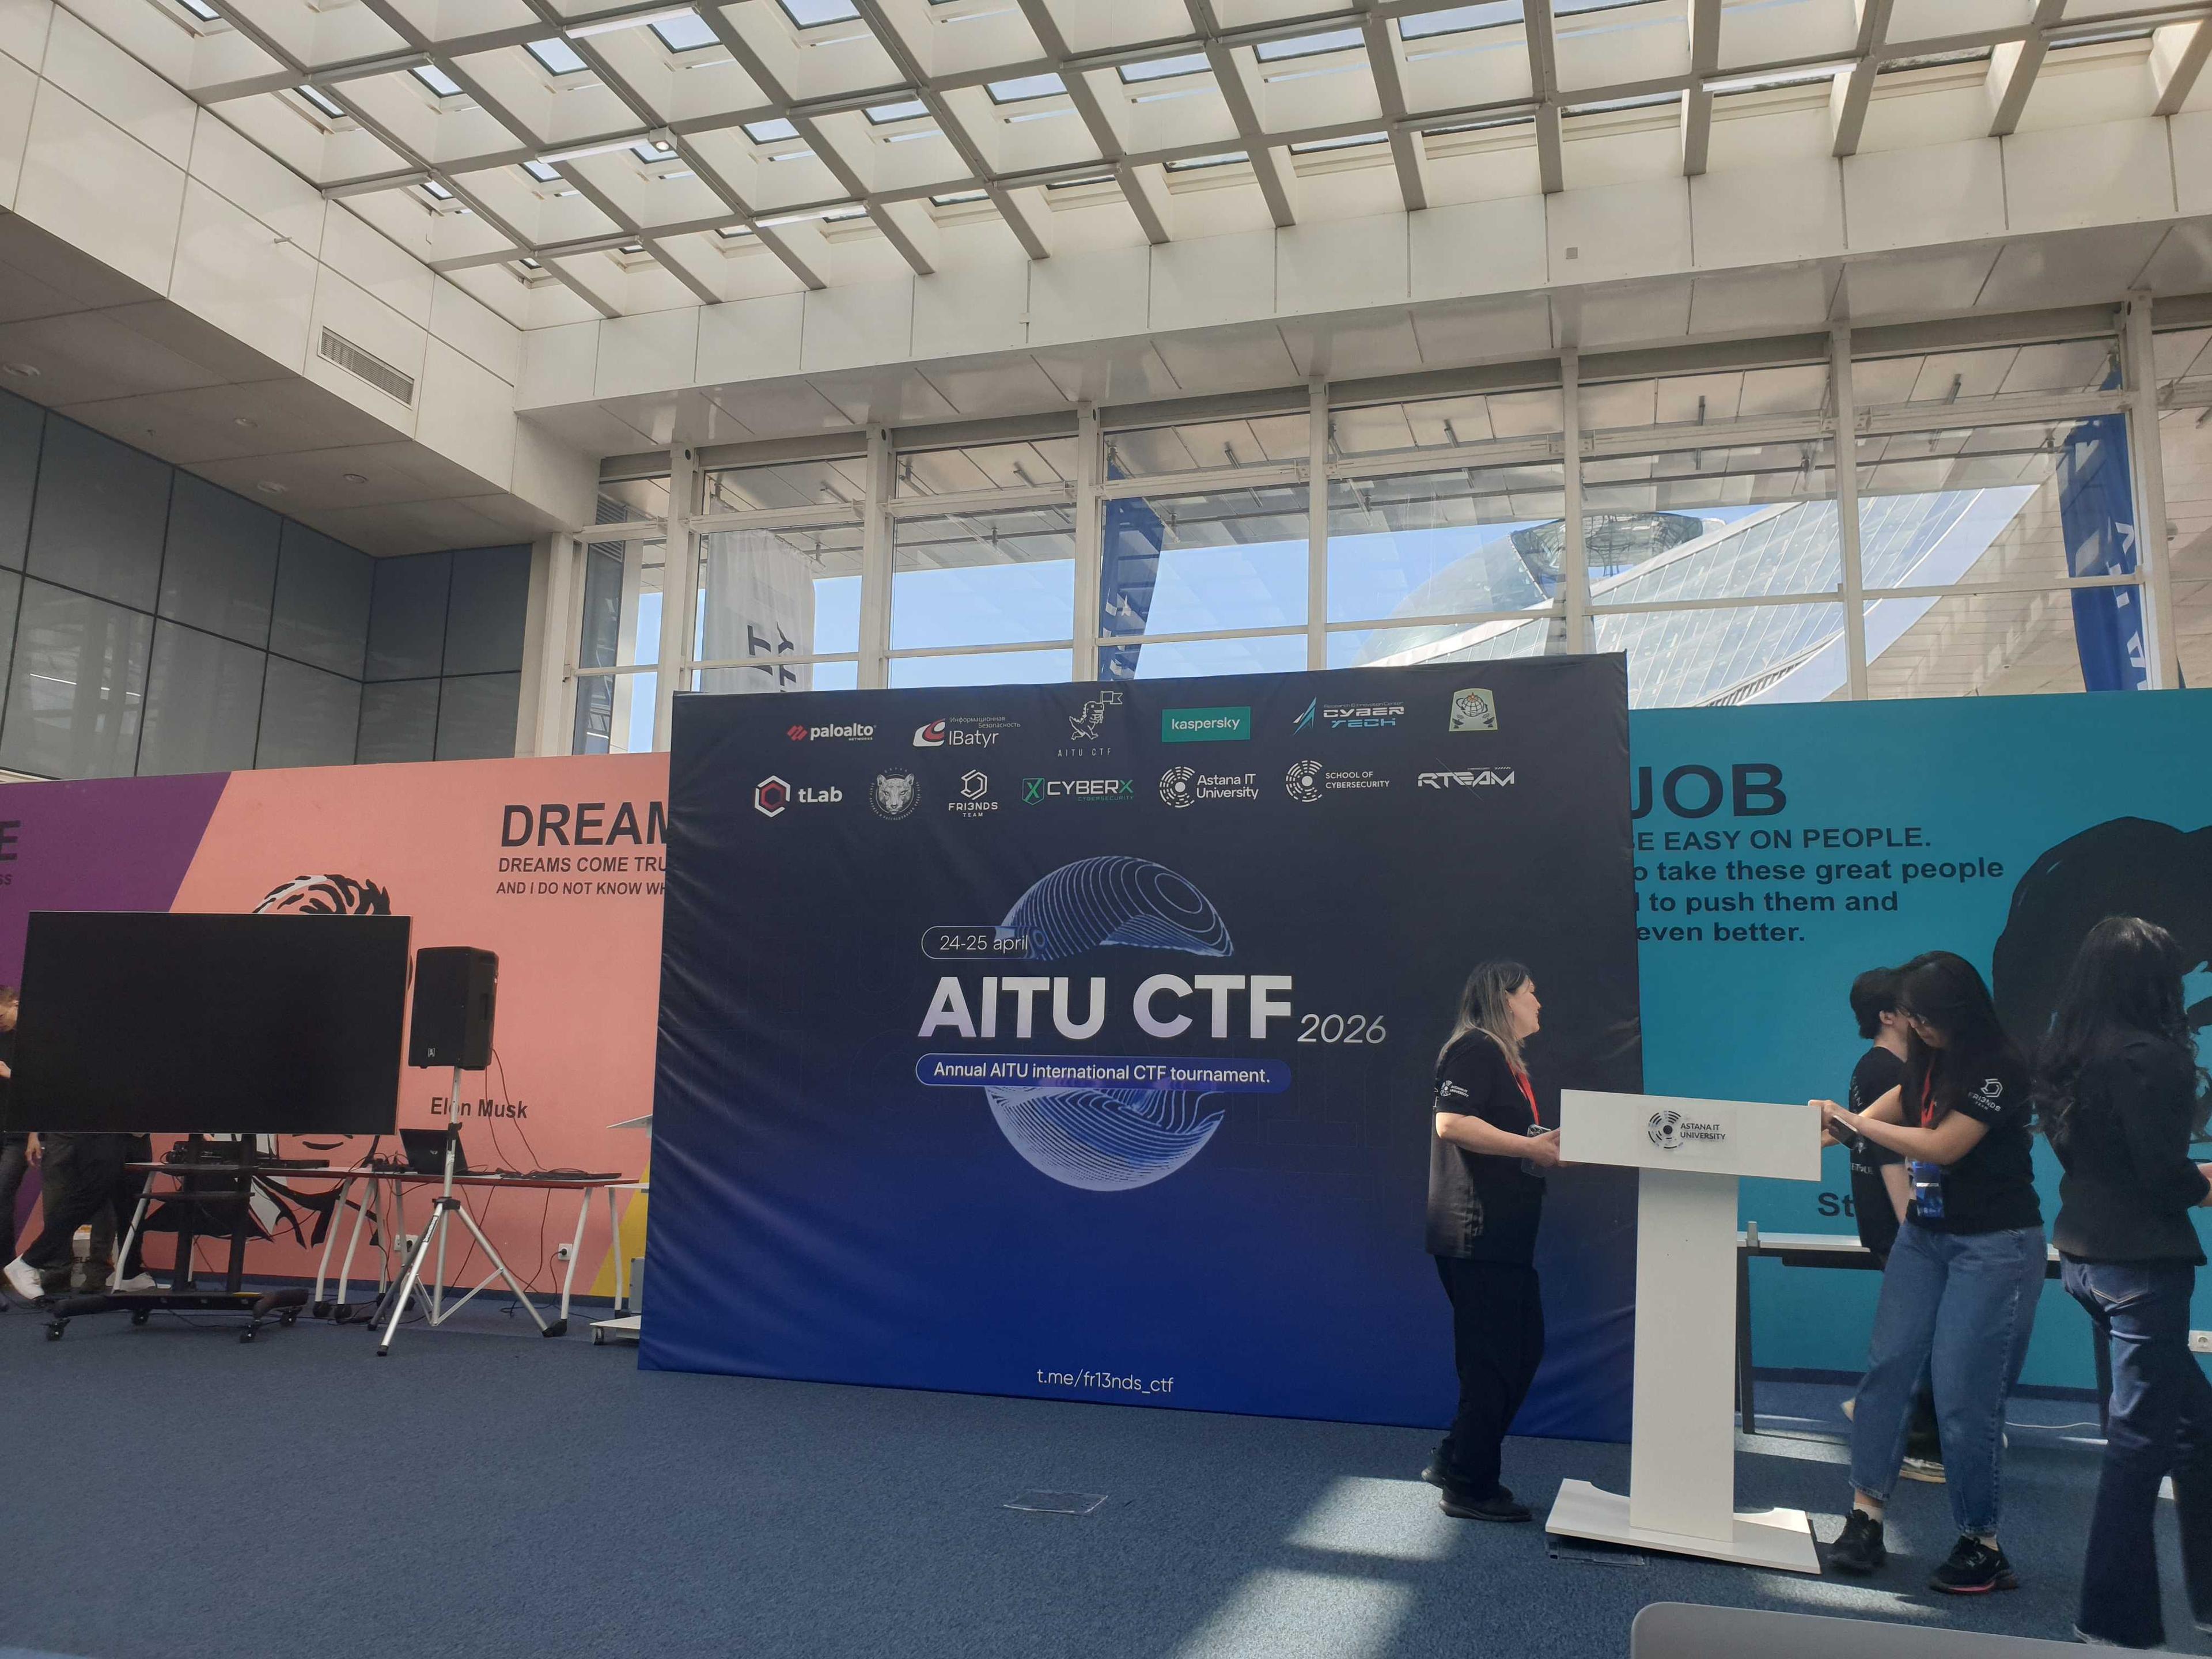
AITU CTF Final 2026 Writeup
Apr 29, 2026

AITU CTF Final 2026 Writeup

Full writeup of the AITU CTF Final (April 25-26, 2026), a HackCity-format competition. We walk through exploiting DMZ hosts via XXE, SSTI, and SQLi, pivoting into the DEV segment through AD lateral movement, escaping a privileged Docker container via cgroup abuse, and breaching a healthcare system through JWT JKU header injection.

Ethan Kim
Ethan Kim
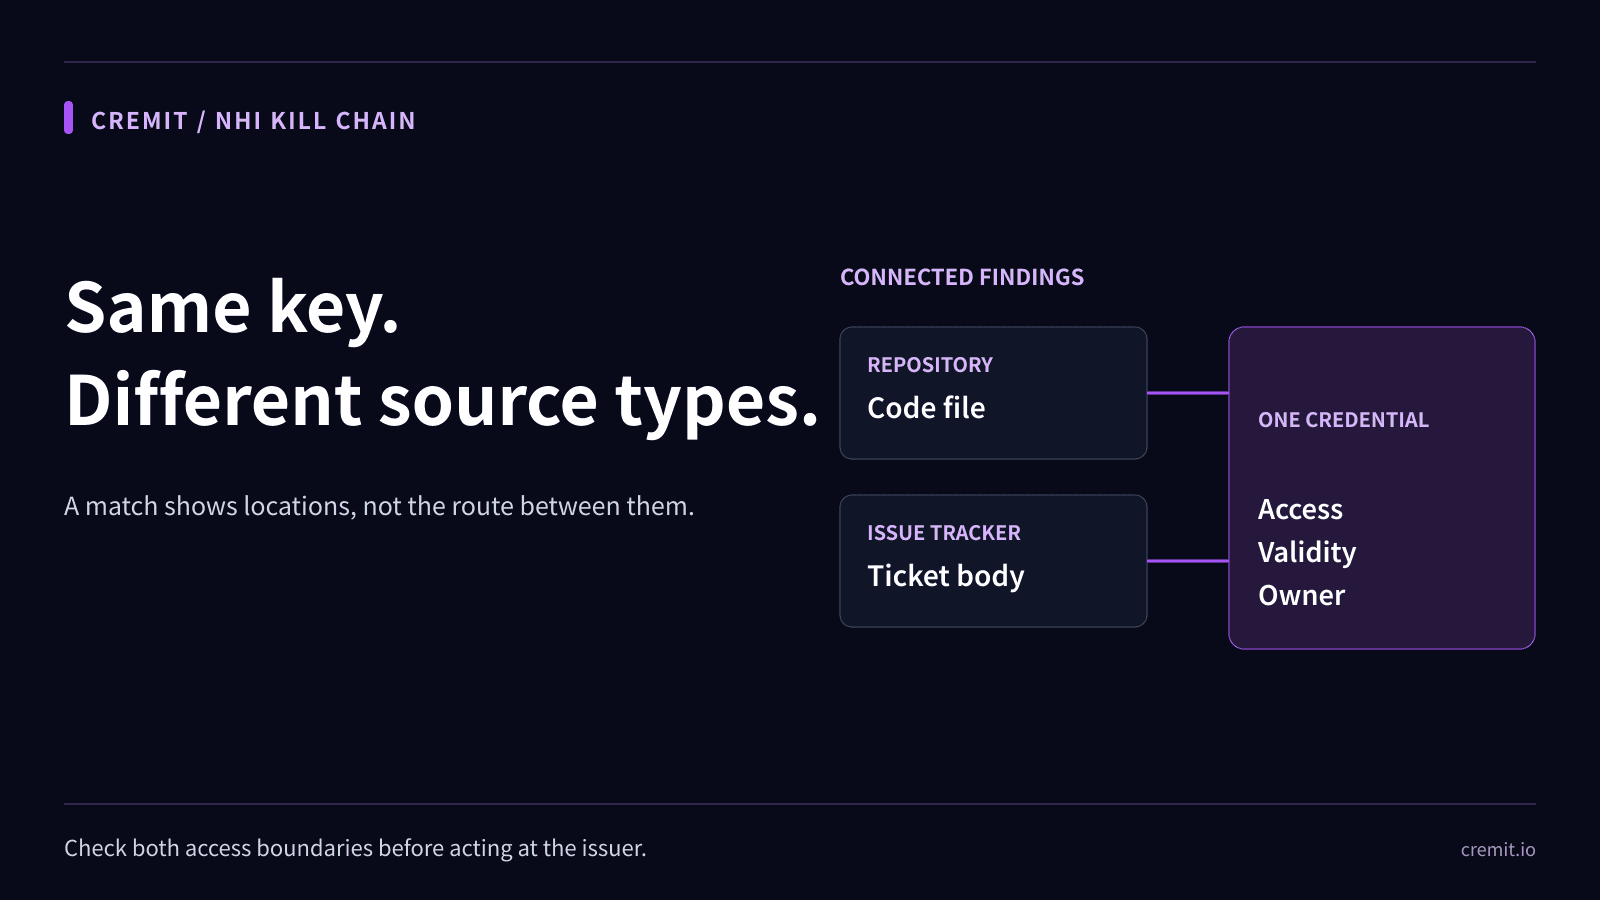
Same key in a repository and ticket: investigating cross-platform findings
Apr 17, 2026

Same key in a repository and ticket: investigating cross-platform findings

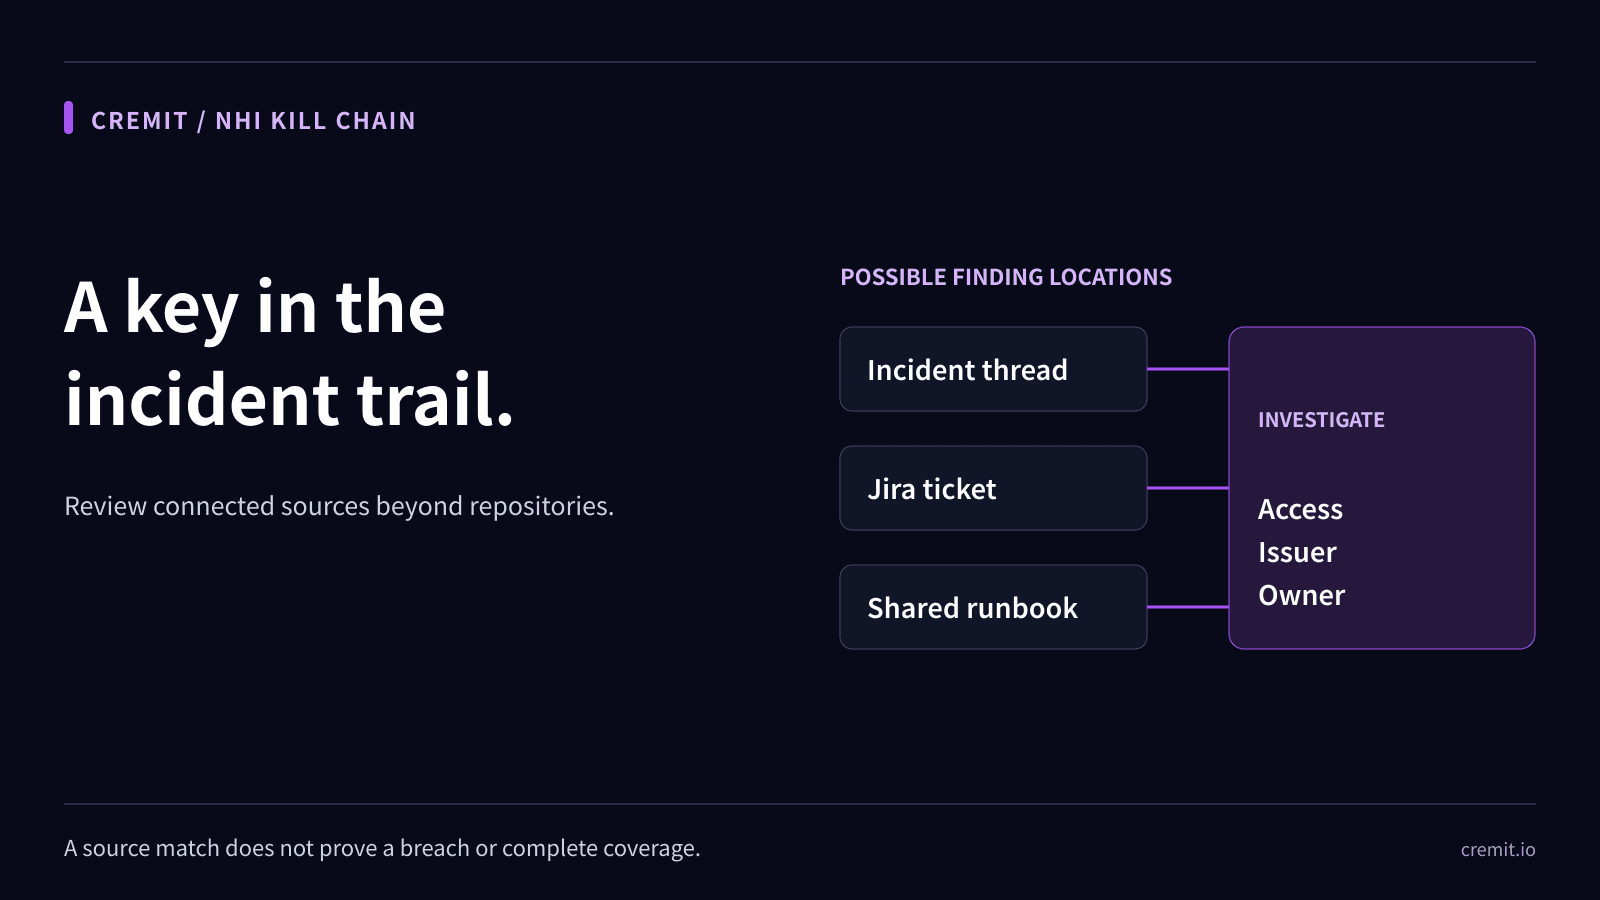
Two source types show two observed locations, not how a credential moved. Check access, issuer status, owner, and actual consumers.

Ben Kim
Ben Kim
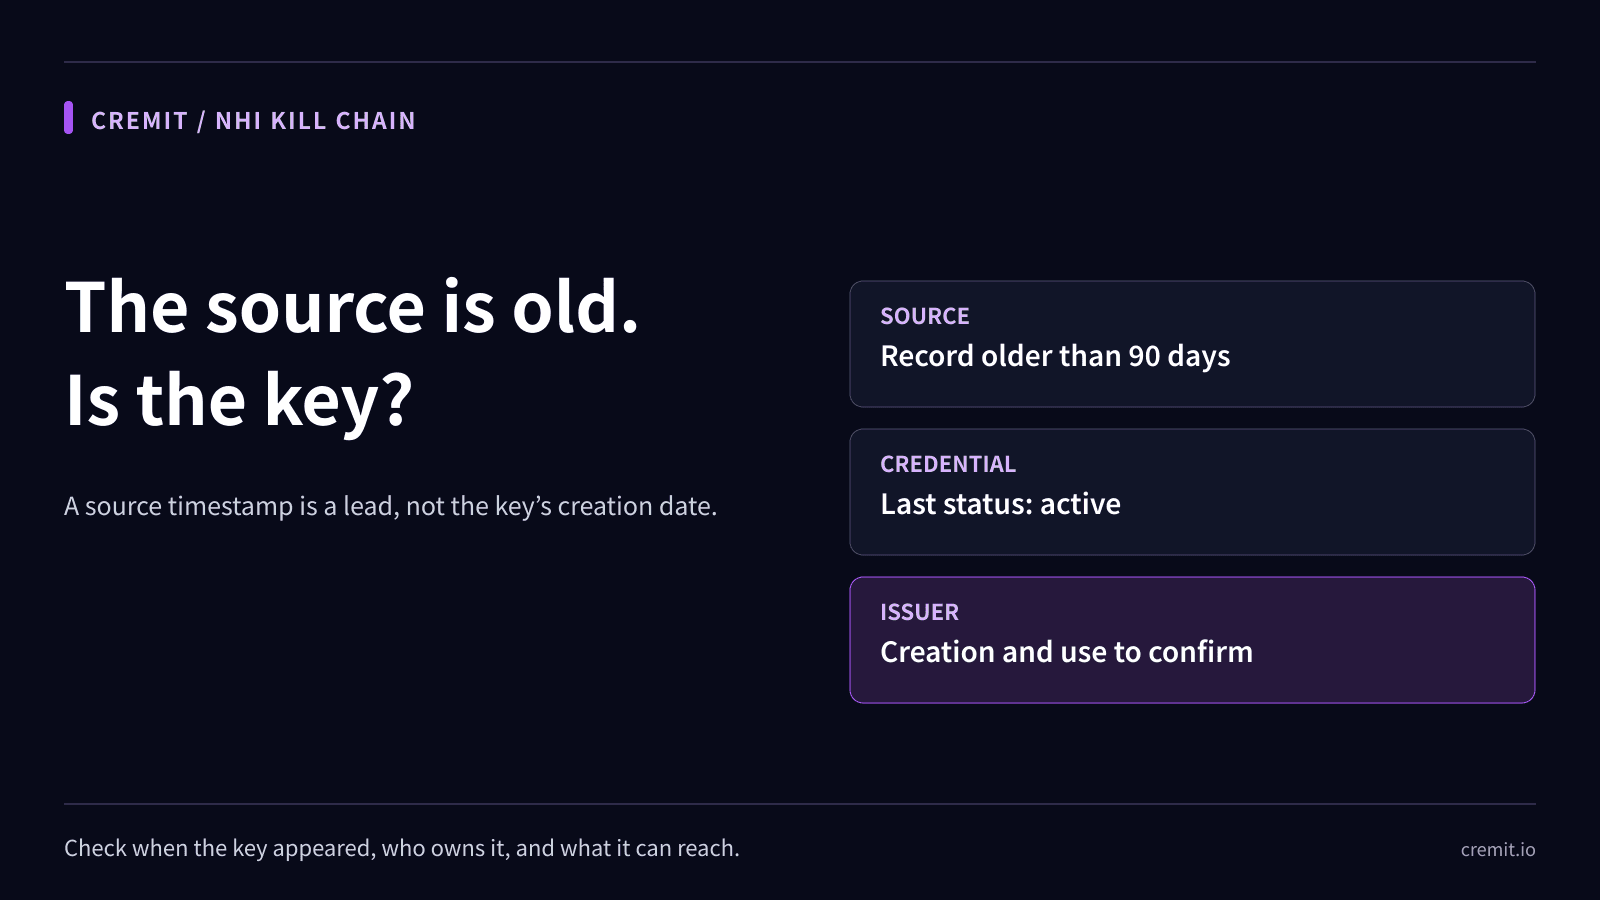
Long-exposed credentials: what a 90-day source record tells you
Apr 10, 2026

Long-exposed credentials: what a 90-day source record tells you

An old source record and an active key do not establish key age. Check when the value appeared, issuer status, permissions, and dependencies.

Ben Kim
Ben Kim
API keys in incident chats and tickets: what to investigate
Apr 5, 2026

API keys in incident chats and tickets: what to investigate

A credential outside a repository needs a source-access review, issuer check, owner, and verified response. A finding alone does not prove misuse.

Ben Kim
Ben Kim
When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack
Mar 25, 2026

When the Security Scanner Became the Weapon: A Cyber Kill Chain Analysis of the Trivy Supply Chain Attack

Aqua Security's Trivy was compromised by TeamPCP, cascading into LiteLLM. A 7-phase Cyber Kill Chain and MITRE ATT&CK analysis of how incomplete credential rotation turned a single breach into a five-ecosystem catastrophe.

Ben Kim
Ben Kim
Git secret scanning in 2026: coverage, setup, and response
Jan 26, 2026

Git secret scanning in 2026: coverage, setup, and response

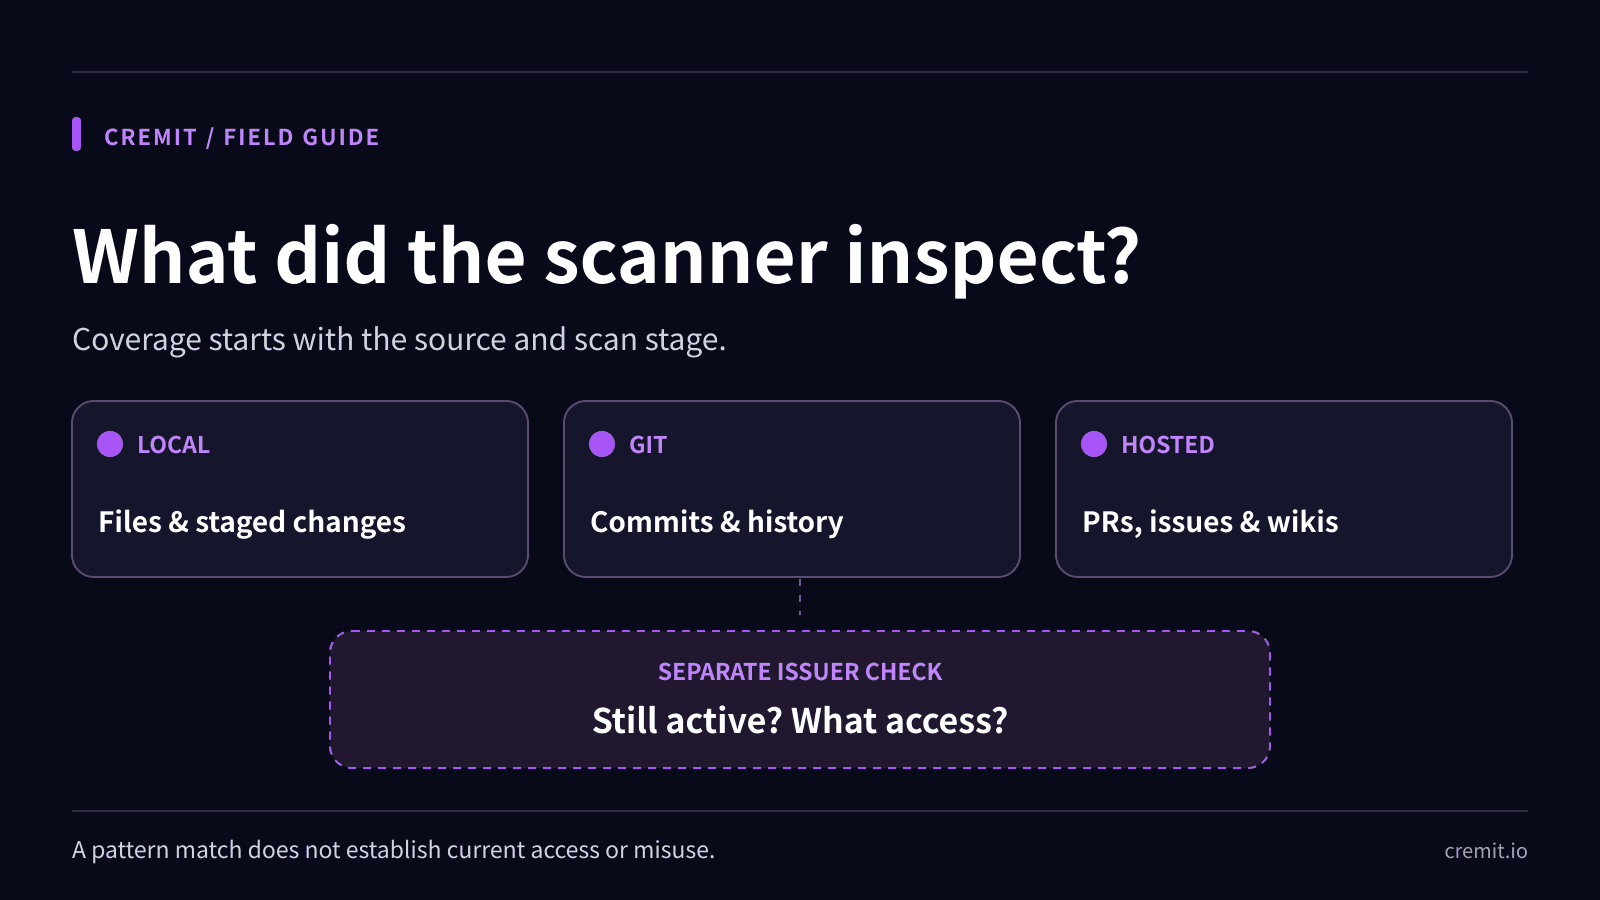
A practical guide to push protection, history scans, validity checks, and issuer-side response, with GitHub, GitLab, and Gitleaks source links.

Ben Kim
Ben Kim
Where credentials escape a CI/CD pipeline
Apr 18, 2025

Where credentials escape a CI/CD pipeline

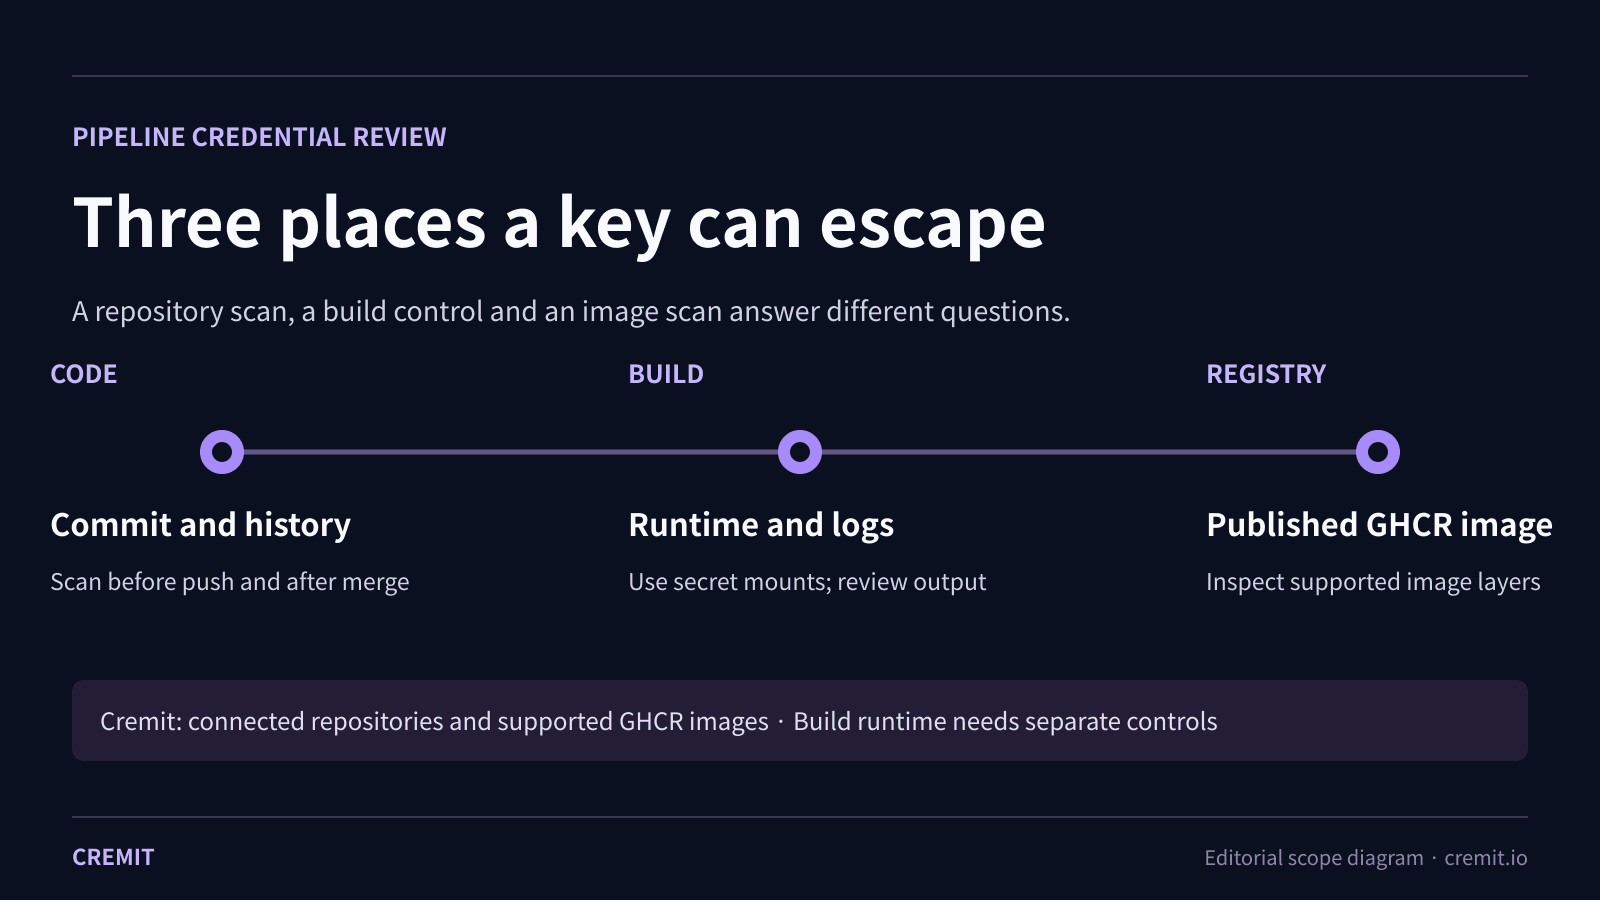
A key can land in Git history, build output or a published image. Use a different check at each boundary and verify any exposure at its issuer.

Ben Kim
Ben Kim
CI/CD Security | Cremit Blog | Cremit