What is secret detection? From pattern match to response
Secret detection finds possible credentials in content a tool actually inspects. Learn what a match proves, where scans run, and how to verify and contain an exposed key.

On this page(6)
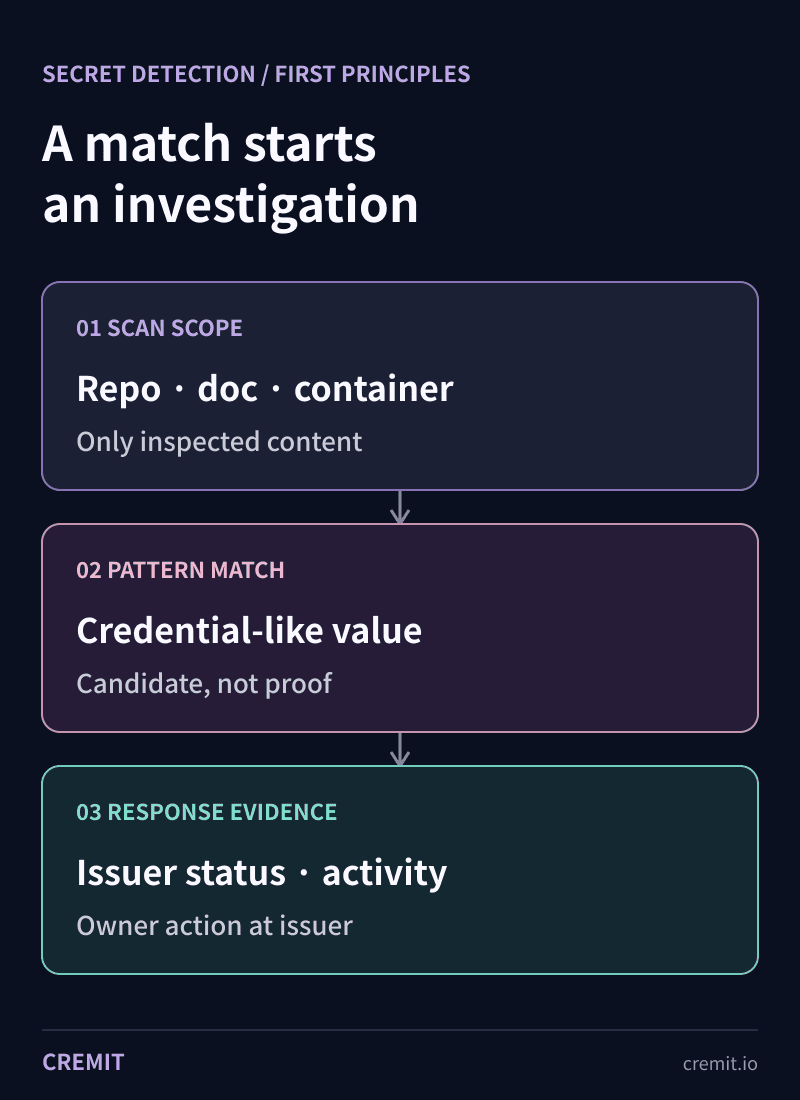
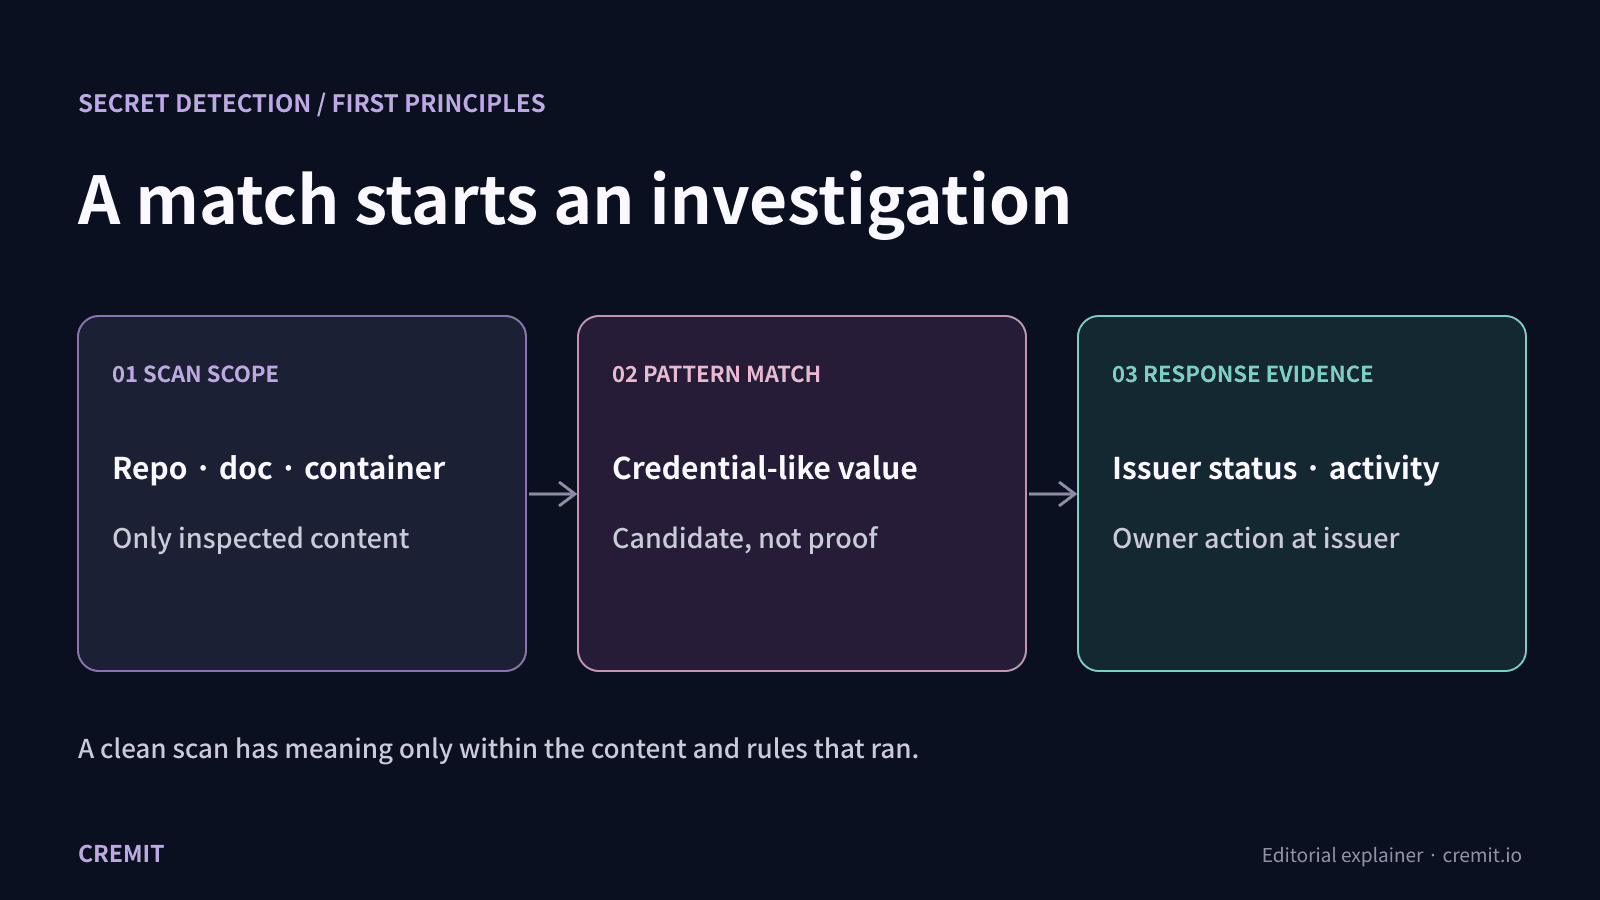
What is secret detection? It is a search for values that may authenticate to a service in a defined set of code, files, history or other content. An API key, token, password or private key found by a scanner is a lead. A pattern match alone does not prove that the credential is still valid, what it can access, or whether anyone used it.
Where can a scan look?
The answer depends on the tool and configuration. Gitleaks can inspect Git history, a directory or standard input. GitHub secret scanning covers repository history and additional GitHub text surfaces such as issues, pull requests and wikis when the relevant service and features apply. A connected-source product can inspect only sources it is authorized and configured to read. Container image layers, CI logs and a running workload are different places; inspecting one does not silently inspect the others.
Start a coverage list with the source, permission, time range and content type. Was the scan limited to current files or did it include history? Were archived objects, private repositories or build outputs included? A clean result means no supported pattern was reported in that inspected scope. It is not proof that an organization has no exposed credentials.
What happens after a match?
First, identify the credential type and where it appeared. A test fixture, masked value or invalid token can resemble a secret. Some tools can ask the issuing service whether supported types still authenticate; others return only a pattern result. Validity checks are type-specific. Permission context for a cloud key is another question, and actual use requires issuer-side activity evidence.
Record the finding location and time without pasting the raw value into a ticket. Find the application that uses it and the person who can act. If a real credential reached an unauthorized location, contain it at the issuing service: revoke or replace the key, update dependent workloads, then check relevant access logs and other copies. For a Git leak, GitHub recommends revocation or rotation before history cleanup; rewriting history cannot recall copies held elsewhere.
Can scanning prevent a leak?
A configured local check or provider push protection may catch supported secrets before a change is shared. It can be bypassed or may not recognize every secret type. A later scan finds values already present in its scope. Avoid putting secrets into build arguments or environment variables that may persist in image metadata; Docker documents secret mounts for build-time use. Prevention, discovery and response are separate controls.
Where Cremit fits
Cremit scans supported connected sources for credential patterns, checks issuer status for supported types, and brings available source, AWS/GCP access context and owner clues into a finding. It does not inspect every CI runner or live process, prove that a key was misused, automatically revoke credentials, or certify compliance. The owner still has to review the source boundary, act at the issuer and record the result.
Primary documentation
GitHub Docs: secret scanning and scanned locations
GitHub Docs: which patterns support validity and push protection
Gitleaks: git, directory and standard-input modes
GitHub Docs: revoke before repository history cleanup
Docker Docs: build secrets and secret mounts
AWS IAM: replace and deactivate access keys
Related reading
Read next
Secret scanning false positives: how to triage findings
A pattern match, a revoked key, and an unverified key need different responses. Learn how to separate them and prioritize exposed credentials.
A rotation record is not a map of leaked credentials
Lifecycle records show intended access. Secret findings show copies in scanned sources. Compare both before deciding who should replace a key.
Where credentials escape a CI/CD pipeline
A key can land in Git history, build output or a published image. Use a different check at each boundary and verify any exposure at its issuer.
Get the next one in your inbox
Monthly NHI security brief from Cremit. One email, high signal.