Secret scanning: when to use built-in, open-source or connected-source checks
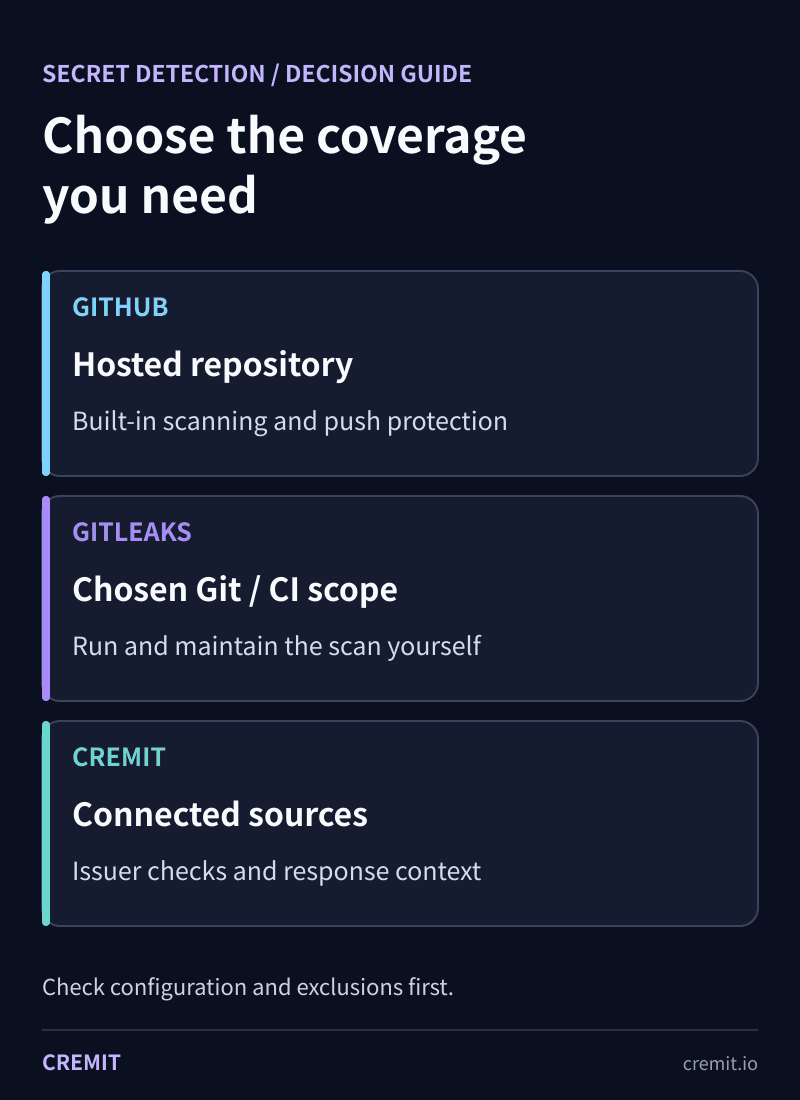
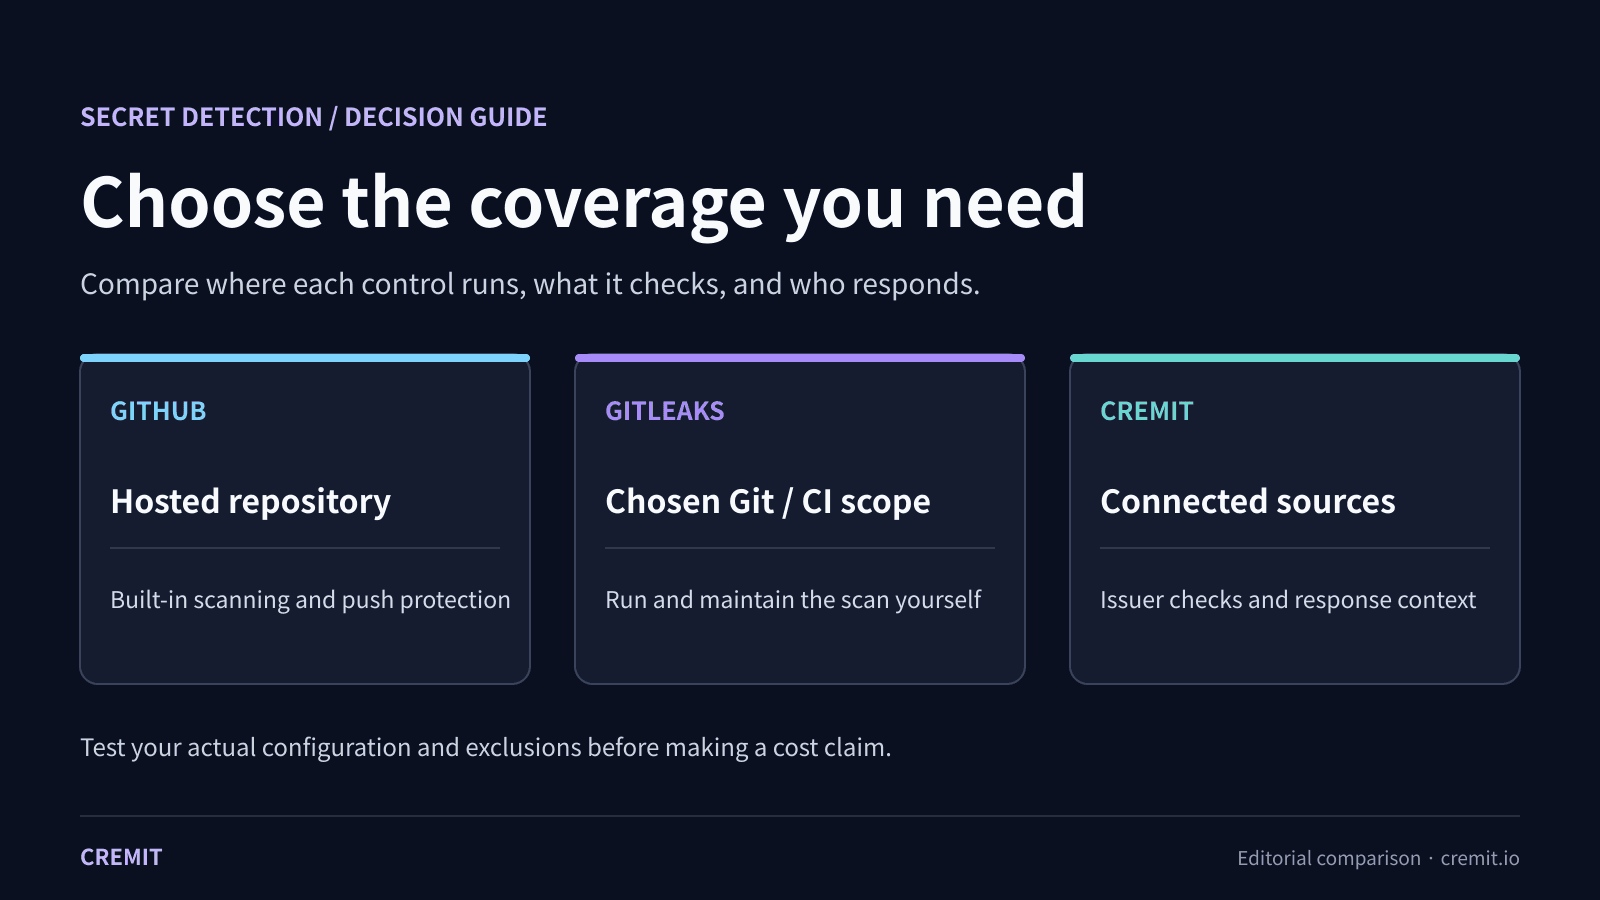
Start with the sources you need to inspect, the evidence each check returns, and who will revoke a live key. Compare GitHub, Gitleaks and Cremit by the work each covers.

On this page(5)
The useful question is not “build or buy?” in the abstract. Write down where your credentials can appear, which checks you need, and who acts when a key still works. GitHub’s built-in controls, a scanner you run yourself and a connected-source platform can work together. Their coverage depends on configuration.
1. Identify the boundary you need to inspect
If the problem is a GitHub repository, review which secret scanning and push protection features are available and enabled for that repository. GitHub documents different availability by repository type and plan, supported patterns and push-protection limits. A blocked push can also be bypassed under the applicable policy. Inspect the actual settings and a harmless fixture before relying on the control.
Gitleaks can scan a Git repository, a directory or standard input. You choose its trigger, commit range, rules, exclusions, baseline and alert destination. A local hook can catch a change early; CI can check a configured range. Both require someone to maintain the job and check what it skipped.
Cremit scans supported sources that you connect, including repositories, cloud storage and collaboration tools. It does not run inside every developer’s local Git hook. Connecting a repository also does not mean every CI log or local file was inspected. List those other surfaces separately.
2. Separate a pattern match from a response decision
A pattern match gives you a location and a candidate credential. For supported types, an issuer-side check can tell you whether the key authenticates at that moment; AWS and GCP integrations can add available access context. Neither result proves that the key was used by an attacker. The responder still needs relevant issuer logs and must revoke or rotate the key at the issuer.
Cremit brings supported validity and access information together with source and ownership clues in a finding. If you only need a GitHub-only preventive check, a properly configured native control may cover the immediate task. If you need local or CI coverage with rules you own, test Gitleaks there. If your investigation crosses connected sources and needs supported issuer context, test whether Cremit covers those exact sources and credential types.
3. Compare work you can actually measure
For each option, record setup and permission review, scanner and rule maintenance, skipped sources, alert triage, issuer checks, response handoff, data retention requirements and any license cost. Do not apply a generic maintenance percentage or assume that a paid product always costs less. The answer changes with the existing controls and the number of sources you operate.
A short evaluation using the same cases
Choose a representative repository and one other source you are authorized to test. Use harmless test patterns and already revoked historical examples; do not publish a working credential as a test. For each control, record the source and commit range read, patterns matched, exclusions, whether validity or access context was available, and the time from finding to an assigned responder. Ask who handles a finding the tool cannot verify.
Keep the controls that answer your actual questions. A clean result is evidence about the configured scan, not proof that no key exists. If a real key has reached a shared source, revoke or rotate it at the issuer before debating history cleanup.
Primary documentation and product scope
GitHub secret scanning detection scope
GitHub push protection and bypass
Gitleaks scan modes and pre-commit setup
Read next
Your Slack Webhook Is Write-Only, Until an AI Agent Reads the Channel
A leaked Slack incoming webhook is usually triaged as low severity: write-only, one channel, no data access. The moment an AI agent reads that channel and can act with tools, that write-only primitive becomes an indirect prompt injection path into the agent's privileges. Here is the full kill chain, the exact preconditions, and how to defend it.
A rotation record is not a map of leaked credentials
Lifecycle records show intended access. Secret findings show copies in scanned sources. Compare both before deciding who should replace a key.
AWS S3 secret scanning: what a connected bucket shows
Cremit reads supported current objects in connected S3 buckets to locate credentials. Check access, skipped objects, earlier versions and the issuer separately.
Get the next one in your inbox
Monthly NHI security brief from Cremit. One email, high signal.